
Generate a treemap graph from Pyright verifytypes output.




A simple cli tool to visualise the state of a Python project's type completeness, from the output of pyright's --outputjson --verifytypes command:
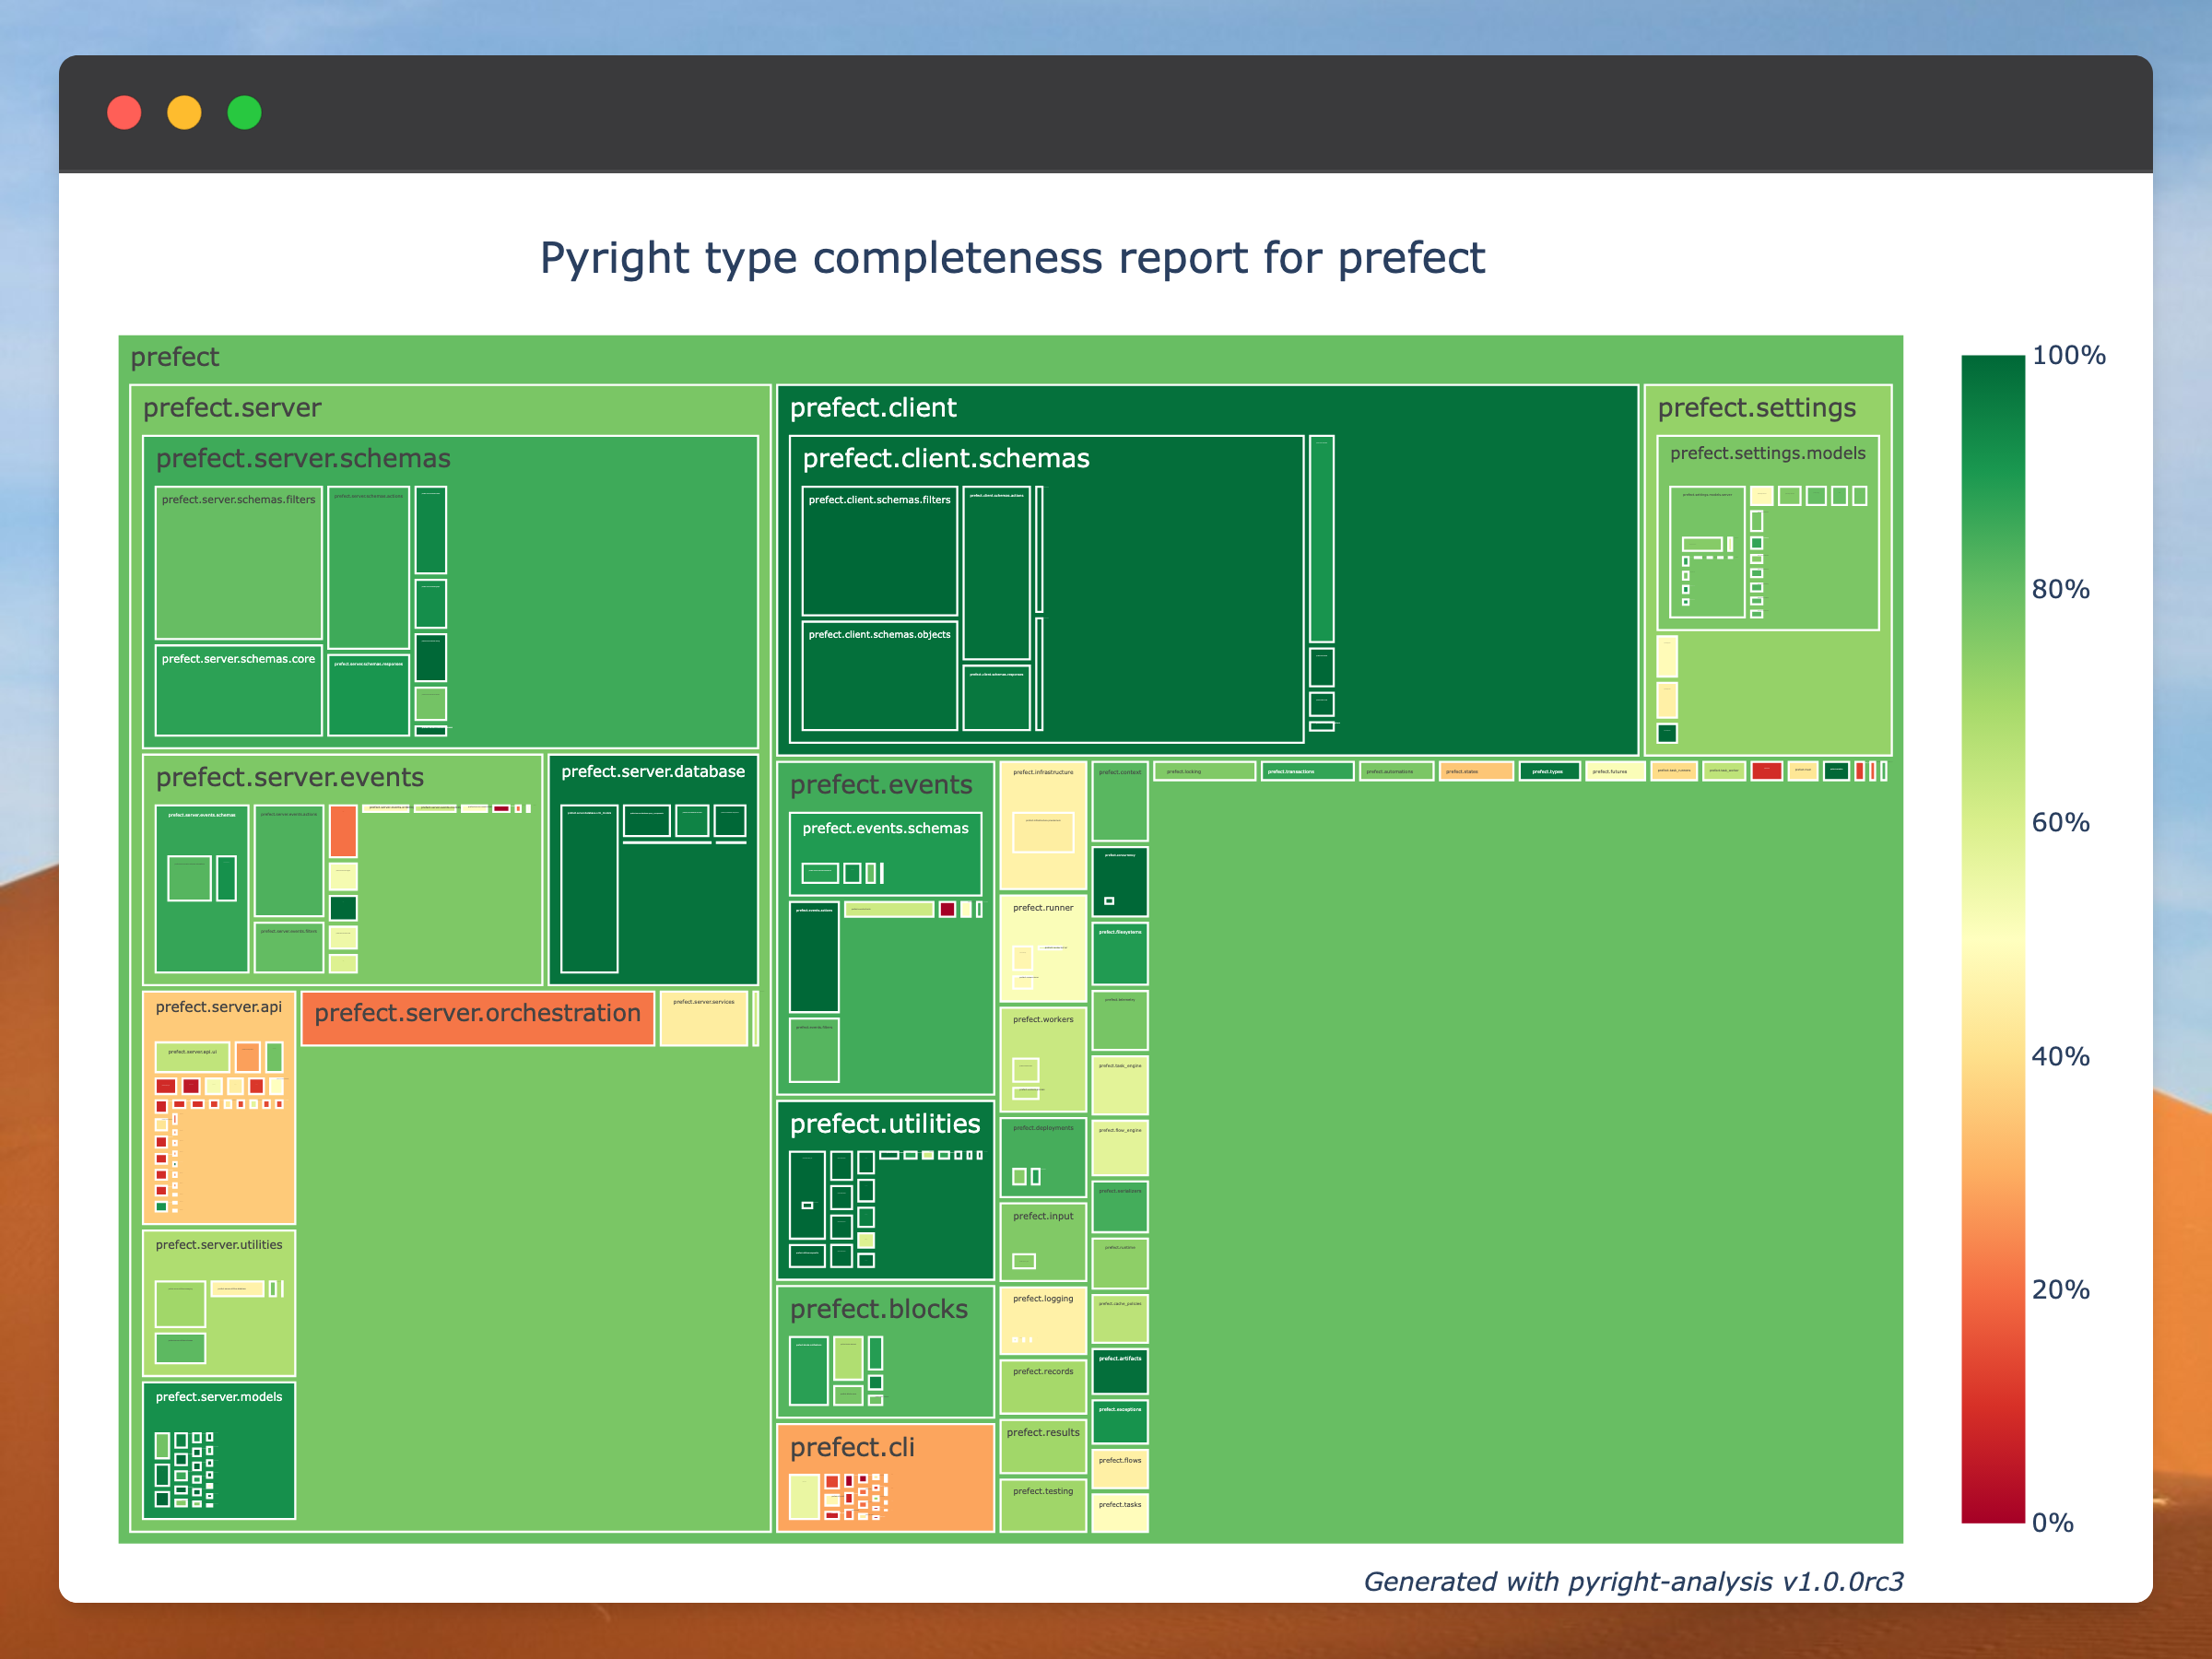
The interactive graph depicts a projects modules as a tree, with each the size of each module based on the number of exported symbols.
Usage
Use a Python tool manager like uv tool or pipx:
$ uv tool install pyright
$ uv tool install pyright-analysis
Then generate a type completeness JSON report for your package, and transform the report into a graph:
$ pyright --outputjson --ignoreexternal --verifytypes PACKAGE > PACKAGE.json
$ pyright-analysis PACKAGE.json
This will open the resulting graph in your browser.
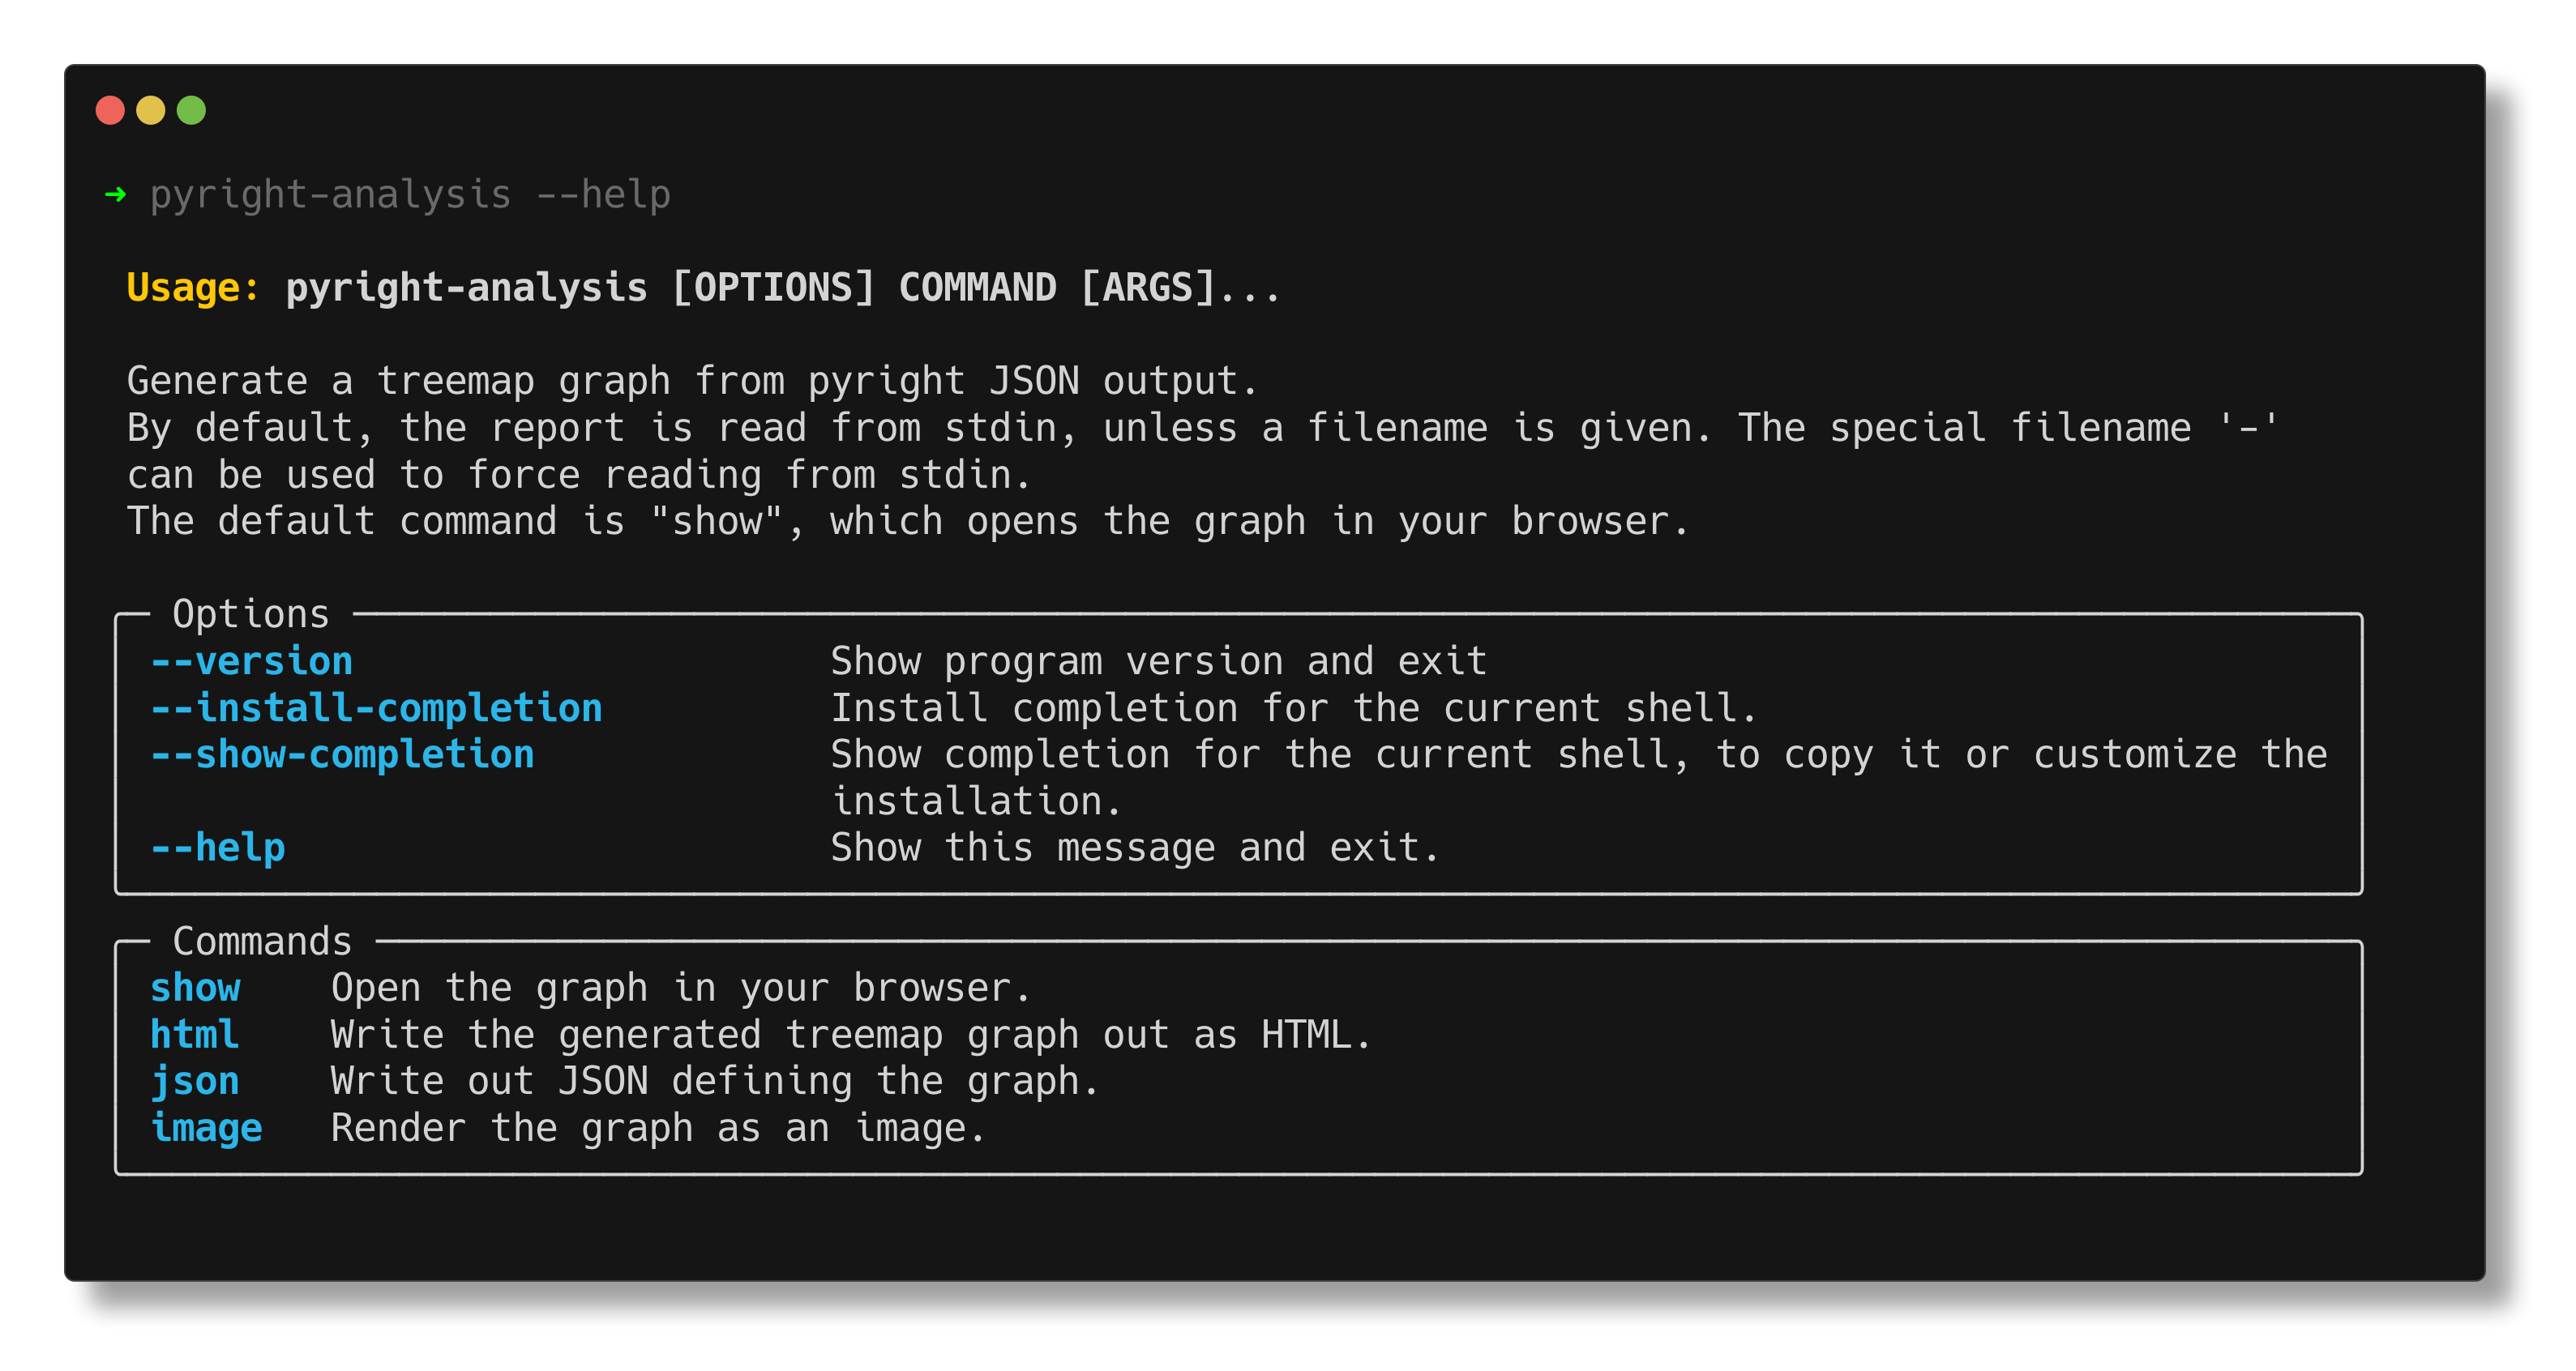
Full help documentation is available on the command-line:
Features
- Interactive responsive graph. Hover over each package to get more detail about symbol counts and completeness, or click on packages to zoom in.
- Export options:
- Full stand-alone HTML page.
- HTML div snippet with configurable HTML id.
- Static image export as PNG, JPG, WebP, SVG or PDF.
- Plotly JSON graph representation.
GitHub Action
You can generate visualiations for your own projects in your GitHub workflow by using the pyright-analysis-action action.
Development
This project uses uv to handle Python dependencies and environments; use uv sync to get an up-to-date virtualenv with all dependencies. This includes development dependencies such as Ruff (used for linting and formatting) and Pyright (used to validate type annotations).
Linting and formatting
While PRs and commits on GitHub are checked for linting and formatting issues, it's easier to check for issues locally first. After running uv sync, run uv run pre-commit install to install pre-commit hooks that will run these tools and format your changes automatically on commits. These hooks also run uv sync whenever you working tree changes.
Testing
This project uses pytest to run its tests: uv run pytest.
1 maintainer

Metadata
1 maintainer
Release files for pyright-analysis 1.0.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| pyright_analysis-1.0.0.tar.gz | 9.3 kB | With provenance | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| pyright_analysis-1.0.0-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 20.4 kB
Release files / pyright_analysis-1.0.0.tar.gz
| Download URL | pyright_analysis-1.0.0.tar.gz |
|---|---|
| Size | 9.3 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
1d76fe897bb6c9f7cd26d09b51a68013ab74b0f33862bdb0ad43c0f46f423f92
|
|
BLAKE2b-256 checksum How to use checksums |
6043fd39aeddd38849b9a0ee45f1614009aff926100dd26ccd30324cfbfef5de
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.0.1 CPython/3.12.8
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jan 22, 2025.
Transparency logRelease files / pyright_analysis-1.0.0-py3-none-any.whl
| Download URL | pyright_analysis-1.0.0-py3-none-any.whl |
|---|---|
| Size | 11.1 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
eabe1123c954c0528eb37fc16afd1095376f6152b7685fc7bf67c8975ad536b0
|
|
BLAKE2b-256 checksum How to use checksums |
b82311fc129e1e91a74bb7ce63c25078f23a339f42bfd8e3632b2b1ba313262e
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.0.1 CPython/3.12.8
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jan 22, 2025.
Transparency logSecurity for pyright-analysis 1.0.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 2 files in this release have been uploaded with provenance metadata.
Attestation for pyright_analysis-1.0.0.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jan 22, 2025.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














