
quite-admin
Version: 0.8.17 · Changelog
An admin panel for your existing FastAPI or Litestar models.
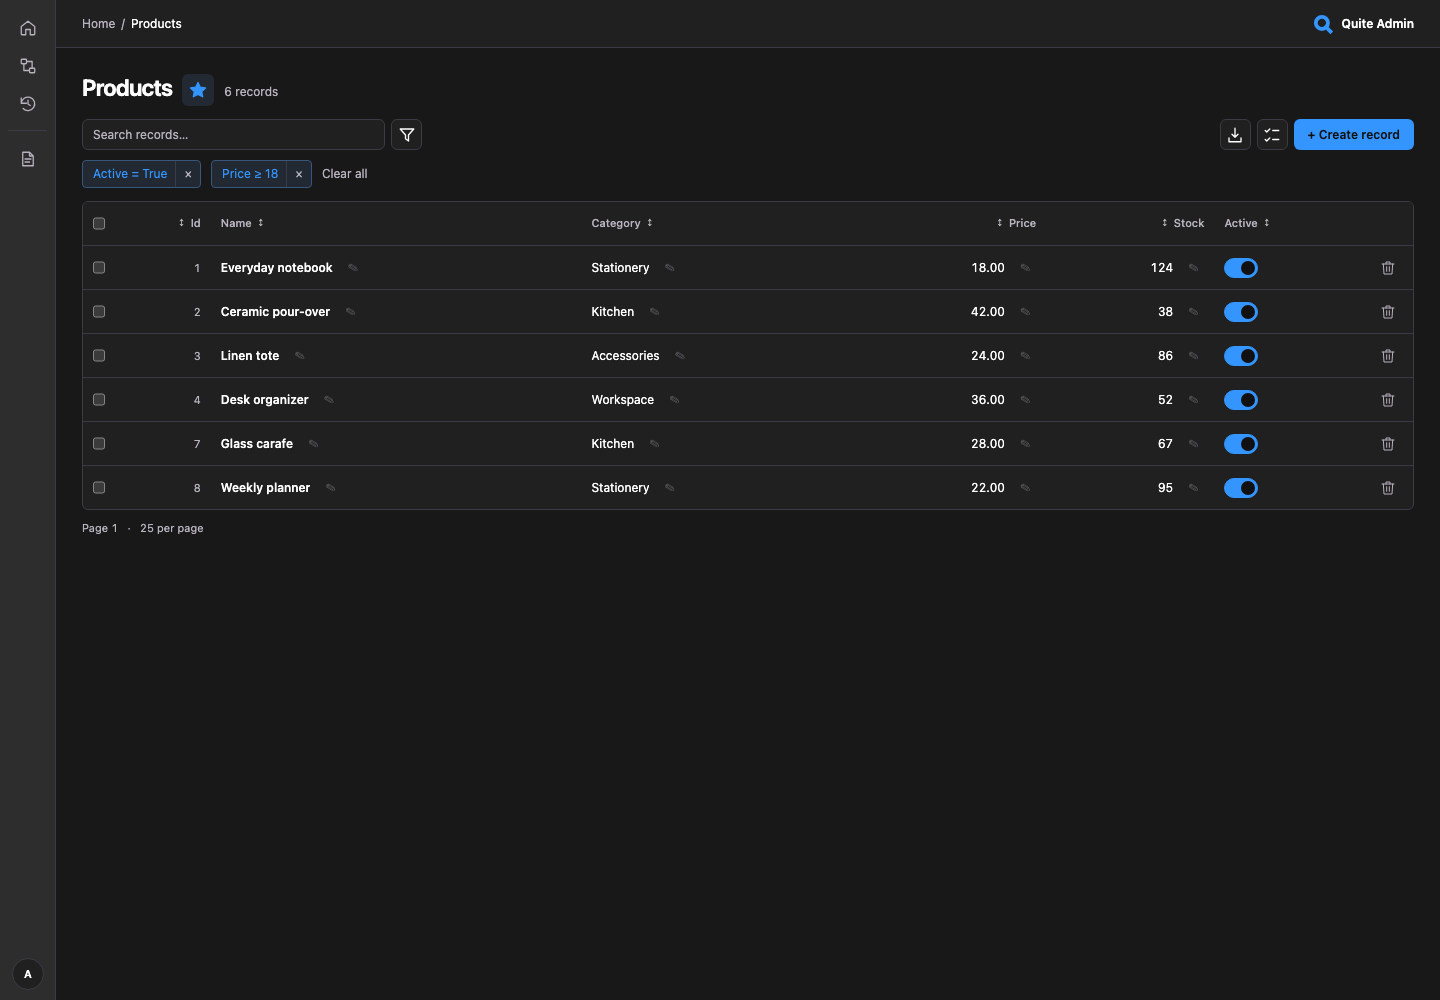
Automatically discover collections and forms without writing a separate admin class for every model. Edit related records, inspect before/after history and export data from the same interface. No additional Pydantic schemas or DTOs are required.
Try the browser demo · Run your first app · Connect an existing app
English documentation · Документация на русском
Supports CPython 3.11–3.15. MIT licensed.
Add to your existing app
Install into your application's environment:
pip install 'quite-admin[sqlalchemy,fastapi]'
# For Litestar: uv add 'quite-admin[sqlalchemy,litestar]'
Add this beside your existing FastAPI app. Replace the database import with your
SQLAlchemy or SQLModel base and session factory:
import os

from quite_admin import Admin, PasswordAuth
from quite_admin.adapters.sqlalchemy import SQLAlchemyAdapter
from myapp.database import Base, SessionFactory

admin = Admin(
    auth=PasswordAuth.single_user("admin", os.environ["QUITE_ADMIN_PASSWORD"]),
    secret_key=os.environ["QUITE_ADMIN_SECRET"],
    adapters=[SQLAlchemyAdapter(SessionFactory, base=Base)],
    secure_cookies=False,  # Local HTTP; keep True for production HTTPS.
)
admin.mount_fastapi(app)
Set QUITE_ADMIN_PASSWORD and a persistent random QUITE_ADMIN_SECRET of at least
32 bytes in your application configuration. Import your model modules before startup,
run the app and open /admin/. Sign in as admin with the configured password.
For Litestar, replace the last line with admin.mount_litestar(app).
Your application keeps its database lifecycle and migrations. See the quickstart and deployment guide.
Try a complete application
The single-file example includes Customers → Orders → Order items, sign-in and persistent SQLite data. Download it and run with uv; its dependency header installs the packages automatically:
curl -fsSLo quickstart.py https://raw.githubusercontent.com/lyova24/quite-admin/master/examples/quickstart.py
QUITE_ADMIN_PASSWORD='local-demo-only' uv run --script quickstart.py
Open localhost:8000/admin/, sign in with
admin / local-demo-only, change an order and inspect Activity history.
No repository checkout or Node.js is needed.
Step-by-step walkthrough and pip alternative.
To explore without running Python, open the
browser demo with admin / admin.
Its fictional data stays in your browser; Reset demo restores it.
See the interface tour.
What you get
- Authenticated CRUD with automatic forms, search, sorting and typed filters.
- Inline cell editing and atomic one-to-one, one-to-many and many-to-many relationship editing.
- CSV/XLSX export with column selection, filters and related-table data.
- Activity history with before/after field values, user and collection filters, configurable recording levels and storage.
- Automatic stale-edit detection, field permissions and server-side write validation.
- Count-free cursor pagination, SQL read deadlines and configurable read concurrency.
- Interactive database schema, grouped navigation and English/Russian UI.
- Type-aware date/time, JSON, multiline text and nullable boolean controls.
- Custom pages, Jinja2 templates, field controls, write hooks, record actions and bulk commands.
- Optional per-model application services, form-only inputs and Pydantic validation.
Choose your data source
Native adapters support SQLAlchemy 2.x, SQLModel, Tortoise ORM, Peewee and GINO 1.x.
Install the matching extra: sqlalchemy, sqlmodel, tortoise, peewee or gino-legacy.
GINO needs a separate environment from SQLAlchemy 2.x.
SQL reflection discovers existing SQL tables without importing ORM models. The custom adapter API can connect another data source or route writes through your application's services. Integration guide · Custom adapters.
Use pip install quite-admin for the ORM-independent core. The pydantic extra is
only needed for optional per-model form schemas; ordinary model discovery does not need it.
Compatibility and guarantees
Read the public API guarantees, database compatibility matrix and dependency compatibility guide before adopting quite-admin. Patch releases preserve the documented public API; adapter and template contracts are versioned.
SQL reflection runs database constraints and triggers. Use a native ORM or application-service adapter when writes must execute Python ORM hooks or business rules. Current limitations.
Development
From a source checkout, run the larger FastAPI or Litestar showcase:
uv sync --locked
QUITE_ADMIN_PASSWORD='local-demo-only' uv run uvicorn examples.fastapi_app:app --reload
# Or: examples.litestar_app:app
Build the English/Russian Diplodoc site with Node.js 24+ and npm 11.5.1+:
npm ci
npm run docs:build
npm run docs:serve
Run the repository checks:
uv run pytest -q
uv run ruff check src tests examples scripts
uv run ruff format --check src tests examples scripts
CI checks CPython 3.11–3.15, with dedicated PostgreSQL/MySQL contracts and isolated minimum/latest dependency profiles. Tagged releases reuse successful CI for the exact commit, publish source archives and deploy its documentation artifact; the separate PyPI workflow builds and validates one wheel/sdist pair before Trusted Publishing. Development · Release policy.
1 maintainer

Metadata
1 maintainer
Release files for quite-admin 0.8.17
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| quite_admin-0.8.17.tar.gz | 4.9 MB | With provenance | Details for quite_admin-0.8.17.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| quite_admin-0.8.17-py3-none-any.whl | Python 3 | none | any | Details for quite_admin-0.8.17-py3-none-any.whl |
Total release size: 5.1 MB
Release files / quite_admin-0.8.17.tar.gz
| Download URL | quite_admin-0.8.17.tar.gz |
|---|---|
| Size | 4.9 MB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
6b08ec78de13165bc54d986acb2d66ec5325616b08ccba8190117fbffc44939a
|
|
BLAKE2b-256 checksum How to use checksums |
2940d9503da55624d9122abb82f45215f3ba31f145b76d3ae5bd4455020be297
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 11, 2026.
Transparency logRelease files / quite_admin-0.8.17-py3-none-any.whl
| Download URL | quite_admin-0.8.17-py3-none-any.whl |
|---|---|
| Size | 232.3 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
720e71fa816183c49fd77ac78db012c5b8408c15e5745e7e85d031a6bf996a50
|
|
BLAKE2b-256 checksum How to use checksums |
7fc811d2b121a1be376358b52fdc13f72882777f6b09483d843a9436938d5c14
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 11, 2026.
Transparency logSecurity for quite-admin 0.8.17
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
Both files in this release have been uploaded with provenance metadata.
Attestation for quite_admin-0.8.17.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 11, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














