
RAI Check Kit
RAI = Responsible AI. A Python package suite for evidence-grade audits of responsible, secure, and trustworthy AI systems.
Run fairness, data quality, robustness, compliance, image, medical imaging, LLM safety, RAG security, and agent trace checks. Export HTML, Markdown, or JSON reports and gate CI pipelines on risk thresholds.
Author: Sai Teja Erukude | License: MIT
Why this exists
AI teams often run fairness, robustness, RAG, and agent security checks separately. RAI Check Kit brings them into one evidence and reporting workflow, so teams can review findings consistently, preserve audit artifacts, and apply the same CI gates across model types.
What it looks like
HTML audit report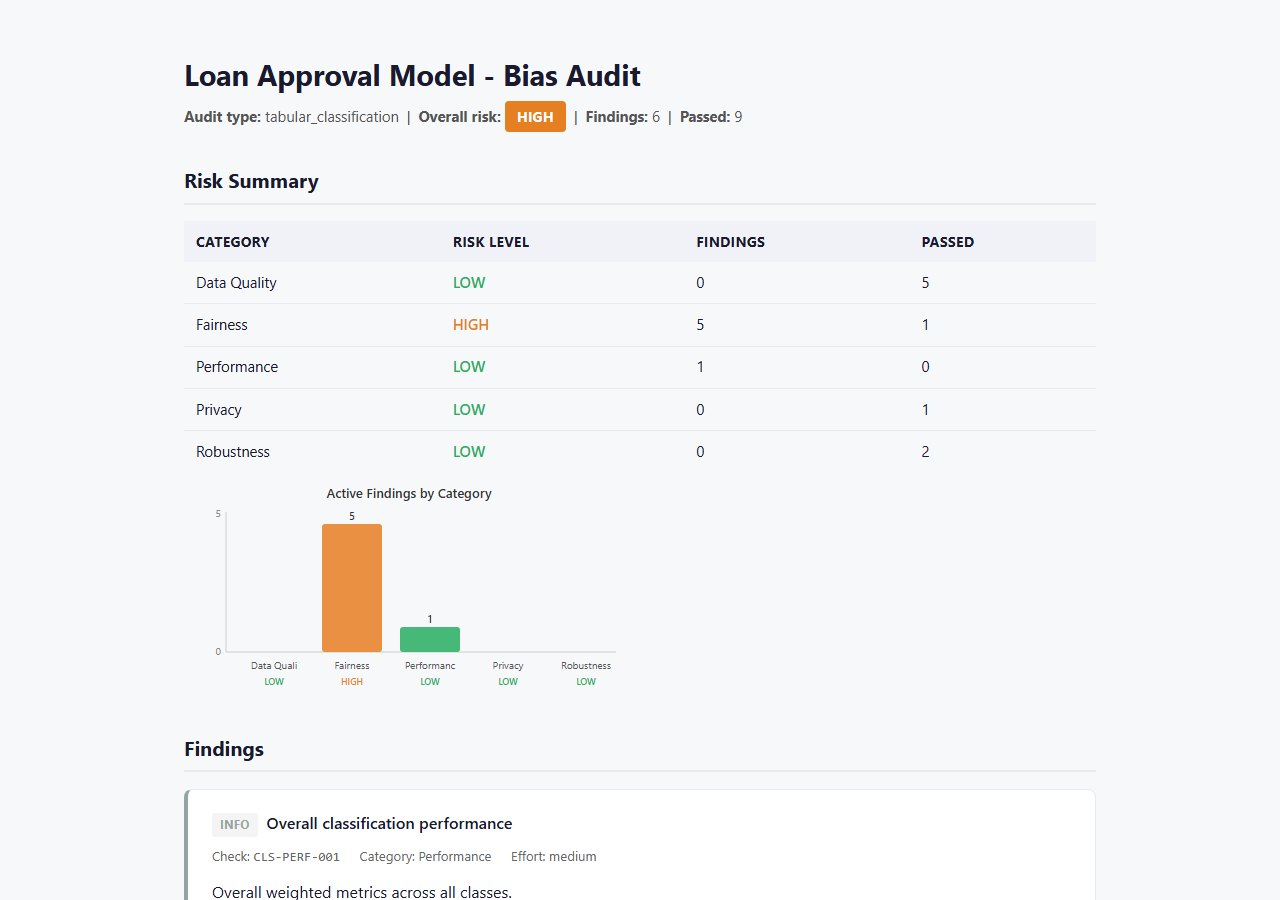
|
Model card export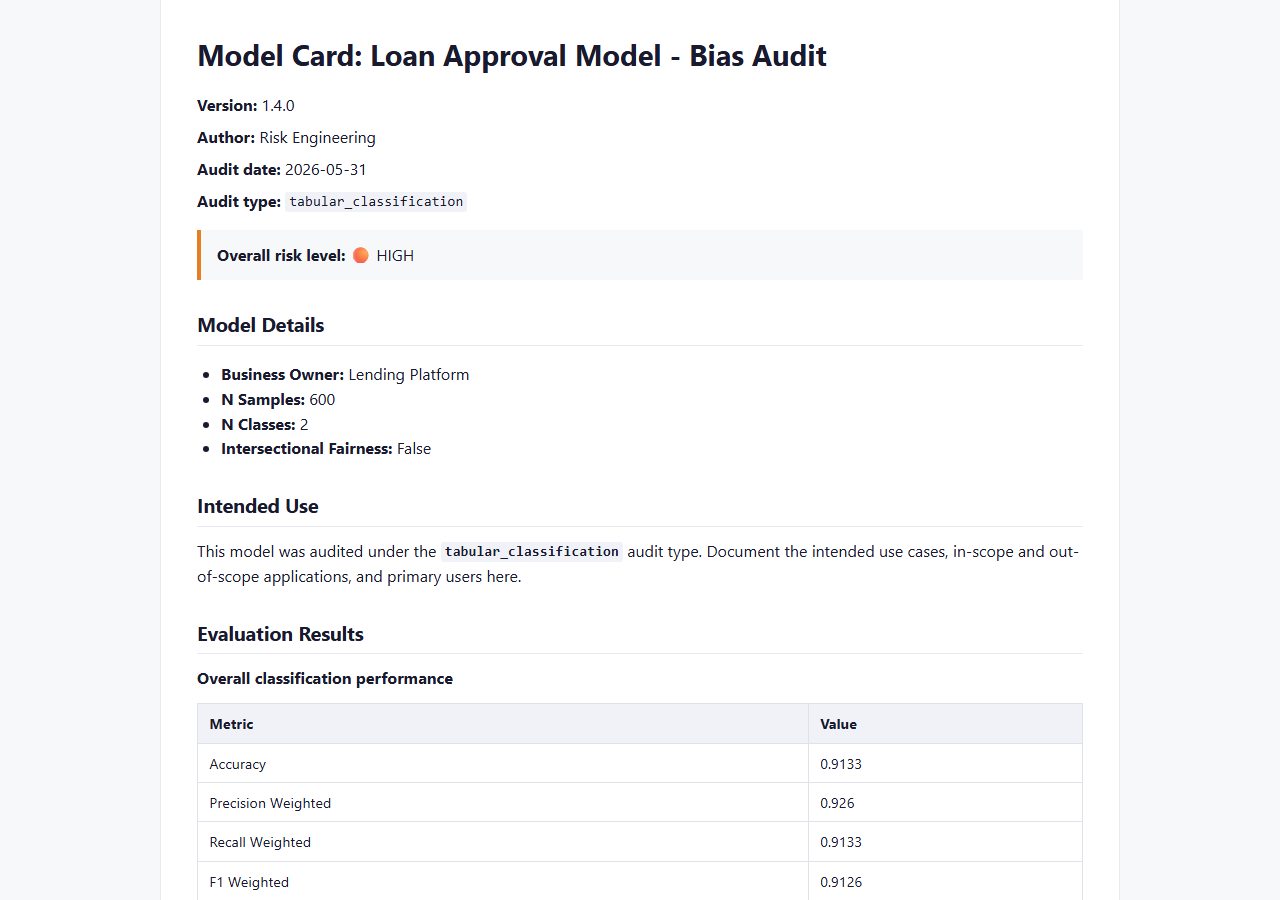
|
LLM and RAG audit output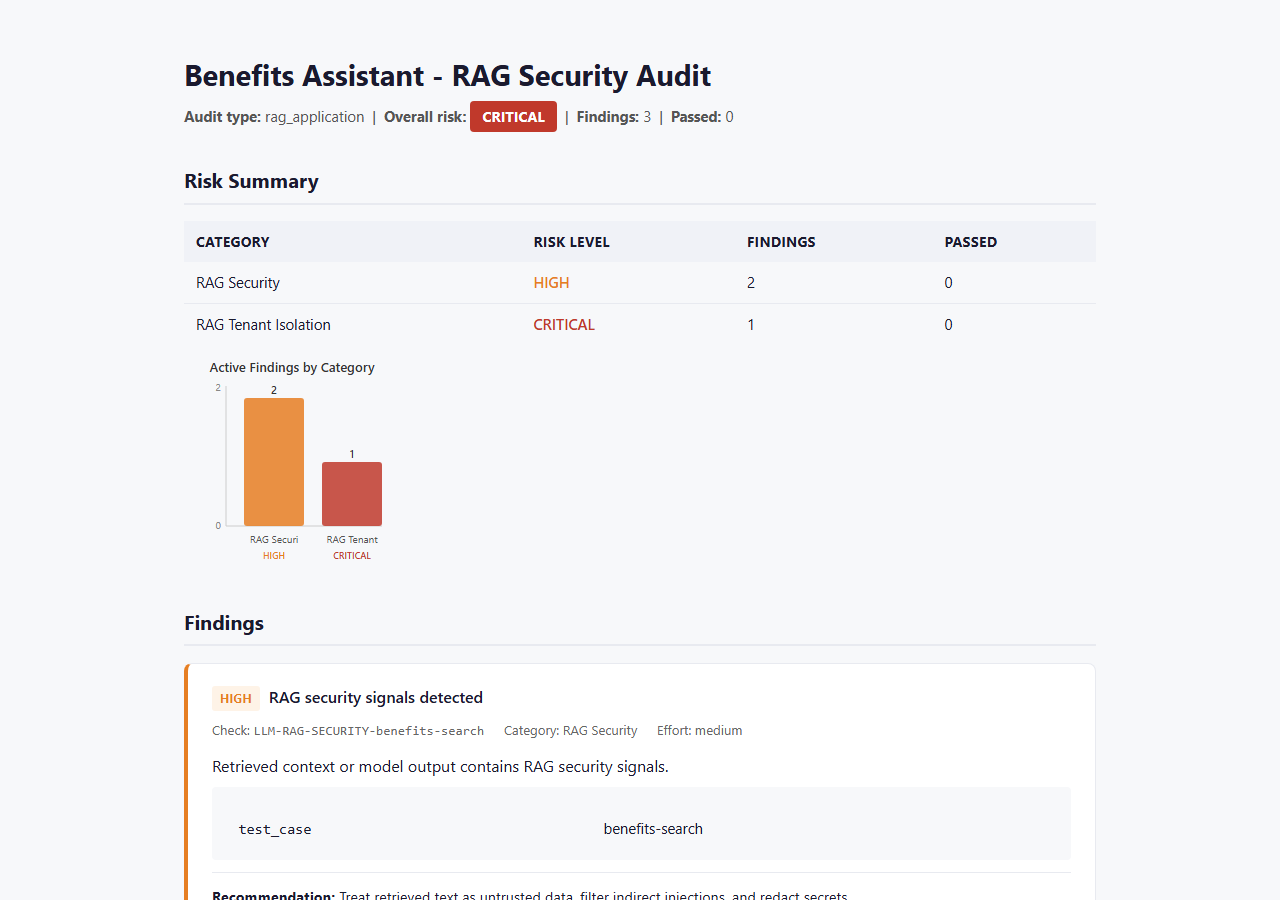
|
Agent trace finding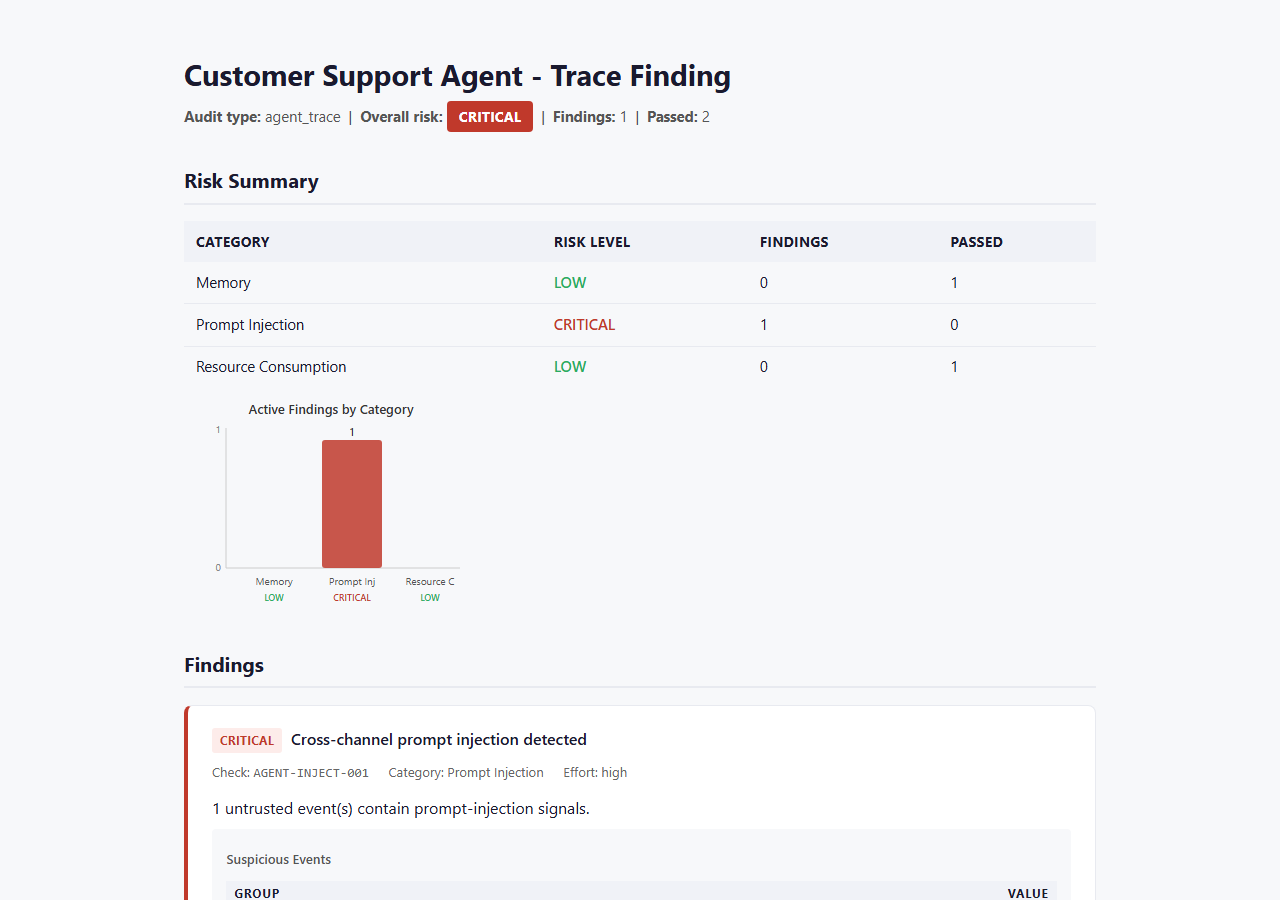
|
Packages
| Package | Purpose |
|---|---|
rai-check-core |
Audit engine, findings, reports, history, CI gates |
rai-check-ml |
Tabular ML - fairness, drift, data quality, robustness |
rai-check-dl |
Image, medical imaging, and scientific AI audits |
rai-check-genai |
LLM, RAG, and agentic AI safety, security, and trace audits |
rai-check-kit |
Meta-package - installs core + ml, unified CLI |
Install
pip install rai-check-kit          # core + tabular ML
pip install "rai-check-kit[all]"   # all modules (dl + genai)
Quick start
rai-check ml run --help
Inspect installed packages, plugin load failures, and missing optional dependencies:
rai-check doctor
rai-check doctor --json
Diagnostics include installation or repair commands. Missing optional features
are informational; installation errors return exit code 1.
For repeatable audit workflows, generate and run a YAML configuration:
rai-check init --project loan-model
rai-check run --config audit.yaml
rai-check init writes a starter predictions.csv beside audit.yaml; replace
it with captured model predictions, or update audit.data to point at your CSV.
Classification configs expect y_true and y_pred columns by default.
Configured runs write report artifacts and an evidence manifest with input, environment, source-revision, and artifact hashes.
from rai_audit.ml import ClassificationAudit

report = ClassificationAudit(
    y_true=y_true,
    y_pred=y_pred,
    sensitive_features=sensitive_df,
).run()

report.to_html("audit_report.html")
Examples
- Fairness audit walkthrough
- Batch drift monitoring
- MLflow and Airflow templates
- Captured-response LLM and RAG audit suite
- Scientific image robustness audit
- Agent trace with a webpage prompt-injection attempt
Development
pip install uv
uv sync
uv run pytest
See CONTRIBUTING.md for monorepo layout and release workflow.
1 maintainer

Metadata
1 maintainer
Release files for rai-check-kit 0.0.2
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| rai_check_kit-0.0.2.tar.gz | 7.7 kB | With provenance | Details for rai_check_kit-0.0.2.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| rai_check_kit-0.0.2-py3-none-any.whl | Python 3 | none | any | Details for rai_check_kit-0.0.2-py3-none-any.whl |
Total release size: 15.4 kB
Release files / rai_check_kit-0.0.2.tar.gz
| Download URL | rai_check_kit-0.0.2.tar.gz |
|---|---|
| Size | 7.7 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
74466866c65a46998765f6f3d82c250b4368defc62417fdb6306b45f684edcb1
|
|
BLAKE2b-256 checksum How to use checksums |
07c1b653ad974975821881f0d034c61d865460c84549661a34c52456b03f84bd
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 11, 2026.
Transparency logRelease files / rai_check_kit-0.0.2-py3-none-any.whl
| Download URL | rai_check_kit-0.0.2-py3-none-any.whl |
|---|---|
| Size | 7.7 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
cd49ac030b2b5590b9f93454175c31b563d8ccaeb5602f7b83f7d39801143249
|
|
BLAKE2b-256 checksum How to use checksums |
f042d1b33b742cccbbf3224a9ad2f48fba749cba3cb5ade3133ace5a1905a564
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 11, 2026.
Transparency logSecurity for rai-check-kit 0.0.2
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 2 files in this release have been uploaded with provenance metadata.
Attestation for rai_check_kit-0.0.2.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 11, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














