
Model Card Lint - EU GPAI (AI Act Art. 53)
Runs the same checker as the npm package
@readystack/model-card-lint-gpaion a Node.js runtime that pip installs for you (nodejs-wheel-binaries) - no system Node.js needed. Your files are checked locally.
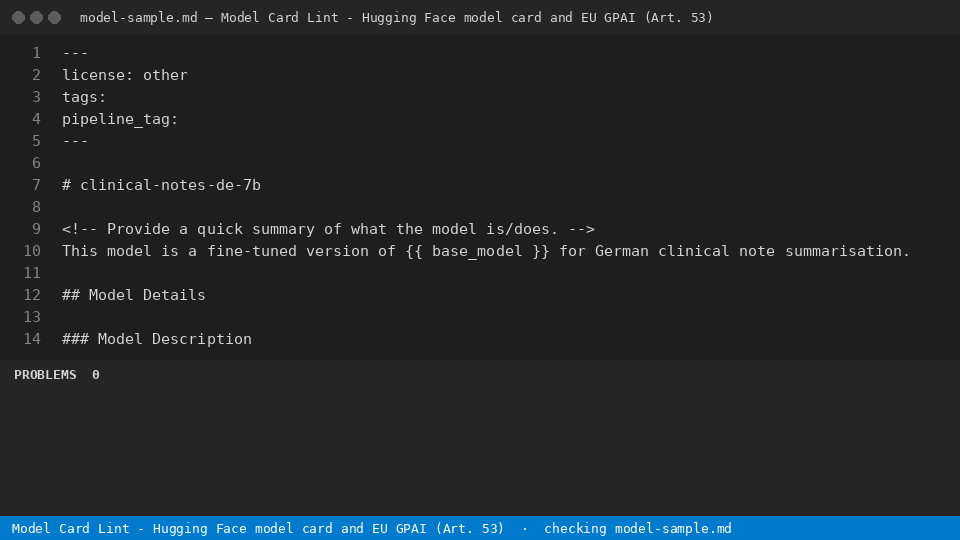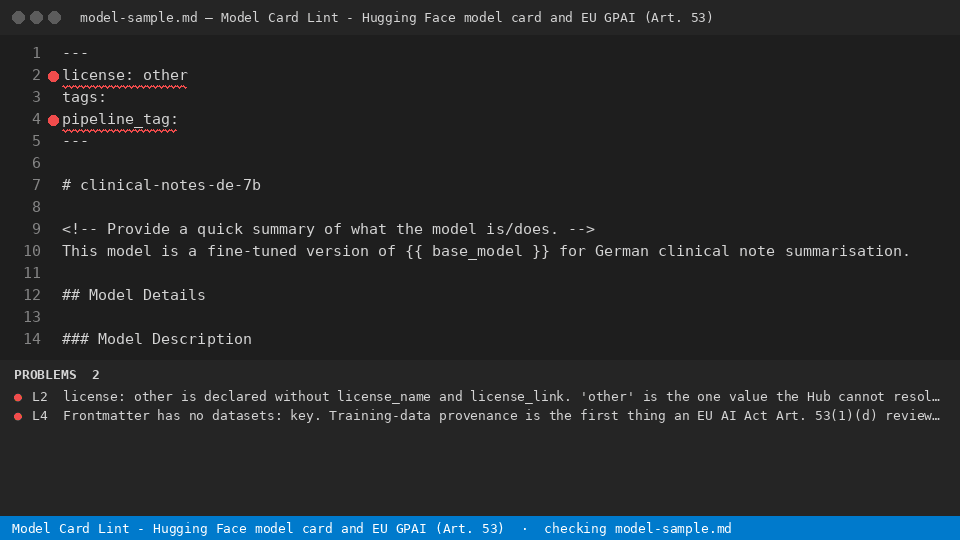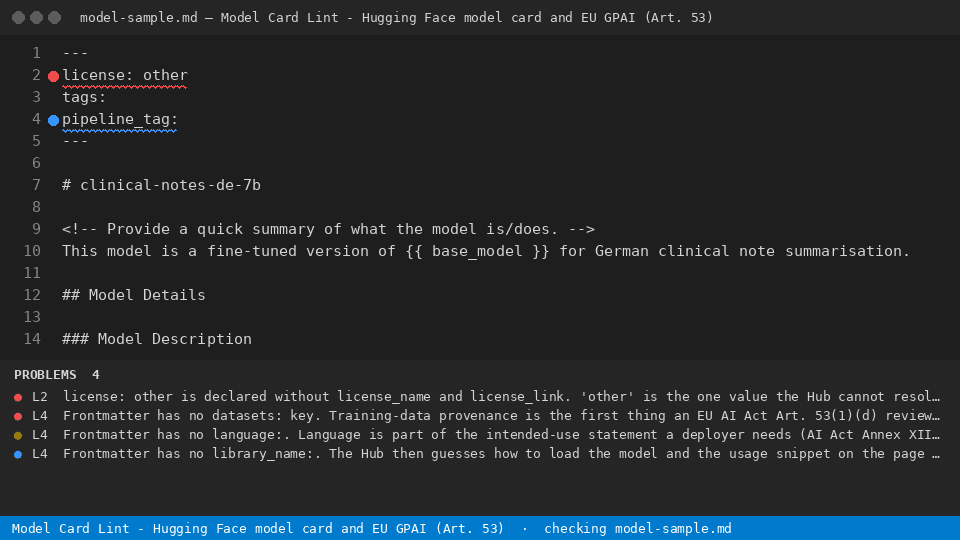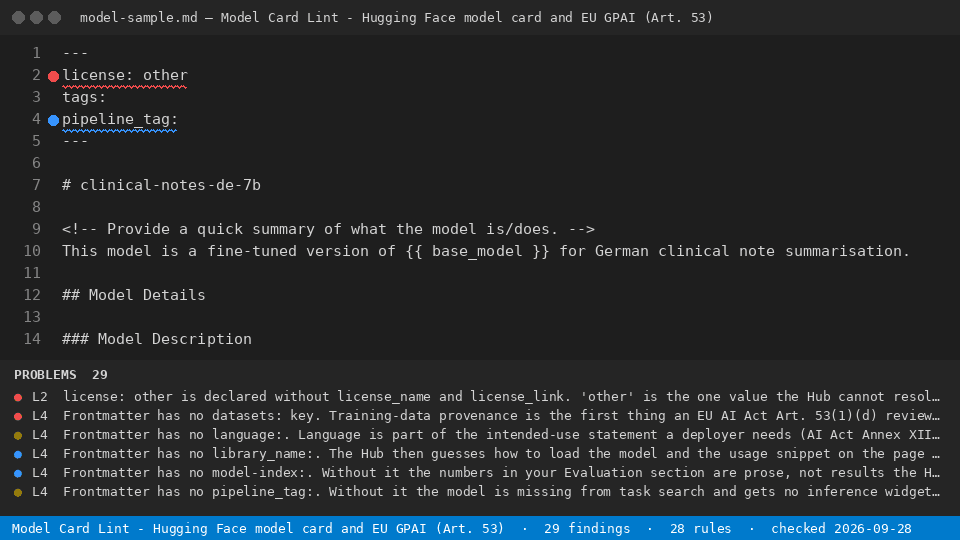
Lints a Hugging Face model card against the Hub metadata spec and the EU AI Act general-purpose AI documentation duties, line by line.
Install
model-card-lint-gpai file
Node 18+. The same 28 rules as the VS Code extension, from a terminal or CI.
Free
- Lint the model card you have open against all 28 rules, as often as you like - line number, rule id, the article it comes from, and the line to write instead. Runs locally, no key, no upload.
--ruleslists every rule
With a licence ($29 once)
- Lint every model card in the repository in one pass and export the dated audit as a file you keep: Markdown for the reviewer, JSON a CI step can fail on.
@readystack/model-card-lint-gpai --dir ./templates --report html --out report.html
An hour of an EU AI Act compliance consultant starts near $200; the Act's own ceiling for a GPAI provider is EUR 15,000,000 or 3% of worldwide annual turnover (Art. 101).
Use from an AI agent (MCP)
Claude Code · Cursor · Windsurf · any MCP client - add to your MCP config:
{ "mcpServers": { "model-card-lint-gpai": { "command": "npx", "args": ["-y", "@readystack/model-card-lint-gpai", "--mcp"] } } }
Tools: check_text and check_file (free) · check_dir (licence). The agent gets every finding with the line number.
Use in CI
- name: Model Card Lint - EU GPAI (AI Act Art. 53)
  run: npx -y @readystack/model-card-lint-gpai --dir . --ci
(container: docker run --rm -v "$PWD:/work" getreadystack/model-card-lint-gpai --dir /work --ci)
The folder sweep, reports and CI mode need one licence — one payment, no subscription. Set READYSTACK_LICENSE=<key> or run --license <key> once.
Install (PyPI)
pip install readystack-model-card-lint-gpai
model-card-lint-gpai --help
1 maintainer

Metadata
1 maintainer
Release files for readystack-model-card-lint-gpai 1.0.9.post1
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| readystack_model_card_lint_gpai-1.0.9.post1.tar.gz | 18.7 kB | Without provenance | Details for readystack_model_card_lint_gpai-1.0.9.post1.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| readystack_model_card_lint_gpai-1.0.9.post1-py3-none-any.whl | Python 3 | none | any | Details for readystack_model_card_lint_gpai-1.0.9.post1-py3-none-any.whl |
Total release size: 39.7 kB
Release files / readystack_model_card_lint_gpai-1.0.9.post1.tar.gz
| Download URL | readystack_model_card_lint_gpai-1.0.9.post1.tar.gz |
|---|---|
| Size | 18.7 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
17fdb67f78fbde637d323122564e6e00f63647288c4de5691a85ea27d33e5977
|
|
BLAKE2b-256 checksum How to use checksums |
6869fef63371460378bf4620b415440d7f4dc7899ae77ced112ed6459471536b
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/7.0.0 CPython/3.12.3
|
Release files / readystack_model_card_lint_gpai-1.0.9.post1-py3-none-any.whl
| Download URL | readystack_model_card_lint_gpai-1.0.9.post1-py3-none-any.whl |
|---|---|
| Size | 20.9 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
c71af70263d1ea65f86f229e40424395947efada22264a36871c4ba2752abef4
|
|
BLAKE2b-256 checksum How to use checksums |
71b8b52e8aab48e832e80bf00b53d060cee6ef4000f760504d99110ff61f5e08
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/7.0.0 CPython/3.12.3
|
Security for readystack-model-card-lint-gpai 1.0.9.post1
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














