
Reenact
Deterministic tests for LLM agents, and an eval cache that only pays for what a change touched.
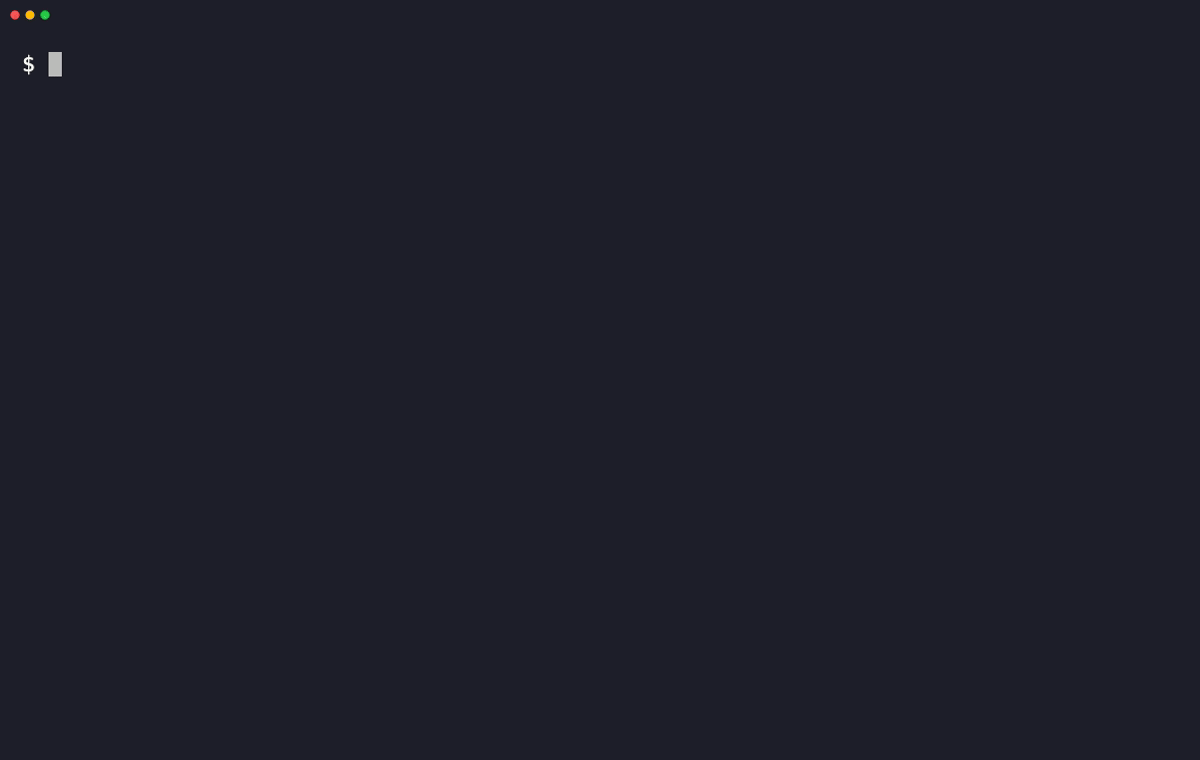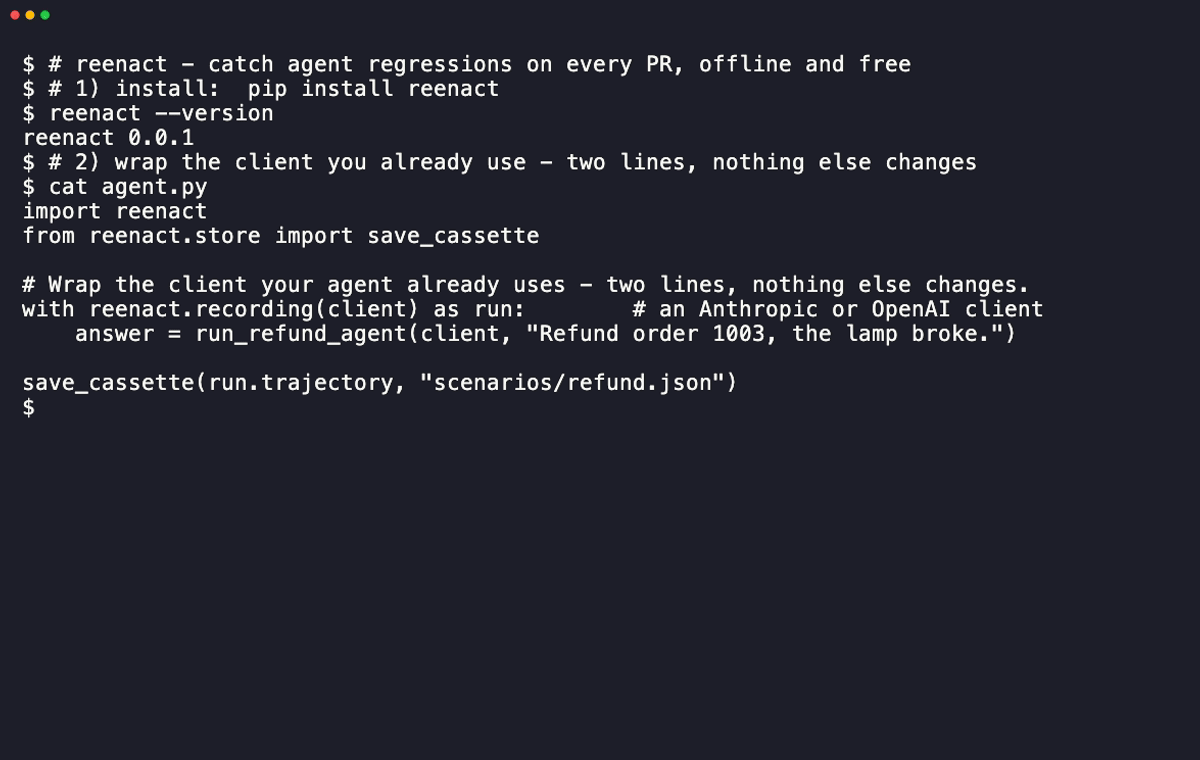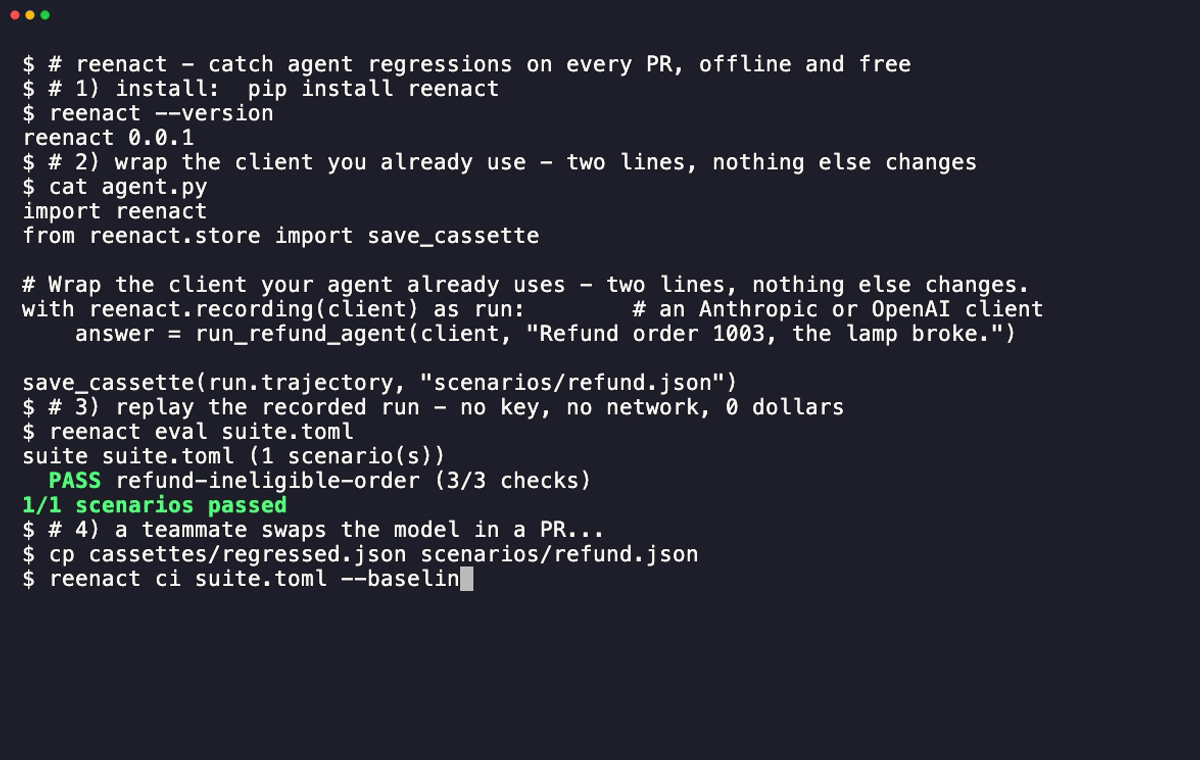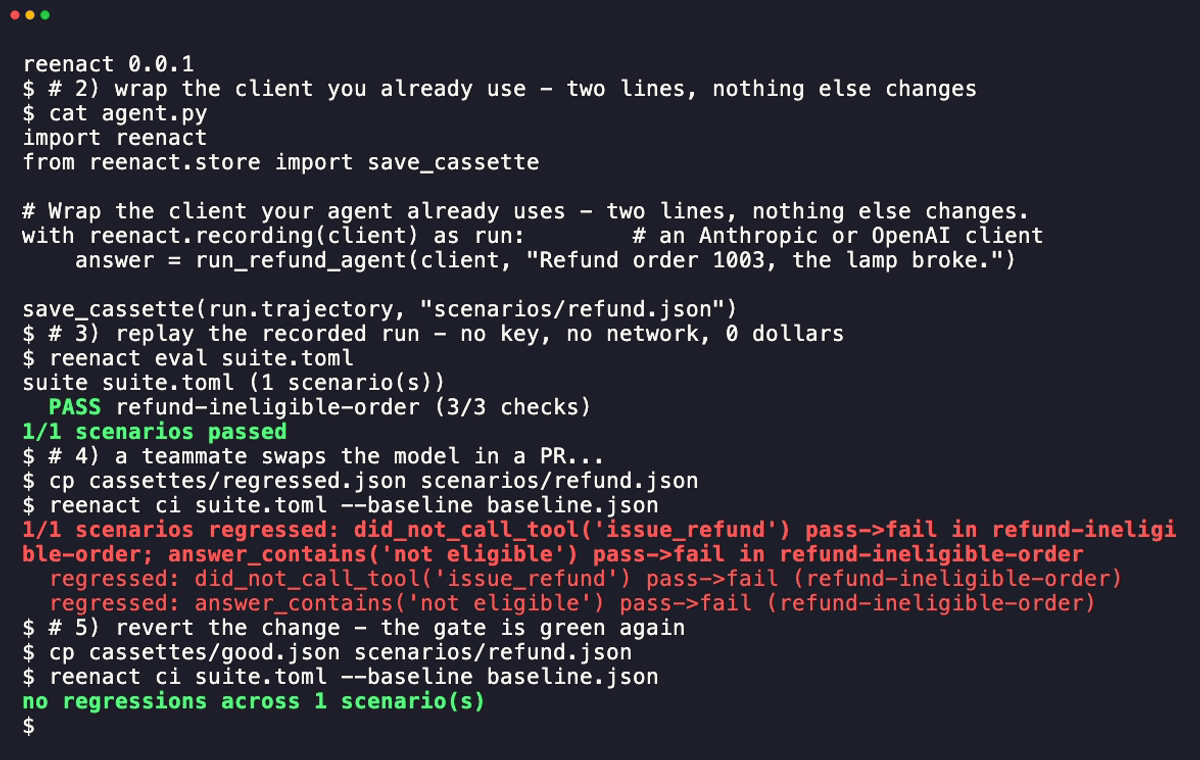
Reenact records a multi-step agent run once - every model call, tool call, and MCP
call - and keeps it as a test fixture. On every pull request, reenact check re-runs
the agent the pull request contains against those recordings, offline: the model's
responses come from the recording, while the requests, tool calls, and control flow
are the current code's own. When nothing the agent sends has changed, the test is
deterministic, free, and needs no API key. When something has, Reenact shows exactly
what changed - and can re-run just those scenarios against the real model.
Install
pip install reenact
reenact[langchain] adds LangChain and LangGraph support; reenact[anthropic] adds
the client that model-judged criteria use.
Quickstart
Write one entrypoint that runs your agent with its model client and tools taken from
rt; Reenact calls it both to record a scenario and to check it:
import reenact

def run(rt: reenact.Session, *, question: str) -> None:
    client = rt.anthropic()                       # records, or answers from the recording
    search = rt.tool(search_docs, side_effect="read_only")
    reply = rt.tool(post_reply, side_effect="mutating", stub=fake_post_reply)
    my_agent(client, tools=[search, reply], question=question)
Name it in a suite with each scenario's arguments, cassette, and checks, then:
reenact record evals/suite.toml    # run each scenario for real, write its cassette
reenact check evals/suite.toml     # re-run the current agent against them, offline
reenact init scaffolds the entrypoint, a suite skeleton, and a pull-request
workflow; reenact suggest drafts the checks from a recording.
What you get
- Tests of the agent's plumbing with the model frozen - $0, no API key.
- Request snapshots - a change to what the agent sends is reported field by field.
- Side-effect safety for every tool - a mutating tool never runs again on replay.
- A live re-run for what changed -
--on-divergence livere-runs only the scenarios whose requests changed against the real model, and gates on their checks. - Baseline-relative gating - fail only on drift, including a check deleted to go green; a GitHub Action posts a sticky comment and a merge-gating check-run.
Works with the Anthropic SDK, OpenAI SDK, LiteLLM, LangChain, and LangGraph.
Documentation
Full docs, the demo, and the GitHub Action: https://github.com/Manas-33/Reenact
License
MIT
1 maintainer

Metadata
1 maintainer
Release files for reenact 0.2.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| reenact-0.2.0.tar.gz | 350.8 kB | Without provenance | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| reenact-0.2.0-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 454.5 kB
Release files / reenact-0.2.0.tar.gz
| Download URL | reenact-0.2.0.tar.gz |
|---|---|
| Size | 350.8 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
12b06c474daa539a7d2e66e52732108948f73b4cc6385bfb873153cdd454a4a0
|
|
BLAKE2b-256 checksum How to use checksums |
e532dd11b20ad823fe9868af709ec49e2562eff24afd15e3df4e849dfc4cd0e2
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/7.0.0 CPython/3.12.12
|
Release files / reenact-0.2.0-py3-none-any.whl
| Download URL | reenact-0.2.0-py3-none-any.whl |
|---|---|
| Size | 103.8 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
83df9442adb6149d45edd423cf9ff8cec371b0f7b424e7a2be8c37ecb7e3cb36
|
|
BLAKE2b-256 checksum How to use checksums |
4a81144f6f723a16d99b0f3ac865362d747a479ca34ca354c3602546d5bbcdbf
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/7.0.0 CPython/3.12.12
|
Security for reenact 0.2.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














