


A Python CLI and pyproject.toml configuration that let you release Python packages multiple times a day with only 2-clicks. Designed for uv-based Python projects, but usable for other projects too. Every step is a CLI command: reusable GitHub Actions workflows are only the trigger, so the same automation runs on your machine.
Maintainer-in-the-loop: nothing is done behind your back. Every change repomatic proposes arrives as a PR you review; every action it needs from you opens an issue.
What it automates
- Version bumping, git tagging, and GitHub release creation
- Changelog management
- Python package building and PyPI publishing with supply chain attestations
- Cross-platform binary compilation (Linux / macOS / Windows, x86_64 / arm64)
- Formatting autofix for Python, Markdown, JSON, Shell, and typos
- Linting: Python code with ruff, Python types with mypy, YAML, shell scripts, GitHub Actions, workflow security, URLs, secrets, and Awesome lists
- Synchronization of
uv.lock, GitHub Action pins, workflow version literals, andrepomatic runtool versions with configurable stabilization cooldowns - Synchronization of
.gitignore,.mailmap, and Mermaid dependency graph - Label management with file-based and content-based rules
- Inactive issue locking
- Static image optimization
- Sphinx documentation building, deployment, and autodoc updates
- Awesome list template synchronization
Why repomatic
repomatic does for the release process what ruff did for linting and uv did for packaging: replace a stack of single-purpose tools with one.
- 23 third-party GitHub Actions replaced by internal CLI commands and SHA-256-verified binary downloads, keeping the supply chain attack surface minimal
- 10 Python linters and formatters (pylint, pydocstyle, pycln, pyupgrade, isort, black, docformatter, mdformat-black, blacken-docs, mdformat-ruff) consolidated into ruff
- 5 packaging and install tools (poetry, build, twine, check-wheel-contents, pip-audit) consolidated into uv
- All
uses:references pinned to full commit SHAs with stabilization windows before adopting new versions, managed entirely by self-hosted sync jobs - SLSA provenance attestations on every release artifact (wheels and compiled binaries)
- VirusTotal scanning of compiled binaries to seed AV vendor databases and reduce false positives
- Trusted Publishing for PyPI uploads: no long-lived tokens stored as secrets
- Immutable releases enforced via GitHub's tag protection and release locking
- Workflow security linting with
zizmoron every push to catch dangerous triggers and excessive permissions - Credential scanning with
gitleaksto prevent secret leakage - Single
pyproject.tomlconfiguration - The CLI itself ships as standalone binaries (Linux / macOS / Windows, x86_64 / arm64)
- 15+ code quality tools (ruff, mypy, biome, typos, mdformat, shfmt, yamllint, actionlint, lychee, oxipng, pyproject-fmt, labelmaker, gitleaks, zizmor, autopep8, awesome-lint, shellcheck) managed through one
repomatic run <tool>interface with automatic installation and platform-specific binary caching
Quick start
$ cd my-project
$ uvx -- repomatic init
$ git add .
$ git commit -m "Add repomatic"
$ git push
Works for new and existing repositories. Managed files are always regenerated to the latest version; changelog.md is never overwritten. Push, and the workflows guide you through remaining setup via issues and PRs.
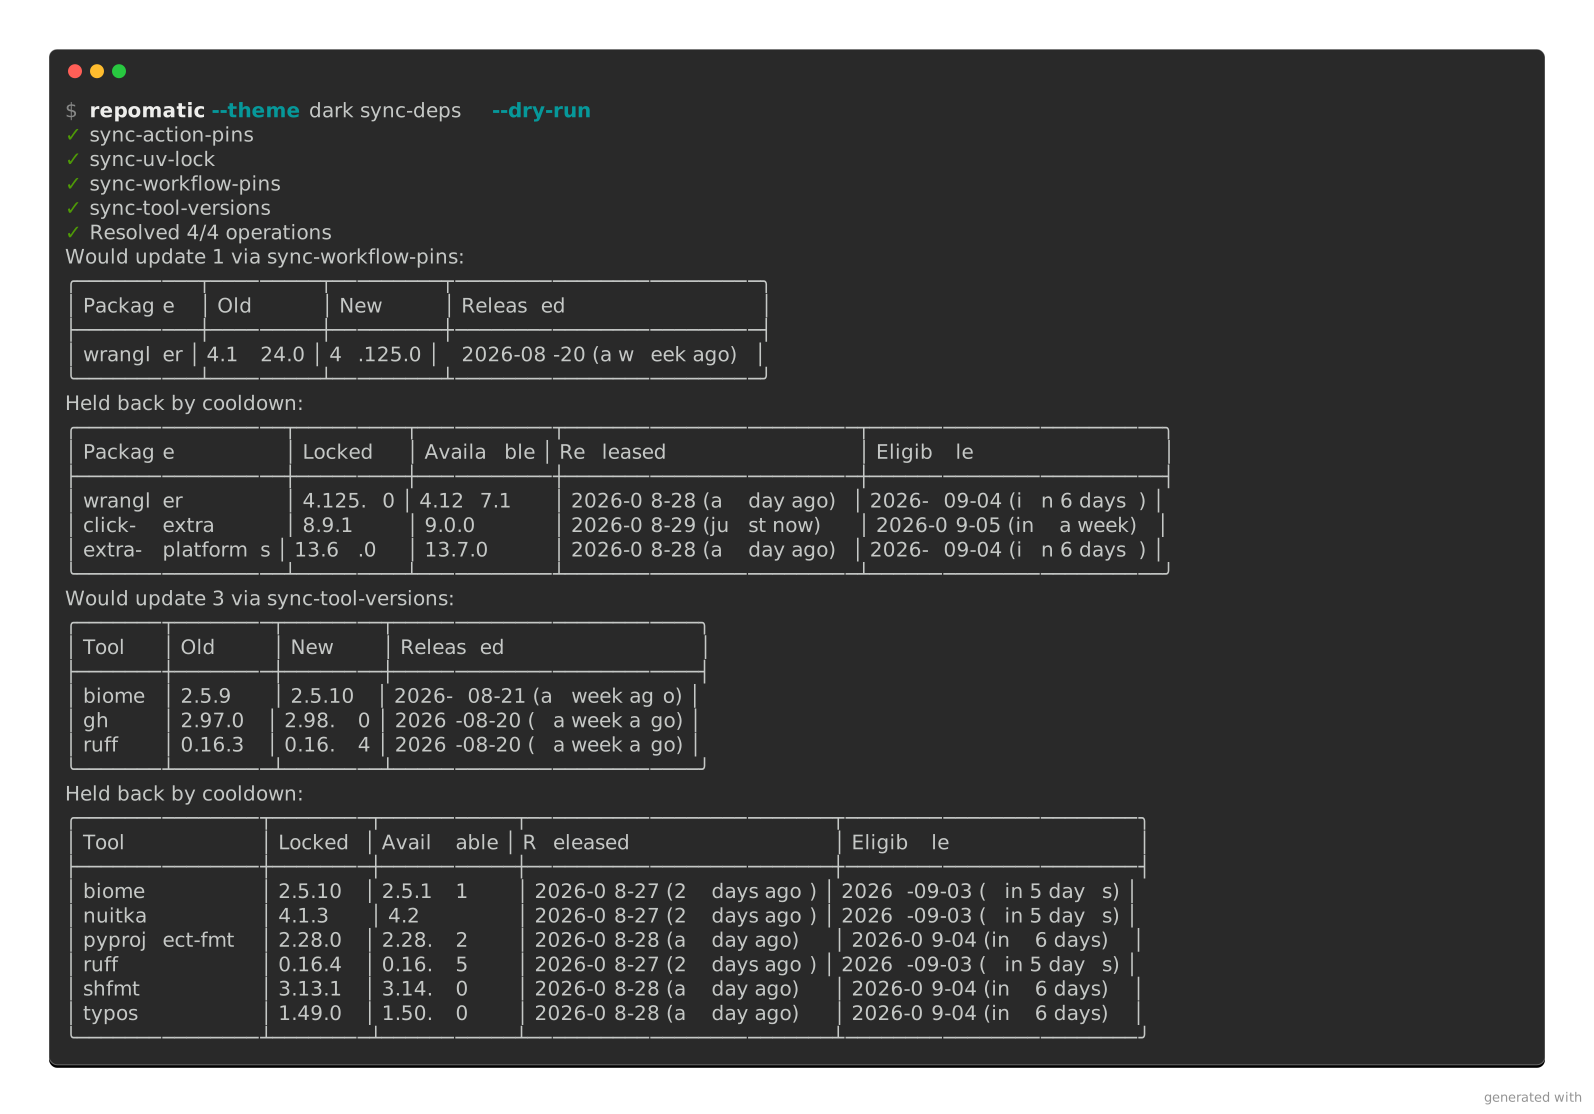
The workflows only call CLI commands, so every automated step can also be run and previewed locally:
$ uvx -- repomatic sync-deps --dry-run
$ uvx -- repomatic run ruff -- check
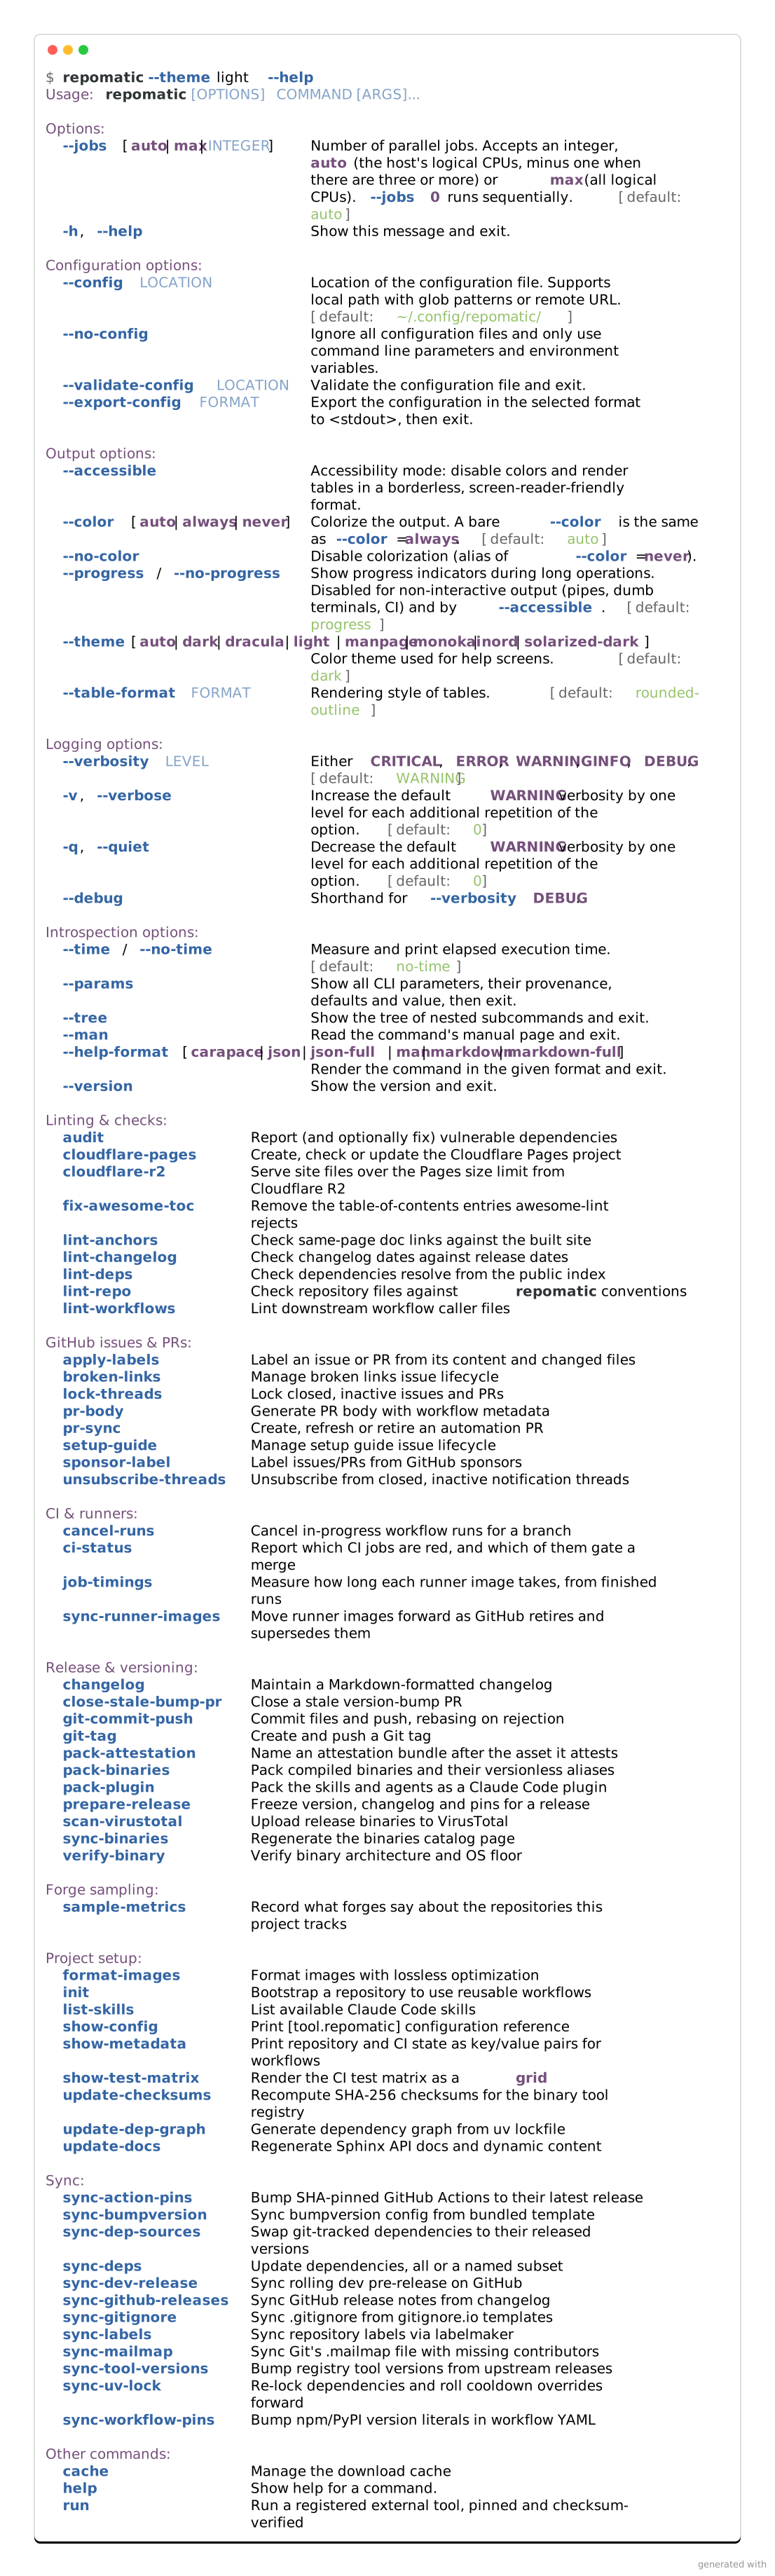
See repomatic init --help for available components and options.
Documentation
See the full documentation for:
- Installation methods and binaries
[tool.repomatic]configuration reference- CLI parameters
- Reusable workflow reference (all 15 workflows with job descriptions)
- Security practices and token setup
- Agent skills and subagents, also installable as a Claude Code plugin
- API reference
- Project history
Used in
Check these projects to get real-life examples of usage and inspiration:
Awesome Falsehood - Falsehoods Programmers Believe in.
Awesome Engineering Team Management - How to transition from software development to engineering management.
Awesome IAM - Identity and Access Management knowledge for cloud platforms.
Awesome Billing - Billing & Payments knowledge for cloud platforms.
Meta Package Manager - A unifying CLI for multiple package managers.
Mail Deduplicate - A CLI to deduplicate similar emails.
dotfiles - macOS dotfiles for Python developers.
Click Extra - Drop-in replacement for Click to make user-friendly and colorful CLI.
repomatic - Itself. Eat your own dog-food.
Plumage - Clean and tidy theme for Pelican, the static site generator.
Kevin Deldycke's blog - My personal blog, based on Pelican.
Extra Platforms - Detect architectures, platforms, shells, terminals, CI systems and agents, grouped by family.
GitHub profile - My GitHub profile page and short bio.
Send a PR to add your project if you use repomatic.
1 maintainer

Metadata
1 maintainer
Release files for repomatic 8.3.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| repomatic-8.3.0.tar.gz | 3.6 MB | With provenance | Details for repomatic-8.3.0.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| repomatic-8.3.0-py3-none-any.whl | Python 3 | none | any | Details for repomatic-8.3.0-py3-none-any.whl |
Total release size: 4.9 MB
Release files / repomatic-8.3.0.tar.gz
| Download URL | repomatic-8.3.0.tar.gz |
|---|---|
| Size | 3.6 MB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
2ebcbde8ab7d382172f3594531c500f43dd1e95080011ef4c1162cd5c65e25b6
|
|
BLAKE2b-256 checksum How to use checksums |
099e88937de3aa3a6037c3c8d69d1cfc5686e11fa49d6b34c9db0153a0f62441
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
uv/0.13.6 {"installer":{"name":"uv","version":"0.13.6","subcommand":["publish"]},"python":null,"implementation":{"name":null,"version":null},"distro":{"name":"Ubuntu","version":"26.04","id":"resolute","libc":null},"system":{"name":null,"release":null},"cpu":null,"openssl_version":null,"setuptools_version":null,"rustc_version":null,"ci":true}
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 17, 2026.
Transparency logRelease files / repomatic-8.3.0-py3-none-any.whl
| Download URL | repomatic-8.3.0-py3-none-any.whl |
|---|---|
| Size | 1.3 MB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
c0c0c868c79aead06d56189152fd87bd602d18783657c917513b1a5683f79c91
|
|
BLAKE2b-256 checksum How to use checksums |
228d69d94cd8b93523b1afa023e43030169a89cb0ecea8abae1055be903e2333
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
uv/0.13.6 {"installer":{"name":"uv","version":"0.13.6","subcommand":["publish"]},"python":null,"implementation":{"name":null,"version":null},"distro":{"name":"Ubuntu","version":"26.04","id":"resolute","libc":null},"system":{"name":null,"release":null},"cpu":null,"openssl_version":null,"setuptools_version":null,"rustc_version":null,"ci":true}
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 17, 2026.
Transparency logSecurity for repomatic 8.3.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
Both files in this release have been uploaded with provenance metadata.
Attestation for repomatic-8.3.0.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 17, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














