
Auditor IBS/CBS para NF-e — NT 2025.002
Runs the same checker as our npm package on a Node.js runtime that pip installs for you (
nodejs-wheel-binaries) - no system Node.js needed. Your files are checked locally.
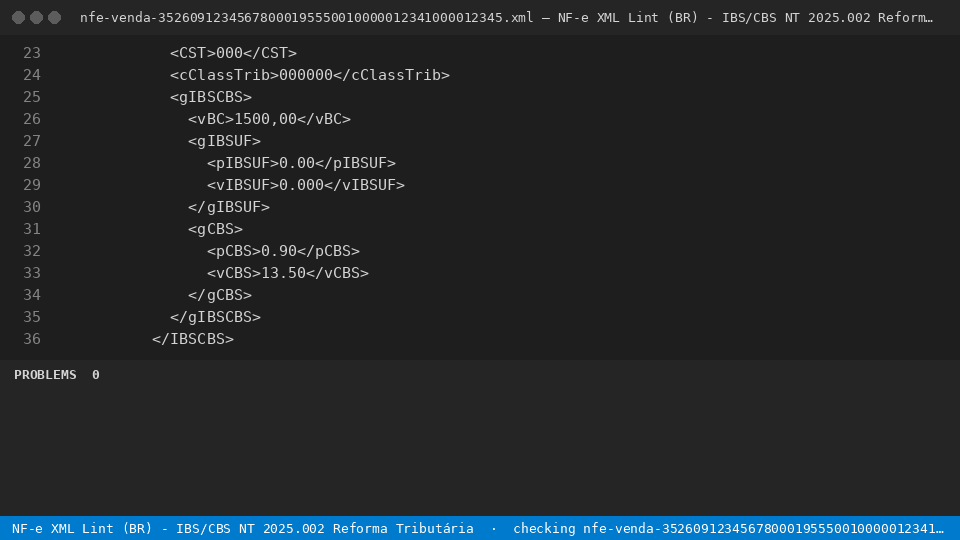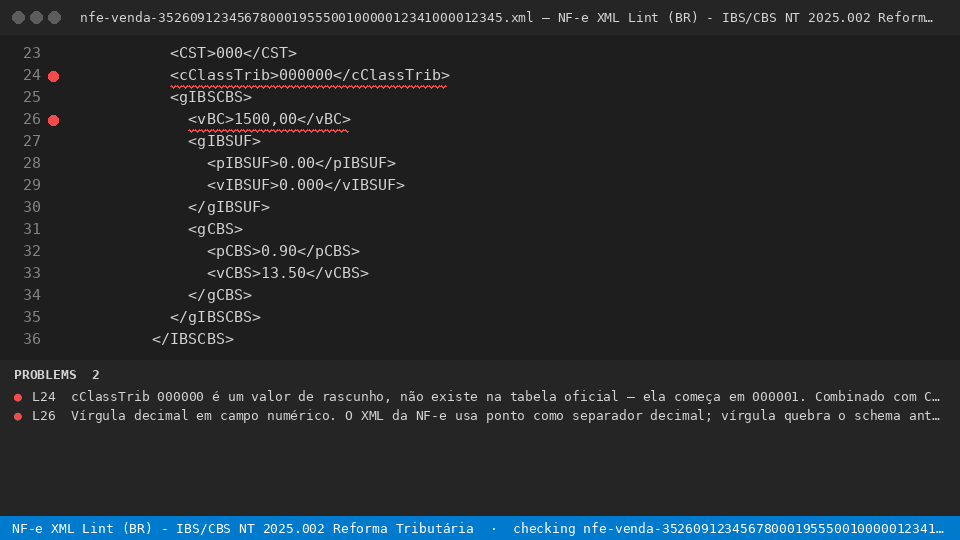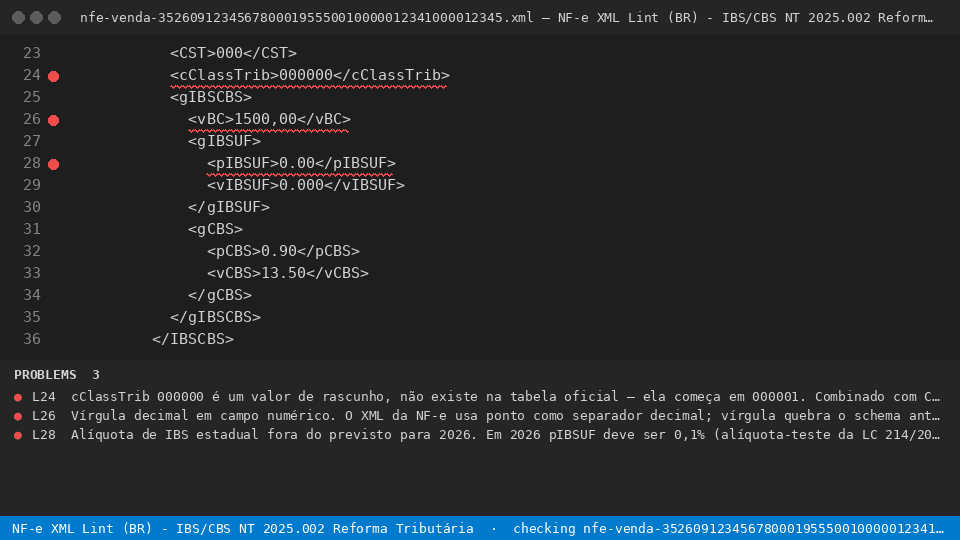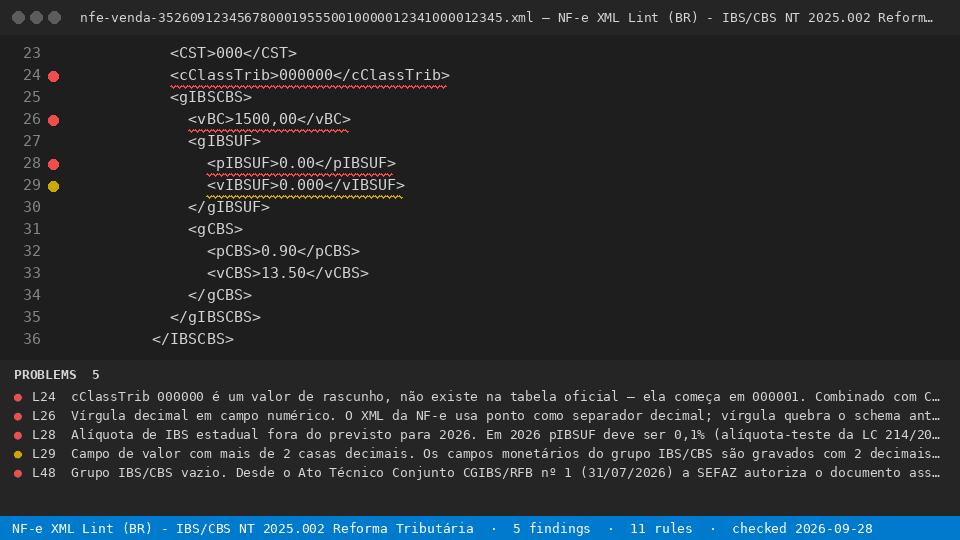
A rejeição por falta de IBS/CBS foi suspensa em 31/07/2026: sua NF-e é autorizada mesmo errada. Este auditor lê o XML no editor e aponta o que a SEFAZ deixou passar.
Install
auditor-ibs-cbs-nfe file
Node 18+. The same 11 rules as the VS Code extension, from a terminal or CI.
Free
- Audita um XML de NF-e inteiro no editor, offline, com as 11 regras da NT 2025.002 e mostra linha, problema e correção.
--ruleslists every rule
With a licence ($29 once)
- Audita todos os XMLs do workspace de uma vez, exporta o laudo em CSV/JSON/HTML e devolve saída JSON para o CI.
auditor-ibs-cbs-nfe --dir ./templates --report html --out report.html
Assinaturas de apoio à Reforma Tributária para times fiscais partem de R$ 147/mês; esta licença é paga uma única vez.
Use from an AI agent (MCP)
Claude Code · Cursor · Windsurf · any MCP client - add to your MCP config:
{ "mcpServers": { "auditor-ibs-cbs-nfe": { "command": "auditor-ibs-cbs-nfe", "args": ["--mcp"] } } }
Tools: check_text and check_file (free) · check_dir (licence). The agent gets every finding with the line number.
Use in CI
- name: Auditor IBS/CBS para NF-e — NT 2025.002
  run: pip install rulestamp-auditor-ibs-cbs-nfe && auditor-ibs-cbs-nfe --dir . --ci
The folder sweep, reports and CI mode need one licence — one payment, no subscription. Set READYSTACK_LICENSE=<key> or run --license <key> once.
Install (PyPI)
pip install rulestamp-auditor-ibs-cbs-nfe
auditor-ibs-cbs-nfe --help
1 maintainer

Metadata
1 maintainer
Release files for rulestamp-auditor-ibs-cbs-nfe 0.1.8
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| rulestamp_auditor_ibs_cbs_nfe-0.1.8.tar.gz | 14.2 kB | Without provenance | Details for rulestamp_auditor_ibs_cbs_nfe-0.1.8.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| rulestamp_auditor_ibs_cbs_nfe-0.1.8-py3-none-any.whl | Python 3 | none | any | Details for rulestamp_auditor_ibs_cbs_nfe-0.1.8-py3-none-any.whl |
Total release size: 29.9 kB
Release files / rulestamp_auditor_ibs_cbs_nfe-0.1.8.tar.gz
| Download URL | rulestamp_auditor_ibs_cbs_nfe-0.1.8.tar.gz |
|---|---|
| Size | 14.2 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
ba1feeb8a92444563a25da725c9a6358de76075bbabfaf0d745d0e2c132538ab
|
|
BLAKE2b-256 checksum How to use checksums |
9bbf6464275e61b8750c629b09b1856d73c2af23dcff6be41034d0a6eb624995
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/7.0.0 CPython/3.12.3
|
Release files / rulestamp_auditor_ibs_cbs_nfe-0.1.8-py3-none-any.whl
| Download URL | rulestamp_auditor_ibs_cbs_nfe-0.1.8-py3-none-any.whl |
|---|---|
| Size | 15.7 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
42931ffdcc44cf370fe142776e0d0537a1e5113a8741fc92f3ffa6244625dcb5
|
|
BLAKE2b-256 checksum How to use checksums |
ae26f2cc1da50f098f0fd33910272d6d6a2fa52d7299ec5a7dd7c0e6e2a31778
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/7.0.0 CPython/3.12.3
|
Security for rulestamp-auditor-ibs-cbs-nfe 0.1.8
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.













