
AVV-Prüfer – Auftragsverarbeitungsvertrag Lint
Runs the same checker as our npm package on a Node.js runtime that pip installs for you (
nodejs-wheel-binaries) - no system Node.js needed. Your files are checked locally.
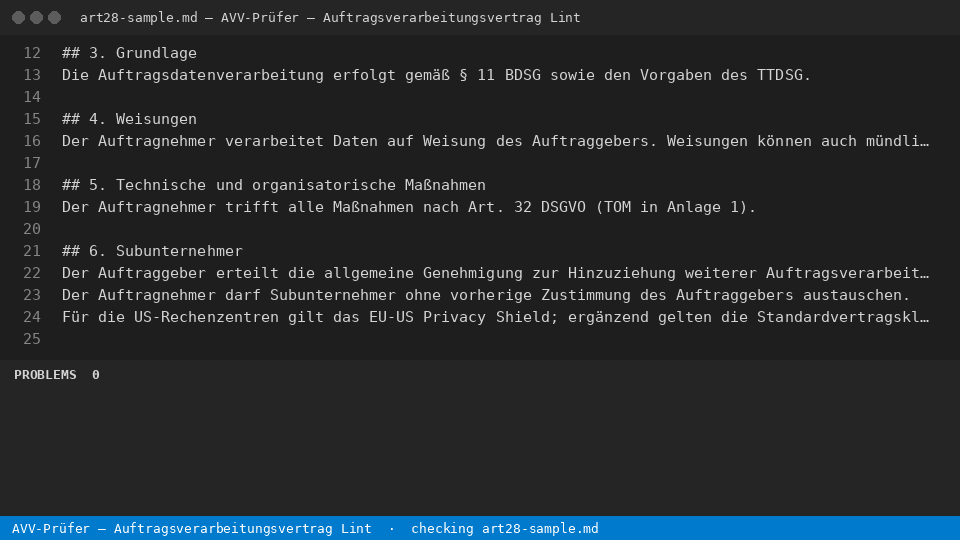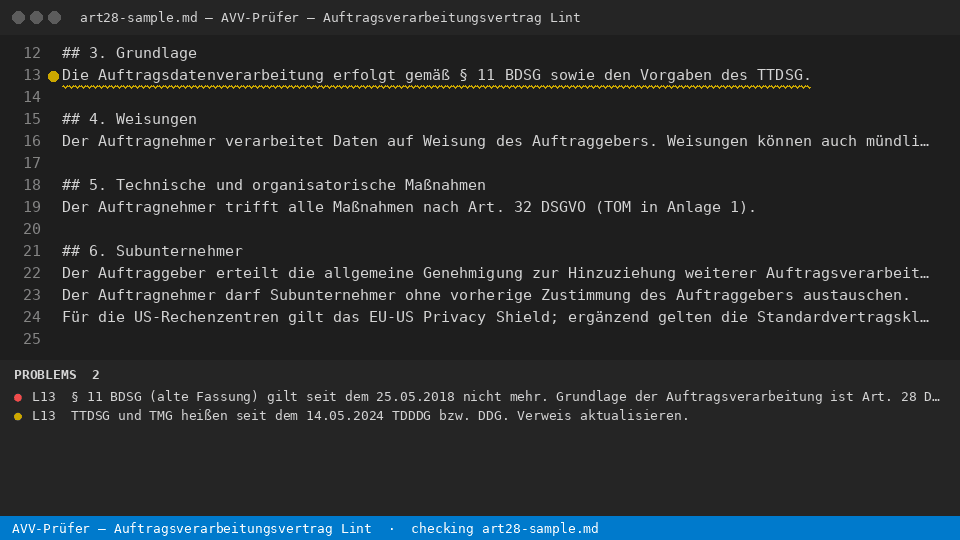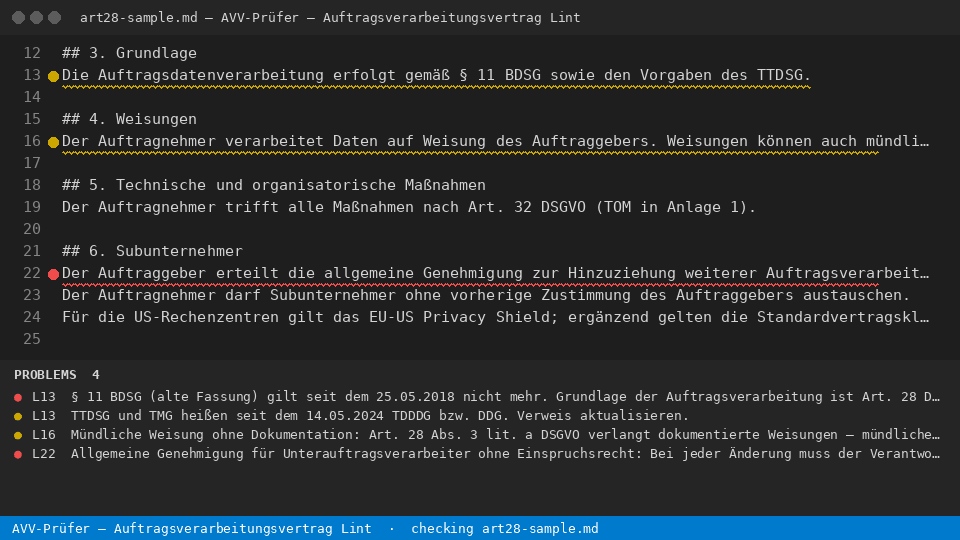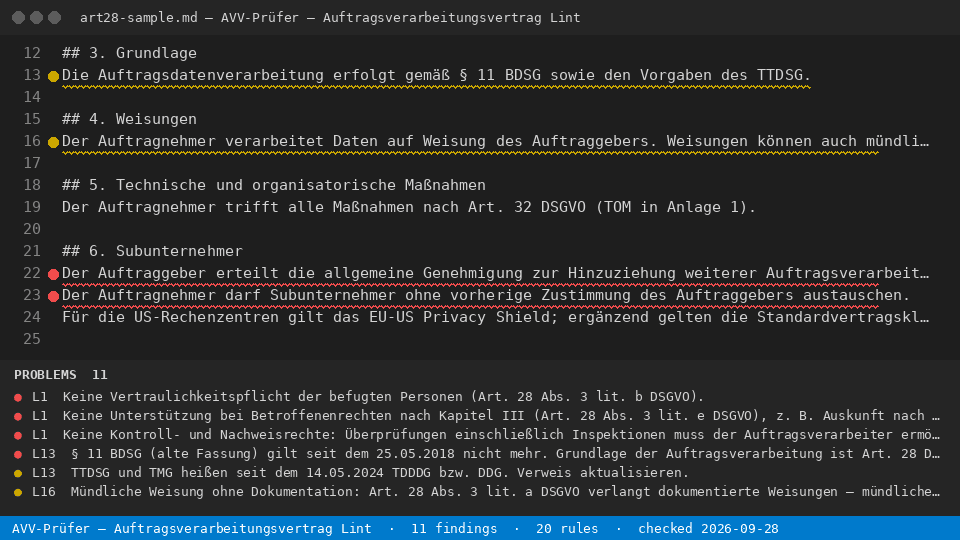
Auftragsverarbeitungsvertrag Check für Markdown-AVVs: 20 Regeln zu Art. 28 Abs. 2 und 3 und Art. 33 Abs. 2 DSGVO, direkt in VS Code und im Browser.
Install
avv-pruefer-art28-lint file
Node 18+. The same 20 rules as the VS Code extension, from a terminal or CI.
Free
- Prüft jeden offenen AVV (.md) mit allen 20 Regeln, ohne Key, in VS Code und im Browser. Der Beispiel-AVV liefert 11 Befunde: § 11 BDSG und TTDSG als Grundlage, mündliche Weisungen, Subunternehmer ohne vorherige Zustimmung, allgemeine Genehmigung ohne Einspruchsrecht, Privacy Shield, SCC 2010/87/EU, Meldung innerhalb von 72 Stunden, fehlende Vertraulichkeit, fehlende Betroffenenrechte und fehlende Kontrollrechte.
--ruleslists every rule
With a licence ($29 once)
- $29 einmalig: Ordner-Prüfbericht über alle AVVs eines Workspace als Datei, als Nachweis für Kunden-Audits und die Dokumentation nach Art. 5 Abs. 2 DSGVO. Ein Lizenzschlüssel pro Person oder Team-Platz.
avv-pruefer-art28-lint --dir ./templates --report html --out report.html
Anwalt nach RVG: 1,3 Geschäftsgebühr (Nr. 2300 VV) bei €5.000 Gegenstandswert = €480,85 netto (Tabelle § 13 RVG).
Use from an AI agent (MCP)
Claude Code · Cursor · Windsurf · any MCP client - add to your MCP config:
{ "mcpServers": { "avv-pruefer-art28-lint": { "command": "avv-pruefer-art28-lint", "args": ["--mcp"] } } }
Tools: check_text and check_file (free) · check_dir (licence). The agent gets every finding with the line number.
Use in CI
- name: AVV-Prüfer – Auftragsverarbeitungsvertrag Lint
  run: pip install rulestamp-avv-pruefer-art28-lint && avv-pruefer-art28-lint --dir . --ci
The folder sweep, reports and CI mode need one licence — one payment, no subscription. Set READYSTACK_LICENSE=<key> or run --license <key> once.
Install (PyPI)
pip install rulestamp-avv-pruefer-art28-lint
avv-pruefer-art28-lint --help
1 maintainer

Metadata
1 maintainer
Release files for rulestamp-avv-pruefer-art28-lint 1.0.3
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| rulestamp_avv_pruefer_art28_lint-1.0.3.tar.gz | 16.2 kB | Without provenance | Details for rulestamp_avv_pruefer_art28_lint-1.0.3.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| rulestamp_avv_pruefer_art28_lint-1.0.3-py3-none-any.whl | Python 3 | none | any | Details for rulestamp_avv_pruefer_art28_lint-1.0.3-py3-none-any.whl |
Total release size: 34.5 kB
Release files / rulestamp_avv_pruefer_art28_lint-1.0.3.tar.gz
| Download URL | rulestamp_avv_pruefer_art28_lint-1.0.3.tar.gz |
|---|---|
| Size | 16.2 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
1eea43600b26810c625ecaa3dbb9f55d272b02a82b6d769491ebee0f56d8cc3b
|
|
BLAKE2b-256 checksum How to use checksums |
6c2664ffc96e39643029f286c84fdd9a177ae0ddbf2cb9ad68a264dbadda383d
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/7.0.0 CPython/3.12.3
|
Release files / rulestamp_avv_pruefer_art28_lint-1.0.3-py3-none-any.whl
| Download URL | rulestamp_avv_pruefer_art28_lint-1.0.3-py3-none-any.whl |
|---|---|
| Size | 18.3 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
f98e255e2df4fb4b1dd1fb9dbbe1defad41af50d4db959baea09066dc65d7718
|
|
BLAKE2b-256 checksum How to use checksums |
2eded09bfe3d4ce9d0979d556b8604db942b66c46275e36f4560c3102716a21c
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/7.0.0 CPython/3.12.3
|
Security for rulestamp-avv-pruefer-art28-lint 1.0.3
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.













