
Canal de Denuncias Lint — Ley 2/2023 (ES)
Runs the same checker as our npm package on a Node.js runtime that pip installs for you (
nodejs-wheel-binaries) - no system Node.js needed. Your files are checked locally.
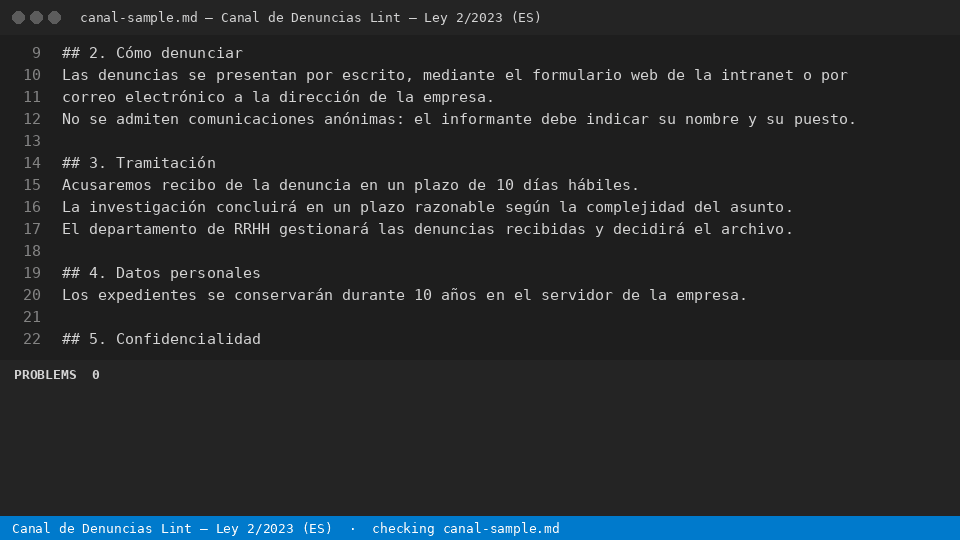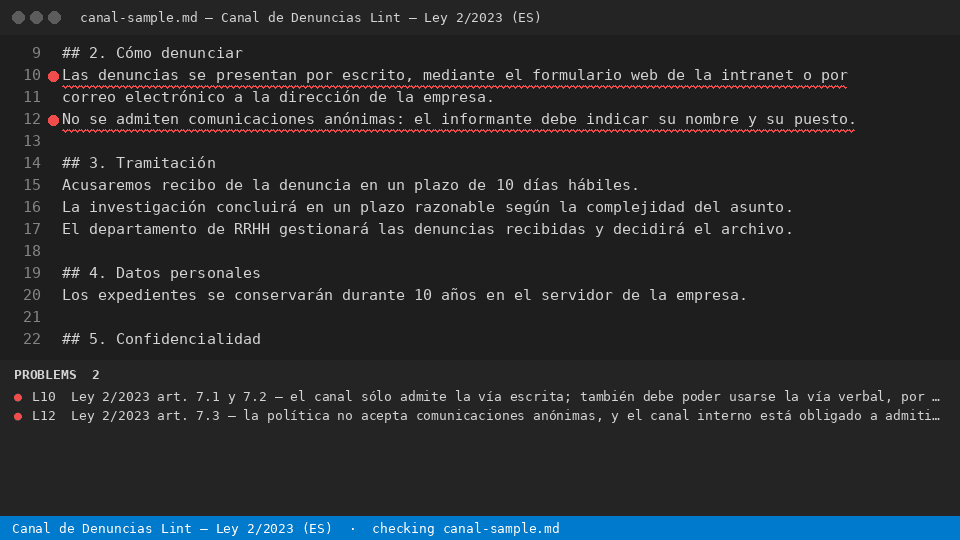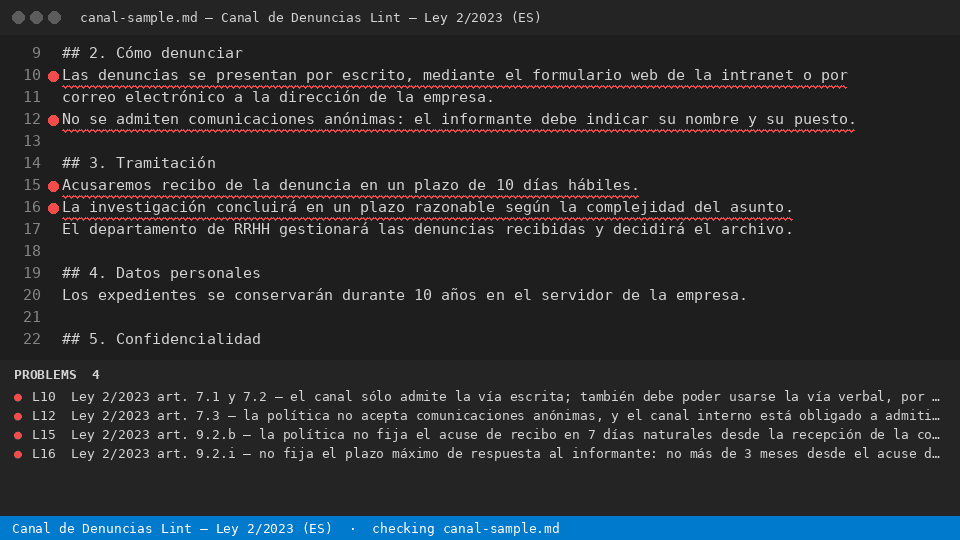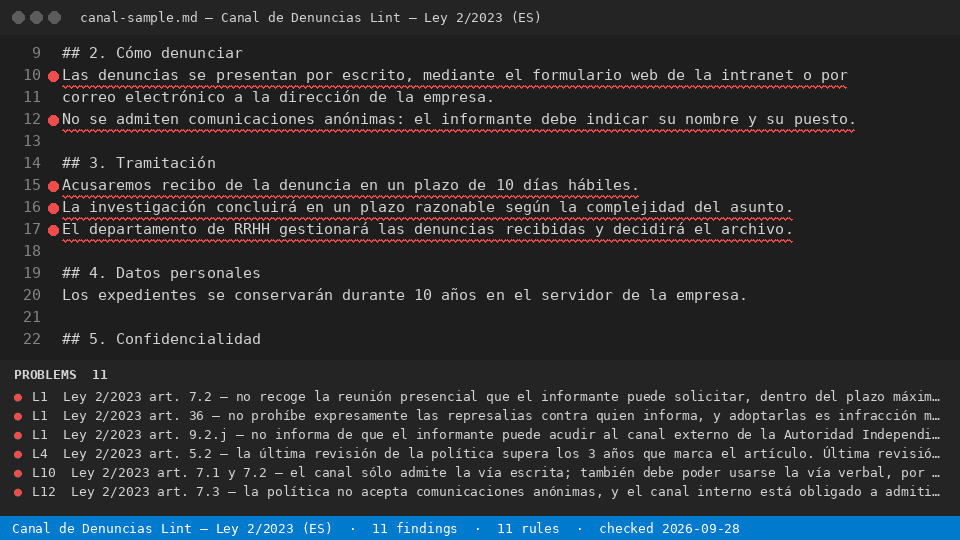
Revisa la política de tu canal interno de denuncias, artículo por artículo
Install
canal-de-denuncias-lint-es file
Node 18+. The same 11 rules as the VS Code extension, from a terminal or CI.
Free
- Aplica las 11 reglas de la Ley 2/2023 al documento de política que tienes abierto y nombra cada requisito que falta, con su artículo y su línea. El ejemplo incompleto incluido devuelve 11 hallazgos: 10 errores y 1 aviso. Las reglas: acuse en 7 días, respuesta en 3 meses, comunicaciones anónimas, vía verbal, reunión presencial, Responsable del Sistema, libro-registro, supresión a los 3 meses, prohibición de represalias, canal externo de la A.A.I. y revisión cada 3 años.
--ruleslists every rule
With a licence ($29 once)
- Revisa de una vez todos los documentos de política del espacio de trabajo —matriz, filiales, versiones por centro— y escribe un informe fechado que te llevas y entregas al auditor. $29 una vez.
canal-de-denuncias-lint-es --dir ./templates --report html --out report.html
Implantar el canal con una consultoría de compliance cuesta entre 1.500 € y 5.000 €.
Use from an AI agent (MCP)
Claude Code · Cursor · Windsurf · any MCP client - add to your MCP config:
{ "mcpServers": { "canal-de-denuncias-lint-es": { "command": "canal-de-denuncias-lint-es", "args": ["--mcp"] } } }
Tools: check_text and check_file (free) · check_dir (licence). The agent gets every finding with the line number.
Use in CI
- name: Canal de Denuncias Lint — Ley 2/2023 (ES)
  run: pip install rulestamp-canal-de-denuncias-lint-es && canal-de-denuncias-lint-es --dir . --ci
The folder sweep, reports and CI mode need one licence — one payment, no subscription. Set READYSTACK_LICENSE=<key> or run --license <key> once.
Install (PyPI)
pip install rulestamp-canal-de-denuncias-lint-es
canal-de-denuncias-lint-es --help
1 maintainer

Metadata
1 maintainer
Release files for rulestamp-canal-de-denuncias-lint-es 1.0.6
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| rulestamp_canal_de_denuncias_lint_es-1.0.6.tar.gz | 16.3 kB | Without provenance | Details for rulestamp_canal_de_denuncias_lint_es-1.0.6.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| rulestamp_canal_de_denuncias_lint_es-1.0.6-py3-none-any.whl | Python 3 | none | any | Details for rulestamp_canal_de_denuncias_lint_es-1.0.6-py3-none-any.whl |
Total release size: 34.8 kB
Release files / rulestamp_canal_de_denuncias_lint_es-1.0.6.tar.gz
| Download URL | rulestamp_canal_de_denuncias_lint_es-1.0.6.tar.gz |
|---|---|
| Size | 16.3 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
c72716e9d81f8537f88a2aabcdd1b171b8ed594e9195a2f136d94875dbe282b1
|
|
BLAKE2b-256 checksum How to use checksums |
6b5a046f28ae10927464ca262d6f38d5c07879c60b9138097bd7c538624f7254
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/7.0.0 CPython/3.12.3
|
Release files / rulestamp_canal_de_denuncias_lint_es-1.0.6-py3-none-any.whl
| Download URL | rulestamp_canal_de_denuncias_lint_es-1.0.6-py3-none-any.whl |
|---|---|
| Size | 18.4 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
d1324299363fb9e75d6120f9e3a4d1d28f21a04f3fce17bcad5cb46b4d84e206
|
|
BLAKE2b-256 checksum How to use checksums |
a4b2f3c7e2680df4ef6b67f26bfd9ae2f3d2f37e1fe1ffc9114d2831a1c5181a
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/7.0.0 CPython/3.12.3
|
Security for rulestamp-canal-de-denuncias-lint-es 1.0.6
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.













