
Dependency Checker — EOL Dates
Runs the same checker as our npm package on a Node.js runtime that pip installs for you (
nodejs-wheel-binaries) - no system Node.js needed. Your files are checked locally.
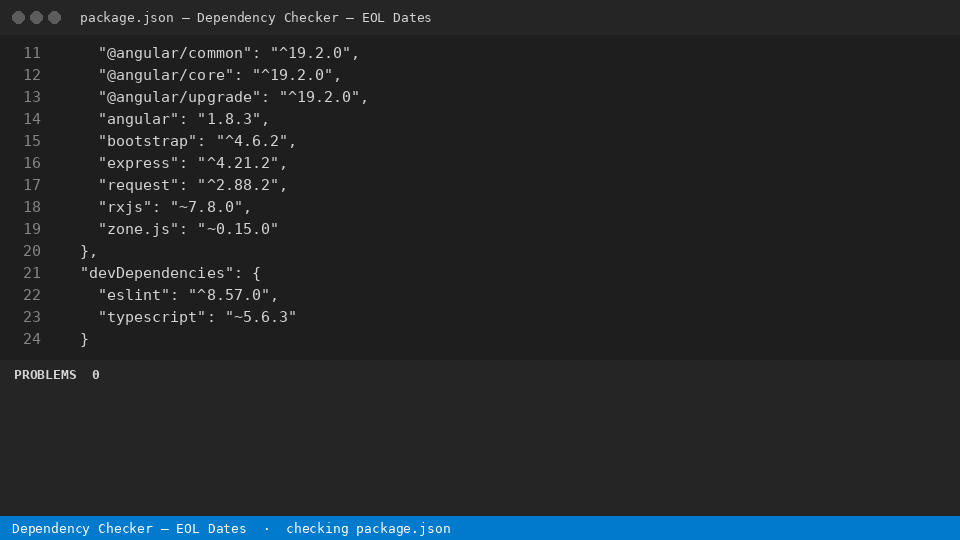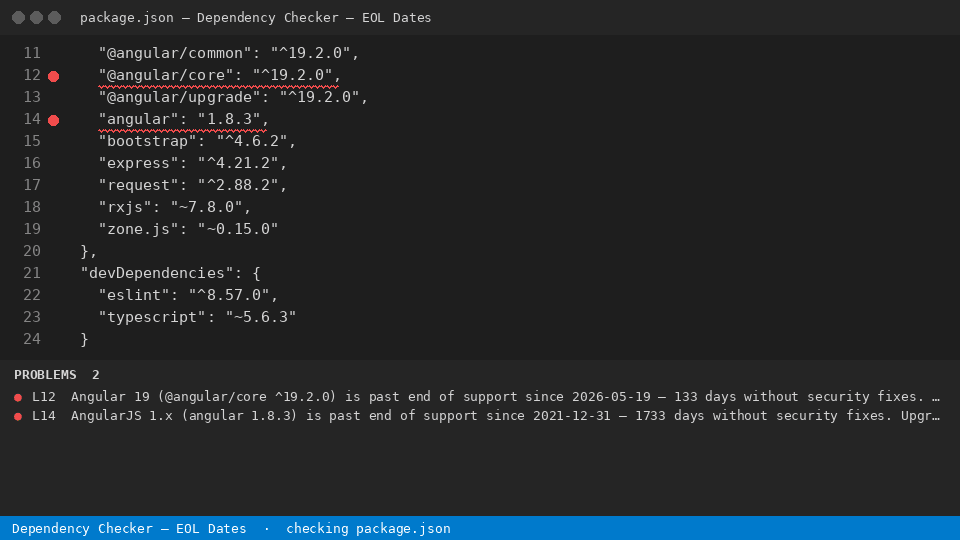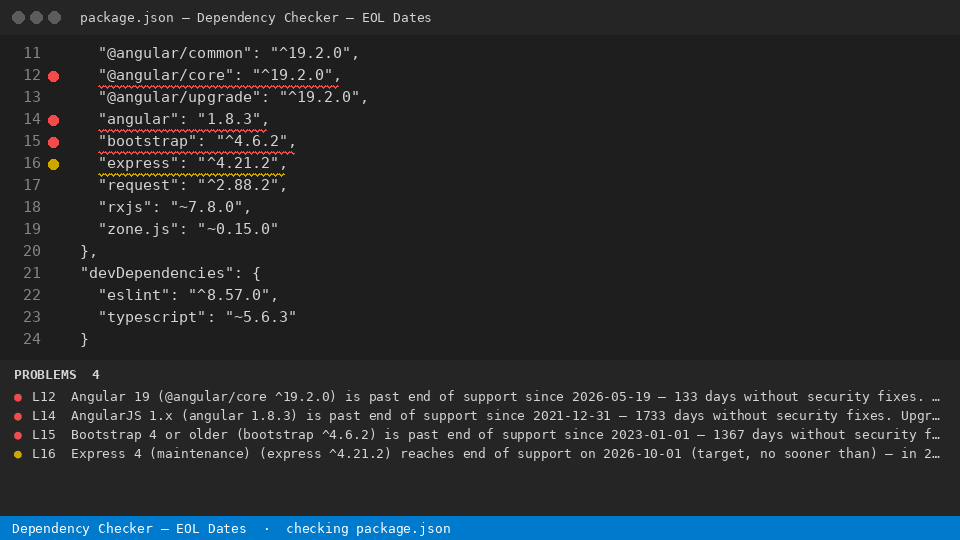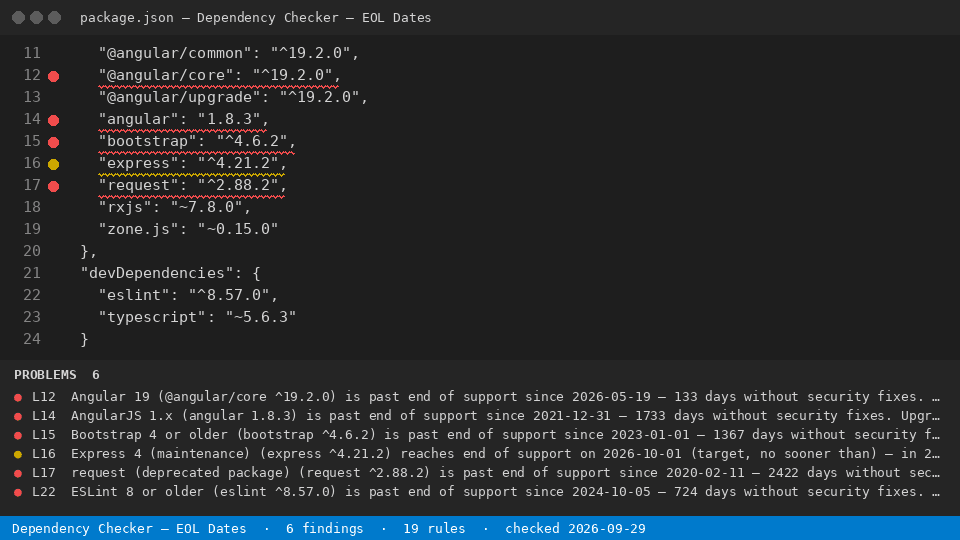
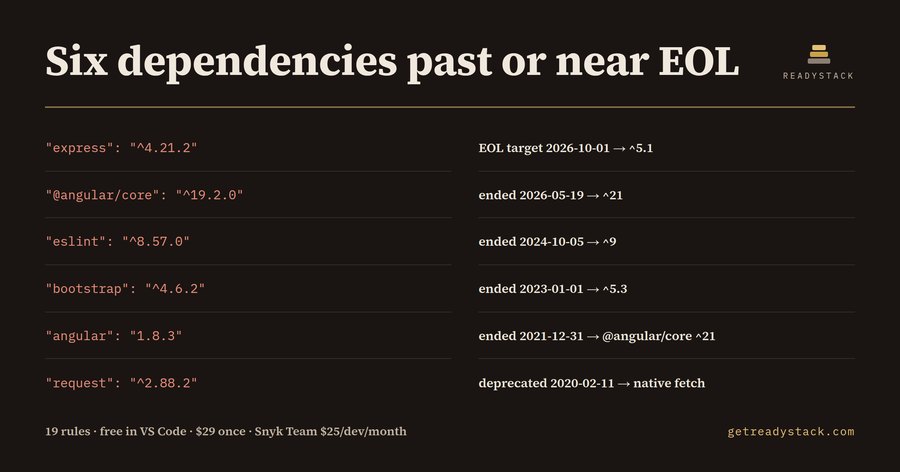
Dependency checker for package.json, composer.json and requirements.txt. On the sample package.json (Angular 19 + Express API, _fixtures/dirty.json) checked on 2026-09-28 it finds six dependencies past or near end of support: express ^4.21.2 (EOL target 2026-10-01), @angular/core ^19.2.0 (ended 2026-05-19), eslint ^8.57.0 (ended 2024-10-05), bootstrap ^4.6.2 (ended 2023-01-01), angular 1.8.3 (ended 2021-12-31), request ^2.88.2 (deprecated 2020-02-11).
Install
dependency-checker-eol-dates file
Node 18+. The same 19 rules as the VS Code extension, from a terminal or CI.
Free
- Checks the open manifest and lists every pinned framework major that is past or within 120 days of its end-of-support date, with the date and the upgrade target.
--ruleslists every rule
With a licence ($29 once)
- Scans every package.json, composer.json and requirements file in the workspace at once and exports one dated EOL report (CSV + Markdown) for a client or audit.
dependency-checker-eol-dates --dir ./templates --report html --out report.html
Snyk Team is listed at $25 per contributing developer per month ($300 a year each); this is $29 once.
Use from an AI agent (MCP)
Claude Code · Cursor · Windsurf · any MCP client - add to your MCP config:
{ "mcpServers": { "dependency-checker-eol-dates": { "command": "dependency-checker-eol-dates", "args": ["--mcp"] } } }
Tools: check_text and check_file (free) · check_dir (licence). The agent gets every finding with the line number.
Use in CI
- name: Dependency Checker — EOL Dates
  run: pip install rulestamp-dependency-checker-eol-dates && dependency-checker-eol-dates --dir . --ci
The folder sweep, reports and CI mode need one licence — one payment, no subscription. Set READYSTACK_LICENSE=<key> or run --license <key> once.
Install (PyPI)
pip install rulestamp-dependency-checker-eol-dates
dependency-checker-eol-dates --help
1 maintainer

Metadata
1 maintainer
Release files for rulestamp-dependency-checker-eol-dates 1.0.1
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| rulestamp_dependency_checker_eol_dates-1.0.1.tar.gz | 15.8 kB | Without provenance | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| rulestamp_dependency_checker_eol_dates-1.0.1-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 34.1 kB
Release files / rulestamp_dependency_checker_eol_dates-1.0.1.tar.gz
| Download URL | rulestamp_dependency_checker_eol_dates-1.0.1.tar.gz |
|---|---|
| Size | 15.8 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
5d58854eb5fcef11443c48a0213d1f99dced9cd3e0258875d751850bcaa00228
|
|
BLAKE2b-256 checksum How to use checksums |
47931d7a1e31eb9b68f17bd0f0b7d8dee65024f48021ade7391c47e4a48901e9
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/7.0.0 CPython/3.12.3
|
Release files / rulestamp_dependency_checker_eol_dates-1.0.1-py3-none-any.whl
| Download URL | rulestamp_dependency_checker_eol_dates-1.0.1-py3-none-any.whl |
|---|---|
| Size | 18.2 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
74a4dcc9a2421feab55c043641196188aa268e47d40f1f01eb26af6070998b26
|
|
BLAKE2b-256 checksum How to use checksums |
b6d222f9ce6aaa83fe3c09b587d5345088d5abb8db83f779a650980b4605cebd
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/7.0.0 CPython/3.12.3
|
Security for rulestamp-dependency-checker-eol-dates 1.0.1
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.













