
Green Claim Lint - EU EmpCo 2026
Runs the same checker as our npm package on a Node.js runtime that pip installs for you (
nodejs-wheel-binaries) - no system Node.js needed. Your files are checked locally.
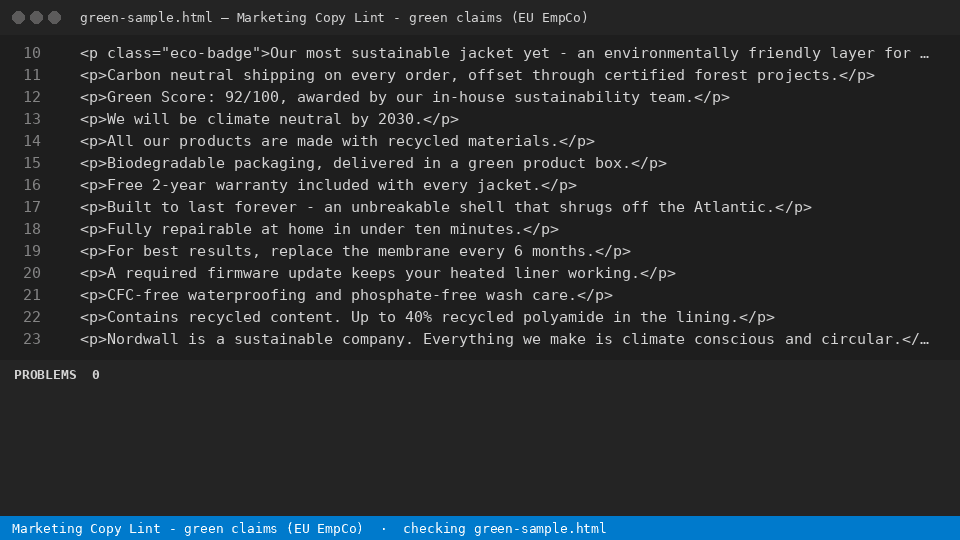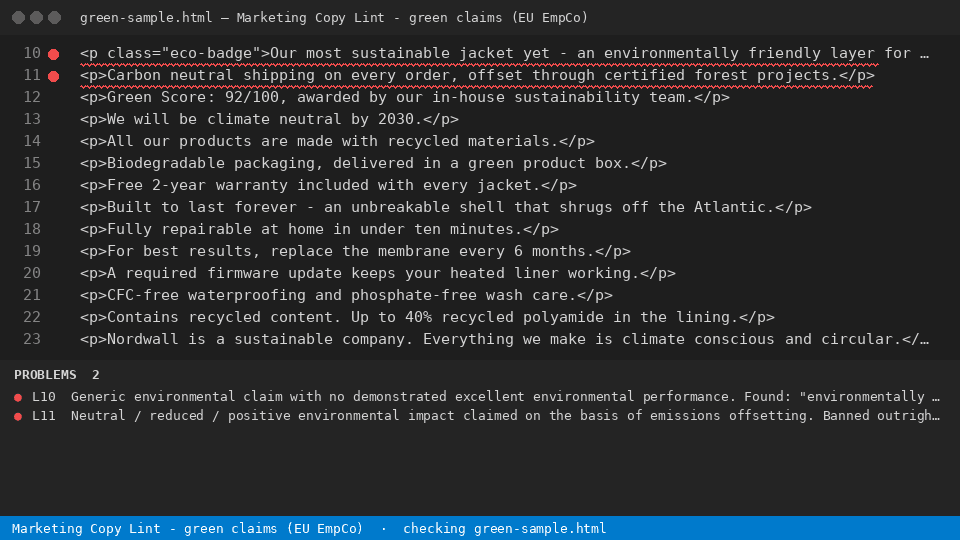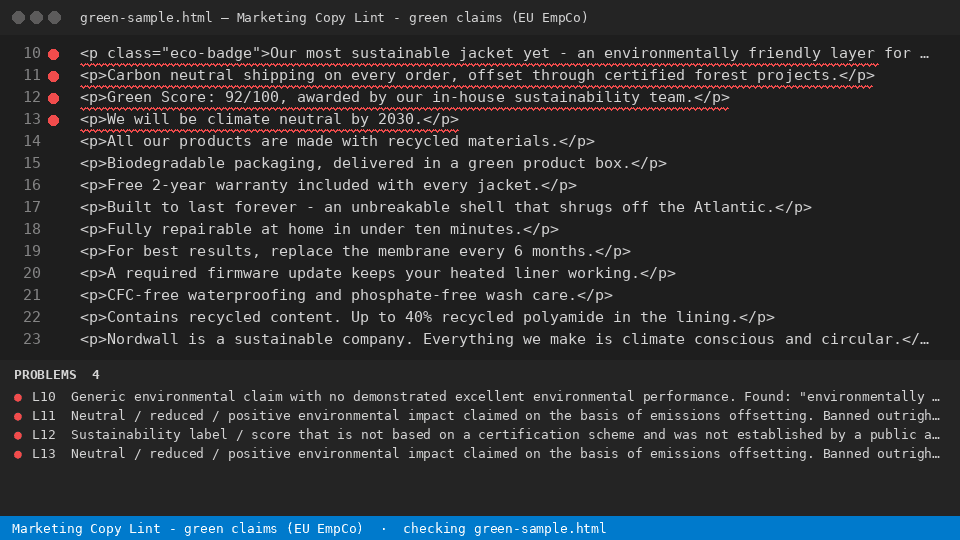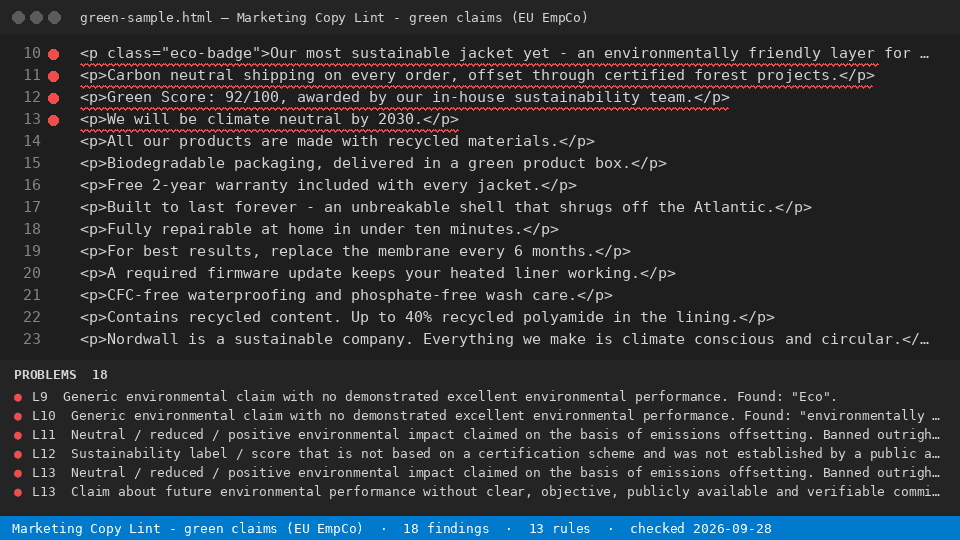
Reads your HTML and Markdown product copy and flags the environmental claims Directive (EU) 2024/825 turns into banned practices on 27 September 2026, with the clause and a compliant rewrite for each hit.
Install
green-claim-lint-empco file
Node 18+. The same 13 rules as the VS Code extension, from a terminal or CI.
Free
- Open a product page in VS Code or paste it into the free web version and get every banned-claim hit with its Directive (EU) 2024/825 clause, the exact phrase, and a compliant rewrite - all 13 rules, no key, no limit on how many pages you open one at a time.
--ruleslists every rule
With a licence ($29 once)
- Scan the entire workspace in one command and export a dated evidence report (CSV plus Markdown) that lists every page, hit, clause and rewrite - a file you keep and hand to counsel, a marketplace or an auditor.
green-claim-lint-empco --dir ./templates --report html --out report.html
UCPD Art. 13(3): for widespread infringements Member States must provide fines of at least 4% of the trader's annual turnover in the Member States concerned, or at least EUR 2,000,000 where turnover information is unavailable.
Use from an AI agent (MCP)
Claude Code · Cursor · Windsurf · any MCP client - add to your MCP config:
{ "mcpServers": { "green-claim-lint-empco": { "command": "green-claim-lint-empco", "args": ["--mcp"] } } }
Tools: check_text and check_file (free) · check_dir (licence). The agent gets every finding with the line number.
Use in CI
- name: Green Claim Lint - EU EmpCo 2026
  run: pip install rulestamp-green-claim-lint-empco && green-claim-lint-empco --dir . --ci
The folder sweep, reports and CI mode need one licence — one payment, no subscription. Set READYSTACK_LICENSE=<key> or run --license <key> once.
Install (PyPI)
pip install rulestamp-green-claim-lint-empco
green-claim-lint-empco --help
1 maintainer

Metadata
1 maintainer
Release files for rulestamp-green-claim-lint-empco 1.0.7
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| rulestamp_green_claim_lint_empco-1.0.7.tar.gz | 18.3 kB | Without provenance | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| rulestamp_green_claim_lint_empco-1.0.7-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 38.9 kB
Release files / rulestamp_green_claim_lint_empco-1.0.7.tar.gz
| Download URL | rulestamp_green_claim_lint_empco-1.0.7.tar.gz |
|---|---|
| Size | 18.3 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
902c65983526d87538d6014c86bb2607ad995df77702496476b9da92c88ee887
|
|
BLAKE2b-256 checksum How to use checksums |
ee4150263495c27e44864ffcf037c9b3cc2e8f25edf6c8cd732127697831cc56
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/7.0.0 CPython/3.12.3
|
Release files / rulestamp_green_claim_lint_empco-1.0.7-py3-none-any.whl
| Download URL | rulestamp_green_claim_lint_empco-1.0.7-py3-none-any.whl |
|---|---|
| Size | 20.6 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
8fb58bfaa50c95e8f82cfdb1fcb3370199162e44fc93f955ee80765a4e28457c
|
|
BLAKE2b-256 checksum How to use checksums |
de0c934e76cdaec09dd2beb35c64d4b89b73a7ea3eb2481ce56d2ad483bdf351
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/7.0.0 CPython/3.12.3
|
Security for rulestamp-green-claim-lint-empco 1.0.7
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.













