
Payroll Deduction Code Audit 2026
Runs the same checker as our npm package on a Node.js runtime that pip installs for you (
nodejs-wheel-binaries) - no system Node.js needed. Your files are checked locally.
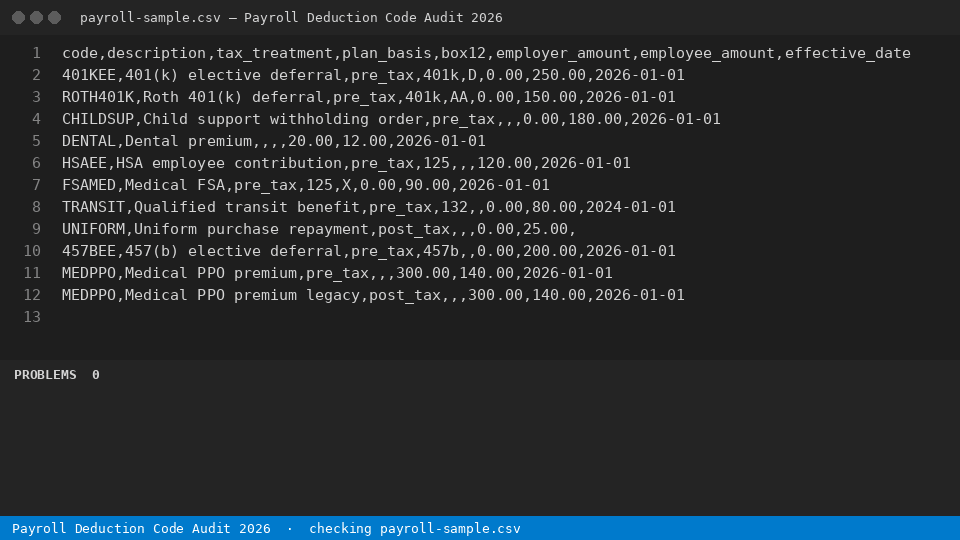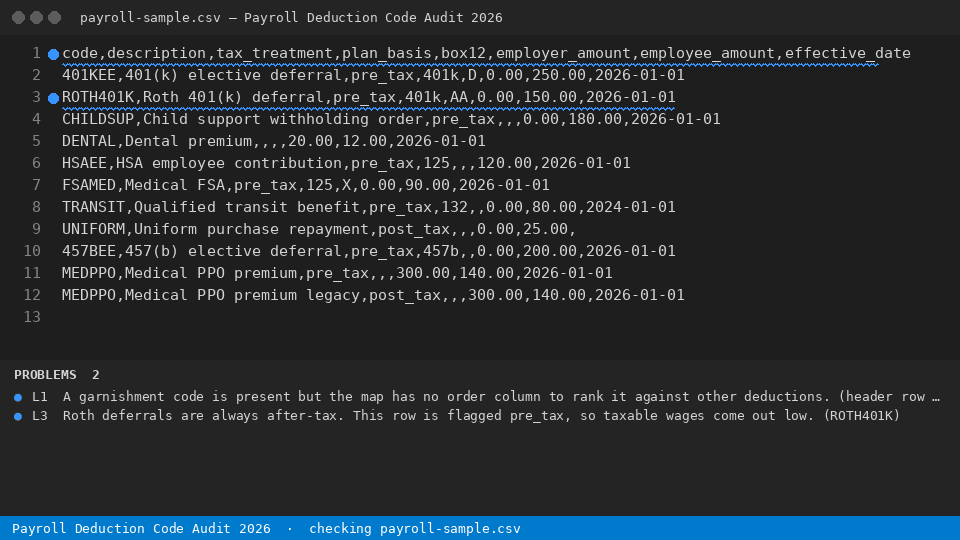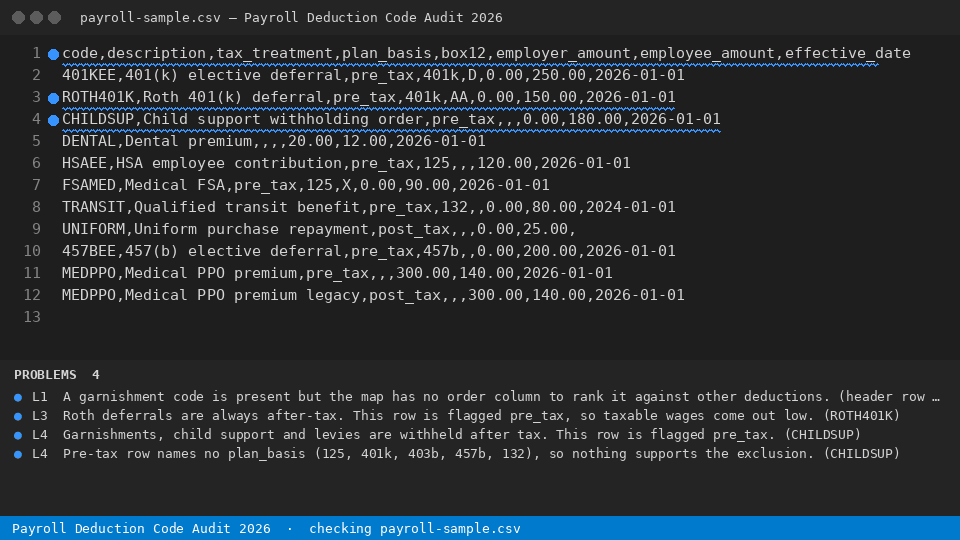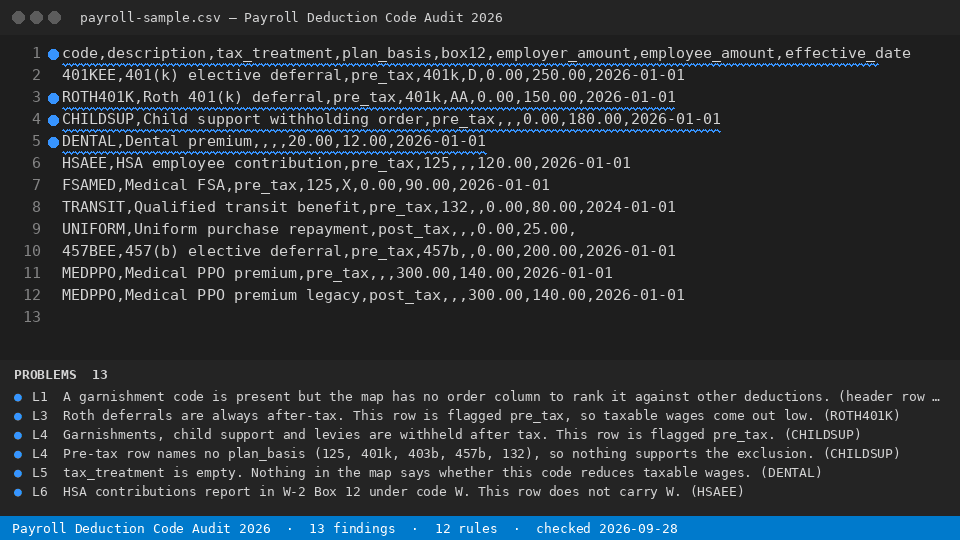
Twelve rules over the deduction-code map, before the January 31 W-2 filing date
Install
payroll-deduction-code-audit file
Node 18+. The same 12 rules as the VS Code extension, from a terminal or CI.
Free
- Every deduction code in the open map is audited against twelve rules and each broken line is named with its line number.
--ruleslists every rule
With a licence ($29 once)
- Audits every deduction map in the workspace at once and writes a dated exposure report you keep as the payroll audit trail.
payroll-deduction-code-audit --dir ./templates --report html --out report.html
Hand-checking one deduction map against the IRS Box 12 letter list is about half a day of a payroll analyst's time, every plan year
Use from an AI agent (MCP)
Claude Code · Cursor · Windsurf · any MCP client - add to your MCP config:
{ "mcpServers": { "payroll-deduction-code-audit": { "command": "payroll-deduction-code-audit", "args": ["--mcp"] } } }
Tools: check_text and check_file (free) · check_dir (licence). The agent gets every finding with the line number.
Use in CI
- name: Payroll Deduction Code Audit 2026
  run: pip install rulestamp-payroll-deduction-code-audit && payroll-deduction-code-audit --dir . --ci
The folder sweep, reports and CI mode need one licence — one payment, no subscription. Set READYSTACK_LICENSE=<key> or run --license <key> once.
Install (PyPI)
pip install rulestamp-payroll-deduction-code-audit
payroll-deduction-code-audit --help
1 maintainer

Metadata
1 maintainer
Release files for rulestamp-payroll-deduction-code-audit 1.0.5
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| rulestamp_payroll_deduction_code_audit-1.0.5.tar.gz | 16.0 kB | Without provenance | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| rulestamp_payroll_deduction_code_audit-1.0.5-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 34.2 kB
Release files / rulestamp_payroll_deduction_code_audit-1.0.5.tar.gz
| Download URL | rulestamp_payroll_deduction_code_audit-1.0.5.tar.gz |
|---|---|
| Size | 16.0 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
8994960dd5a249f167904c6fa3efd9c7e18a4dea79e34f03b62682366cfe5398
|
|
BLAKE2b-256 checksum How to use checksums |
18b25820cf0a696bcd2a613199925f220d4cd42401e454acdc75222271101d4f
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/7.0.0 CPython/3.12.3
|
Release files / rulestamp_payroll_deduction_code_audit-1.0.5-py3-none-any.whl
| Download URL | rulestamp_payroll_deduction_code_audit-1.0.5-py3-none-any.whl |
|---|---|
| Size | 18.2 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
16c594d0aac4cf6d710c5869f2ed3ac71a08a299475cce332bfd11156595cc2a
|
|
BLAKE2b-256 checksum How to use checksums |
3fd3e4eb2cf280645dfde03df31ebc55634a4ed4d87694583501e98be448f28e
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/7.0.0 CPython/3.12.3
|
Security for rulestamp-payroll-deduction-code-audit 1.0.5
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.













