
run-dig
Scan messy ML folders to find checkpoints, recover experiment metadata, and trace possible relationships.
Requires Python 3.10+ and Git.
pip install git+https://github.com/cz0211wyx/run-dig.git
run-dig scan ./experiments --open
Opens a local HTML report and saves run-dig-report/index.html and report.json.
Hover a graph node to highlight its links; click to see its files, metadata, and
relationship evidence. Arrows show recorded or possible sources; undirected links
show similarity or identical files.
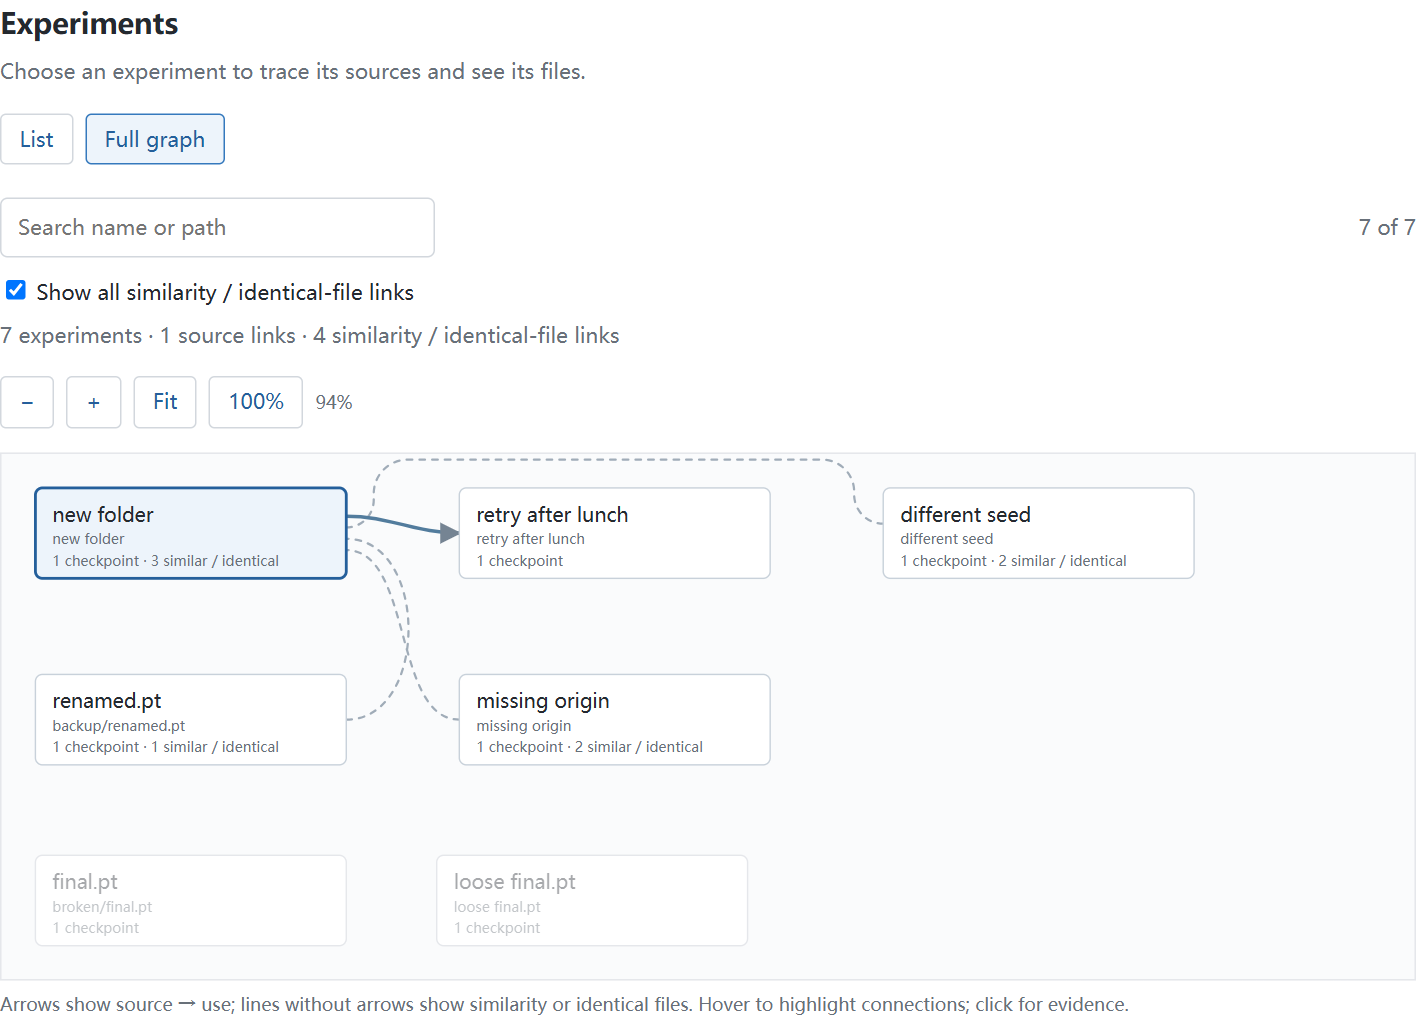
Try the interactive demo — explore sample experiments in your browser, no installation needed.
Supports .pt, .pth, .ckpt, .safetensors, and model .npz files.
NPZ detection uses array names and file context to distinguish models from feature
caches; it does not verify model validity. Arrays are never loaded.
Use the terminal to list, inspect, or compare checkpoints:
run-dig list ./experiments --sort size --name best
run-dig inspect run-a/best.pt --root ./experiments
run-dig compare run-a/best.pt run-b/best.pt --root ./experiments
--root includes related runs; --full shows all fields for inspect and compare.
Scanning is read-only. Checkpoints and scripts are never executed.
Relationships and checkpoint metrics include evidence and confidence. Similarity does not prove ancestry, and confidence is not a calibrated probability. Missing or conflicting settings remain unknown; conflicting values keep their sources.
1 maintainer

Metadata
1 maintainer
Release files for run-dig 0.2.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| run_dig-0.2.0.tar.gz | 57.6 kB | With provenance | Details for run_dig-0.2.0.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| run_dig-0.2.0-py3-none-any.whl | Python 3 | none | any | Details for run_dig-0.2.0-py3-none-any.whl |
Total release size: 105.1 kB
Release files / run_dig-0.2.0.tar.gz
| Download URL | run_dig-0.2.0.tar.gz |
|---|---|
| Size | 57.6 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
31391090e3300b783fbcb798a73398be95dcea95c2b309b61147f66b66513adb
|
|
BLAKE2b-256 checksum How to use checksums |
68a8e891a5e196fc39282207ac1f22e06288625bf31f463d438698423ebfc78b
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 13, 2026.
Transparency logRelease files / run_dig-0.2.0-py3-none-any.whl
| Download URL | run_dig-0.2.0-py3-none-any.whl |
|---|---|
| Size | 47.5 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
adb8edc230b7f7d0630892004fbad847f988e3c0a118c666172cd37f89349e55
|
|
BLAKE2b-256 checksum How to use checksums |
b13ad855d9ceff435459cf25784a44c2e15efc8994ae0ea64221ec77670852fd
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 13, 2026.
Transparency logSecurity for run-dig 0.2.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
Both files in this release have been uploaded with provenance metadata.
Attestation for run_dig-0.2.0.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 13, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














