
s3pe for Python


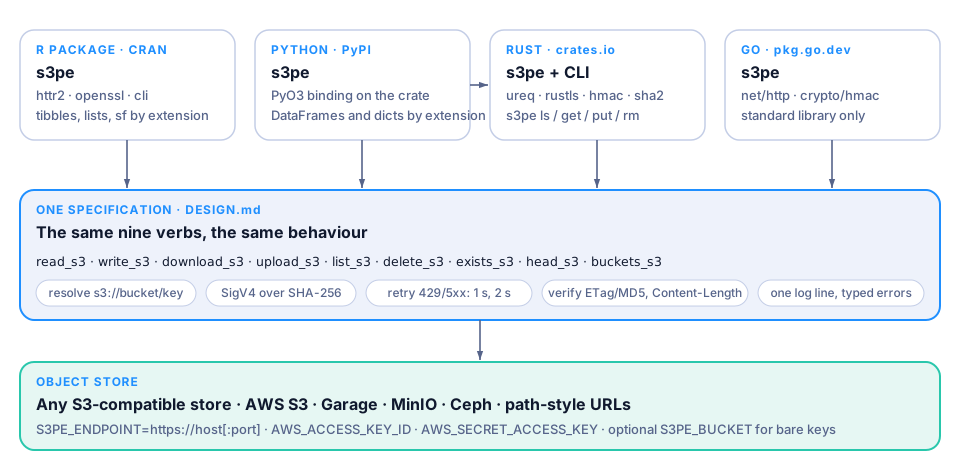
Read and write data on any S3-compatible object store (AWS S3, Garage, MinIO, Ceph, …). Nine verbs plus copy, pre-signed URLs and sync, three environment variables, and a Rust core that signs, retries and checks every transfer. Big files go up as multipart uploads by themselves.
Website: https://strategicprojects.github.io/s3pe/python/ · API reference: https://strategicprojects.github.io/s3pe/python/api/ · Português
Install
pip install s3pe            # bytes, str, dict/list and files
pip install "s3pe[pandas]"  # also CSV, Parquet and Excel as DataFrames
Wheels for Linux (x86_64, aarch64), macOS (Intel, Apple silicon) and Windows; Python 3.9 or later.
Use
import s3pe

# S3PE_ENDPOINT, AWS_ACCESS_KEY_ID and AWS_SECRET_ACCESS_KEY in the environment
meta = s3pe.read_s3("s3://my-bucket/data/manifest.json")      # dict
meta["version"]

df = s3pe.read_s3("series/sales.csv.gz", bucket="my-bucket")  # DataFrame
s3pe.write_s3(df, "s3://my-bucket/reports/sales.parquet")      # by extension
s3pe.upload_s3("figure1.png", "s3://my-bucket/reports/")       # keeps the file name
s3pe.download_s3("s3://my-bucket/data/regions.geojson", "regions.geojson")

for o in s3pe.list_s3("s3://my-bucket/data/"):
    print(o.size, o.key)
s3pe.exists_s3("s3://my-bucket/data/manifest.json")
s3pe.delete_s3("s3://my-bucket/reports/old.parquet")
Every call prints one line on stderr (↑ s3://my-bucket/reports/sales.parquet (1.2 MB, 0.3 s)); s3pe.quiet() or S3PE_QUIET=1 silences it.
With S3PE_BUCKET=my-bucket in the environment, or after
s3pe.configure(bucket="my-bucket"), bare keys work:
s3pe.read_s3("data/manifest.json"). For explicit settings use a client:
s3 = s3pe.Client(endpoint="http://127.0.0.1:9000", bucket="my-bucket",
                 access_key="...", secret_key="...")
s3.read("data/manifest.json")
s3.write(df, "reports/sales.csv")
s3.list("data/")
Big files, copies, batches, folders, metadata
s3pe.upload_s3("backup.tar", "s3://my-bucket/backups/")   # > 64 MiB: multipart, 4 parts at a time
s3pe.copy_s3("s3://my-bucket/etl/sales.parquet", "s3://my-bucket/archive/sales-2026.parquet")
s3pe.delete_s3([o.key for o in s3pe.list_s3("s3://my-bucket/tmp/")], bucket="my-bucket")
for e in s3pe.list_s3("s3://my-bucket/", delimiter="/"):      # one level: "folders" have size None
    print("dir " if e.is_prefix else "file", e.key)
s3pe.write_s3(df, "s3://my-bucket/reports/sales.csv",
              metadata={"author": "ana"}, headers={"Cache-Control": "max-age=3600"})
s3pe.head_s3("s3://my-bucket/reports/sales.csv").metadata     # {'author': 'ana'}
metadata becomes x-amz-meta-*; headers are sent as given, so
{"x-amz-server-side-encryption": "AES256"} turns on SSE where the store
supports it. Client(multipart_threshold=..., part_size=..., parallel=...)
or S3PE_MULTIPART_THRESHOLD, S3PE_PART_SIZE, S3PE_PARALLEL tune the
multipart upload (defaults 64 MiB, 16 MiB, 4).
Pre-signed URLs and sync
url = s3pe.presign_s3("s3://my-bucket/reports/report.pdf", expires=3600)   # anyone can GET it for an hour
url = s3pe.presign_s3("s3://my-bucket/inbox/upload.csv", method="PUT")

r = s3pe.sync_up_s3("./out", "s3://my-bucket/reports/", last="manifest.json")   # by ETag; manifest last
r.transferred, r.skipped, r.deleted
s3pe.sync_down_s3("s3://my-bucket/reports/", "./mirror", delete=True)
Formats
| Extension | read_s3 returns |
write_s3 accepts |
|---|---|---|
.json, .geojson |
dict / list |
dict, list, str, DataFrame (orient="records") |
.csv, .csv.gz, .tsv |
pandas.DataFrame |
DataFrame |
.parquet |
pandas.DataFrame |
DataFrame |
.xlsx |
pandas.DataFrame |
DataFrame |
.txt, .md, .html, .xml, .svg, ... |
str |
str |
| anything else | bytes |
bytes, file-like, pathlib.Path |
format="bytes" (or "text", "json", "csv", "parquet", "xlsx")
overrides the extension; extra keyword arguments go to the reader or writer
(s3pe.read_s3("x.csv", bucket="b", sep=";", dtype=str)). A .gz suffix
is compressed and decompressed on the way.
Configuration
| Setting | Environment | Default |
|---|---|---|
| endpoint | S3PE_ENDPOINT, then AWS_ENDPOINT_URL |
required (https://host[:port]) |
| region | AWS_REGION, then AWS_DEFAULT_REGION |
us-east-1 |
| credentials | AWS_ACCESS_KEY_ID, AWS_SECRET_ACCESS_KEY (AWS_SESSION_TOKEN) |
required |
| bucket | S3PE_BUCKET |
none: use s3://bucket/key or bucket= |
Errors
All errors derive from s3pe.S3Error: NotFoundError (404),
AccessDeniedError (403), HttpError (other statuses, with .status,
.code, .message), TransportError (network, after retries),
ConfigError (missing endpoint, credentials or bucket) and
IntegrityError (the bytes that arrived differ from the bytes sent).
exists_s3 and head_s3 turn 404 into False / None.
What happens in every call
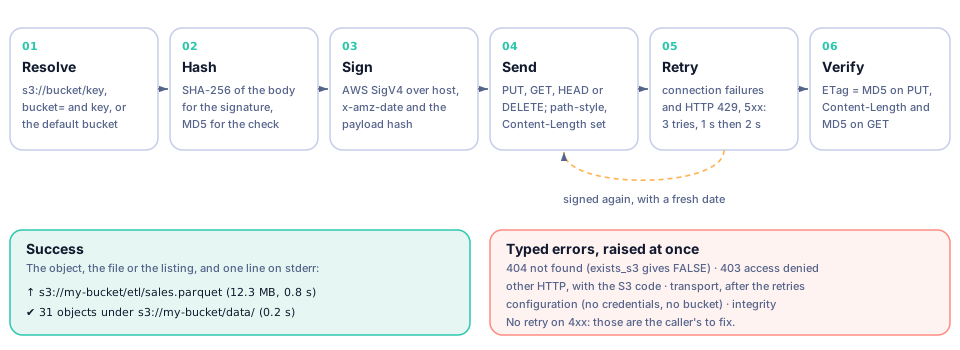
Dependable by default
- SigV4 signatures over the real SHA-256 of the payload, path-style URLs.
- Connection failures and HTTP 429/500/502/503/504 are retried twice (1 s, then 2 s). Other errors are raised at once, typed.
- After an upload the server's ETag is compared with the local MD5; after a
download the byte count with
Content-Lengthand, when the ETag is an MD5, the MD5 of what arrived. - Files are streamed to a
.s3pe-partfile and renamed when complete. - The Rust core releases the GIL during transfers.
Architecture
Em português
s3pe lê e grava dados em qualquer armazenamento de objetos compatível com
S3, com nove verbos: read_s3, write_s3, download_s3, upload_s3,
list_s3, delete_s3, exists_s3, head_s3, buckets_s3, mais
copy_s3, presign_s3 (URL temporária), sync_up_s3 e sync_down_s3
(espelho por ETag). Arquivos grandes sobem em partes automaticamente. O endpoint e
as credenciais vêm do ambiente (S3PE_ENDPOINT, AWS_ACCESS_KEY_ID,
AWS_SECRET_ACCESS_KEY); o formato vem da extensão do arquivo. Cada
transferência imprime uma linha no terminal; s3pe.quiet() silencia.
The family
The same package exists for R (install.packages("s3pe")), Rust
(cargo add s3pe, with the s3pe command line) and Go
(go get github.com/StrategicProjects/s3pe), all in
one repository.
Made in Pernambuco 🌵
s3pe is developed in Recife, Brazil. MIT license.
1 maintainer

Metadata
1 maintainer
Release files for s3pe 0.3.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| s3pe-0.3.0.tar.gz | 70.5 kB | With provenance | Details |
Built distributions (wheels)
| File | Reset | |||
|---|---|---|---|---|
| s3pe-0.3.0-cp39-abi3-win_amd64.whl | CPython 3.9 | abi3 | Windows x86-64 | Details |
| s3pe-0.3.0-cp39-abi3-manylinux_2_17_x86_64.manylinux2014_x86_64.whl | CPython 3.9 | abi3 | Linux glibc 2.17+ x86-64 | Details |
| s3pe-0.3.0-cp39-abi3-manylinux_2_17_aarch64.manylinux2014_aarch64.whl | CPython 3.9 | abi3 | Linux glibc 2.17+ ARM64 | Details |
| s3pe-0.3.0-cp39-abi3-macosx_11_0_arm64.whl | CPython 3.9 | abi3 | macOS 11.0+ ARM64 | Details |
| s3pe-0.3.0-cp39-abi3-macosx_10_12_x86_64.whl | CPython 3.9 | abi3 | macOS 10.12+ x86-64 | Details |
Total release size: 6.8 MB
Release files / s3pe-0.3.0.tar.gz
| Download URL | s3pe-0.3.0.tar.gz |
|---|---|
| Size | 70.5 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
2a962f8b5107c6f6d2e239956258b9079012e35cf458eb0c7899cc6e840b43ac
|
|
BLAKE2b-256 checksum How to use checksums |
0a4234aa331895f2f355465992da1900ee5865188a6c6f0c456309020cb91f4b
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 24, 2026.
Transparency logRelease files / s3pe-0.3.0-cp39-abi3-win_amd64.whl
| Download URL | s3pe-0.3.0-cp39-abi3-win_amd64.whl |
|---|---|
| Size | 1.3 MB |
| Tags | CPython 3.9 Windows x86-64 abi3 |
|
SHA-256 checksum How to use checksums |
172a63ecc29e7461b754e6f4be35335d4dda970b009a494ae47449de381a4257
|
|
BLAKE2b-256 checksum How to use checksums |
af5bb9b3c6c225d5a7bd1ab7796af8d932d86a8d15a16eb29d2e71a4d1e4e92f
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 24, 2026.
Transparency logRelease files / s3pe-0.3.0-cp39-abi3-manylinux_2_17_x86_64.manylinux2014_x86_64.whl
| Download URL | s3pe-0.3.0-cp39-abi3-manylinux_2_17_x86_64.manylinux2014_x86_64.whl |
|---|---|
| Size | 1.4 MB |
| Tags | CPython 3.9 Linux glibc 2.17+ x86-64 abi3 |
|
SHA-256 checksum How to use checksums |
444427d6ad4f3a7f9f84d54d00bf737b37127ccf863d514c5a04b30c3914c9e7
|
|
BLAKE2b-256 checksum How to use checksums |
2ae27bd1e2040295963f93afb524c2e0e4ce8104d2272a1e79ceb7338e159148
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 24, 2026.
Transparency logRelease files / s3pe-0.3.0-cp39-abi3-manylinux_2_17_aarch64.manylinux2014_aarch64.whl
| Download URL | s3pe-0.3.0-cp39-abi3-manylinux_2_17_aarch64.manylinux2014_aarch64.whl |
|---|---|
| Size | 1.4 MB |
| Tags | CPython 3.9 Linux glibc 2.17+ ARM64 abi3 |
|
SHA-256 checksum How to use checksums |
c004bd214f44b534b8c04896ffa7fcf2b50a601f8dbbeb088b5a2f9b750c2b10
|
|
BLAKE2b-256 checksum How to use checksums |
871cf873a1010e5a3437ec5c2318c31c56975e6883b6770dd59594d61f10361b
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 24, 2026.
Transparency logRelease files / s3pe-0.3.0-cp39-abi3-macosx_11_0_arm64.whl
| Download URL | s3pe-0.3.0-cp39-abi3-macosx_11_0_arm64.whl |
|---|---|
| Size | 1.3 MB |
| Tags | CPython 3.9 abi3 macOS 11.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
24354739c03f3a9cf5e2274d15c8207e688ce54246388ca84b26ef720d98c729
|
|
BLAKE2b-256 checksum How to use checksums |
801704fa49ee6b3579770d7f8a0ecd4753a35c02005d4048d968eca273a19653
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 24, 2026.
Transparency logRelease files / s3pe-0.3.0-cp39-abi3-macosx_10_12_x86_64.whl
| Download URL | s3pe-0.3.0-cp39-abi3-macosx_10_12_x86_64.whl |
|---|---|
| Size | 1.4 MB |
| Tags | CPython 3.9 abi3 macOS 10.12+ x86-64 |
|
SHA-256 checksum How to use checksums |
9052c997a3429137aac9c015675285407b715e1372f3e59a89d49ecedc027aa8
|
|
BLAKE2b-256 checksum How to use checksums |
a380f25627dfe5c2cdd7f7c834e87c26a92647759c673095f9470de1f087053e
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 24, 2026.
Transparency logSecurity for s3pe 0.3.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 6 files in this release have been uploaded with provenance metadata.
Attestation for s3pe-0.3.0.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 24, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














