
Scion SDK

Build secure connectors once. Serve, synchronize, and write back through one governed contract.
The typed source-integration boundary for MCP services and Medulla.








Documentation · Capabilities · Interfaces · Status
Quick Start
Install Scion SDK as scion-sdk and import it as
agent_connector_sdk. The repository is scion-sdk; package, CLI and API
identifiers remain unchanged.
Create a project and install the SDK:
uv init --bare demo-connector
cd demo-connector
uv add scion-sdk
uv sync
uv run connector-sync --help
The command prints the supervised synchronization options without opening a source session. Continue with the connector tutorial to build and run a one-file MCP connector, observe its health response, add declarative content, certify the live schema, and join source synchronization.
Overview
Scion SDK is the ecosystem's source-integration boundary. It turns vendor APIs and domain tools into secure MCP connectors, transports bounded source evidence into Medulla, indexes immutable repository snapshots, and applies authorized changes back to source systems.
Connector packages retain vendor behavior. The SDK owns transport, lifecycle, certification, and effect execution. Generated Medulla contracts own durable graph records, checkpoints, content identity, and receipts.
Key Capabilities
- Build FastMCP servers with authentication, safe exposure, health, visibility, rate limits, change subscriptions, and consistent tool surfaces.
- Publish skills, prompts, ontologies, SHACL shapes, and connector manifests as typed MCP content.
- Extract bounded source pages and advance checkpoints only from matching durable Medulla receipts.
- Import deterministic ConnectorPack archives without copying graph DTOs or digest algorithms into connector packages.
- Stream authenticated immutable repository snapshots into the generated
IndexRepositoryboundary without becoming a semantic writer. - Govern write-back through dry-run, authorization, source-version checks, idempotency, and uncertain-effect reconciliation.
- Certify extension identity, live MCP schemas, pagination, and safety behavior before activation.
Documentation
Start with Build the operator's first connector, then choose the reference that matches the work:
- Documentation home
- Capabilities
- Architecture
- Connector servers
- Schema disclosure
- Source synchronization
- Repository ingestion
- Extension interfaces
- Current status
Sibling authorities: Medulla owns durable graph state and generated contracts; Arbora owns authenticated runtime composition.
Architecture
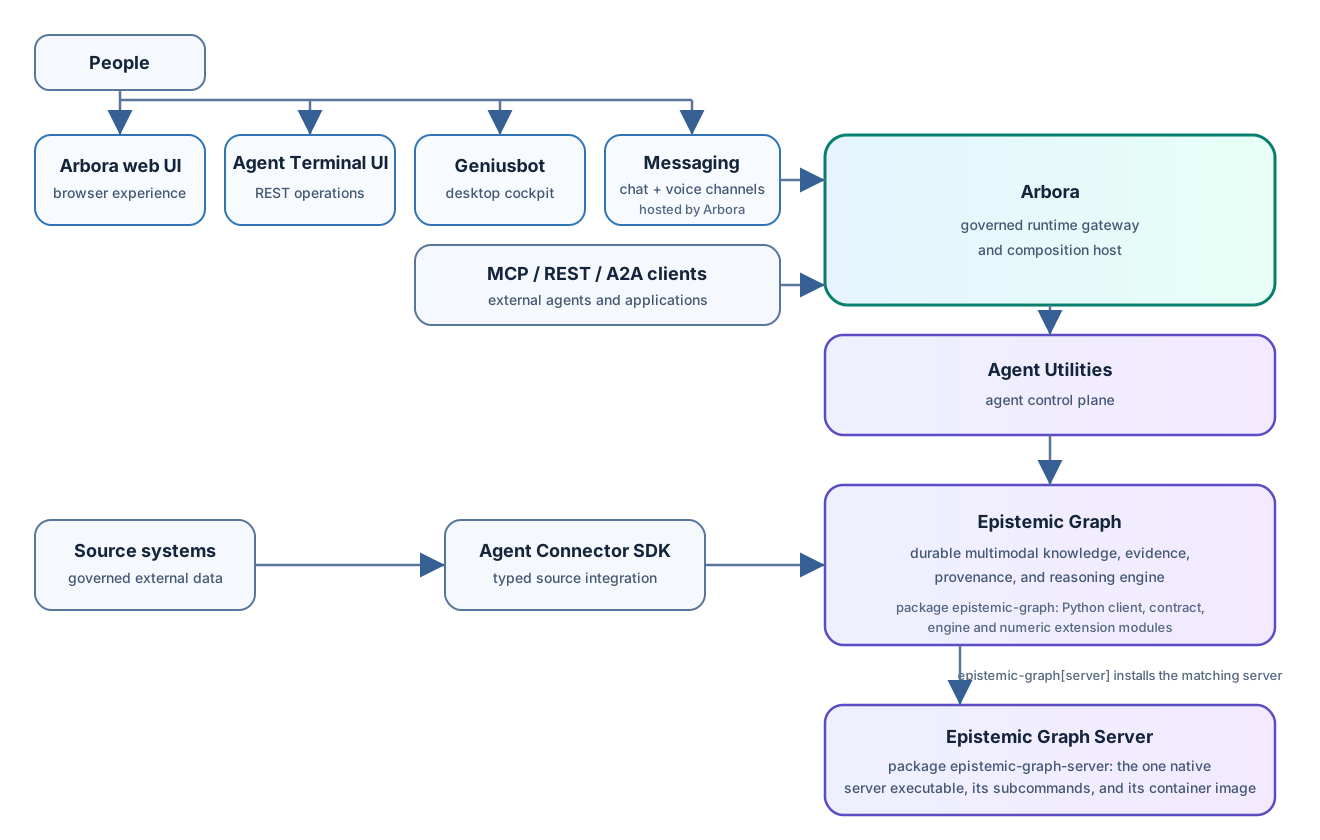
| Boundary | Owned here | Owned elsewhere |
|---|---|---|
| Connector service | MCP lifecycle, exposure policy, content capture, certification | Vendor models and business semantics stay in the connector package. |
| Source ingest | Discovery, bounded extraction, transport, receipt verification | Medulla owns mapping, checkpoints, provenance, and commit receipts. |
| Repository ingest | Authenticated snapshots, stable manifests, bounded object transport | Medulla owns indexing, graph projection, and semantic interpretation. |
| Write-back | Preview, source-version checks, apply, and reconciliation | Medulla owns change sets, authorization decisions, and durable outcomes. |
| Runtime composition | Typed ports and checked dependency requirements | Arbora supplies authenticated identity, clients, and live authority. |
The SDK depends directly on epistemic-graph>=2.27.6. Generated SourceIngest,
ConnectorPack, IndexRepository, and WriteBack clients and models are the graph
boundary; the SDK adds no parallel graph contract.
Contributing
Issues and pull requests are welcome. Follow AGENTS.md for ownership, isolation, and validation rules, and run the affected tests and public-surface gates before submitting a change.
License
Scion SDK is released under the MIT License.
1 maintainer

Metadata
1 maintainer
Release files for scion-sdk 0.5.6
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| scion_sdk-0.5.6.tar.gz | 796.5 kB | Without provenance | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| scion_sdk-0.5.6-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 1.6 MB
Release files / scion_sdk-0.5.6.tar.gz
| Download URL | scion_sdk-0.5.6.tar.gz |
|---|---|
| Size | 796.5 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
a8a9e52ade50835fe828de74c81db9ce983ef7b088e243762dd12757169bff99
|
|
BLAKE2b-256 checksum How to use checksums |
d335dd48282419c4488d451463e922379e6580fdb89b7b24159705da1aae79bb
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
uv/0.11.7 {"installer":{"name":"uv","version":"0.11.7","subcommand":["publish"]},"python":null,"implementation":{"name":null,"version":null},"distro":{"name":"Ubuntu","version":"26.04","id":"resolute","libc":null},"system":{"name":null,"release":null},"cpu":null,"openssl_version":null,"setuptools_version":null,"rustc_version":null,"ci":true}
|
Release files / scion_sdk-0.5.6-py3-none-any.whl
| Download URL | scion_sdk-0.5.6-py3-none-any.whl |
|---|---|
| Size | 784.8 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
0276f6aea3eecfabc408191a112ac9bb221ce994033e714231ae59fb3f7ab117
|
|
BLAKE2b-256 checksum How to use checksums |
692cb63f9dec5c402c51a37a2466936b336510e89ac72b183cbedcc0d9ae7590
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
uv/0.11.7 {"installer":{"name":"uv","version":"0.11.7","subcommand":["publish"]},"python":null,"implementation":{"name":null,"version":null},"distro":{"name":"Ubuntu","version":"26.04","id":"resolute","libc":null},"system":{"name":null,"release":null},"cpu":null,"openssl_version":null,"setuptools_version":null,"rustc_version":null,"ci":true}
|
Security for scion-sdk 0.5.6
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














