
scivol
scivol fits univariate conditional volatility models and dynamic conditional correlation (DCC) models in Python. Models are built from components (a mean, a volatility recursion and an innovation density) and estimated jointly by exact maximum likelihood, with analytical gradients and Hessians computed in a standalone C++20 library.
from scivol import ARMA, GJRGARCH, SkewT

result = (ARMA(1, 0) + GJRGARCH(1, 1) + SkewT()).fit(returns)
result.summary()
forecast = result.forecast(10)
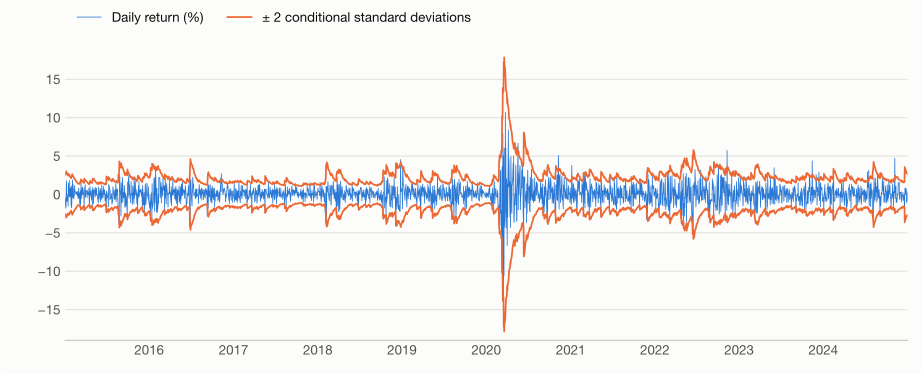
Daily returns of an equal-weighted portfolio of 1,381 US stocks, 2015–2024, with ±2 conditional standard deviations from a fitted GJR-GARCH model with skewed-t innovations:
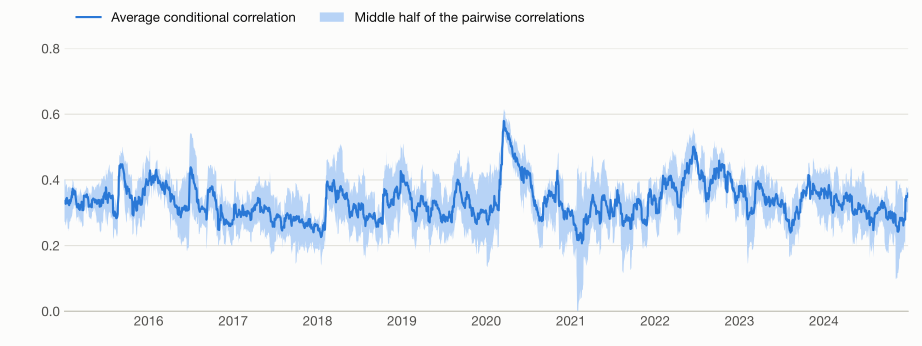
Conditional correlations among five of those stocks from a DCC model; the line is their average and the band the middle half of the ten pairwise correlations:
Models. ARMA, ARX and HARX means; GARCH, GJR-GARCH, EGARCH and APARCH volatility; Normal, Student-t, Hansen's skewed t, GED, generalized hyperbolic, NIG, hyperbolic and variance-gamma innovations; DCC with Gaussian or Student-t copulas. Every combination is one model with one likelihood.
Estimation you can check. Each likelihood and its derivatives are tested against an automatic-differentiation reference. A fit is reported as successful only when the first-order conditions hold in the model's parameter domain; otherwise the estimate comes back with a status that says why. Standard errors are withheld where ordinary inference does not apply. Several starting points are tried by default, because volatility likelihoods often have more than one local maximum.
Speed. On 500 liquid US stocks and ten models, a fit took a median 1–6 ms, 4.9 times faster than arch and 53 times faster than rugarch per fit, while missing its own likelihood maximum less often than either; DCC fits were 20–50 times faster than rmgarch. See the benchmarks for the method and its limits.
Installation
pip install scivol
Wheels for CPython 3.10–3.12 on Linux (x86-64), macOS (Apple Silicon) and Windows (x64); elsewhere pip builds from source, which needs a C++20 compiler, CMake and Ninja.
Documentation
Getting started · Models · Estimation · Inference · Forecasting · Diagnostics · Model selection · API · References
The defaults of the automatic model-selection procedures have not yet been calibrated by simulation.
License
MIT.
1 maintainer

Metadata
1 maintainer
Release files for scivol 0.4.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| scivol-0.4.0.tar.gz | 1.1 MB | With provenance | Details for scivol-0.4.0.tar.gz |
Built distributions (wheels)
Total release size: 65.7 MB
Release files / scivol-0.4.0.tar.gz
| Download URL | scivol-0.4.0.tar.gz |
|---|---|
| Size | 1.1 MB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
81d2fb326083aca706fc5eaebb30760291ae677c454fecc12ee8d76b2190f0fd
|
|
BLAKE2b-256 checksum How to use checksums |
5b955f2fcc52d81bf452ff45fc957b4c64db58608f2577f326214bfb689a8337
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 30, 2026.
Transparency logRelease files / scivol-0.4.0-cp312-cp312-win_amd64.whl
| Download URL | scivol-0.4.0-cp312-cp312-win_amd64.whl |
|---|---|
| Size | 2.9 MB |
| Tags | CPython 3.12 Windows x86-64 |
|
SHA-256 checksum How to use checksums |
41f3fe1c2ee2c86ec98d3faa37322d489a83c2e30a424f48b2eec24f531bafaf
|
|
BLAKE2b-256 checksum How to use checksums |
99491e56709a7cda2459431b2cc1257e5632ad5b34ebdc53bcb47fe839d8cafc
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 30, 2026.
Transparency logRelease files / scivol-0.4.0-cp312-cp312-musllinux_1_2_x86_64.whl
| Download URL | scivol-0.4.0-cp312-cp312-musllinux_1_2_x86_64.whl |
|---|---|
| Size | 7.8 MB |
| Tags | CPython 3.12 Linux musl 1.2+ x86-64 |
|
SHA-256 checksum How to use checksums |
271c4a0c56177298832040b031268d98668c4f3d8d15f24081071ac5a5689ea1
|
|
BLAKE2b-256 checksum How to use checksums |
76426137c0979de5918f0a191ed464063c2ab299777327866144034a6dffc975
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 30, 2026.
Transparency logRelease files / scivol-0.4.0-cp312-cp312-manylinux_2_27_x86_64.manylinux_2_28_x86_64.whl
| Download URL | scivol-0.4.0-cp312-cp312-manylinux_2_27_x86_64.manylinux_2_28_x86_64.whl |
|---|---|
| Size | 7.3 MB |
| Tags | CPython 3.12 Linux glibc 2.27+ x86-64 Linux glibc 2.28+ x86-64 |
|
SHA-256 checksum How to use checksums |
1ee048d7a064d57316afab62fa65ec3cdbf78debcd1f5ddf49c88be488b8419e
|
|
BLAKE2b-256 checksum How to use checksums |
8fbf625b41df5a55e17e55520053ec6aeb1fc55492c55d6c33d0c3b295440fe0
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 30, 2026.
Transparency logRelease files / scivol-0.4.0-cp312-cp312-macosx_11_0_arm64.whl
| Download URL | scivol-0.4.0-cp312-cp312-macosx_11_0_arm64.whl |
|---|---|
| Size | 3.6 MB |
| Tags | CPython 3.12 macOS 11.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
b7ae1ef2a62d1155efb649b1bd610f0772953de430b6001a9cac735155459f86
|
|
BLAKE2b-256 checksum How to use checksums |
d26e7c2e5d88060a692c8facf19abea722945b94d35e71347493ef78ecb1df90
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 30, 2026.
Transparency logRelease files / scivol-0.4.0-cp311-cp311-win_amd64.whl
| Download URL | scivol-0.4.0-cp311-cp311-win_amd64.whl |
|---|---|
| Size | 2.9 MB |
| Tags | CPython 3.11 Windows x86-64 |
|
SHA-256 checksum How to use checksums |
c5aa1b9b17aaeb6ff607e4d55675daedf730bf0e0c39690f32832c7186e8bde4
|
|
BLAKE2b-256 checksum How to use checksums |
d010aa0119b562430905f16d033256f739e5f81ebf33fa97d0df4beefe1fc8dc
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 30, 2026.
Transparency logRelease files / scivol-0.4.0-cp311-cp311-musllinux_1_2_x86_64.whl
| Download URL | scivol-0.4.0-cp311-cp311-musllinux_1_2_x86_64.whl |
|---|---|
| Size | 7.8 MB |
| Tags | CPython 3.11 Linux musl 1.2+ x86-64 |
|
SHA-256 checksum How to use checksums |
03dae3b2dabc0093aa65ec06b3d15d4d6874dc1b17c861d415b88761220061af
|
|
BLAKE2b-256 checksum How to use checksums |
4fc0d6517598c0f3b36721e0f5900d45bff9f8ba031f848aad0eb0ceb335a2fd
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 30, 2026.
Transparency logRelease files / scivol-0.4.0-cp311-cp311-manylinux_2_27_x86_64.manylinux_2_28_x86_64.whl
| Download URL | scivol-0.4.0-cp311-cp311-manylinux_2_27_x86_64.manylinux_2_28_x86_64.whl |
|---|---|
| Size | 7.3 MB |
| Tags | CPython 3.11 Linux glibc 2.27+ x86-64 Linux glibc 2.28+ x86-64 |
|
SHA-256 checksum How to use checksums |
b121ca2b9dd7d05dfb0307c06bbaa564707079db1710e676fee043ace32386c4
|
|
BLAKE2b-256 checksum How to use checksums |
e254bb4d70c31940a1fb942d8b4ca1671049ca795aacecc3ffa3279d9c945196
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 30, 2026.
Transparency logRelease files / scivol-0.4.0-cp311-cp311-macosx_11_0_arm64.whl
| Download URL | scivol-0.4.0-cp311-cp311-macosx_11_0_arm64.whl |
|---|---|
| Size | 3.6 MB |
| Tags | CPython 3.11 macOS 11.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
f8e073164d57d4f78284cdb16aab377783c843f17935fb90e0d33da853a999a2
|
|
BLAKE2b-256 checksum How to use checksums |
e00a77cce456a88d5f4bf12283d26848a043b91a9ff90652e8ad861152a3b6e1
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 30, 2026.
Transparency logRelease files / scivol-0.4.0-cp310-cp310-win_amd64.whl
| Download URL | scivol-0.4.0-cp310-cp310-win_amd64.whl |
|---|---|
| Size | 2.9 MB |
| Tags | CPython 3.10 Windows x86-64 |
|
SHA-256 checksum How to use checksums |
a47d79c4061781ca11cb2a2b3b15675f2da5bc28a65751bb8a638ad9939e3e5a
|
|
BLAKE2b-256 checksum How to use checksums |
193354c4261d352a0a7f9c3d064a93fda04b7d2fb26bf0c1940e94b495b44fbc
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 30, 2026.
Transparency logRelease files / scivol-0.4.0-cp310-cp310-musllinux_1_2_x86_64.whl
| Download URL | scivol-0.4.0-cp310-cp310-musllinux_1_2_x86_64.whl |
|---|---|
| Size | 7.8 MB |
| Tags | CPython 3.10 Linux musl 1.2+ x86-64 |
|
SHA-256 checksum How to use checksums |
55a1c4a39ae3da9d1f4a3c9d1eae17127756753846e2b34b9c4a3d53b8f2679c
|
|
BLAKE2b-256 checksum How to use checksums |
90d6faf4fb093944e8fabd66ada952251c455cd0ea8ed1e29a7afeec285d444a
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 30, 2026.
Transparency logRelease files / scivol-0.4.0-cp310-cp310-manylinux_2_27_x86_64.manylinux_2_28_x86_64.whl
| Download URL | scivol-0.4.0-cp310-cp310-manylinux_2_27_x86_64.manylinux_2_28_x86_64.whl |
|---|---|
| Size | 7.3 MB |
| Tags | CPython 3.10 Linux glibc 2.27+ x86-64 Linux glibc 2.28+ x86-64 |
|
SHA-256 checksum How to use checksums |
328b7a06d68e1884515700c63ce3e977e6cfc071ca413fe8e0cf35813cdd82ec
|
|
BLAKE2b-256 checksum How to use checksums |
bc7157c14095fbc066cea6a81b1ccb14bb79acc6b833fcdf16399a9f5756dda2
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 30, 2026.
Transparency logRelease files / scivol-0.4.0-cp310-cp310-macosx_11_0_arm64.whl
| Download URL | scivol-0.4.0-cp310-cp310-macosx_11_0_arm64.whl |
|---|---|
| Size | 3.6 MB |
| Tags | CPython 3.10 macOS 11.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
0fe8bf8fe8680b6b4aa340826f2a9bce12d932b092fd34a8de7992694091d8c1
|
|
BLAKE2b-256 checksum How to use checksums |
7220e32afcbbbcce0410ac3491512ed1ec8d3b54dfb980078ae859ea1dd20adc
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 30, 2026.
Transparency logSecurity for scivol 0.4.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 13 files in this release have been uploaded with provenance metadata.
Attestation for scivol-0.4.0.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 30, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














