
sensez




Coding agents produce tech debt. Bring them to their senses.
Coding agents forget the maintainability rules you give them. They hide logic in nested functions, reach for dict[str, Any] instead of a typed model, and pass around boolean flags whose meaning only exists in the agent’s current context.
Instructions help, but they’re soft constraints. Static analysis tools in your CI pipeline catch the problem too late and it starts rotting in a Jira ticket.
sensez adds fast, deterministic static feedback that agents can act on while they’re still working. It runs inside the coding-agent loop, giving agents fast, structured feedback on duplication, dead code, cycles, architecture violations, and design smells—so they fix problems before technical debt compounds.
In controlled evaluations, agents using Sensez produced 86% fewer code smells, 90% less duplicated code, and 67% fewer lines.
Website · Documentation · MCP and agent guide · Configuration reference
Quick start
Python
uv add --dev sensez      # or install globally: uv tool install sensez
uv run sensez init       # writes a starter config and registers the MCP server
uv run sensez noze .     # scan once — no install needed with: uvx sensez noze .
JavaScript and TypeScript
npm install --save-dev sensez
npx sensez init
npx sensez noze .
sensez init writes a commented starter sensez.toml and registers Sensez as
an MCP server with your coding agent — Claude Code, Cursor, Cline, Codex,
OpenCode, and Pi are supported. Restart the agent afterwards so the server
is picked up. sensez . and sensez noze . both run the default scan.
A report is one screen, focused on what to fix first:
$ sensez noze .
sensez — structural maintainability report

Circular imports (1)
    [warning] ↻ shop.promo → shop.cart
        ./shop/promo.py:1  shop.promo → shop.cart
        ./shop/cart.py:1  shop.cart → shop.promo

Duplication (1)
    [advisory] structural clone (53):
      ./shop/clone_a.py:1-12
      ./shop/clone_b.py:1-12

Dead code candidates (2)
    [advisory] ./shop/legacy.py:1  shop.legacy::orphan_helper (function) [high]
    [advisory] ./shop/promo.py:10  shop.promo::recap (function) [high]

Code smells (0)

Boundary violations (not configured)
Why Sensez?
Coding agents are excellent at producing code—and, occasionally, at producing
the same helper three times, gently ignoring architecture notes, and replacing
type-safe models with dict[str, Any]. The vibes are immaculate; the result
can still be a slopocalypse that takes hours to untangle.
Sensez closes that feedback loop while an edit is still fresh. It gives agents short, structured feedback on the repository's shape, so problems can be fixed before they become load-bearing.
The gap is especially visible in agent-driven work:
- Context rots. Architecture guidance fades across long, summarized turns.
- CI is too late. Small, non-blocking structural warnings are easy to defer.
- Slow checks do not fit the turn. If a check takes minutes, it cannot run in every feedback loop—and debt has time to accumulate.
[Agent proposes turn finish] ──> [Sensez MCP sniff] ──> [Finds cycle / clone / smell]
                                      │
                                      └──> Immediate, actionable feedback
Sensez complements—not replaces—Ruff, ty, mypy, ESLint, TypeScript, rustc,
and Clippy. Use those tools for local correctness; use Sensez for the structural
relationships across the codebase.
What it finds
| Area | Output key | What it catches |
|---|---|---|
| Duplication | duplication |
Structural clones, including local-rename copies. |
| Dead code | dead_code |
Unreferenced symbols with confidence tiers. |
| Cycles | cycles |
Import loops and load-order tangles. |
| Boundaries | boundaries |
Imports that cross configured architecture rules. |
| Smells | smells |
Design pressure inside functions, classes, modules, and the graph. |
Some examples of the included smells:
| Smell | Why Sensez flags it |
|---|---|
tuple_packing |
Positional tuples hide meaning; tuple[int, str, int] is not a data model. |
loose_typing |
Any, schema-erasing maps, and primitive containers erase caller contracts. |
boolean_blindness |
do_thing(True, False) makes argument meaning a guessing game. |
implicit_schema |
Repeated string-key access often means a real shape is hiding in a dict. |
mutated_parameter |
A function returns a parameter after chewing it up. |
feature_envy |
A method that mostly uses another object's data may belong elsewhere. |
message_chain |
Long a.b.c.d chains couple callers to deep object plumbing. |
god_module |
One module has become the place everything depends on. |
magic_string_default |
|| "" or or "" hides a string that should be required. |
split_variable |
Multiple reassignments of a variable in one scope add hidden state. |
nested_loop |
Beta, opt-in: nested iteration may have unintended complexity. |
nested_ternary |
Nested conditional expressions make agent-generated decisions hard to follow. |
n_plus_one_call |
Beta, opt-in: one-by-one external calls may need batching. |
The default report is intentionally fixable in one screen: each pillar shows its
top five offenders, each smell kind shows its total plus its top three examples,
and dead-code output includes high-confidence findings only. Use --all for
every finding, or --max N to set another cap.
# Focus a CI check on the pillars you care about
sensez noze . --duplicates
sensez noze . --duplicates --dead-code --json
Performance
Sensez evaluates all structural pillars in one pass.
Python: pylint benchmark
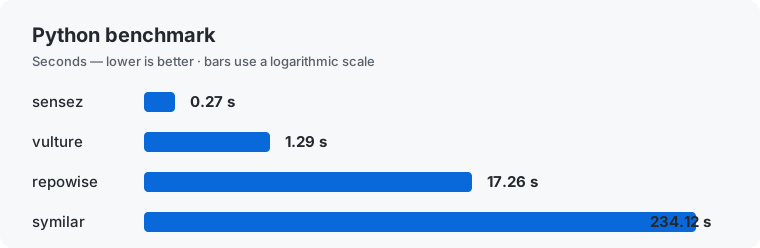
| Tool | Time | Scope |
|---|---|---|
| sensez | 0.27 s | All structural pillars in one pass |
| vulture | 1.29 s | Python dead code |
| repowise | 17.26 s | Repository intelligence, including dead code |
| symilar | 234.12 s | Line-based duplication |
JavaScript / TypeScript: zod benchmark
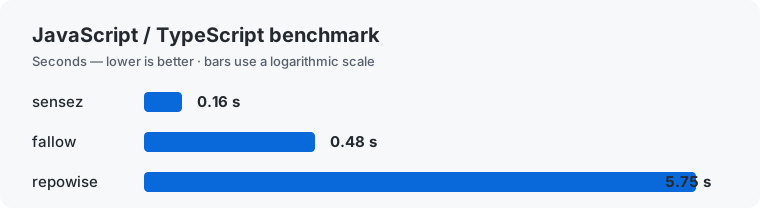
| Tool | Time | Scope |
|---|---|---|
| sensez | 0.16 s | All structural pillars in one pass |
| fallow | 0.48 s | JS/TS structural dead-code and dependency findings |
| repowise | 5.75 s | Repository intelligence, including dead code |
Agent impact
The same coding agent completed 70 real-world Python tasks from SWE-PolyBench
and SWE-bench Verified, plus 21 synthetic tasks designed to trigger specific
maintainability traps. Both variants received SOLID/DRY principles. The Sensez
variant additionally had to call noze_sniff in a feedback loop before it could
declare a task complete.
| New quality issues | Clone tokens | New clones | Lines written | Tokens used | |
|---|---|---|---|---|---|
| Without Sensez | 14 | 1,251 | 129 | 2,080 | 1.23M |
| With Sensez | 2 | 126 | 0 | 682 | 1.34M |
| Reduction | 86% | 90% | 100% | 67% | +8.7% overhead |
Sensez agents produced structurally cleaner code with 67% fewer lines. Benchmarks used SWE-PolyBench_500, SWE-bench Verified, and synthetic pillar tests. See the evaluation suite for the methodology and per-benchmark results.
MCP for agents
MCP is the recommended integration when Sensez should run repeatedly during a
coding session rather than as a one-off shell command. sensez init registers
the server with your coding agent, which then launches it automatically at
startup — there is nothing to run by hand.
| Tool | Use |
|---|---|
noze_sniff |
Scan the repository for smells and structural issues. |
noze_gate |
Experimental end-of-turn diff gate; may be noisy for short or Q&A turns. |
noze_explain |
Explain a finding category. |
get_configuration_summary |
Summarize the effective configuration and noisiest rules when tuning. |
brainz_report |
Summarize local usage and resolution metrics. |
brainz_triage |
Record user-approved debt or false-positive verdicts. |
eyez_search_docs |
Disabled unless eyez is enabled; searches docstrings and comments. |
Sensez can also run standalone in GitHub Actions. See the GitHub Action guide.
Configuration
Sensez reads sensez.toml from the project root, or [tool.sensez] from
pyproject.toml when sensez.toml is absent.
sensez init
The main configuration areas are:
[duplication]for clone thresholds[dead_code]for dynamic entry points[cycles]for cycle-only path excludes[smells]for smell toggles and thresholds[[boundaries.forbidden]]for architecture contracts[action]for how strongly agents and gates treat each pillar[accept]for shared accepted findings[self_improvement]for local metrics[cache]enables MCP/LSP process-memory reuse; CLI scans always stay stateless
[duplication]
threshold = 50

[dead_code]
entrypoint_names = ["register", "main", "setup"]

[smells.rules.long_function]
max_lines = 80
action = "warning"

# The beta performance heuristics are disabled by default.
[smells.rules.nested_loop]
enabled = true

[smells.rules.n_plus_one_call]
enabled = true
Smell rules can also be overridden per language, and every finding carries an
action level (info → must_fix) that drives gates and CI. See the
Configuration reference
for action levels, per-language overrides, boundary patterns, and accepting
findings.
Local-only metrics and privacy
brainz records scans, gate blocks, triage decisions, resolved findings,
regressions, detector precision, and usage reports locally.
sensez brainz report .
sensez brainz report . --json
Everything remains under .sensez/local-metrics/. Sensez sends no telemetry
and uploads no source code. Disable local metrics for a repository with:
[self_improvement]
enabled = false
Project anatomy
spine: file discovery, parsing, shared IR, and dependency graph.profiles: language adapters for Python, JS/TS, TSX, and Rust.noze: duplication, dead code, cycles, and design smells.bonez: architecture-boundary auditing.brainz: local-only metrics and feedback memory.eyez: optional doc/comment search; not yet enabled.mcp: JSON-RPC/MCP surface for agent integration.reporter: terminal and JSON output.setup: starter configuration, MCP registration, and hook setup.
Disclaimer
Please review DISCLAIMER.md for the project disclaimer.
1 maintainer

Metadata
1 maintainer
Release files for sensez 0.4.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Built distributions (wheels)
| File | Reset | |||
|---|---|---|---|---|
| sensez-0.4.0-py3-none-win_amd64.whl | Python 3 | none | Windows x86-64 | Details |
| sensez-0.4.0-py3-none-manylinux_2_39_x86_64.whl | Python 3 | none | Linux glibc 2.39+ x86-64 | Details |
| sensez-0.4.0-py3-none-manylinux_2_39_aarch64.whl | Python 3 | none | Linux glibc 2.39+ ARM64 | Details |
| sensez-0.4.0-py3-none-macosx_11_0_arm64.whl | Python 3 | none | macOS 11.0+ ARM64 | Details |
| sensez-0.4.0-py3-none-macosx_10_12_x86_64.whl | Python 3 | none | macOS 10.12+ x86-64 | Details |
Total release size: 27.1 MB
Release files / sensez-0.4.0-py3-none-win_amd64.whl
| Download URL | sensez-0.4.0-py3-none-win_amd64.whl |
|---|---|
| Size | 5.0 MB |
| Tags | Python 3 Windows x86-64 |
|
SHA-256 checksum How to use checksums |
f8c885cdd8d9a7e17671091687b4378206ff6a86de8d17428790f67138934c50
|
|
BLAKE2b-256 checksum How to use checksums |
610fa2de74146f2ac7c097bccfa0147e43010c21960a7cc9d882222f91779fa4
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 29, 2026.
Transparency logRelease files / sensez-0.4.0-py3-none-manylinux_2_39_x86_64.whl
| Download URL | sensez-0.4.0-py3-none-manylinux_2_39_x86_64.whl |
|---|---|
| Size | 5.7 MB |
| Tags | Linux glibc 2.39+ x86-64 Python 3 |
|
SHA-256 checksum How to use checksums |
fc43bf79b0e06780dd1db0a0aa5609fcb23ddc3fc351986f79a806afc4d2d10b
|
|
BLAKE2b-256 checksum How to use checksums |
4f8cf5c0e2e3af7d14d1946563cefb8864e124fddeb0753aeaee66f1f81541a6
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 29, 2026.
Transparency logRelease files / sensez-0.4.0-py3-none-manylinux_2_39_aarch64.whl
| Download URL | sensez-0.4.0-py3-none-manylinux_2_39_aarch64.whl |
|---|---|
| Size | 5.7 MB |
| Tags | Linux glibc 2.39+ ARM64 Python 3 |
|
SHA-256 checksum How to use checksums |
2cd6c4768193cebffbe926c6cac7b28e3f648bcff602fad958e70e5d961489fd
|
|
BLAKE2b-256 checksum How to use checksums |
dd247a163d88fc3cd5119a384353e03d9be4aa9ebbd5dcc413a63f366238eb0d
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 29, 2026.
Transparency logRelease files / sensez-0.4.0-py3-none-macosx_11_0_arm64.whl
| Download URL | sensez-0.4.0-py3-none-macosx_11_0_arm64.whl |
|---|---|
| Size | 5.2 MB |
| Tags | Python 3 macOS 11.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
58f9bb3e6bce2a56c9bac1acdbe82ac5377e72397f0bd55b6399edf95ffd8e65
|
|
BLAKE2b-256 checksum How to use checksums |
bc392a20d3f01178eeef6d54808f930594fea6b7eae817433547098408133802
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 29, 2026.
Transparency logRelease files / sensez-0.4.0-py3-none-macosx_10_12_x86_64.whl
| Download URL | sensez-0.4.0-py3-none-macosx_10_12_x86_64.whl |
|---|---|
| Size | 5.4 MB |
| Tags | Python 3 macOS 10.12+ x86-64 |
|
SHA-256 checksum How to use checksums |
34fdac2d1ce09d7371b43e0317d18924d73ad88cc2d3fd7955814eec050c6c6b
|
|
BLAKE2b-256 checksum How to use checksums |
1c76fa3034c8a5b29c7900efc1e599153dc69758c4b94fcc3194cda2cfce2b16
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 29, 2026.
Transparency logSecurity for sensez 0.4.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 5 files in this release have been uploaded with provenance metadata.
Attestation for sensez-0.4.0-py3-none-win_amd64.whl
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 29, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.














