
shad0w
Compile the decisions your LLM already makes into a certified 2 MB table that answers in microseconds on a CPU.
It learns from your model's own answers, needs no labels, and tells you in writing how often it will disagree.



Live demo · Docs · 2-minute video · Benchmarks
Your app sends small, typed decisions to a big model millions of times: which intent is this, which queue gets this ticket, is this spam, should this agent step run. Every call takes 20–1,500 ms and a round trip to someone else's GPU.
shad0w sits in front of that model like a shadow. It watches the answers, learns the decision, and compiles it into a tiny integer table. Before the table answers anything, it certifies how often it will disagree with your model. On public intent and topic benchmarks, it then served 45–71% of traffic itself, at under 5% certified disagreement and in microseconds. Everything else goes to your model, exactly as before.
import shad0w

sh = shad0w.Shadow("bundle/", teacher=ask_my_llm, log="teacher_log.jsonl")

sh.decide("my card was stolen yesterday")
# Decision(answer='lost_card', source='table', confidence=0.98, certified=True, latency_us=14)
| ~1 µs per decision in C 7–11 µs JS · 15 µs Python |
45–71% of LLM traffic served locally at a certified 5% bound |
0 labels learns from your model's own logged answers |
2 MB one file, no GPU, no network 256 KB still keeps 88.5% |
How it works
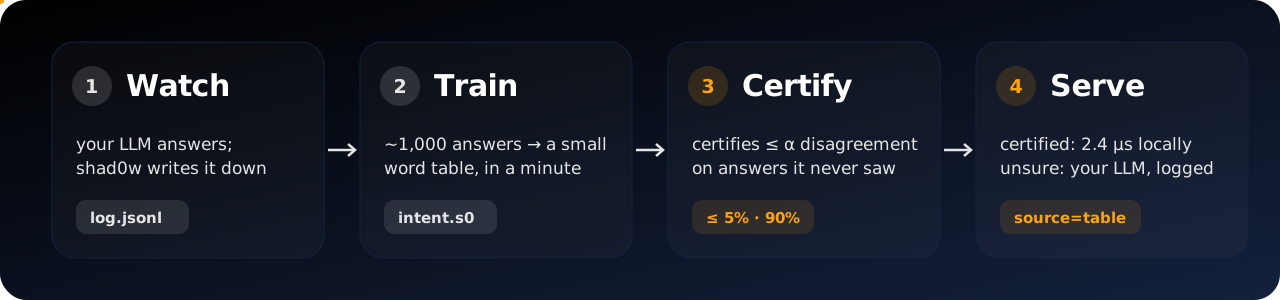
- Shadow. Your model keeps serving. Its answers are logged as
(text, answer)pairs, either by theShadowwrapper or by your own logging. - Compile. The log trains a hashed n‑gram table with int8 weights. There is no tokenizer and no GPU, and it takes seconds to minutes on a laptop.
- Certify. On a held-out slice, a Learn‑then‑Test procedure picks the confidence threshold. Among answers the table serves, disagreement with your model is ≤ α (say 5%), with probability ≥ 1 − δ.
- Serve. Certified answers come back in microseconds, in your process. Everything else goes to your model and is logged, so the share the table can take grows with traffic: 31% → 70% as AG News shadow traffic went from 2k to 100k.
Results
Measured on public datasets. Every number links to its raw result file on the benchmarks page.
| Result | |
|---|---|
| LLM traffic answered locally (7 intent/topic tasks, 2 teachers), certified α = 5% | 45–71%, realised disagreement 3.9–5.7% (mean of 3 seeds) |
| End-to-end accuracy (table + teacher) vs teacher alone | within 1 point on every task; +0.7 with Kev‑0.8B as teacher |
| Mean latency of the cascade, Kev‑0.8B → BANKING77 | 75 ms → 22 ms |
| Offload as shadow traffic grows (AG News, 2k → 100k decisions) | 31% → 70% at α = 5%; 5% → 52% at 2% |
| Per decision | ~1 µs C · 7–11 µs JavaScript · 15 µs Python · 0.19 ms over HTTP |
| Public benchmark (local‑jev‑bench, BANKING77, 20 options) | 89.7% at 0.018 ms on 1 CPU thread; Kev‑0.8B 88% at 57.6 ms; Clef‑flash (9B) 97% at 1,274 ms |
| Out-of-scope queries (CLINC150) separated by confidence | AUROC 0.94 |
Reproduce on your laptop (examples/shadow_demo.py, MIT-licensed teacher, BANKING77) |
69.4% answered locally at α = 5% (realised 4.6%); cascade 67.8% vs teacher 68.0% |
Compared with what you would otherwise do
| Per decision | Runs on | Needs | Bound on what it serves | |
|---|---|---|---|---|
| Keep calling the LLM / decision API | 20–1,500 ms | GPU or vendor API | — | it is the reference |
| Semantic cache (GPTCache, gateway caches) | ms (embed + vector search) | embedding model + store | nothing | similarity threshold, no bound |
| Embedding router (e.g. semantic-router) | ms | embedding model | example utterances | threshold, no bound |
| Distil into a smaller LLM | 10–100 ms | GPU | teacher outputs | none |
| Hand-built fastText / SetFit / Model2Vec | µs–ms | CPU | human labels | none |
| shad0w | 1–15 µs | CPU, in-process, browser, edge | your model's logged answers | finite-sample, against your model |
It is not new science. The certificate is Learn‑then‑Test, in the spirit of Trust or Escalate and BARGAIN. The table is fastText-shaped on purpose. What is new is the packaging: one workflow from shadow logs to a certified, KB-to-MB artifact, with the same decisions in C, Python and JavaScript.
Quick start
pip install "shad0wllm[compile]" # the runtime alone is: pip install shad0wllm (numpy only, C core included)
The package installs as shad0wllm and imports as shad0w. The command-line tool is shad0w.
1. Log your model's answers. Wrap the call you already make. With no bundle yet, every call goes to your model and is logged:
import shad0w

sh = shad0w.Shadow(None, teacher=ask_my_llm, question="intent", log="teacher_log.jsonl")
answer = sh.decide(text).answer          # = ask_my_llm(text), logged
2. Compile and certify once you have 1,000+ lines (10k–100k for high offload):
shad0w init                                        # starter schema.json: the options your model chooses from
shad0w shadow --schema schema.json --data teacher_log.jsonl --teacher my-llm-v3 --alpha 0.05 --out bundle/
shad0w report --bundle bundle/                      # the certificate, in plain words and numbers
3. Serve. Point the wrapper at the bundle. Certified answers come from the table and the rest from your model. 1% of certified answers are spot-checked against your model, so sh.stats() shows live disagreement:
sh = shad0w.Shadow("bundle/", teacher=ask_my_llm, log="teacher_log.jsonl")
4. Re-certify on fresh traffic every week, or when traffic changes:
shad0w certify --bundle bundle/ --data last_week.jsonl
Everywhere else
| JavaScript (Node, browsers, Workers, Deno, Bun), zero dependencies | npm i shad0wllm → const b = await Bundle.load("bundle/"); b.decide(text) |
| HTTP sidecar, any language | shad0w serve --bundle bundle/ → POST /v1/decide |
| C, any language with an FFI | shad0w/_native/reflex.c: s0_load, s0_decide |
| Decorator | @shad0w.cascade("bundle/") on your existing classify function |
| Human labels instead of a teacher | shad0w compile --data labels.jsonl + shad0w calibrate (~300 labels) |
| No teacher, no labels | shad0w compile --unlabeled logs.txt (option names + raw logs, pip install "shad0wllm[logs]") |
Integration recipes for FastAPI, LiteLLM, LangGraph, Cloudflare Workers and the browser are in the docs.
When not to use it
The limits below are measured. Knowing them is what makes the certificate useful.
- Sentiment, tone, emotion. A hashed table tops out near 79% on SST‑2 even with perfect labels. shad0w certifies almost nothing there and defers everything to your model, which is the correct behaviour.
- When you need the most accurate answer. A 9B decision model is 7 points better on the public BANKING77 file, at ~70,000× the latency. Put shad0w in front of such a model, not instead of it.
- The bound is against your model, not the truth. A certified table in front of a wrong model is wrong in the same way. For a bound against the truth, calibrate with ~300 real labels.
- The bound holds on traffic like the calibration slice. A big shift in the request mix can break it. The drift guard flags confidence shifts, the audits watch live disagreement, and
shad0w certifyre-certifies. - Reasoning or world knowledge. It learns surface decisions: intents, routes, topics, policies with distinctive wording.
Documentation
Getting started · Shadow mode guide · Integrations · The certificate, explained · API & CLI · Architecture & file format · Benchmarks · Limitations · FAQ
Contributing
Run it on one of your decisions and share your numbers, including failures. That is the most valuable contribution. Code contributions: see CONTRIBUTING.md.
Citation
@software{chauhan2026shad0w,
  author = {Chauhan, Gaurav},
  title  = {shad0w: certified microsecond decisions compiled from the model you already run},
  year   = {2026},
  url    = {https://github.com/2796gaurav/shad0w}
}
Built by Gaurav Chauhan · Apache-2.0
1 maintainer

Metadata
1 maintainer
Release files for shad0wllm 0.1.1
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | |
|---|---|---|---|
| shad0wllm-0.1.1.tar.gz | 53.8 kB | Details |
Built distributions (wheels)
Total release size: 1.2 MB
Release files / shad0wllm-0.1.1.tar.gz
| Download URL | shad0wllm-0.1.1.tar.gz |
|---|---|
| Size | 53.8 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
c4940a7b9b2f56af044d14633e898c0e2670fc4237bd79d2355c169a4b5af3bd
|
|
BLAKE2b-256 checksum How to use checksums |
9c46fc1b6f0f9d052b3baf50189e5f74e68cd0c4183e182134461fe69c85f6f7
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 7, 2026.
Transparency logRelease files / shad0wllm-0.1.1-cp313-cp313-win_amd64.whl
| Download URL | shad0wllm-0.1.1-cp313-cp313-win_amd64.whl |
|---|---|
| Size | 55.2 kB |
| Tags | CPython 3.13 Windows x86-64 |
|
SHA-256 checksum How to use checksums |
5dc83020d8c56572ba9d4be5fcc41440aad83a046ec4f95dc4638115c1f4d490
|
|
BLAKE2b-256 checksum How to use checksums |
46a8e21ea98f735b72f96151039293ec2741f5a25602d6a71287897692f0f0b8
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 7, 2026.
Transparency logRelease files / shad0wllm-0.1.1-cp313-cp313-manylinux_2_27_x86_64.manylinux_2_28_x86_64.whl
| Download URL | shad0wllm-0.1.1-cp313-cp313-manylinux_2_27_x86_64.manylinux_2_28_x86_64.whl |
|---|---|
| Size | 68.0 kB |
| Tags | CPython 3.13 Linux glibc 2.27+ x86-64 Linux glibc 2.28+ x86-64 |
|
SHA-256 checksum How to use checksums |
5205914040ba700eea7ba89fbeea888b9ab4cc3fea8534bfaf458dc930331340
|
|
BLAKE2b-256 checksum How to use checksums |
513ae4a10ee921b13b5d538031c54cfb5b797532236f61b29b0b1f7359e9c419
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 7, 2026.
Transparency logRelease files / shad0wllm-0.1.1-cp313-cp313-manylinux_2_27_aarch64.manylinux_2_28_aarch64.whl
| Download URL | shad0wllm-0.1.1-cp313-cp313-manylinux_2_27_aarch64.manylinux_2_28_aarch64.whl |
|---|---|
| Size | 69.4 kB |
| Tags | CPython 3.13 Linux glibc 2.27+ ARM64 Linux glibc 2.28+ ARM64 |
|
SHA-256 checksum How to use checksums |
dfb9c9af3fb9556f1d1bbf7c9f8f17967c9f763a05df32a2f1031f59822b3502
|
|
BLAKE2b-256 checksum How to use checksums |
f583b9364e77abe9c540851d89fa56d55d68077c46d6a8e6b898b61d9bc361f2
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 7, 2026.
Transparency logRelease files / shad0wllm-0.1.1-cp313-cp313-macosx_11_0_arm64.whl
| Download URL | shad0wllm-0.1.1-cp313-cp313-macosx_11_0_arm64.whl |
|---|---|
| Size | 52.8 kB |
| Tags | CPython 3.13 macOS 11.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
994477cacf1cf027bd7dd33b6e52e5e75bf14ec8fe11ed5f52860858d80a8f58
|
|
BLAKE2b-256 checksum How to use checksums |
13a3a17e9a005b27a90588244e6ca75433c3f4d2900e87e0ac3c876380044c25
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 7, 2026.
Transparency logRelease files / shad0wllm-0.1.1-cp313-cp313-macosx_10_13_x86_64.whl
| Download URL | shad0wllm-0.1.1-cp313-cp313-macosx_10_13_x86_64.whl |
|---|---|
| Size | 52.5 kB |
| Tags | CPython 3.13 macOS 10.13+ x86-64 |
|
SHA-256 checksum How to use checksums |
3be9f428b4195c18ea6849aecd1805b7f2d139dcfdf341914f7725bfa01efa75
|
|
BLAKE2b-256 checksum How to use checksums |
c5b52ae0509d9b47662eda1715d2d080c3396a7787d4d82fd62a4946415aab4d
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 7, 2026.
Transparency logRelease files / shad0wllm-0.1.1-cp312-cp312-win_amd64.whl
| Download URL | shad0wllm-0.1.1-cp312-cp312-win_amd64.whl |
|---|---|
| Size | 55.2 kB |
| Tags | CPython 3.12 Windows x86-64 |
|
SHA-256 checksum How to use checksums |
a487f437a23cd42c5840053adfad01126422aa9b5198cb0b5cc4cb5c11ae6ee1
|
|
BLAKE2b-256 checksum How to use checksums |
66b0bb37860fbf543474504bccea78a25d0b334c941c463e56bcd3d3b79994e0
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 7, 2026.
Transparency logRelease files / shad0wllm-0.1.1-cp312-cp312-manylinux_2_27_x86_64.manylinux_2_28_x86_64.whl
| Download URL | shad0wllm-0.1.1-cp312-cp312-manylinux_2_27_x86_64.manylinux_2_28_x86_64.whl |
|---|---|
| Size | 67.9 kB |
| Tags | CPython 3.12 Linux glibc 2.27+ x86-64 Linux glibc 2.28+ x86-64 |
|
SHA-256 checksum How to use checksums |
d07030758d18cbaab55fa81cdeb96ac270e368c3620f783309a5f886f534b249
|
|
BLAKE2b-256 checksum How to use checksums |
b664e8d7bbf07ebb2019f237594c41c45bc857643031cfbda463715720637a63
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 7, 2026.
Transparency logRelease files / shad0wllm-0.1.1-cp312-cp312-manylinux_2_27_aarch64.manylinux_2_28_aarch64.whl
| Download URL | shad0wllm-0.1.1-cp312-cp312-manylinux_2_27_aarch64.manylinux_2_28_aarch64.whl |
|---|---|
| Size | 69.3 kB |
| Tags | CPython 3.12 Linux glibc 2.27+ ARM64 Linux glibc 2.28+ ARM64 |
|
SHA-256 checksum How to use checksums |
6a064f47979b9b9e2cb61e36b7ece24fa33cefc196a3c60f9359f15facebe2e7
|
|
BLAKE2b-256 checksum How to use checksums |
d709538346ce737e4fd6e2a08b86ee8f91bfe587ab9c093e131e163579de1076
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 7, 2026.
Transparency logRelease files / shad0wllm-0.1.1-cp312-cp312-macosx_11_0_arm64.whl
| Download URL | shad0wllm-0.1.1-cp312-cp312-macosx_11_0_arm64.whl |
|---|---|
| Size | 52.8 kB |
| Tags | CPython 3.12 macOS 11.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
b0ea42ba73e2cdd1260fafeed9c9f293b8d2dd468bfb27356db50261db478b1f
|
|
BLAKE2b-256 checksum How to use checksums |
e427481533587e562fbe03c5d2879f58735891e9e614211b509b2834afb07b8a
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 7, 2026.
Transparency logRelease files / shad0wllm-0.1.1-cp312-cp312-macosx_10_13_x86_64.whl
| Download URL | shad0wllm-0.1.1-cp312-cp312-macosx_10_13_x86_64.whl |
|---|---|
| Size | 52.5 kB |
| Tags | CPython 3.12 macOS 10.13+ x86-64 |
|
SHA-256 checksum How to use checksums |
a6aa955561e33d499dfba87bee72a6ddf4572c3395001c030ac86f2025c00676
|
|
BLAKE2b-256 checksum How to use checksums |
6034d17d39e7a2d5d17a41c7af123d98136eedcdc504db677930d9b629d668a6
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 7, 2026.
Transparency logRelease files / shad0wllm-0.1.1-cp311-cp311-win_amd64.whl
| Download URL | shad0wllm-0.1.1-cp311-cp311-win_amd64.whl |
|---|---|
| Size | 55.2 kB |
| Tags | CPython 3.11 Windows x86-64 |
|
SHA-256 checksum How to use checksums |
b9e82b83f4db6733495ad546d9536c07756e0703de2795395aa8a6a9118f2a57
|
|
BLAKE2b-256 checksum How to use checksums |
3c05768c321aeb204b5d7622908f15efab27a8d0c8fa595ed40e17ec463d644f
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 7, 2026.
Transparency logRelease files / shad0wllm-0.1.1-cp311-cp311-manylinux_2_27_x86_64.manylinux_2_28_x86_64.whl
| Download URL | shad0wllm-0.1.1-cp311-cp311-manylinux_2_27_x86_64.manylinux_2_28_x86_64.whl |
|---|---|
| Size | 67.8 kB |
| Tags | CPython 3.11 Linux glibc 2.27+ x86-64 Linux glibc 2.28+ x86-64 |
|
SHA-256 checksum How to use checksums |
28dffe8ed1b3ba6b3777019924068aadd41ae958b5ed6ce834410d66c970be5a
|
|
BLAKE2b-256 checksum How to use checksums |
bbe559549588105a136d7642459755426b24c2835469d3fc89061835d2b420d2
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 7, 2026.
Transparency logRelease files / shad0wllm-0.1.1-cp311-cp311-manylinux_2_27_aarch64.manylinux_2_28_aarch64.whl
| Download URL | shad0wllm-0.1.1-cp311-cp311-manylinux_2_27_aarch64.manylinux_2_28_aarch64.whl |
|---|---|
| Size | 69.2 kB |
| Tags | CPython 3.11 Linux glibc 2.27+ ARM64 Linux glibc 2.28+ ARM64 |
|
SHA-256 checksum How to use checksums |
295a853c78532cff0c0863a608feb6a81dd7fd01b6b1a44e05d534464c21a8e0
|
|
BLAKE2b-256 checksum How to use checksums |
e240ea0d4a521d9cfa65199d8dafcfcf183e40380d81156c847311a9836ed9a8
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 7, 2026.
Transparency logRelease files / shad0wllm-0.1.1-cp311-cp311-macosx_11_0_arm64.whl
| Download URL | shad0wllm-0.1.1-cp311-cp311-macosx_11_0_arm64.whl |
|---|---|
| Size | 52.8 kB |
| Tags | CPython 3.11 macOS 11.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
7f8d540b2271615f4ca67b22c0cdfef18906191b9274031ae16ec9d4e109f08b
|
|
BLAKE2b-256 checksum How to use checksums |
d1ff586cb05c19f7e1fb0407383f9b7d0681a1251a1b690265ed47cbaf49e92d
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 7, 2026.
Transparency logRelease files / shad0wllm-0.1.1-cp311-cp311-macosx_10_9_x86_64.whl
| Download URL | shad0wllm-0.1.1-cp311-cp311-macosx_10_9_x86_64.whl |
|---|---|
| Size | 52.6 kB |
| Tags | CPython 3.11 macOS 10.9+ x86-64 |
|
SHA-256 checksum How to use checksums |
dab567e86a7455bdd5783525c92b10966183ab97aa18c6aa4a4e2958c32d4973
|
|
BLAKE2b-256 checksum How to use checksums |
fedb43e26c48215c41aa61a4db190953b74c41ae57b1c8aaf64e8c30499bff67
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 7, 2026.
Transparency logRelease files / shad0wllm-0.1.1-cp310-cp310-win_amd64.whl
| Download URL | shad0wllm-0.1.1-cp310-cp310-win_amd64.whl |
|---|---|
| Size | 55.2 kB |
| Tags | CPython 3.10 Windows x86-64 |
|
SHA-256 checksum How to use checksums |
f1ca1f68de410bbee7d391e634c4e1aee5dcd02488336fe6d0ffb50903541712
|
|
BLAKE2b-256 checksum How to use checksums |
c65d471bc2e66b2a59ea2ff079e014ae26de85934baf327ae8ca2d847e4abb36
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 7, 2026.
Transparency logRelease files / shad0wllm-0.1.1-cp310-cp310-manylinux_2_27_x86_64.manylinux_2_28_x86_64.whl
| Download URL | shad0wllm-0.1.1-cp310-cp310-manylinux_2_27_x86_64.manylinux_2_28_x86_64.whl |
|---|---|
| Size | 67.7 kB |
| Tags | CPython 3.10 Linux glibc 2.27+ x86-64 Linux glibc 2.28+ x86-64 |
|
SHA-256 checksum How to use checksums |
53b52b4d330e203544f5bec6644bcd87d8745a667df9323b66163b8d6c92e82e
|
|
BLAKE2b-256 checksum How to use checksums |
6490b0703bc49231018e5ec70739b7e542a58d29723aa8338220c7bf8ee0bc21
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 7, 2026.
Transparency logRelease files / shad0wllm-0.1.1-cp310-cp310-manylinux_2_27_aarch64.manylinux_2_28_aarch64.whl
| Download URL | shad0wllm-0.1.1-cp310-cp310-manylinux_2_27_aarch64.manylinux_2_28_aarch64.whl |
|---|---|
| Size | 69.1 kB |
| Tags | CPython 3.10 Linux glibc 2.27+ ARM64 Linux glibc 2.28+ ARM64 |
|
SHA-256 checksum How to use checksums |
697859de8831c2141934c051208f2602cfa209e54c1d8cf190cd162bf5e795a7
|
|
BLAKE2b-256 checksum How to use checksums |
632594812e9840b51882803716185d9014c97d536bb156412e52b344b75b912d
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 7, 2026.
Transparency logRelease files / shad0wllm-0.1.1-cp310-cp310-macosx_11_0_arm64.whl
| Download URL | shad0wllm-0.1.1-cp310-cp310-macosx_11_0_arm64.whl |
|---|---|
| Size | 52.8 kB |
| Tags | CPython 3.10 macOS 11.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
b4cda3ac844b9e3b211588f7907af7ef5a37399e06a4235b000cb10904d08484
|
|
BLAKE2b-256 checksum How to use checksums |
d4489b238f303f21e822136fdc790cf20dcbf1c969f9568c31a535e077c7d49b
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 7, 2026.
Transparency logRelease files / shad0wllm-0.1.1-cp310-cp310-macosx_10_9_x86_64.whl
| Download URL | shad0wllm-0.1.1-cp310-cp310-macosx_10_9_x86_64.whl |
|---|---|
| Size | 52.6 kB |
| Tags | CPython 3.10 macOS 10.9+ x86-64 |
|
SHA-256 checksum How to use checksums |
96c108ffc09ec1169f26825368f10cd61fab0d066a8b05c7840c57b79e3a2c4c
|
|
BLAKE2b-256 checksum How to use checksums |
3c05c710d33abfb7045b14ac4e575dec37515f2e76906eedbf4e9ed420e2892b
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 7, 2026.
Transparency log













