
sharpit





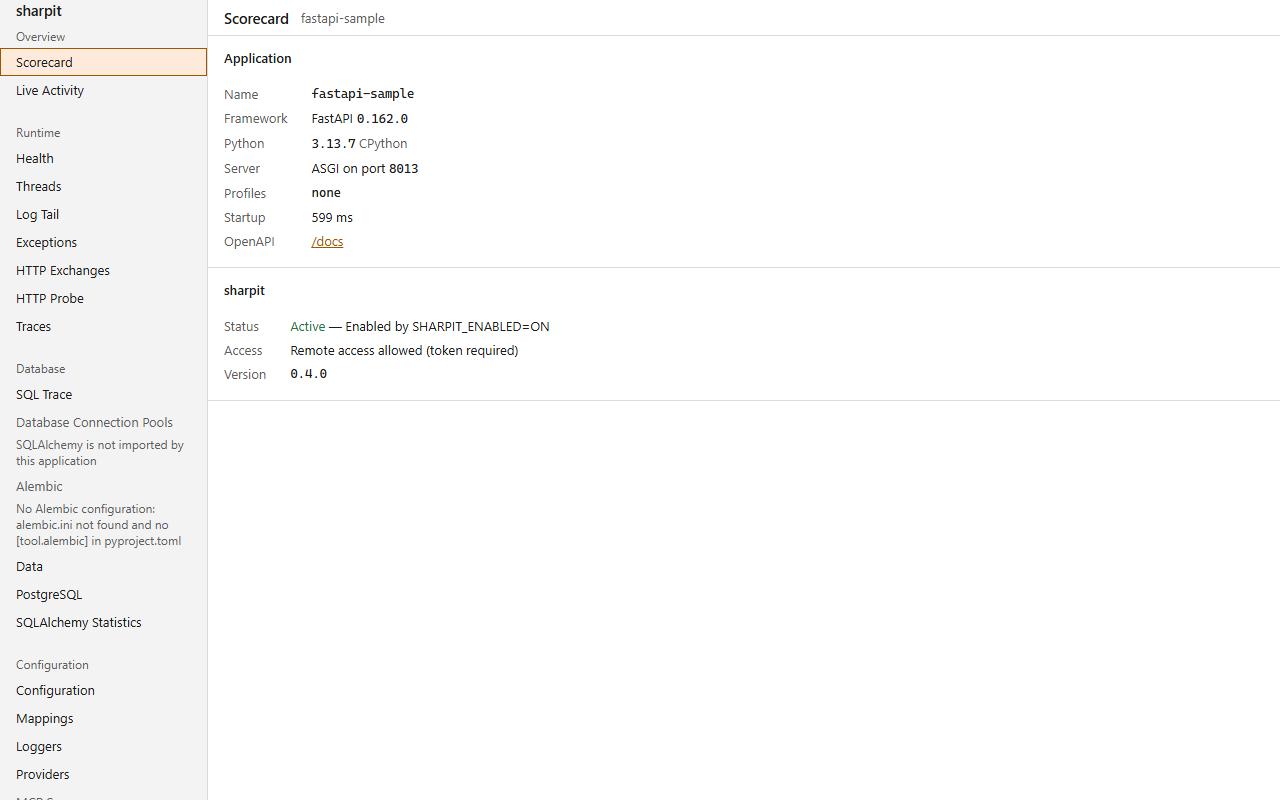
An embedded, local-only developer console for FastAPI apps. One call mounts a web console at /sharpit and a
JSON API at /sharpit/api inside your own app, so a running service becomes understandable in minutes: its
configuration and where each value came from, every route, the dependency providers, loggers you can retune live,
and a vulnerability scan of the installed packages.
sharpit is a Python/FastAPI port of BootUI by Julien Dubois (Apache-2.0), the Spring Boot developer console. It ports BootUI's design goals, JSON contract and test cases; the UI is new.
Status: alpha (0.2.0, FastAPI only). Django and Flask are not supported. See CHANGELOG.md.
Install
sharpit is not on PyPI yet. Install it from git:
pip install "sharpit @ git+https://github.com/ffroliva/sharpit.git"
# or
uv add "sharpit @ git+https://github.com/ffroliva/sharpit.git"
Python 3.12+. Runtime dependencies are only starlette>=0.44 and packaging>=23. Optional extras:
| Extra | Adds | Why |
|---|---|---|
sharpit[fastapi] |
fastapi>=0.115 |
the supported host |
sharpit[settings] |
pydantic-settings>=2.4 |
the Config panel shows which source each value came from |
Quickstart
from fastapi import FastAPI
import sharpit

app = FastAPI()

# Register your application's middleware first:
# app.add_middleware(...)

# Install sharpit after your app's middleware:
sharpit.install(app)  # mounts /sharpit and /sharpit/api
Call sharpit.install(app) after adding your own middleware. Starlette builds middleware from the outside in, so
calling install() last ensures sharpit's capture middleware sits outside your application middleware. This lets sharpit
measure total request durations and record unhandled errors correctly.
Run it with a dev signal and open http://127.0.0.1:8000/sharpit/:
fastapi dev app.py # or: uvicorn app:app --reload
Keyword arguments for sharpit.install():
engines: optional sequence of SQLAlchemyEngineorAsyncEngineinstances to monitor in connection pools and health checks (e.g.engines=[engine]). If omitted, engines are discovered automatically on first connection.health_checks: optional mapping of check names to zero-argument callables (e.g.health_checks={"cache": ping_cache}).alembic_config: optional path toalembic.ini(default"alembic.ini").settings: optional pydantic-settings instance or sequence of instances to show configuration provenance.
Other options are keyword arguments or environment variables, see Settings.
If /sharpit answers 404, read Activation: sharpit stays off unless a dev signal turns it on.
Documentation
The full documentation is at https://ffroliva.github.io/sharpit/:
- Activation: when sharpit turns on, and why a plain
uvicorn app:appgives 404 - Panels: what each panel shows
- MCP for AI agents: the read-only MCP endpoint and its 18 tools
- Settings: every environment variable and
install()keyword - Safety model: local-only guard, tokens, masking, proxies and workers
- How it works and Deviations from BootUI
License
Apache License 2.0. See LICENSE and NOTICE. sharpit is derived from BootUI, Copyright Julien Dubois.
1 maintainer

Metadata
1 maintainer
Release files for sharpit 0.2.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| sharpit-0.2.0.tar.gz | 602.4 kB | With provenance | Details for sharpit-0.2.0.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| sharpit-0.2.0-py3-none-any.whl | Python 3 | none | any | Details for sharpit-0.2.0-py3-none-any.whl |
Total release size: 837.6 kB
Release files / sharpit-0.2.0.tar.gz
| Download URL | sharpit-0.2.0.tar.gz |
|---|---|
| Size | 602.4 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
f861353d7366f7507c6a483e5d6f38a9605ecfdff8d3201fb675d5b38801a710
|
|
BLAKE2b-256 checksum How to use checksums |
0f9d786fbd94d909370cef1cb05b643c29def4cd28f6568e751fe1b2428827b6
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 1, 2026.
Transparency logRelease files / sharpit-0.2.0-py3-none-any.whl
| Download URL | sharpit-0.2.0-py3-none-any.whl |
|---|---|
| Size | 235.1 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
fcd393bbdccbd5c1a09bb71d19e2c781592800d1cda24e69b7121ffb05faa3a8
|
|
BLAKE2b-256 checksum How to use checksums |
5a69d06958b60890e9c942e87394e09f693f6c7ab62ef72005d0e25afcf70d72
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 1, 2026.
Transparency logSecurity for sharpit 0.2.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 2 files in this release have been uploaded with provenance metadata.
Attestation for sharpit-0.2.0.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 1, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














