
Stop guessing how your tables connect




smartjoin helps you understand how unfamiliar datasets fit together — without schema docs, manual SQL detective work, or opaque guesses.
It scans structured data, profiles columns, discovers likely keys, infers candidate joins, and generates an interactive explorer so you can inspect the results.
Supports .csv, .xlsx, .json, .parquet input files.
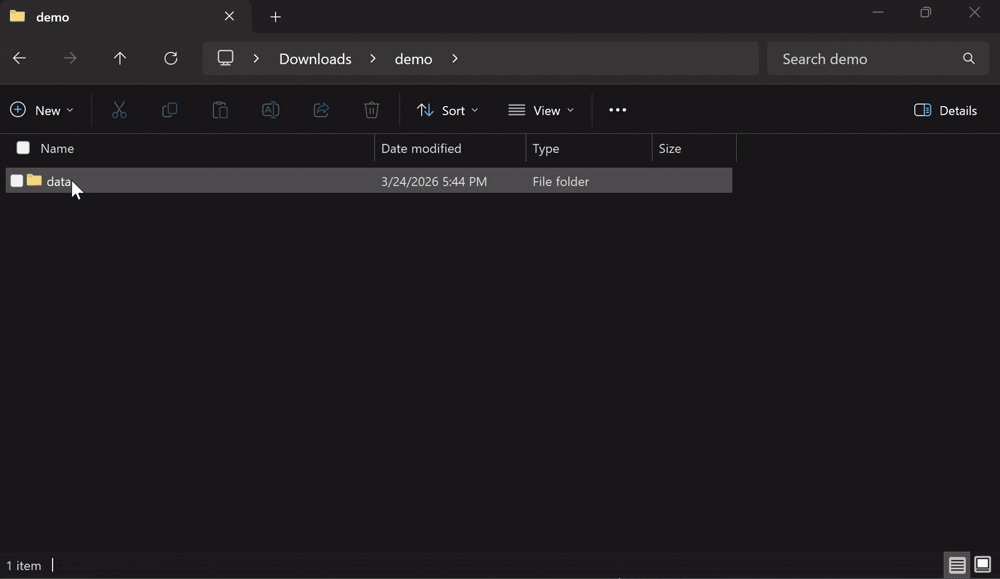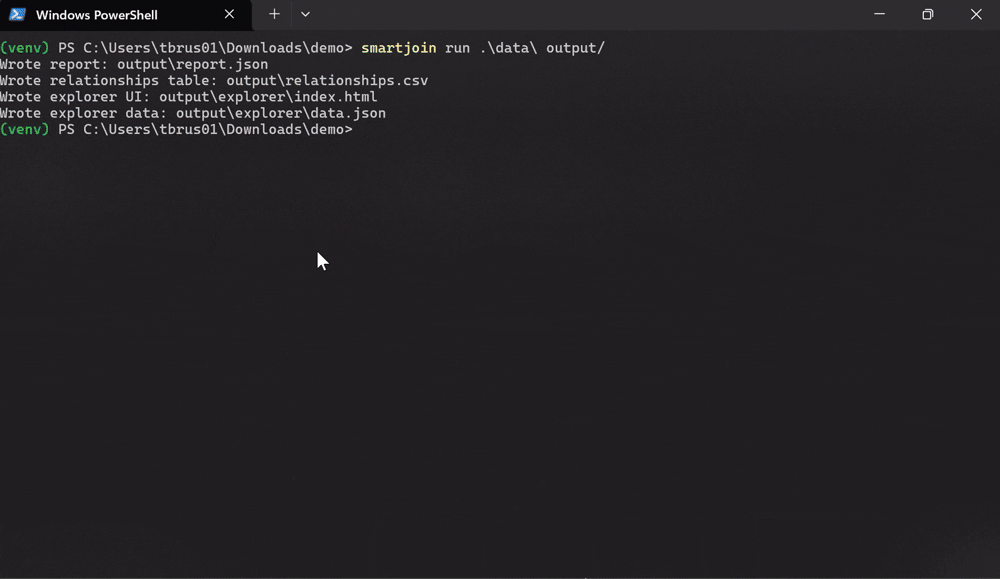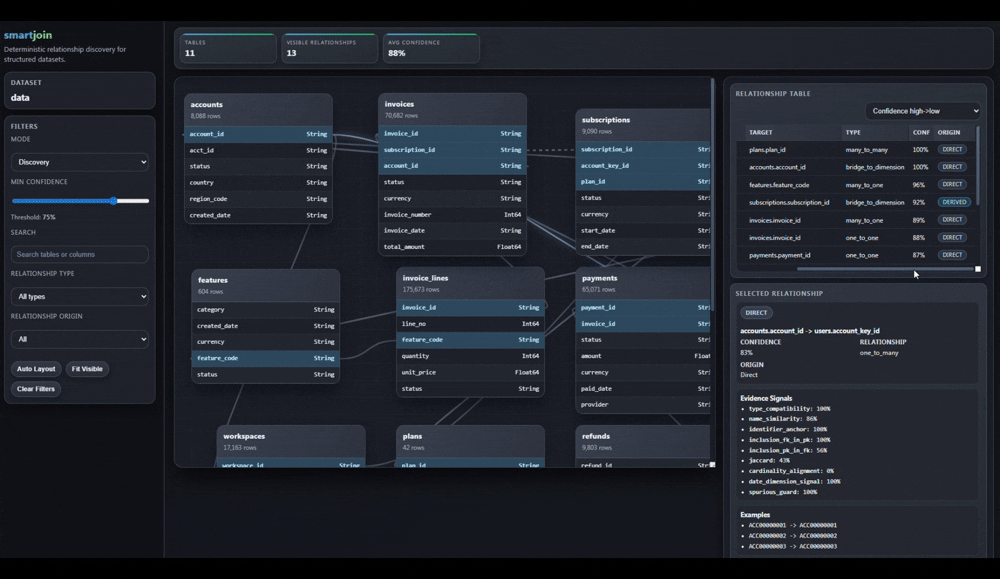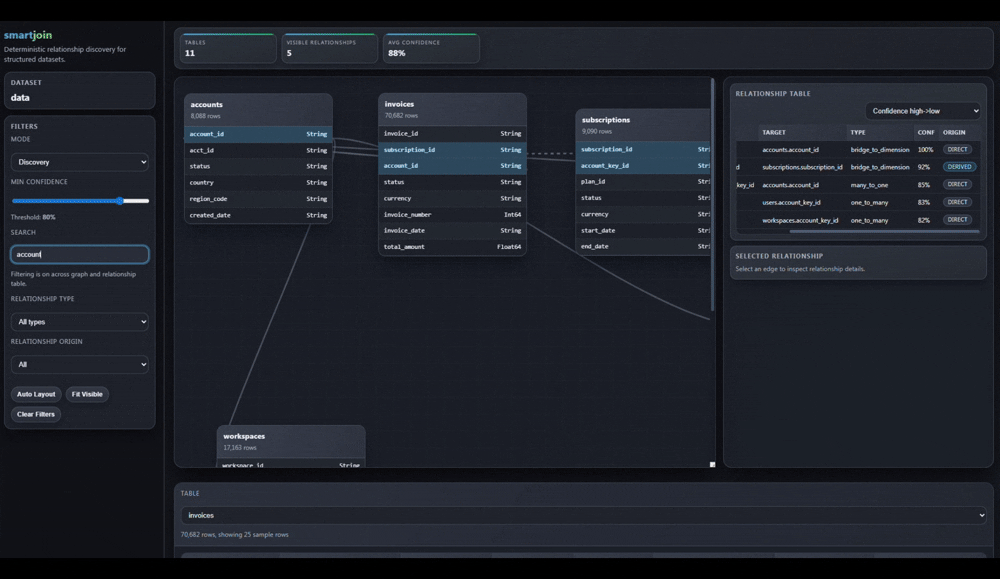
Example
Given a folder like:
orders.csvcustomers.xlsxpayments.parquetshipments.json
smartjoin can infer relationships such as:
| Source | Target | Type | Confidence | Origin |
|---|---|---|---|---|
orders.customer_id |
customers.id |
many_to_one |
98% |
Direct |
payments.order_id |
orders.order_id |
many_to_one |
95% |
Derived |
shipments.order_ref |
orders.order_id |
one_to_one |
89% |
Direct |
Quickstart
Installation
pip install smartjoin-py
Run
smartjoin run <path> <out_dir>
This analyzes the structured datasets in <path> and writes results to <out_dir>.
Outputs
report.json— full structured analysis outputrelationships.csv— flat table of discovered joins and scoring signalsexplorer/index.html— interactive explorer UIexplorer/data.json— explorer payload
Generate demo datasets
To explore smartjoin on deterministic synthetic data:
smartjoin generate-test-datasets --output-dir <output-dir>
Limitations
smartjoin identifies candidate relationships across structured datasets. It does not guarantee semantic correctness.
Always review inferred joins before using them downstream. Domain meaning may still require human interpretation, and output quality depends on the structure and consistency of the input data.
Roadmap
Future development may include:
- stronger semantic matching across columns and tables
- optional AI-assisted reasoning and scoring
- improved explorer and debugging capabilities
- broader support for real-world edge cases and heterogeneous datasets
Contributing
See CONTRIBUTING.md.
License
Licensed under the MIT License
1 maintainer

Metadata
1 maintainer
Release files for smartjoin-py 0.1.2
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| smartjoin_py-0.1.2.tar.gz | 8.1 MB | With provenance | Details for smartjoin_py-0.1.2.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| smartjoin_py-0.1.2-py3-none-any.whl | Python 3 | none | any | Details for smartjoin_py-0.1.2-py3-none-any.whl |
Total release size: 8.2 MB
Release files / smartjoin_py-0.1.2.tar.gz
| Download URL | smartjoin_py-0.1.2.tar.gz |
|---|---|
| Size | 8.1 MB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
f5717c8d4c3247a89e3d6cf3a7aacc811125377964728e4d456959726bb152d9
|
|
BLAKE2b-256 checksum How to use checksums |
638aecdbc57454db922d50c1eaa9eedc8f8b83330db4c3c0c9d4286acb53ea84
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Mar 25, 2026.
Transparency logRelease files / smartjoin_py-0.1.2-py3-none-any.whl
| Download URL | smartjoin_py-0.1.2-py3-none-any.whl |
|---|---|
| Size | 89.3 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
04917c4bd188cf0d9418aed2fbdfa46befb11d107cb2fa23bfe26036a9c41c30
|
|
BLAKE2b-256 checksum How to use checksums |
6f968668100c3f7ed728cbffcd6f337c2e5fa81fad6dc9bb6efa6bcfd49038df
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Mar 25, 2026.
Transparency logSecurity for smartjoin-py 0.1.2
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 2 files in this release have been uploaded with provenance metadata.
Attestation for smartjoin_py-0.1.2.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Mar 25, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














