
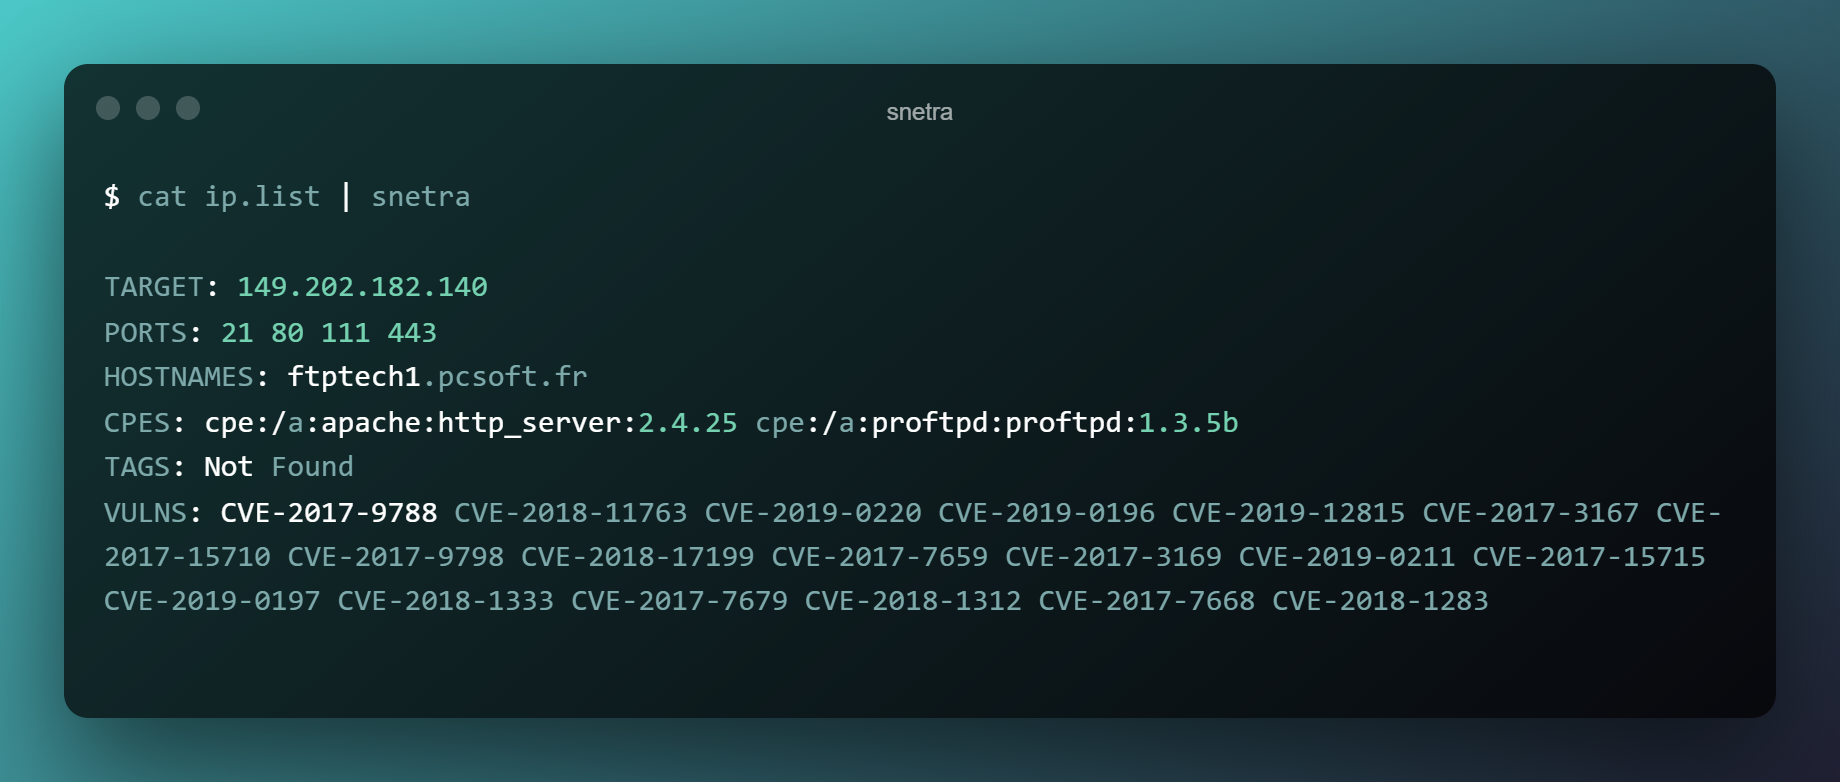
A python based script which takes IPs as stdin and scans for open ports and vulnerabilities using shodan-internetdb
Note: I made it just to check if I implement
https://gitlab.com/shodan-public/nrichin python or not.
InternetDB
The InternetDB API provides a fast way to see the open ports for an IP address. It gives a quick, at-a-glance view of the type of device that is running behind an IP address to help you make decisions based on the open ports.
Installation
$ pip3 install snetra
Usage
$ cat ip.list | snetra
Inspired from: https://gitlab.com/shodan-public/nrich
1 maintainer

Metadata
1 maintainer
Release files for snetra 1.1
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| snetra-1.1.tar.gz | 2.5 kB | Without provenance | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| snetra-1.1-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 5.0 kB
Release files / snetra-1.1.tar.gz
| Download URL | snetra-1.1.tar.gz |
|---|---|
| Size | 2.5 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
e82b3a886473c3b5e88c2b251b6ae3df038bf1430e30cbffc2a54d19a6b4fde9
|
|
BLAKE2b-256 checksum How to use checksums |
d280b8693914d55502ebf7f1a6cedac3fa56b1a8045c87ecd88e78fc2782c5cf
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/3.7.1 importlib_metadata/4.8.2 pkginfo/1.8.2 requests/2.27.1 requests-toolbelt/0.9.1 tqdm/4.36.1 CPython/3.8.10
|
Release files / snetra-1.1-py3-none-any.whl
| Download URL | snetra-1.1-py3-none-any.whl |
|---|---|
| Size | 2.6 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
028d84afef38572d0055d11b5b165a431d9ed5d898ce708057cf47644912f0a3
|
|
BLAKE2b-256 checksum How to use checksums |
4635d45527e6e7343360a0a27e35bdc996535e1f465f47e2127543581fbdff2a
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/3.7.1 importlib_metadata/4.8.2 pkginfo/1.8.2 requests/2.27.1 requests-toolbelt/0.9.1 tqdm/4.36.1 CPython/3.8.10
|
Security for snetra 1.1
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.














