
Sourcery Rules Generator
This is an experimental project. It might become a part of the Sourcery CLI.
Sourcery Rules Generator creates architecture rules for your project.
The generated rules can be used by Sourcery to review your project's architecture.
Currently, the project can create dependency rules.
Usage
You can create Sourcery rules based on a template with the command:
sourcery-rules <TEMPLATE-NAME> create
Supported templates:
- dependencies
- naming / voldemort: avoid some names
- naming / name vs type mismatch (coming soon)
- performance / expensive loop
For example:
sourcery-rules dependencies create
Create Dependencies Rules
With the dependencies template, you can create rules to check the dependencies:
- between the packages of your application
- to external packages.
Let's say your project has an architecture like this:
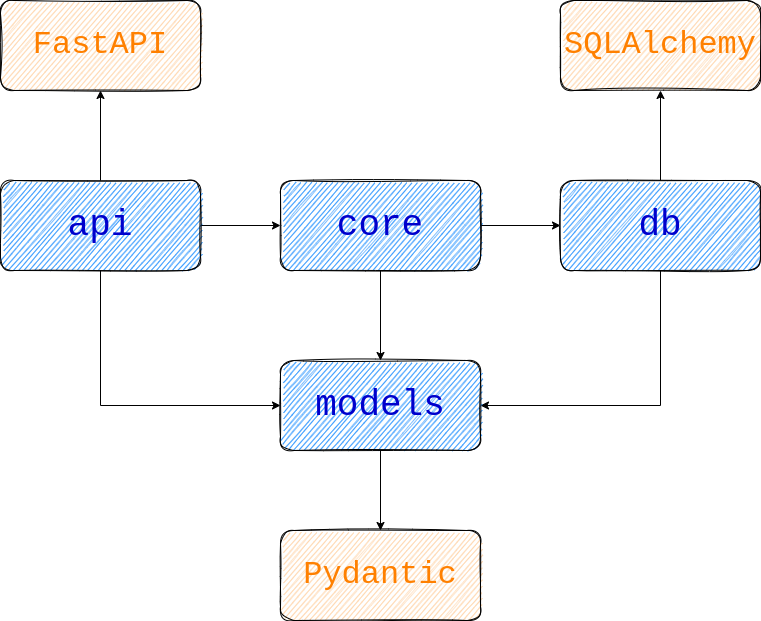
You can create rules to ensure:
- no other package imports
api - only
apiimportscore - only
dbimportSQLAlchemy - etc.
Run the command:
sourcery-rules dependencies create
You'll be prompted to provide:
- a package name
- the packages that are allowed to import the package above
The 1st parameter is the fully qualified name of a package or module.
It can be a package within your project or an external dependency.
The 2nd parameter is optional.
You have the following possibilities:
- 0 allowed importer (e.g. for packages like
api,cli). Leave this parameter empty. - 1 allowed importer. Provide the importer package's fully qualified name.
- Multiple allowed importers. Provide multiple fully qualified package names separated by a comma
,
=>
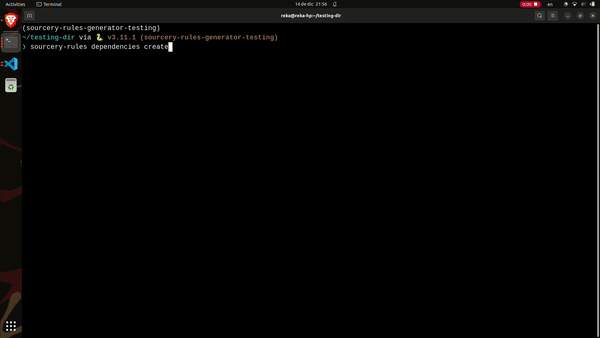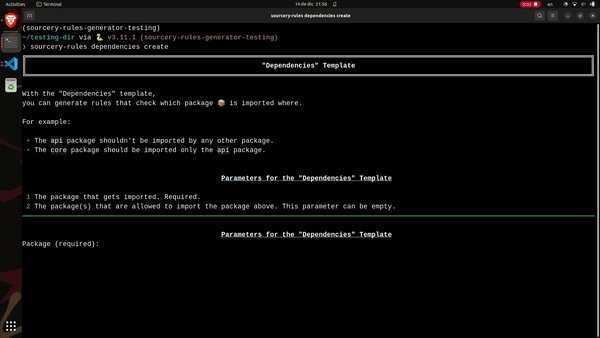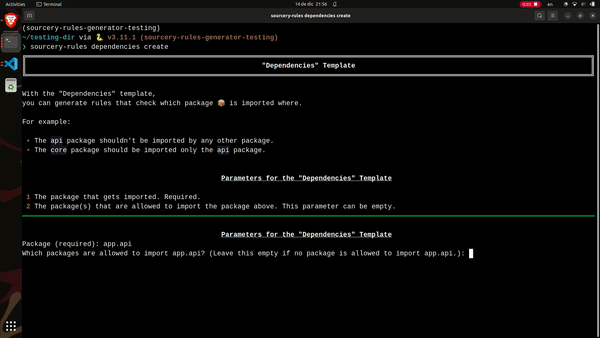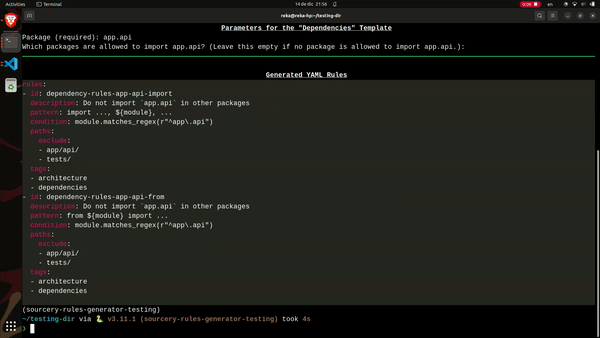
2 rules will be generated:
- 1 for
importstatements - 1 for
from ... importstatements
Every generated rule allows imports:
- within the package itself
- in tests
Dependencies Use Cases
Internal Dependencies Between the Packages of a Project
- Law of Demeter: Packages should talk only to their "direct neighbors".
- A mature package shouldn't depend on a less mature package
- A core package shouldn't depend on a customer-specific package
Thanks to w_t_payne and hbrn for their input in this HackerNews discussion 😃
External Dependencies
- Gateway pattern: Ensure that only a dedicated package of your software communicates with an external dependency.
- Ensure that a deprecated library isn't used
This blog post shows a 3-step method of defining dependency rules:
- Draw a diagram showing the optimal dependencies between your packages.
- Phrase some rules in a human language based on the diagram: Which package should depend on which?
- Translate the rules into code with Sourcery Rules Generator.
Create Voldemort Rules
With a "voldemort" template, you can create rules that ensure that a specific name isn't used in your code.
For example:
- The word
annualshouldn't be used, because the preferred term isyearly. - The word
utilshouldn't be used, because it's overly general.
You can create a "voldemort" rule with the command:
sourcery-rules voldemort create
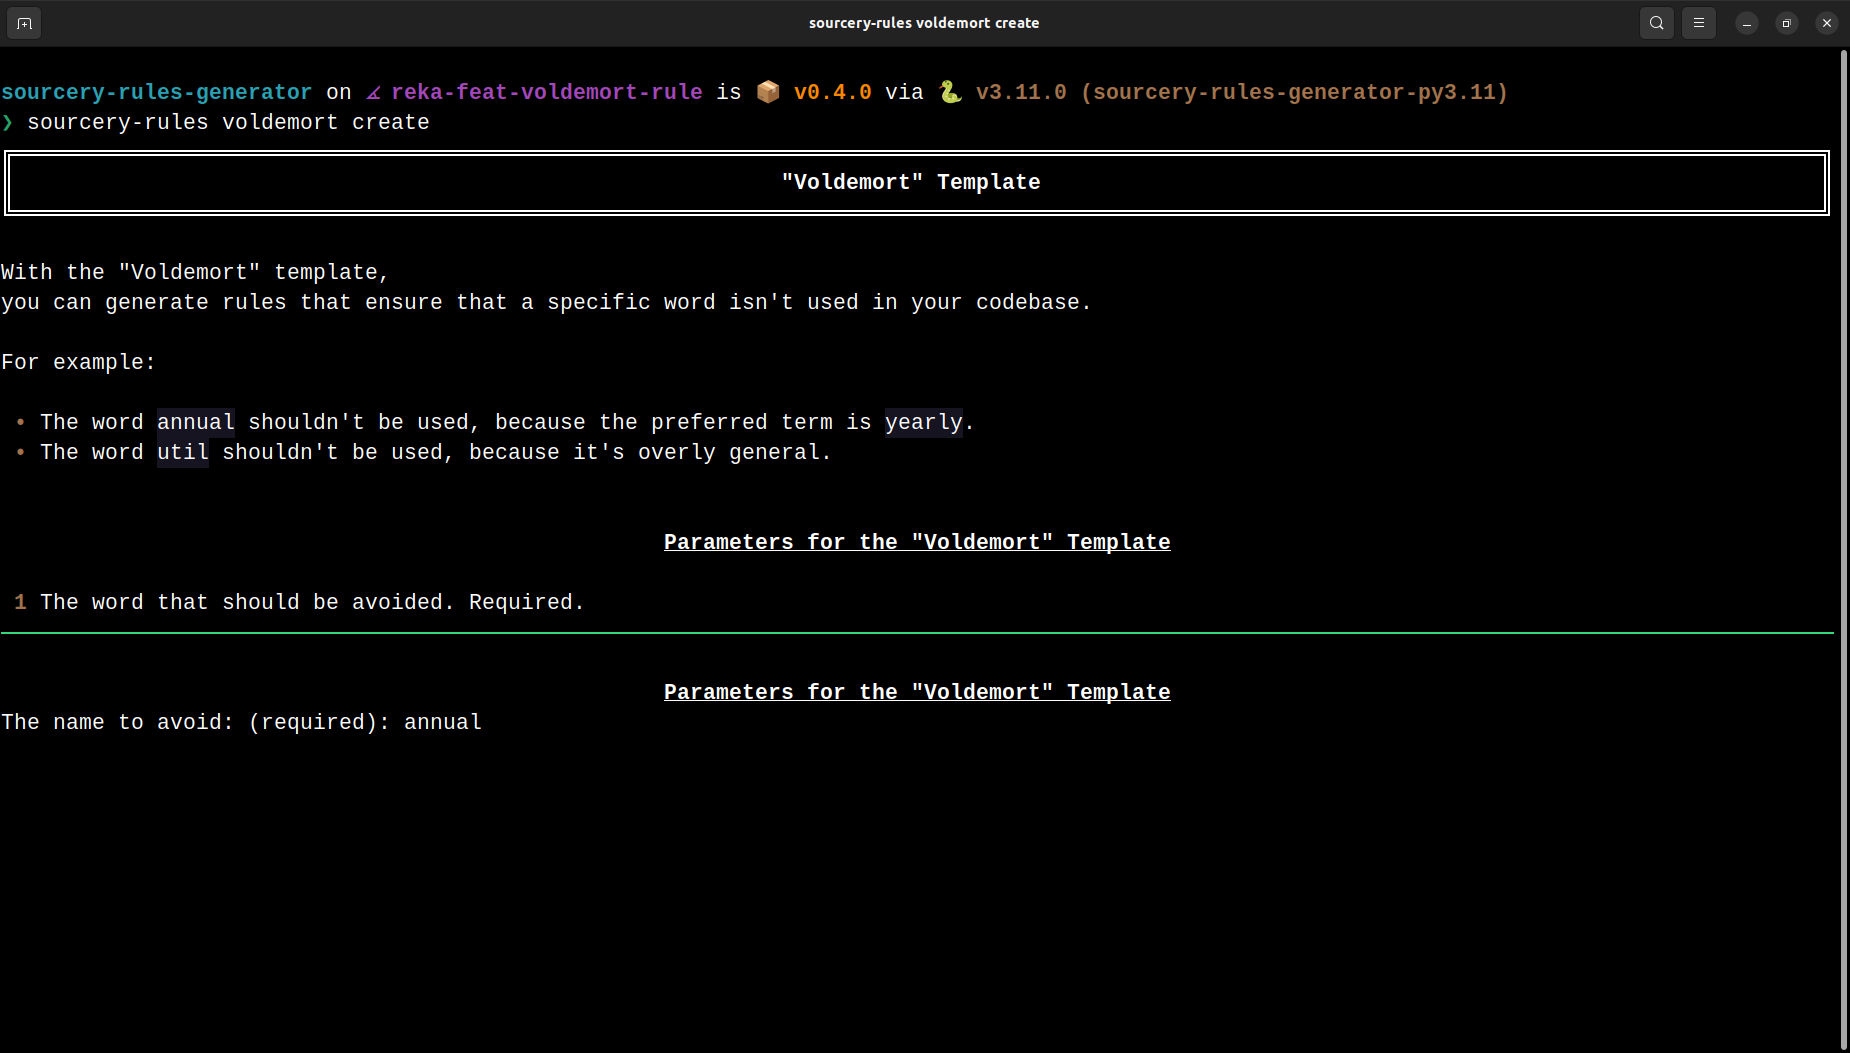
You'll be prompted to provide:
- the name that you want to avoid
=>
5 rules will be generated:
- function names
- function arguments
- class names
- variable declarations
- variable assignments
Expensive Loop
Loops often cause performance problems. Especially, if they execute expensive operations: talking to external systems, complex calculations.
sourcery-rules expensive-loop create
You'll be prompted to provide:
- the fully qualified name of the function that shouldn't be called in loops
=>
2 rules will be generated:
- for
forloops - for
whileloops
Using the Generated Rules
The generated rules can be used by Sourcery to review your project.
If you copy the generated rules into your project's .sourcery.yaml, Sourcery will use them automatically.
All the generated rules have the tag architecture. Once you've copied them to your .sourcery.yaml, you can run them with:
sourcery review --enable architecture .
1 maintainer

Metadata
1 maintainer
Release files for sourcery-rules-generator 0.6.1
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| sourcery_rules_generator-0.6.1.tar.gz | 9.5 kB | Without provenance | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| sourcery_rules_generator-0.6.1-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 21.2 kB
Release files / sourcery_rules_generator-0.6.1.tar.gz
| Download URL | sourcery_rules_generator-0.6.1.tar.gz |
|---|---|
| Size | 9.5 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
53b08260d578e251e706d0baaa00564f2b80ff93809730c2e85b2186b6c10503
|
|
BLAKE2b-256 checksum How to use checksums |
d757223ef4930a98a4b4a89db88e34742aadb3757cbaef4d9fb88002c845260a
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
poetry/1.2.2 CPython/3.11.0 Linux/5.19.0-35-generic
|
Release files / sourcery_rules_generator-0.6.1-py3-none-any.whl
| Download URL | sourcery_rules_generator-0.6.1-py3-none-any.whl |
|---|---|
| Size | 11.7 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
674c1201b7b7a441f7bcfb30cacaa1fb50cf97765e19d17d1164d5389e82ba1c
|
|
BLAKE2b-256 checksum How to use checksums |
6c23473fd8372b28bf1be5f9007aee52305b3148695f9e3bf79687b0768ff954
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
poetry/1.2.2 CPython/3.11.0 Linux/5.19.0-35-generic
|
Security for sourcery-rules-generator 0.6.1
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.














