
sphinx-autodoc-typehints


This Sphinx extension reads the
type hints of the code autodoc documents and writes them into the
parameter and return fields, so you state each type once, in the code. It links every part of a type to its
documentation, and resolves names your code imports only for type checkers (inside an if TYPE_CHECKING: block) or
declares in .pyi stub files. It also documents @overload variants and default values, and types Google and NumPy
style docstrings written for napoleon or numpydoc.
pip install sphinx-autodoc-typehints
# conf.py: load autodoc first, then this extension
extensions = ["sphinx.ext.autodoc", "sphinx_autodoc_typehints"]
Why not Sphinx's built-in autodoc_typehints?
Sphinx's
autodoc_typehints = "description"
already moves annotations into the parameter and return fields, links them, and works with napoleon docstrings and type
comments. If your annotations resolve at runtime and you use Sphinx fields or napoleon, that setting may be enough.
Show example code and configuration
The same demo.py below renders differently with each option. It uses typing-extensions for Doc. Both builds use
.. automodule:: demo with :members:. The left adds typehints_defaults = "braces" and
always_document_param_types = True to the configuration above; the right loads only sphinx.ext.autodoc with
autodoc_typehints = "description".
from __future__ import annotations

from typing import Annotated, Literal, NotRequired, TypedDict, Unpack, overload

from typing_extensions import Doc


class Options(TypedDict):
    """Optional controls for a request."""

    retries: NotRequired[int]
    trace: NotRequired[bool]


@overload
def fetch(path: str, *, mode: Literal["text"], **options: Unpack[Options]) -> str: ...


@overload
def fetch(path: str, *, mode: Literal["bytes"], **options: Unpack[Options]) -> bytes: ...


def fetch(
    path: Annotated[str, Doc("resource path")],
    *,
    mode: Literal["text", "bytes"] = "text",
    **options: Unpack[Options],
) -> str | bytes:
    """Fetch a resource.

    :keyword retries: attempts after a failure
    :keyword trace: log each request
    """
    return "" if mode == "text" else b""
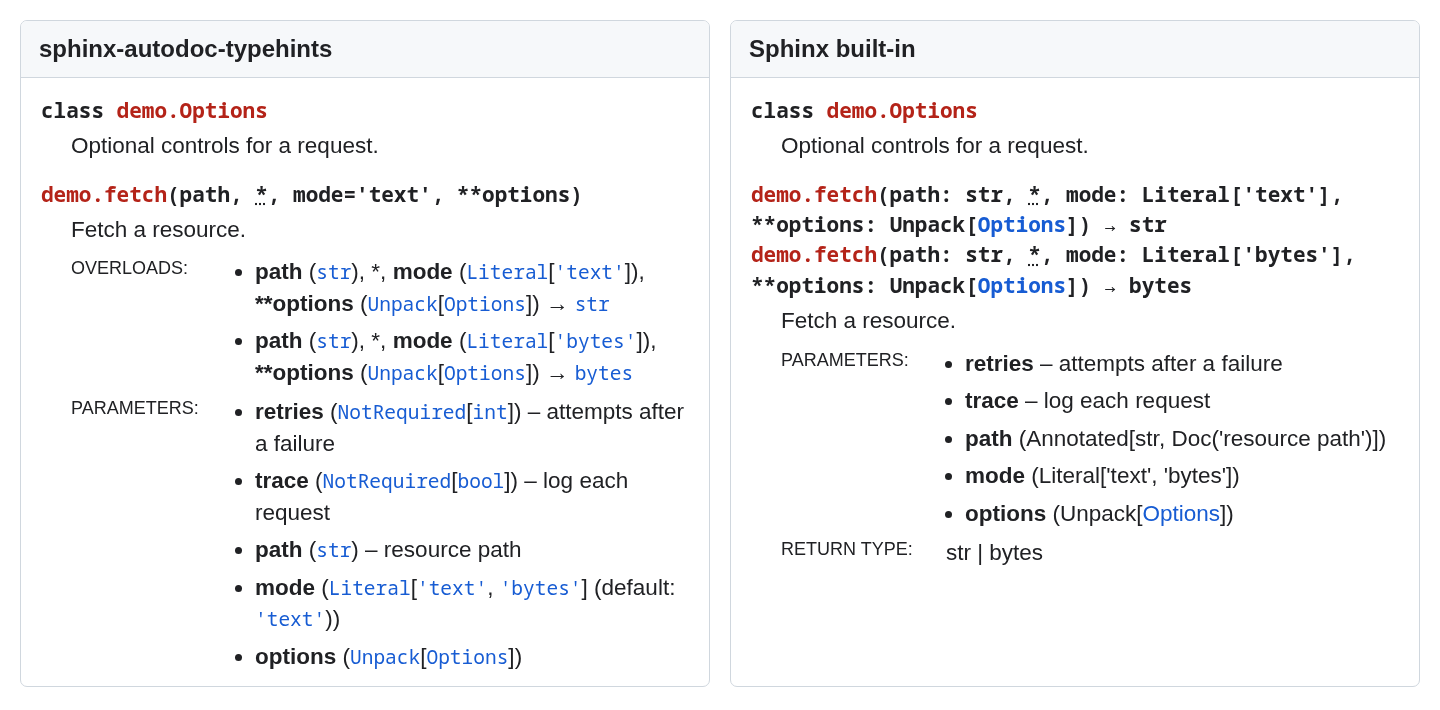
The live TypedDict example lets you change the configuration and inspect its output. See the examples for each difference:
- Names imported under
if TYPE_CHECKING:link to their real module (decimal.Decimal, not a bareDecimal). - Types from
.pyistubs fill in functions that carry no annotations, such as those of a C extension. **kwargs: Unpack[TypedDict]gets keyword fields typed from theTypedDictentries.Annotated[..., Doc(...)]puts descriptions from annotations into the parameter fields.- numpydoc
Parameterssections get types in place, rather than in a second list. @overloadvariants get anOverloadsfield, and default values appear next to the types.@deprecatednotices,@overridelinks, and property setter types add details beyond parameter types.
The full comparison lists the differences, and the live examples show each module rendered both ways.
The typing features gallery shows source and rendered output for each construct. The documentation also has a tutorial, how-to guides and the option reference; CONTRIBUTING.md explains how to work on the extension.
2 maintainers


Metadata
2 maintainers
Release files for sphinx-autodoc-typehints 3.17.4
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| sphinx_autodoc_typehints-3.17.4.tar.gz | 511.4 kB | With provenance | Details for sphinx_autodoc_typehints-3.17.4.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| sphinx_autodoc_typehints-3.17.4-py3-none-any.whl | Python 3 | none | any | Details for sphinx_autodoc_typehints-3.17.4-py3-none-any.whl |
Total release size: 652.0 kB
Release files / sphinx_autodoc_typehints-3.17.4.tar.gz
| Download URL | sphinx_autodoc_typehints-3.17.4.tar.gz |
|---|---|
| Size | 511.4 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
a5ddd545192380292f13dd9fc232717a0925fbc66617bc51b3db1e0480db0fec
|
|
BLAKE2b-256 checksum How to use checksums |
9ea9cfe13ff89678c6d310a8a9060333b7823bae1dbce9615c7032be89aaec20
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 27, 2026.
Transparency logRelease files / sphinx_autodoc_typehints-3.17.4-py3-none-any.whl
| Download URL | sphinx_autodoc_typehints-3.17.4-py3-none-any.whl |
|---|---|
| Size | 140.6 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
251271a49e46573c2e752bcc92dae232def822a2c9983272cb04d282eadc2bfa
|
|
BLAKE2b-256 checksum How to use checksums |
fa6640004fe2aea60edc4800328599dd115b3058f79bf148be1746349281f308
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 27, 2026.
Transparency logSecurity for sphinx-autodoc-typehints 3.17.4
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 2 files in this release have been uploaded with provenance metadata.
Attestation for sphinx_autodoc_typehints-3.17.4.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 27, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














