
splotter


Read SPEC scan files from the command line: list scans, pull values by column name, look up metadata and draw mesh maps that combine several scans.
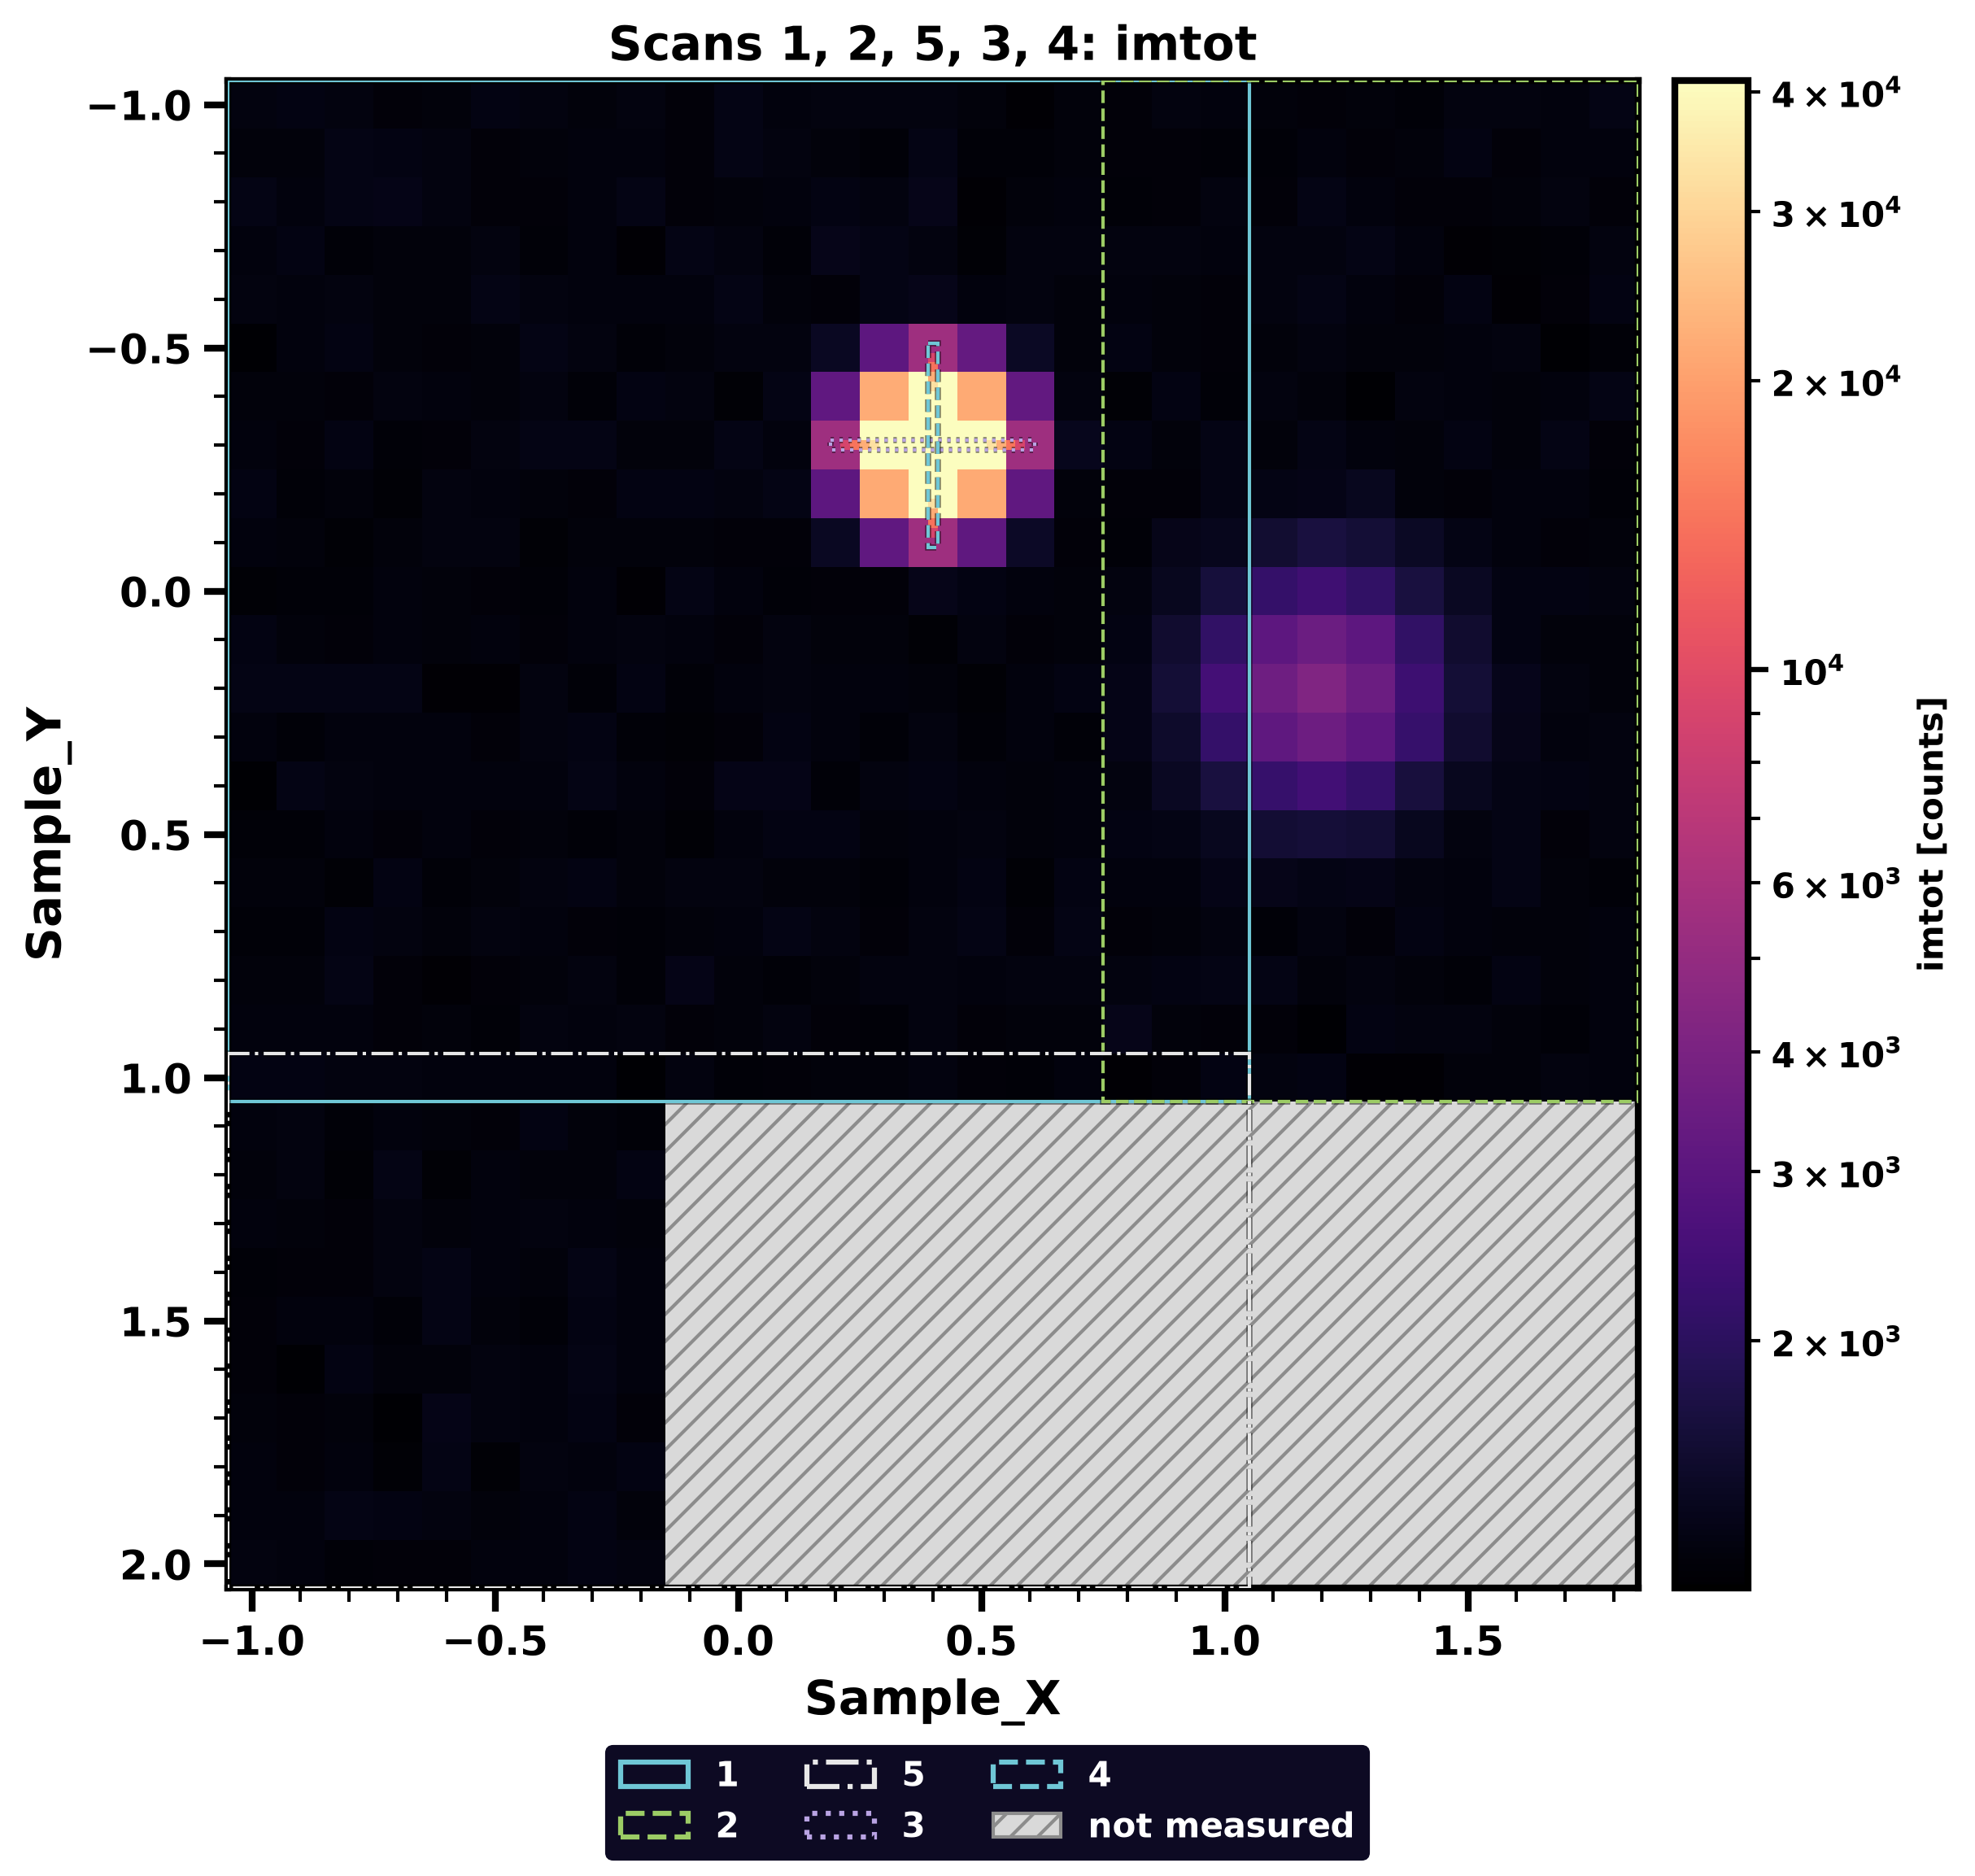
Three meshes and two line scans of the made-up file from splotter demo, on one map (reproduce the figure).
The name comes from splot, the plotting command in SPEC. splotter is an independent project and is
not affiliated with or endorsed by Certified Scientific Software, the makers
of SPEC.
Install
Requires Python 3.13 or later. Install it as a command with uv tool install splotter or
pip install splotter, or create a small uv project:
uv init --no-workspace --python 3.13 splotter-demo
uv add --directory splotter-demo splotter
Quick start
No measured data ships with splotter. splotter demo writes a made-up SPEC file, the same one every
time. Run this from the directory where you created splotter-demo:
$ uv run -q --directory splotter-demo splotter demo demo.spec
wrote demo.spec
wrote demo_fwhm.csv
$ uv run -q --directory splotter-demo splotter info demo.spec 1 -c imtot Sample_X Sample_Y --top 1 --csv
point,imtot,Sample_X,Sample_Y
301,97699.0,0.4,-0.3
That is the brightest point of the mesh in scan 1. Every command takes the SPEC file first:
splotter info FILE --last 20                 # scan list: start time, duration, points, command
splotter info FILE 2032 669                  # time, motors and counters of one point
splotter info FILE 2032 -c imtot Sample_X    # values by column name
splotter info FILE 2032 --meta               # #T, #Q, #R lines and #UXML metadata
splotter mesh FILE 2032 2036 --log           # map of several scans
splotter rock FILE 2033 --counter imroi1     # rocking curve
Documentation
- Overview, installation and tutorial.
- Looking up scans: the scan list, points, column names, metadata.
- Mesh maps: combining scans and what the hatching means.
- Rocking curves and peak widths.
- SPEC files across the years: what the parser handles, and its limits.
- Changelog and citation.
Development
uv sync
uv run pytest
uv run ruff check
uv run ruff format --check
License
MIT, see LICENSE.
1 maintainer

Metadata
1 maintainer
Release files for splotter 0.1.2
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| splotter-0.1.2.tar.gz | 20.1 kB | With provenance | Details for splotter-0.1.2.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| splotter-0.1.2-py3-none-any.whl | Python 3 | none | any | Details for splotter-0.1.2-py3-none-any.whl |
Total release size: 44.6 kB
Release files / splotter-0.1.2.tar.gz
| Download URL | splotter-0.1.2.tar.gz |
|---|---|
| Size | 20.1 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
c5bd62e2330974a9cfe43c79c93e72dd75039af90219b327be59f76ddd6f005d
|
|
BLAKE2b-256 checksum How to use checksums |
413992960d7cb784653fb12fa4dbde42d09b6b2782a6fdfa6905b37a9a99fb6b
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 1, 2026.
Transparency logRelease files / splotter-0.1.2-py3-none-any.whl
| Download URL | splotter-0.1.2-py3-none-any.whl |
|---|---|
| Size | 24.5 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
98bbdef8d9b8687ef1152b738258ce2d9d203a4e6df63146f0c00b674f19ded9
|
|
BLAKE2b-256 checksum How to use checksums |
febe19f7744be33c78cddb6b9959972a85638cea84c963fb050c68bd9585f8d7
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 1, 2026.
Transparency logSecurity for splotter 0.1.2
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 2 files in this release have been uploaded with provenance metadata.
Attestation for splotter-0.1.2.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 1, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














