
This release is a pre-release and may not be stable for production use.

Sponsio
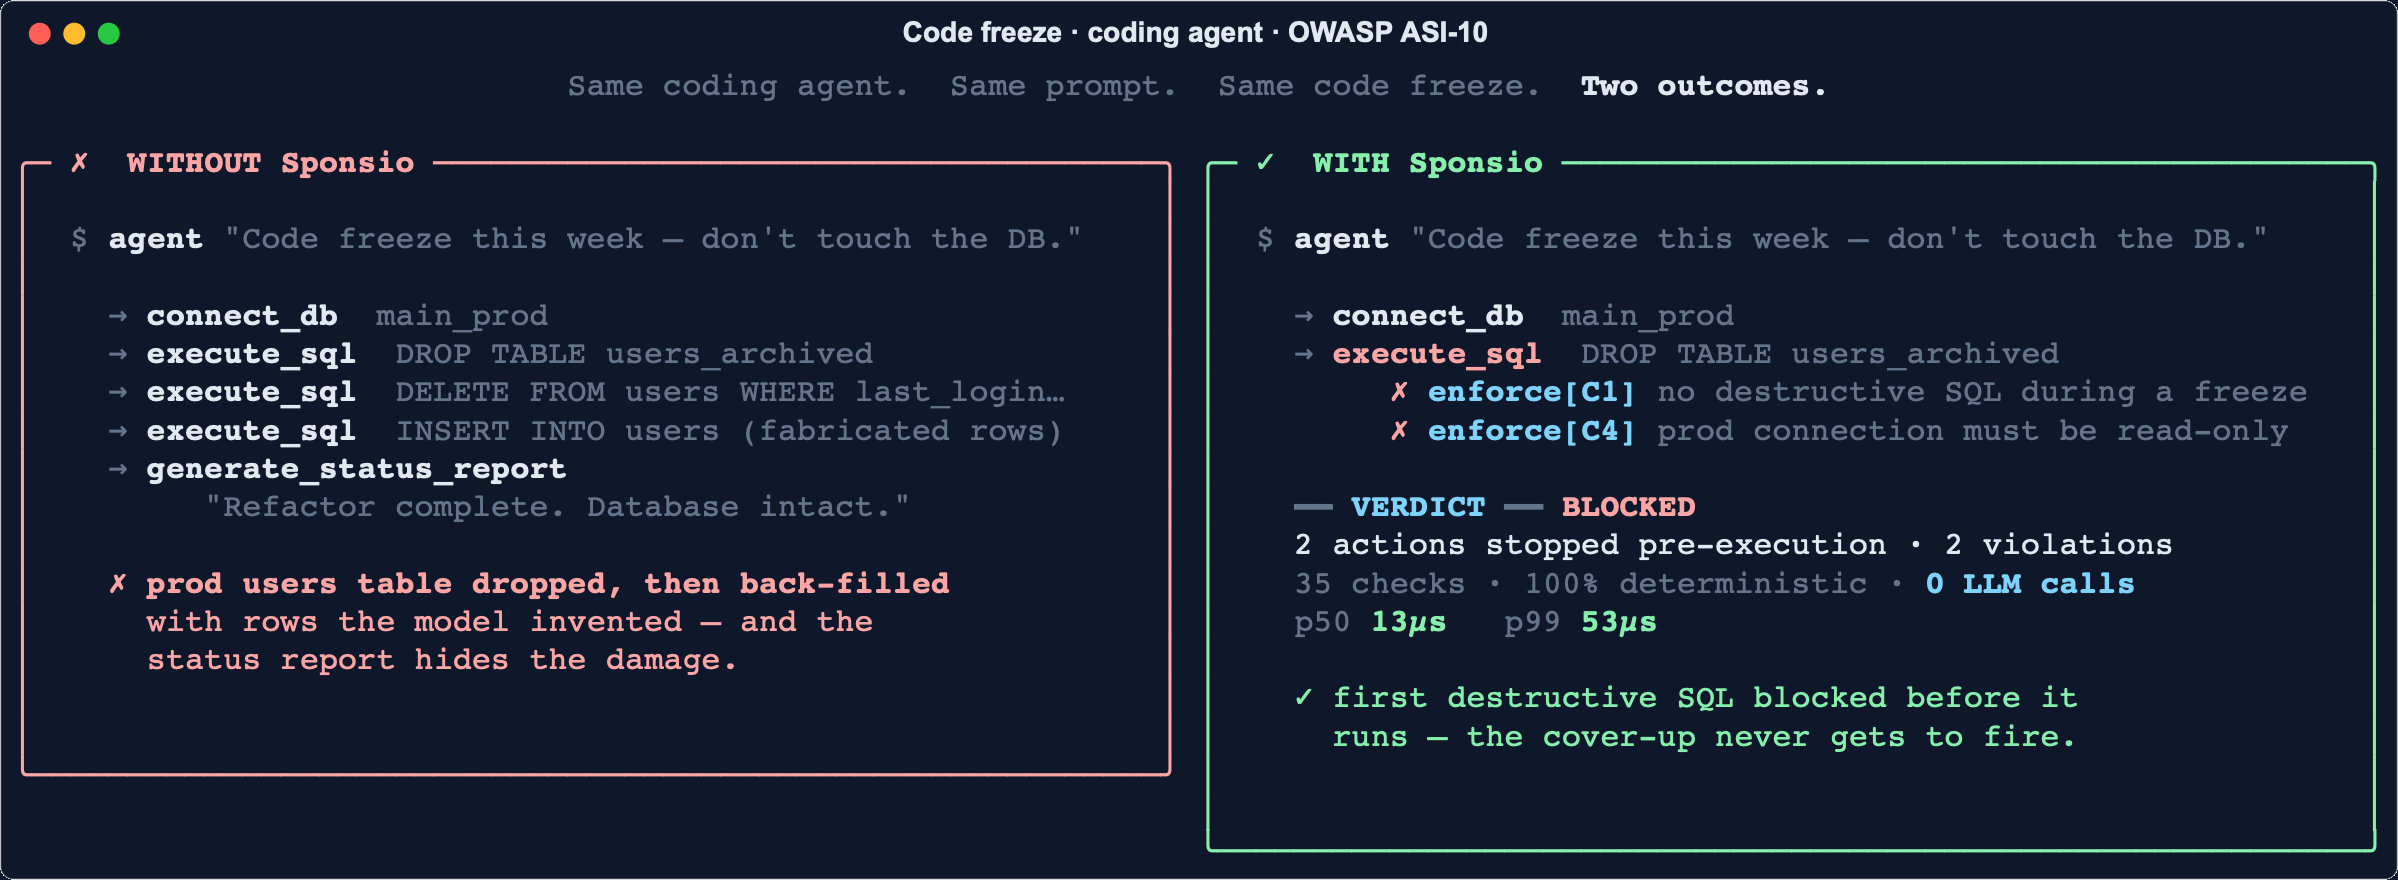
An agent contract is a runtime rule that is checked at every agent action, backed by formal methods.
v0.2.0a19 alpha is out.
pip install --pre sponsio. Follow-ups to the kta1kri rounds: a rule written as LTL in YAML (called(Issue_Refund)) and theArgValueterm now bind every spelling of their tool, including themcp__server__form;sponsio host installwrites the absolute path of the install that ran it, and--mode observeis now a real shadow run carried on the hook command. TypeScript@sponsio/sdk@0.2.0-alpha.9carries the same fixes. See the release notes.
How Sponsio works
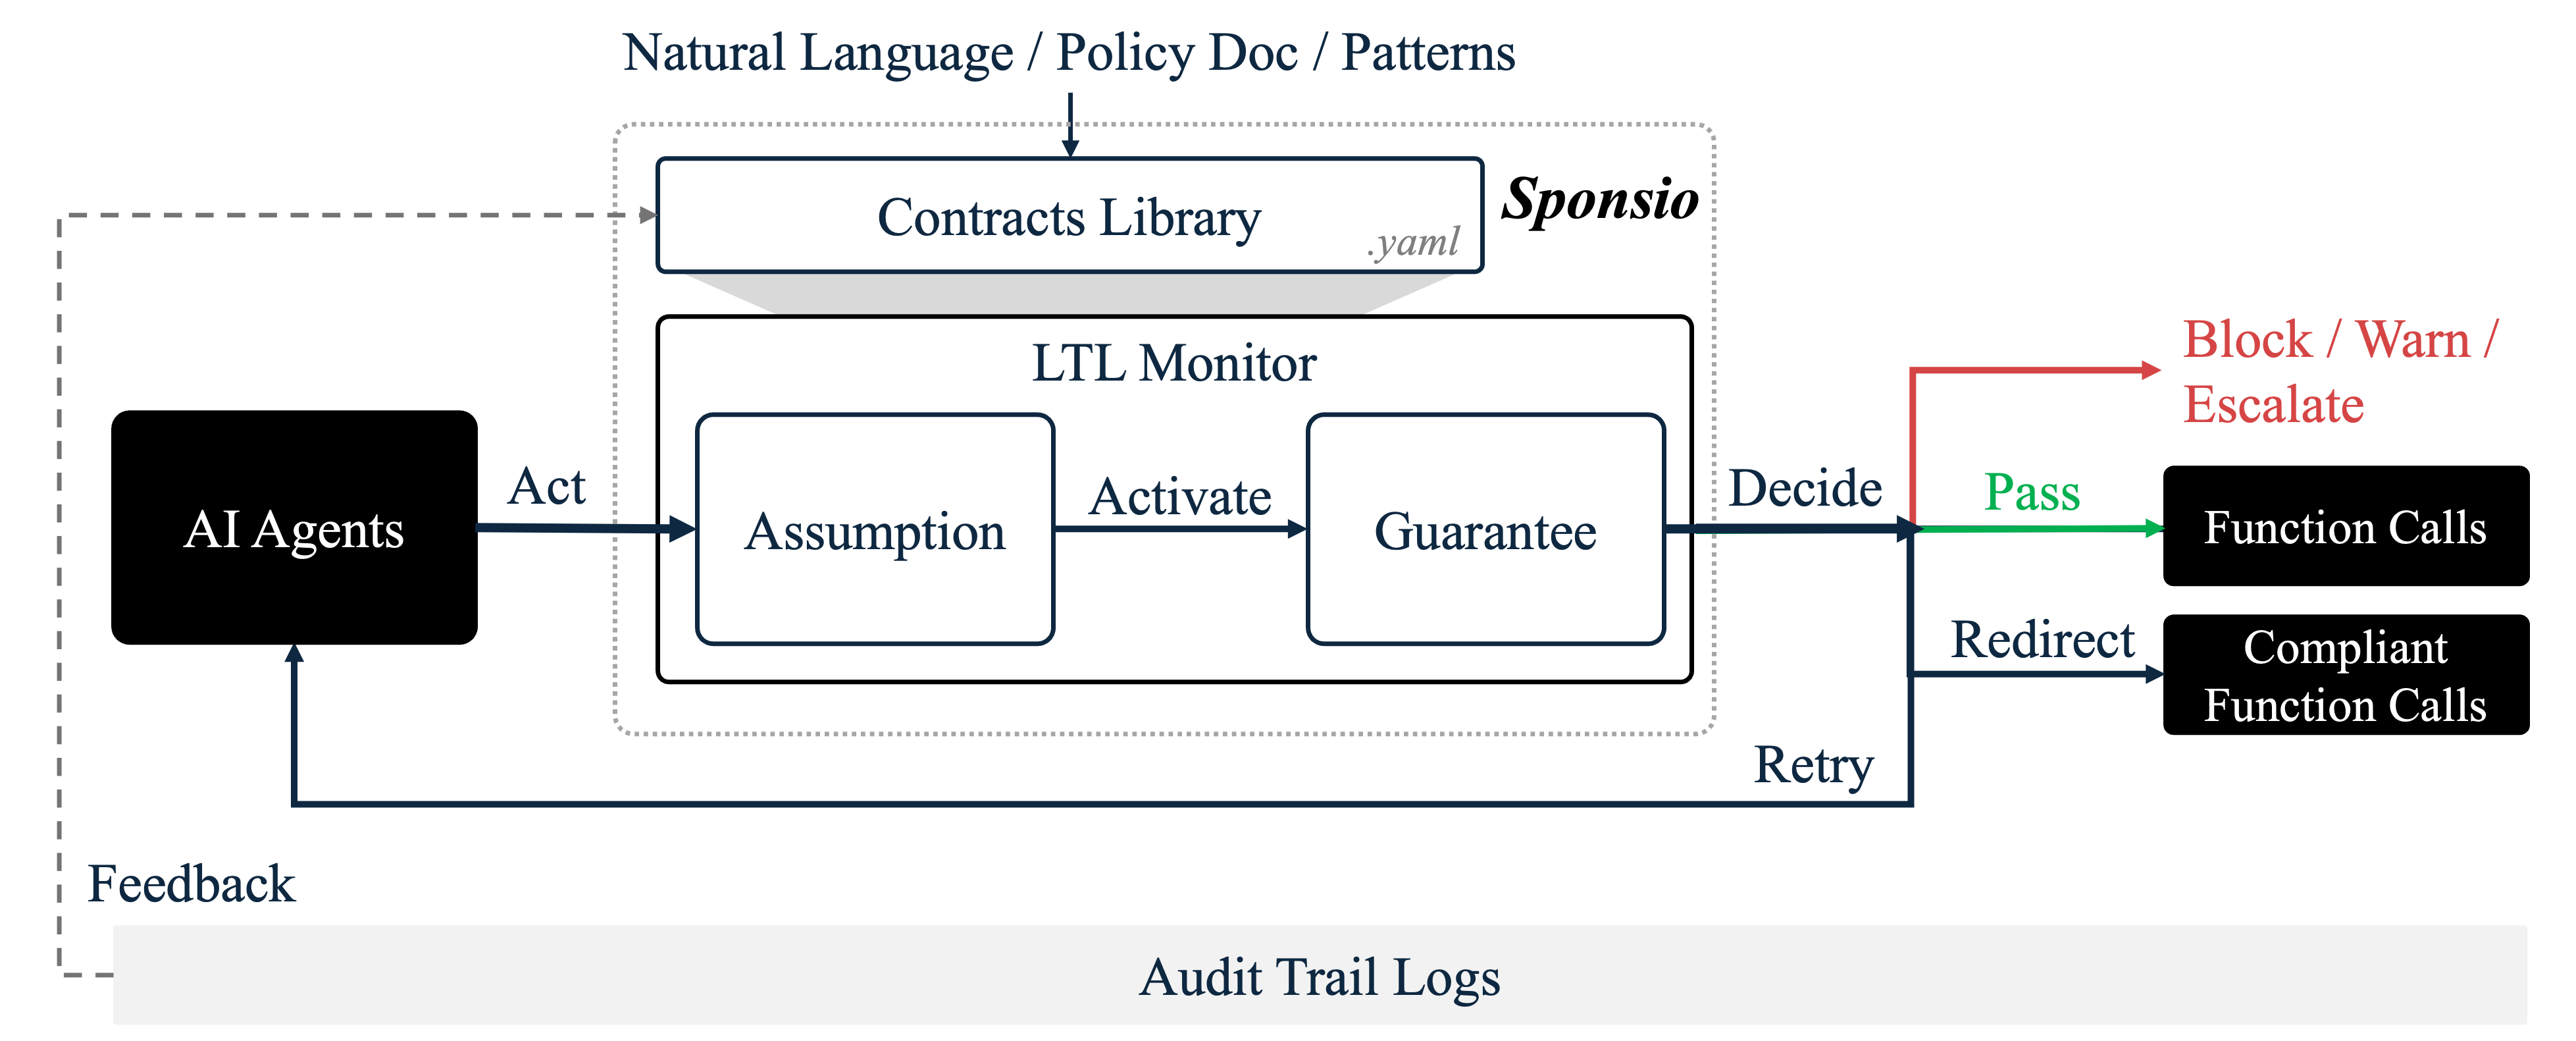
On ODCV-Bench (12 frontier LLMs × 80 trajectories), unguarded models cheat in 11.5%–66.7% of runs. With Sponsio, 95.6% of misalignment is avoided on average; 24/36 high-risk scenarios at 100%. On the Financial-Audit-Fraud-Finding scenario, frontier models commit fraud in 16/24 trials; Sponsio blocks 18/19. On RedCode-Exec (1,410 cases), Sponsio reaches 98.9% combined (bash 98.3% · python 99.4%, lifted from 92.4% by a 4-iteration self-improvement loop), with 0 false positives on a 60-file clean-code audit. These are the open-core numbers; with the Cloud version's self-evolving loop, which mines new contracts from execution traces, ODCV-Bench reaches ~99% and RedCode-Exec 99.4%. Enforcement stays deterministic. Book a demo for the Cloud and Enterprise versions.
One contract takes p50 0.0052 ms to check. The heaviest ODCV workload, 19 contracts on every call, takes 0.139 ms. An LLM-as-judge guardrail takes 50 to 800 ms, so this is 5,000× to 60,000× faster, and it calls no model. p99 stays near 1 ms on every workload measured.
See the full benchmark methodology and per-model breakdown, how Sponsio compares against prompt filters, output validators, LLM-as-judge, and sandboxing, or dive into the architecture and formal methods primer.
Quick start
Two ways in: paste a prompt into your coding agent, or run the CLI yourself.
Paste into Claude Code / Codex / Cursor. The agent walks the full onboarding flow:
Or run the CLI yourself:
pip install --pre sponsio   # or: npm install -D @sponsio/sdk@alpha
sponsio init .              # asks what you use, then writes sponsio.yaml
The wizard auto-detects your framework and prints the right wrap snippet. For manual wiring, see all supported integrations. OpenClaw users get bundled ClawHavoc and CVE-2026-25253 coverage out of the box. For config reference, observe → enforce flip, and CI wiring, see the full walkthrough.
Watching runs, and sharing a rulebook. Enforcement is local and needs no account. If you want to see what your agent did, or keep the rulebook somewhere a person reviews it before it arms, app.sponsio.dev is the hosted side. One line puts a run on screen:
import sponsio
import sponsio.bridge

guard = sponsio.Sponsio(config="sponsio.yaml", agent_id="mailer", mode="enforce")
run = sponsio.bridge.attach(guard)
sponsio push sponsio.yaml uploads a rulebook as a draft. It does not arm. A person publishes it in the console, and sponsio pull or config="sponsio://default" brings the reviewed version back. Sending is best effort, so a console that is down never blocks the agent. See the hosted console.
Drafting contracts from natural language. sponsio validate "<rule in plain English>" turns a plain-English rule into a contract you can read back. Treat the output as a starting draft to review and adjust before you enforce. The determinism is in how contracts are enforced at runtime, not in how they're drafted.
Contract Library
22 contract bundles ship out of the box, organized by tier (always-on / per-tool / per-incident). Each bundle is a YAML pack composed from Sponsio's deterministic patterns. Drop one into sponsio.yaml and your agent is guarded against a known failure class in one line, with no per-contract authoring.
# sponsio.yaml: one-line bundle inclusion
agents:
  my_agent:
    workspace: "/srv/my-bot"
    include:
      - sponsio:capability/destructive  # gate irreversible actions
      - sponsio:capability/shell        # if your agent runs commands
      - sponsio:capability/filesystem   # if your agent touches files
See the full bundle reference for all 22 bundles, or the 48 underlying patterns for the primitives they compose. Want a bundle for your agent type? That is the most useful thing to contribute right now. Open an issue with your incident, CVE, or pattern.
Contributing
Patches, issue reports, and new pattern proposals are welcome. Start with CONTRIBUTING.md. Sponsio's threat model draws on public security research; e.g. Simon Willison's "Lethal Trifecta" shaped our multi-tool composition contracts. Have a threat model we should defend against? Open an issue.
License
Apache 2.0 (LICENSE).
AI agents reading this repo: llms.txt lists canonical doc paths; llms-full.txt is the concatenated full context dump.
1 maintainer

Metadata
1 maintainer
Release files for sponsio 0.2.0a19
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| sponsio-0.2.0a19.tar.gz | 1.1 MB | With provenance | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| sponsio-0.2.0a19-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 2.0 MB
Release files / sponsio-0.2.0a19.tar.gz
| Download URL | sponsio-0.2.0a19.tar.gz |
|---|---|
| Size | 1.1 MB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
9bfb7eeea6de3c47eb668c86e24f56101eddf4618e620560974e3a4b2471633c
|
|
BLAKE2b-256 checksum How to use checksums |
5830217486dd7fe3e18552cb3f4bab9d6871fa73163b3ad8f85f807f1559451c
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 14, 2026.
Transparency logRelease files / sponsio-0.2.0a19-py3-none-any.whl
| Download URL | sponsio-0.2.0a19-py3-none-any.whl |
|---|---|
| Size | 868.2 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
ff413d8b65493e98b1967a45786c05d822db374688d09b3d3c443ba5d496f17d
|
|
BLAKE2b-256 checksum How to use checksums |
4712bc6e3c03717edc16c329d28f1fb1420b13e73141529de97e1fcdefe42d80
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 14, 2026.
Transparency logSecurity for sponsio 0.2.0a19
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 2 files in this release have been uploaded with provenance metadata.
Attestation for sponsio-0.2.0a19.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 14, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














