
by SQLStack
Streaming pipelines for ClickHouse, in typed SQL.
Change your SQL, see exactly what will rebuild, and replay it from retained stream history.
Website ·
Get started ·
Docs ·
Demo

SQLTide brings dbt-style authoring and deployment to streaming. Models compile into ClickHouse tables and materialized views, every build shows its plan first, and a change to your logic is rebuilt from retained Kafka history.
uv tool install sqltide # or: pip install sqltide
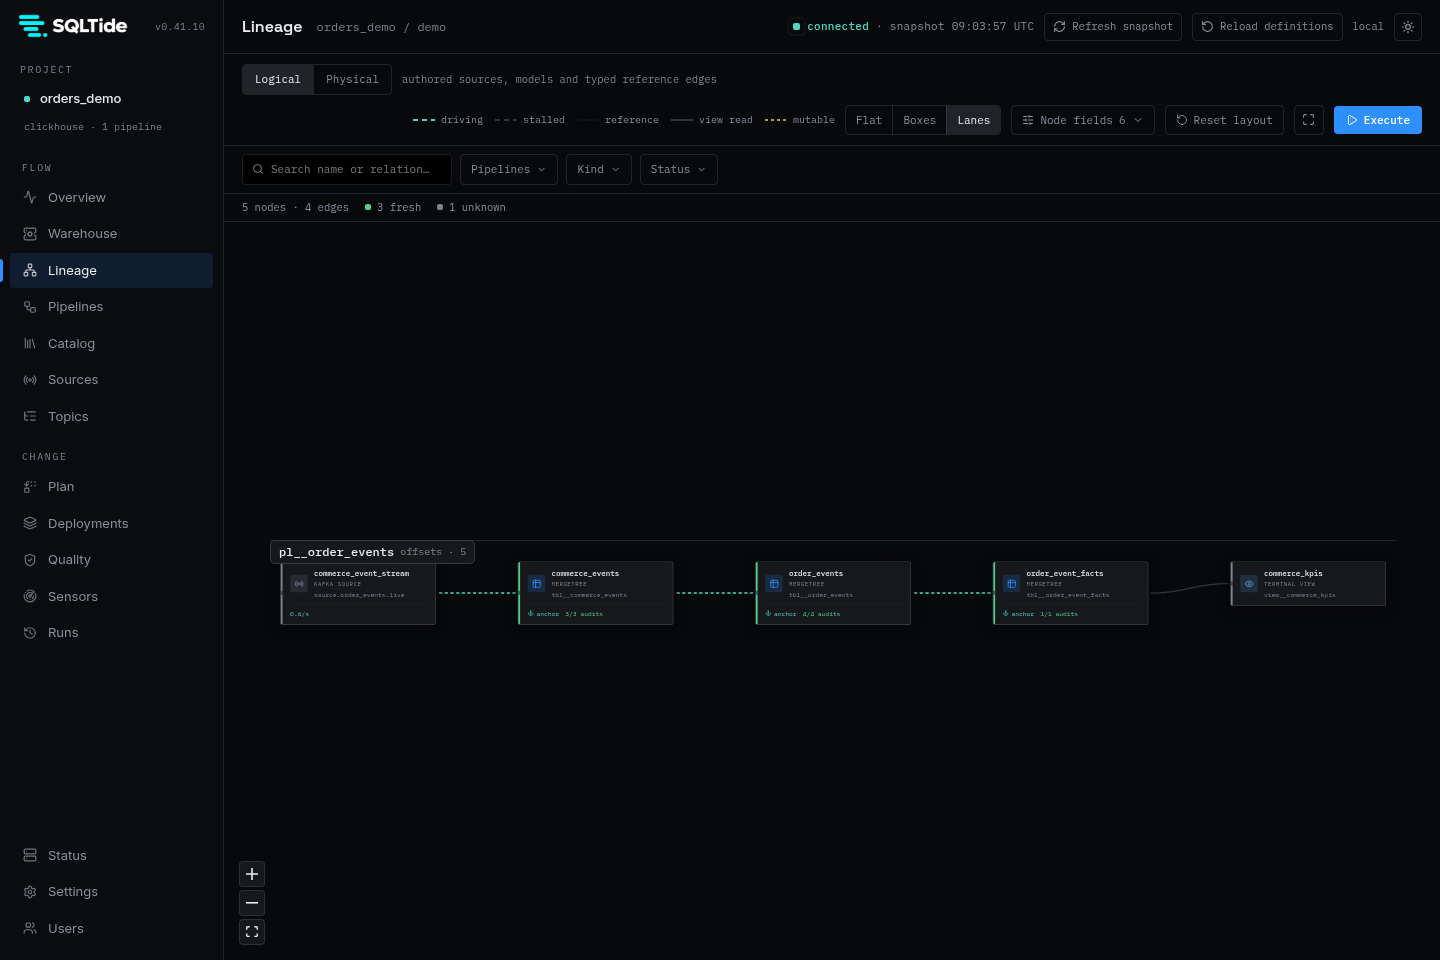
Key features
- Typed SQL models. Explicit output types,
__source()and__ref()dependencies, and offline compilation with no warehouse connection. - Replay-aware builds. Affected models are reconstructed from retained stream history.
- Plans before changes.
sqt planis read-only, andsqt buildreplans against current warehouse state before it runs. - Staged deployments. Build virtually, then audit, promote, and roll back.
- Quality built in. SQL tests, audits, sensors, and SQLClean rules and formatting.
- A UI for operating it. Sources, lag, lineage, plans, runs, and quality in
sqt dev, with trusted-proxy or password authentication for shared installations.
Example
A source and a model:
sources:
  - name: orders
    kind: kafka
    broker_list: kafka:9092
    topic: source.orders
    replay_boundary:
      mode: offsets
MODEL (
  engine "MergeTree()",
  order_by ["order_id", "_replay_partition", "_replay_offset"],
);

SELECT
  order_id::String AS order_id,
  _replay_partition::Int32 AS _replay_partition,
  _replay_offset::Int64 AS _replay_offset,
  _replay_timestamp::DateTime64(3) AS _replay_timestamp
FROM __source("orders")
Quick start
sqt discover    # inspect authored resources
sqt compile     # validate offline
sqt plan        # read-only warehouse plan
sqt build       # confirm and execute
sqt test
sqt audit
sqt dev         # local UI at 127.0.0.1:8000
The orders demo runs the whole workflow locally with Redpanda and ClickHouse. See the quickstart to start your own project.
Documentation
- Models and pipelines
- Replay and lineage
- Deployments
- Destructive operations
- Project configuration
- SQL Rules and formatting
- Changelog and contributing
License
Apache-2.0
1 maintainer

Metadata
1 maintainer
Release files for sqltide 0.65.2
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| sqltide-0.65.2.tar.gz | 2.1 MB | With provenance | Details for sqltide-0.65.2.tar.gz |
Built distributions (wheels)
| File | Actions Reset | |||
|---|---|---|---|---|
| sqltide-0.65.2-cp312-abi3-win_amd64.whl | CPython 3.12 | abi3 | Windows x86-64 | Details for sqltide-0.65.2-cp312-abi3-win_amd64.whl |
| sqltide-0.65.2-cp312-abi3-manylinux2014_x86_64.manylinux_2_17_x86_64.whl | CPython 3.12 | abi3 | Linux glibc 2.17+ x86-64 | Details for sqltide-0.65.2-cp312-abi3-manylinux2014_x86_64.manylinux_2_17_x86_64.whl |
| sqltide-0.65.2-cp312-abi3-manylinux2014_aarch64.manylinux_2_17_aarch64.whl | CPython 3.12 | abi3 | Linux glibc 2.17+ ARM64 | Details for sqltide-0.65.2-cp312-abi3-manylinux2014_aarch64.manylinux_2_17_aarch64.whl |
| sqltide-0.65.2-cp312-abi3-macosx_11_0_arm64.whl | CPython 3.12 | abi3 | macOS 11.0+ ARM64 | Details for sqltide-0.65.2-cp312-abi3-macosx_11_0_arm64.whl |
| sqltide-0.65.2-cp312-abi3-macosx_10_12_x86_64.whl | CPython 3.12 | abi3 | macOS 10.12+ x86-64 | Details for sqltide-0.65.2-cp312-abi3-macosx_10_12_x86_64.whl |
Total release size: 93.1 MB
Release files / sqltide-0.65.2.tar.gz
| Download URL | sqltide-0.65.2.tar.gz |
|---|---|
| Size | 2.1 MB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
2ec5093d93fa99c3c4f9a1370235f59a99a91c60b23c54f1d247960d3386dc27
|
|
BLAKE2b-256 checksum How to use checksums |
70d4bb12f666333eeab27aa8ac347dd87a86e879ac0a70f796d53cd2701996c6
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 9, 2026.
Transparency logRelease files / sqltide-0.65.2-cp312-abi3-win_amd64.whl
| Download URL | sqltide-0.65.2-cp312-abi3-win_amd64.whl |
|---|---|
| Size | 19.7 MB |
| Tags | CPython 3.12 Windows x86-64 abi3 |
|
SHA-256 checksum How to use checksums |
9b6772c31fd9c82ddcca33c232dc06deb39f23e86ea2de166655099c6fb09f00
|
|
BLAKE2b-256 checksum How to use checksums |
1d7693f4e263713a38d96296349845d1a68a2ca11b3fae39e95c86a5f9231727
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 9, 2026.
Transparency logRelease files / sqltide-0.65.2-cp312-abi3-manylinux2014_x86_64.manylinux_2_17_x86_64.whl
| Download URL | sqltide-0.65.2-cp312-abi3-manylinux2014_x86_64.manylinux_2_17_x86_64.whl |
|---|---|
| Size | 18.1 MB |
| Tags | CPython 3.12 Linux glibc 2.17+ x86-64 abi3 |
|
SHA-256 checksum How to use checksums |
920f68693ad9dee678c28dd67319ba39788a0b93da503d0421c18ce4a52f23a0
|
|
BLAKE2b-256 checksum How to use checksums |
1fbce3dce8ac3b540ecf1a8f22542884a7477d117aedd0f37f0fe8d52740448e
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 9, 2026.
Transparency logRelease files / sqltide-0.65.2-cp312-abi3-manylinux2014_aarch64.manylinux_2_17_aarch64.whl
| Download URL | sqltide-0.65.2-cp312-abi3-manylinux2014_aarch64.manylinux_2_17_aarch64.whl |
|---|---|
| Size | 17.6 MB |
| Tags | CPython 3.12 Linux glibc 2.17+ ARM64 abi3 |
|
SHA-256 checksum How to use checksums |
56d9cd8882c4738c7277903062df372f6bfb1fa813a6f17fc7fbbcc1175d5f7c
|
|
BLAKE2b-256 checksum How to use checksums |
b269e76fc15411e5afa6fb467af52ec5154649a751dd32067b2cf3fa198187b8
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 9, 2026.
Transparency logRelease files / sqltide-0.65.2-cp312-abi3-macosx_11_0_arm64.whl
| Download URL | sqltide-0.65.2-cp312-abi3-macosx_11_0_arm64.whl |
|---|---|
| Size | 17.5 MB |
| Tags | CPython 3.12 abi3 macOS 11.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
8efd2ac5d8b4866e0cc462bafea99f7d6957c1c5a0fa2d29976d3be9bca796b8
|
|
BLAKE2b-256 checksum How to use checksums |
d02dc2ac2c935c88ac2a0518eac884922d3d8c2b084538f8dedd43142c351a7d
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 9, 2026.
Transparency logRelease files / sqltide-0.65.2-cp312-abi3-macosx_10_12_x86_64.whl
| Download URL | sqltide-0.65.2-cp312-abi3-macosx_10_12_x86_64.whl |
|---|---|
| Size | 18.0 MB |
| Tags | CPython 3.12 abi3 macOS 10.12+ x86-64 |
|
SHA-256 checksum How to use checksums |
0aafac89a8ca8dd1f5dfd2b99ddbd1fa6c3ad23e68857205456c5d28c0368d21
|
|
BLAKE2b-256 checksum How to use checksums |
bbfc57239c0e878af0760713a608e2c825331eb911e192d0a854d562a3a68bac
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 9, 2026.
Transparency logSecurity for sqltide 0.65.2
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 6 files in this release have been uploaded with provenance metadata.
Attestation for sqltide-0.65.2.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 9, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














