
This release is a pre-release and may not be stable for production use.
Overview
SSH Deploy key is a high-performance tool to distribute your ssh public key to one or more remote servers. It accepts lists of remote hosts from redirected standard in, or the remote hosts can be entered interactively.
Documentation
Documentation and example usage can be found at
Installation
SSH deploy key is installed from the command line.
ssh-deploy-key is normally installed via pip. However, on some systems, there are source files that must be installed first.
Prerequisites
ssh-deploy-key depends on the excellent Paramiko ssh library, which requires the Python sources. You can install these using the normal package managers for your OS.
Debian/Ubuntu (apt-get)
sudo apt-get install python-dev
Red Hat/Centos (yum)
sudo yum install python-devel
OS X
You will need a compiler installed – either XCode or gcc. Normally, you can just run the command to install ssh-deploy-key (see below), and if no compiler is available on your system, you will be prompted to install one:
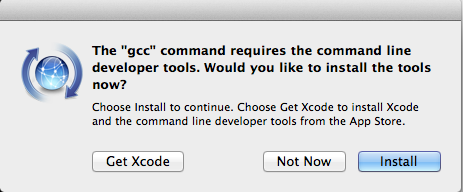
If this happens, click the ‘install’ button, then run the pip command again.
Install ssh-deploy-key via Pip
Once the development libraries are in place, the best way to install ssh-deploy-key is via pip. To get pip, see http://www.pip-installer.org/en/latest/installing.html
Then,
sudo pip install ssh-deploy-key
Source
The SSH deploy key sources are hosted on bitbucket.
1 maintainer

Metadata
1 maintainer
Release files for ssh-deploy-key develop
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| ssh-deploy-key-develop.tar.gz | 13.9 kB | Without provenance | Details |
Release files / ssh-deploy-key-develop.tar.gz
| Download URL | ssh-deploy-key-develop.tar.gz |
|---|---|
| Size | 13.9 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
5b8dfb679eb1feda3dcb1084c3e4e6c0f5aef5045031508b7e17a8757953711c
|
|
BLAKE2b-256 checksum How to use checksums |
3f12676af404672902b5ae5fe5901f2d263fd320b7475fed12ff3fcfeb9255d8
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
Security for ssh-deploy-key develop
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.














