
sshield


Audit SSH configuration for weak settings.
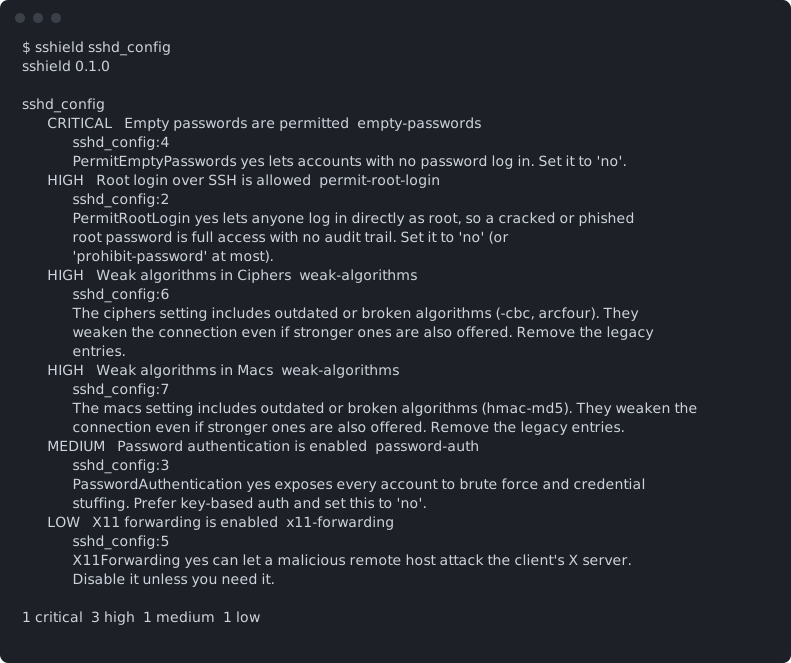
Most SSH incidents trace back to a config line nobody revisited: root login left
on, password auth still enabled, a legacy cipher hanging around, or a client set
to accept any host key. sshield reads your sshd_config, ssh_config and
~/.ssh/config and points at those lines.
Runs offline. Nothing leaves your machine.
Install
pip install sshield
Usage
sshield                         scan the current directory
sshield /etc/ssh/sshd_config    scan a single file
sshield --min high              only high and critical findings
sshield --json                  machine-readable output
Exit status is 0 when clean, 1 when there is a finding at or above the fail
level (--fail-on, default high), and 2 on error.
What it checks
Server (sshd_config)
| Check | Severity | What it finds |
|---|---|---|
empty-passwords |
critical | PermitEmptyPasswords yes. |
legacy-protocol |
critical | SSH protocol 1 enabled. |
permit-root-login |
high | PermitRootLogin yes. |
weak-algorithms |
high | Broken ciphers/MACs/KEX (CBC, arcfour, hmac-md5/sha1, DH group1, ...). |
password-auth |
medium | Password authentication enabled. |
pubkey-disabled |
medium | Public-key auth turned off. |
x11-forwarding, permit-tunnel |
low | Forwarding/tunnelling left on. |
Client (ssh_config / ~/.ssh/config)
| Check | Severity | What it finds |
|---|---|---|
no-host-key-checking |
high | StrictHostKeyChecking no (defeats MITM protection). |
known-hosts-devnull |
high | UserKnownHostsFile /dev/null. |
Settings are read last-wins, the way sshd resolves them, and commented-out defaults are ignored, so a stock config stays quiet.
License
MIT
1 maintainer

Metadata
1 maintainer
Release files for sshield 0.1.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| sshield-0.1.0.tar.gz | 9.0 kB | With provenance | Details for sshield-0.1.0.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| sshield-0.1.0-py3-none-any.whl | Python 3 | none | any | Details for sshield-0.1.0-py3-none-any.whl |
Total release size: 17.7 kB
Release files / sshield-0.1.0.tar.gz
| Download URL | sshield-0.1.0.tar.gz |
|---|---|
| Size | 9.0 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
23940f5995488851f40162395de74bb238b15c810fd5eebae0f10dd85e830950
|
|
BLAKE2b-256 checksum How to use checksums |
9e63a037d719e329eef4f5d250b73f30ed523218b23ccdd6a4ef9a0892ee3de7
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 5, 2026.
Transparency logRelease files / sshield-0.1.0-py3-none-any.whl
| Download URL | sshield-0.1.0-py3-none-any.whl |
|---|---|
| Size | 8.7 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
90eb2fe9595d74da1a359b9a6f9fe9b99358f4ea581285c82e82e44da310559a
|
|
BLAKE2b-256 checksum How to use checksums |
073a6f4d2b38c801ca55721001ad1589f2fcfd98610ddc824a850be1f4e42f0e
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 5, 2026.
Transparency logSecurity for sshield 0.1.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
Both files in this release have been uploaded with provenance metadata.
Attestation for sshield-0.1.0.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 5, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.













