
Stampla Desktop


The desktop app for photo and video archives that can prove their own integrity: import memory cards, check the archive's health, fix names, undo anything — every action a preview first.
Stampla stamps every photo and video with an identity derived purely from the file itself — the capture time plus a fingerprint of the content:
20260703_150727_9b677b64.nef
└──────┬──────┘ └──┬───┘
  capture time    hash
There is no database to maintain or lose: the files carry their own catalog. Names sort chronologically across every camera and phone, duplicates identify themselves, and the whole archive can be re-checked at any time — corruption told apart from ordinary edits — with any tool that can hash a file, decades from now.
The app covers the whole workflow:
- Import copies a card into the archive, names every file on arrival, and re-hashes every copy at its destination. It ends in a verdict, not a guess: safe to format appears only when every file on the card is accounted for.
- Organize triages a messy folder — what each file would become, what is already archived, what needs your eyes first — and never renames anything.
- Verify recomputes every name from metadata and content and explains disagreements in plain language, worst first.
- Rename brings names in line after edits, whole groups (RAW, sidecars, derivatives) at a time. Masters managed by Lightroom Classic are handed off through a rename token, never touched behind the catalog's back.
- History lists every applied change with Undo, and Resume for interrupted runs.
- Settings edits the archive configuration with validation before every save; the naming pattern editor previews an example name as you type.
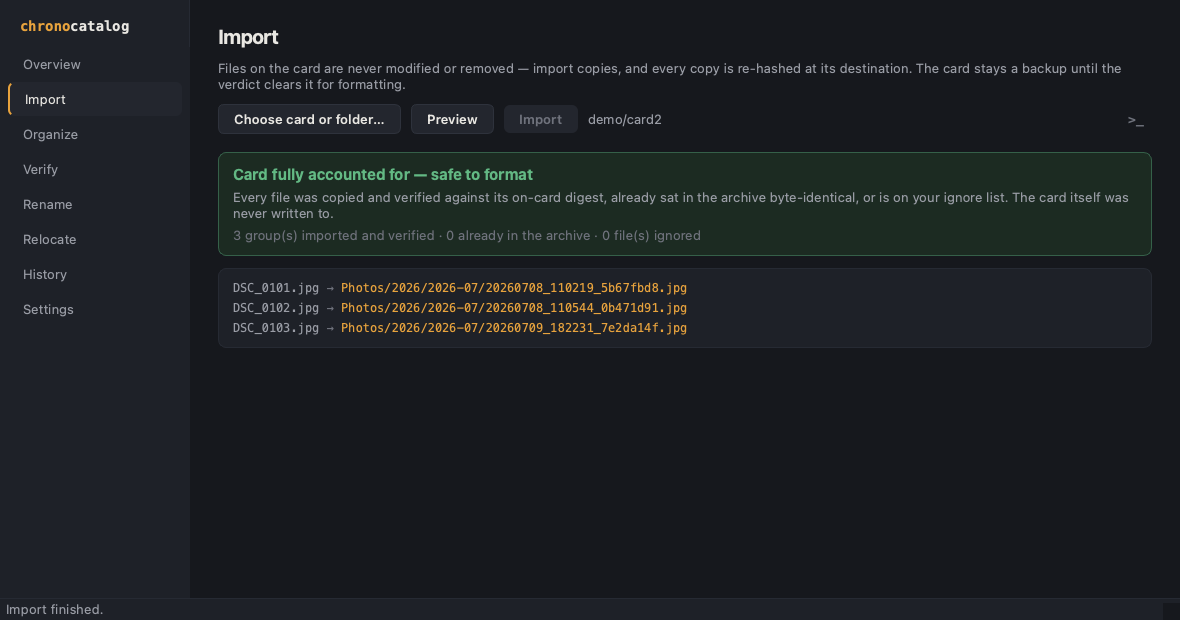
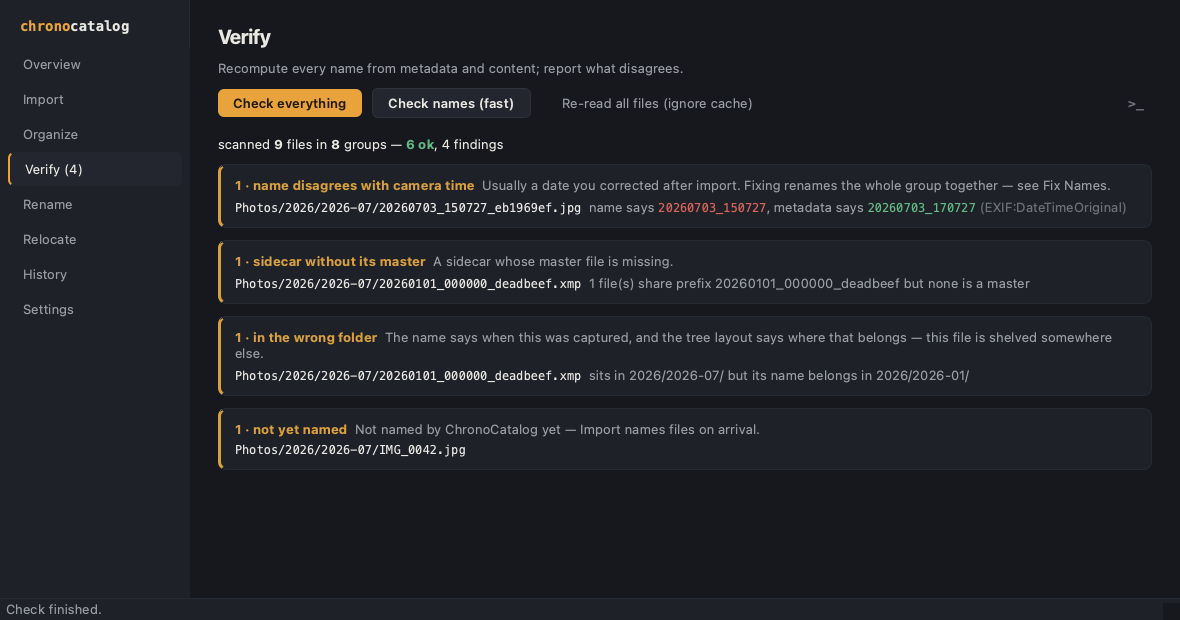
The app adds no behavior of its own: every view renders the plans and
reports of the stampla
library — the same engine behind the CLI — and every change goes
through its validated, write-ahead-journaled apply. The exact terminal
equivalent of any action is one click away, behind the quiet >_
toggle.
Install
macOS (Apple Silicon): download Stampla-<version>-arm64.dmg
from Releases
and drag the app to Applications. The build is not yet signed with an
Apple Developer ID, so the first launch is blocked: open System
Settings → Privacy & Security, scroll to Security and click
Open Anyway. This is needed once.
Any platform (Python 3.11+):
$ uv tool install stampla-desktop
or pipx install stampla-desktop. Either way you also need
ExifTool on PATH (macOS:
brew install exiftool).
Run
$ stampla-desktop [archive.toml]
Without an argument the app asks for an archive configuration and remembers it — or creates a new archive from scratch. Everything is a dry run until Apply, which confirms first; every applied change lands in History with Undo.
Run from this repository
With uv:
$ git clone https://github.com/stampla/stampla-desktop.git
$ cd stampla-desktop
$ uv run stampla-desktop
With plain pip:
$ python3 -m venv .venv
$ .venv/bin/pip install -e .
$ .venv/bin/stampla-desktop
For a tour that touches none of your own files, generate the demo
archive (macOS only — it leans on sips): a small throwaway archive
imported through the real engine, then seeded with a date edit, an
unnamed file and an orphan sidecar so every view has something to
show:
$ uv run python demo/make_demo.py
$ uv run stampla-desktop demo/demo.toml
Development setup, checks and expectations: CONTRIBUTING.md.
Requirements
- Python 3.11+ (the macOS app bundles its own)
- ExifTool on
PATH
License
1 maintainer

Metadata
1 maintainer
Release files for stampla-desktop 0.3.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| stampla_desktop-0.3.0.tar.gz | 273.5 kB | With provenance | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| stampla_desktop-0.3.0-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 340.1 kB
Release files / stampla_desktop-0.3.0.tar.gz
| Download URL | stampla_desktop-0.3.0.tar.gz |
|---|---|
| Size | 273.5 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
84d838792cf6d06b1194720cdad67e3a16faace1272064cf2e0ea8b884c24494
|
|
BLAKE2b-256 checksum How to use checksums |
b07c7b3ae355dcf20545123e4811961786582a21891c34da8c01b33638446166
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Aug 28, 2026.
Transparency logRelease files / stampla_desktop-0.3.0-py3-none-any.whl
| Download URL | stampla_desktop-0.3.0-py3-none-any.whl |
|---|---|
| Size | 66.5 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
5f002b63c51059d404c06879318dcd707cf4936c2e907c0f6be3adbac5c33afa
|
|
BLAKE2b-256 checksum How to use checksums |
d38e0ef9e647d980252f1c0ee976bb3d1820cc8bede6688564a63be0f998cfc6
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Aug 28, 2026.
Transparency logSecurity for stampla-desktop 0.3.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 2 files in this release have been uploaded with provenance metadata.
Attestation for stampla_desktop-0.3.0.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Aug 28, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.













