
starcheck
GitHub stars are for sale, and millions of them are fake. Researchers have counted millions of bought stars on GitHub, often on repos pushing malware or crypto scams. starcheck looks at who starred a repo and tells you whether the stars look real.
uvx starcheck owner/repo
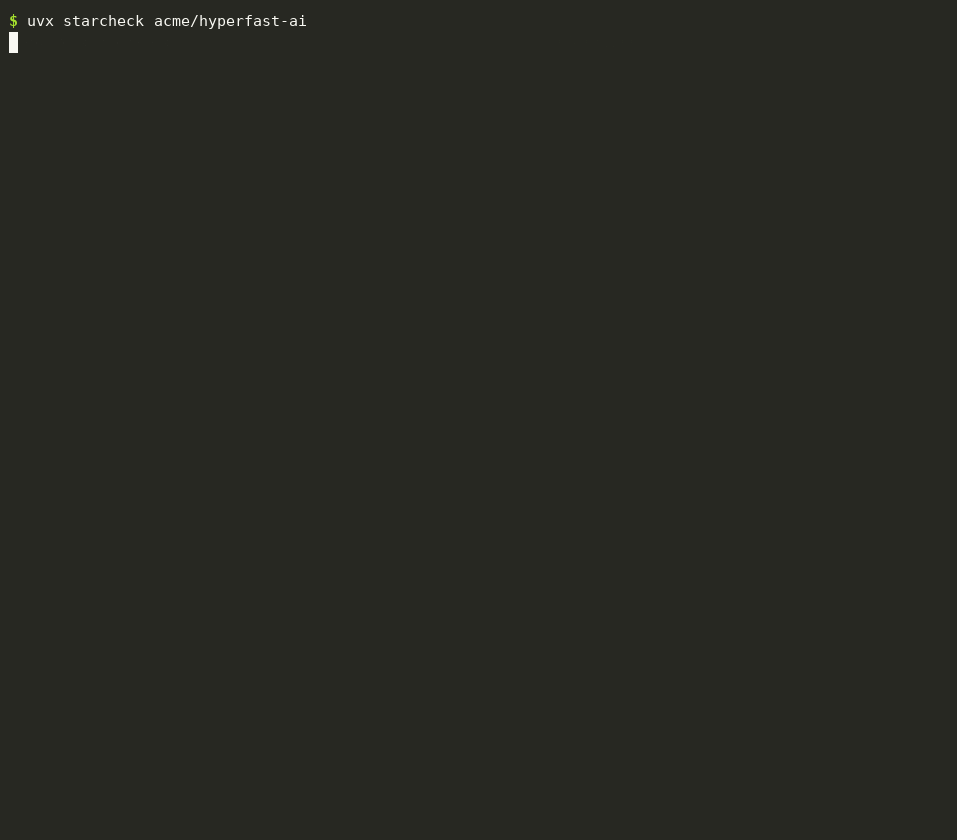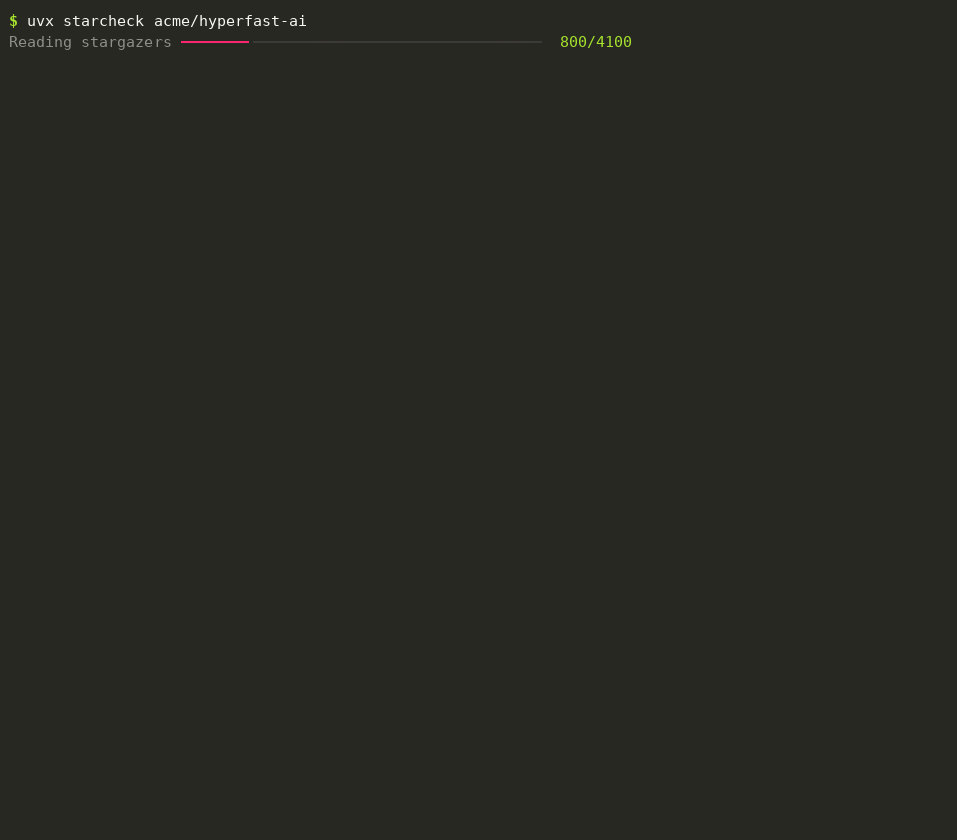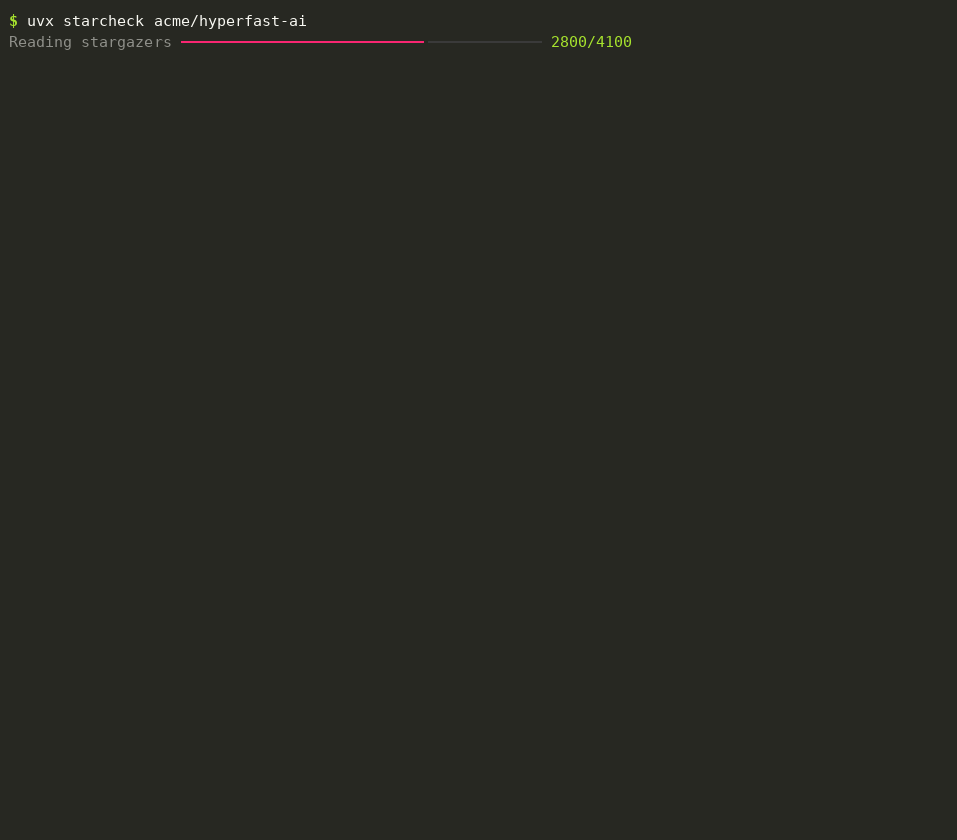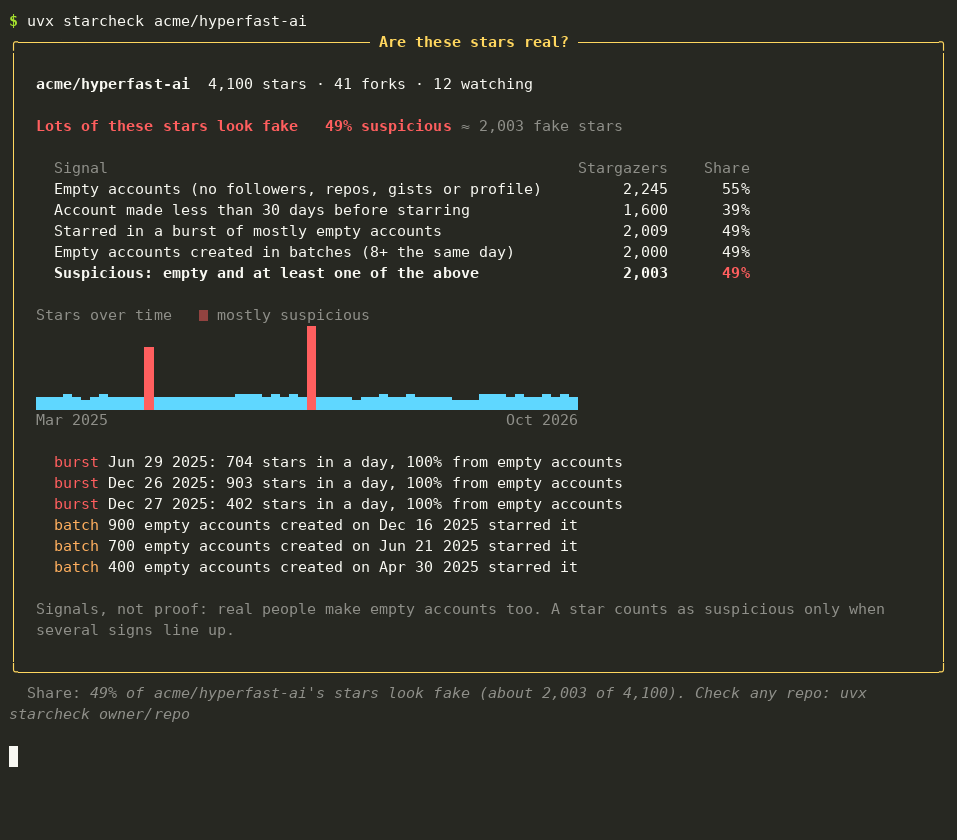
Demo on a made-up repo with made-up stargazers, generated by docs/demo.py. acme/hyperfast-ai doesn't exist.
What it looks for
Bought stars come from throwaway accounts, and throwaway accounts look alike:
| Signal | |
|---|---|
| Empty account | no followers, no repos, no gists, nothing in the profile |
| Brand new | the account was made less than 30 days before it starred the repo |
| Bursts | hundreds of stars in one day, mostly from empty accounts |
| Batches | many empty accounts created on the same day, all starring the same repo |
| No forks | thousands of stars but almost nobody forked it |
Plenty of real people have empty accounts, so that alone means nothing. A star is counted as suspicious only when an empty account also shows another sign: brand new, part of a burst, or part of a batch. A launch on Hacker News makes a burst too, but of real accounts, so it doesn't count.
The result is a set of signals, not proof. starcheck never names the accounts it flags.
Use it before you trust a repo
- Before installing a tool you found through its star count
- Before depending on a library, alongside its maintainers, downloads and issues
- To check a competitor's or a "trending" repo
- To check your own repo: if someone bought you stars (it happens, as a smear), you'll want to know
Token
GitHub only lists stargazers to signed-in users, so starcheck needs a token. If you use the GitHub CLI it just works (gh auth token). Otherwise set GITHUB_TOKEN to any personal access token; it needs no scopes. Checking 3,000 stargazers takes 30 API calls.
Options
starcheck owner/repo              # up to 3,000 stargazers
starcheck github.com/owner/repo   # URLs work too
starcheck owner/repo --max 10000  # check more (big repos are sampled from both ends of the timeline)
starcheck owner/repo --json       # for scripts and CI
Install
uvx starcheck           # run without installing
pipx install starcheck  # or install it
Requires Python 3.9+. The only dependency is rich. macOS, Linux and Windows.
License
MIT
1 maintainer

Metadata
1 maintainer
Release files for starcheck 0.1.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| starcheck-0.1.0.tar.gz | 10.7 kB | With provenance | Details for starcheck-0.1.0.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| starcheck-0.1.0-py3-none-any.whl | Python 3 | none | any | Details for starcheck-0.1.0-py3-none-any.whl |
Total release size: 21.6 kB
Release files / starcheck-0.1.0.tar.gz
| Download URL | starcheck-0.1.0.tar.gz |
|---|---|
| Size | 10.7 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
cbe082304d9a7db6bf4a98a24eed512f646094d4f227e13d0380f2afd850abea
|
|
BLAKE2b-256 checksum How to use checksums |
d6ffc749dab1bc731c868e51e997a1b4213c81db146fd3dbd4544664a0e03ffa
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 10, 2026.
Transparency logRelease files / starcheck-0.1.0-py3-none-any.whl
| Download URL | starcheck-0.1.0-py3-none-any.whl |
|---|---|
| Size | 10.9 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
807b000830d6a9bf8d6070b58906dbee265eb99e0a5eda3e3afedb964f3bcefd
|
|
BLAKE2b-256 checksum How to use checksums |
1458f54fd0177864eb730b53c55a5782b7a4150d86d506d8f8650be393336e5c
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 10, 2026.
Transparency logSecurity for starcheck 0.1.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
Both files in this release have been uploaded with provenance metadata.
Attestation for starcheck-0.1.0.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 10, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.













