
StepUp Core




StepUp is a dynamic build tool and a modern alternative to
Make.
Its defining feature is that workflow generation and execution are unified:
a plan.py script defines the initial build steps.
While the workflow is being executed, any step can add more steps and dependencies,
based on the outputs built so far.
This makes StepUp ideal for builds
where the full set of dependencies cannot be determined in advance.
StepUp Core provides the basic framework for StepUp, without any domain-specific features. Those live in extension packages:
- StepUp RepRep for creating reproducible reports: papers, presentations, theses, etc.
- StepUp Queue submits jobs to a SLURM scheduler.
Installation
pip install stepup
See the installation guide for details.
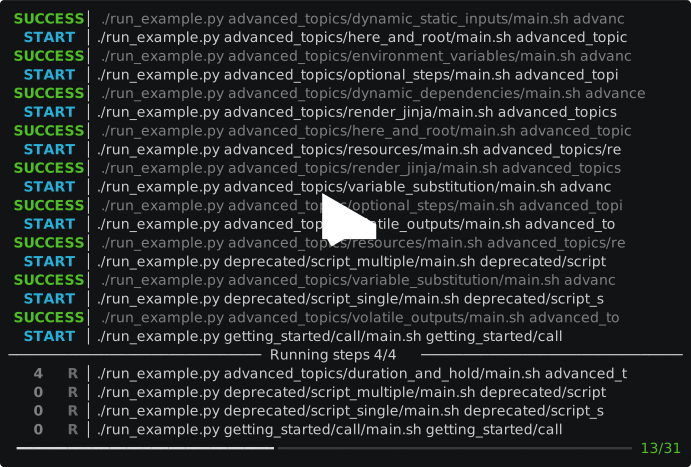
Quick Visual Impression
Documentation
Full documentation, including a tutorial and a feature overview, is available at https://reproducible-reporting.github.io/stepup-core.
License
StepUp Core is distributed under the terms of the LGPL-3.0-or-later license. Contributions are welcome; see the development guide to get started.
1 maintainer

Metadata
1 maintainer
Release files for stepup 4.0.2
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | |
|---|---|---|---|
| stepup-4.0.2.tar.gz | 380.6 kB | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| stepup-4.0.2-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 731.5 kB
Release files / stepup-4.0.2.tar.gz
| Download URL | stepup-4.0.2.tar.gz |
|---|---|
| Size | 380.6 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
a1a88f8ea035dcb0dda59dd244c451186024e2d678389d0315253e015478c8b6
|
|
BLAKE2b-256 checksum How to use checksums |
5cdaaab8b112b9e9cd8d65eb8f80bdfe9fc4039129f9153aef6ffb372404ccbb
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 18, 2026.
Transparency logRelease files / stepup-4.0.2-py3-none-any.whl
| Download URL | stepup-4.0.2-py3-none-any.whl |
|---|---|
| Size | 350.9 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
d1c966bce6158e03f9a0ed3b9f2bf0e512fd2e46ec0e7e70e351dbc2d50f15b1
|
|
BLAKE2b-256 checksum How to use checksums |
9827ef7f506c882a2c7d108de16402ae50514a32cae088c37e863aba9e1daed2
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 18, 2026.
Transparency log













