
StratigraPy
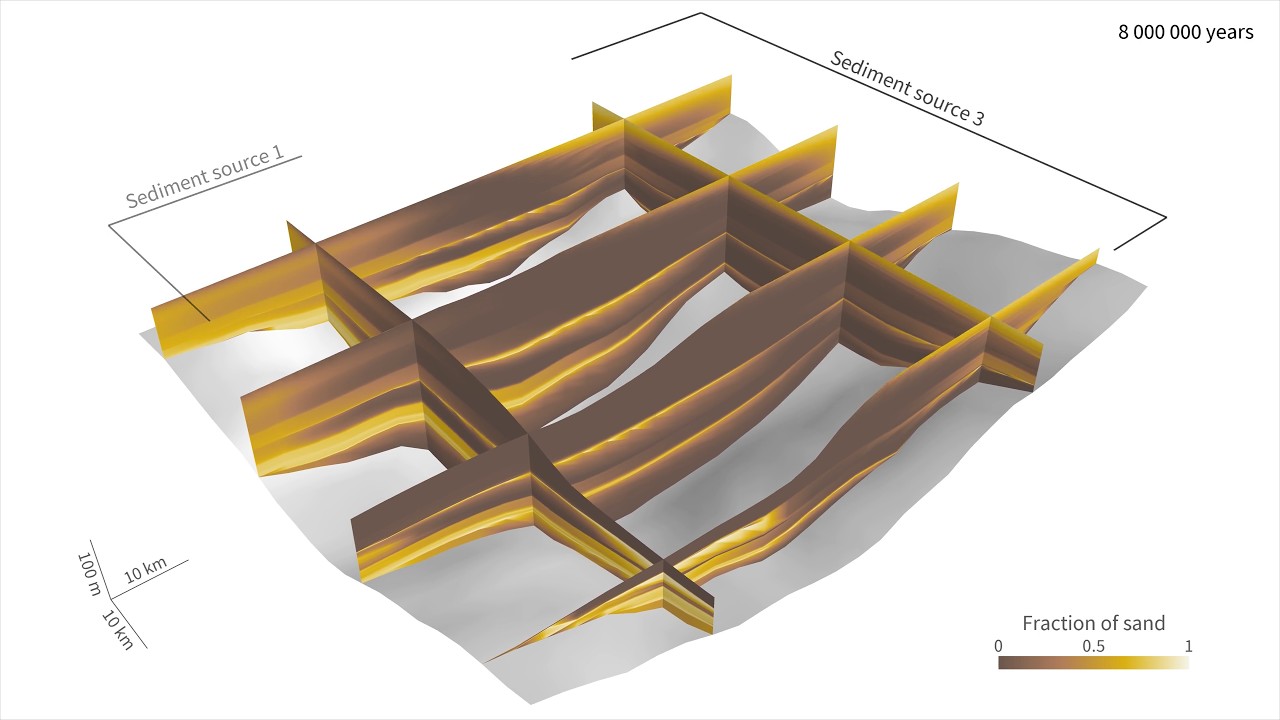
StratigraPy is a Python package for stratigraphic modeling based on Landlab. Similarly to Landlab, StratigraPy favors flexibility for prototyping and teaching rather than speed.
StratigraPy is still experimental and under heavy development.
Installation
You can directly install StratigraPy from pip:
pip install stratigrapy
Or from GitHub using pip:
pip install git+https://github.com/grongier/stratigrapy.git
To run the Jupyter notebook in examples you will also need tqdm, cmocean, pyvista, trame, trame-vtk, trame-vuetify, and jupyter, which you can install from pip too:
pip install tqdm cmocean pyvista trame trame-vtk trame-vuetify jupyter
You can also install everything using conda and the environment.yml file included in this repository:
conda env create -f environment.yml
Usage
StratigraPy follows Landlab's API and you can check Landlab's extensive documentation to get an idea of its features. Here's a very basic example of setting up and running a model:
import numpy as np
import matplotlib.pyplot as plt
from stratigrapy import RasterModelGrid
from stratigrapy.components import GravityDrivenRouter

# Create the grid with two sediment classes
grid = RasterModelGrid((50, 50),
                       xy_spacing=(500., 500.),
                       number_of_classes=2,
                       initial_allocation=1020,
                       number_of_layers_to_fuse=20,
                       number_of_top_layers=20)
grid.set_closed_boundaries_at_grid_edges(True, True, True, False)

# Define the initial topography
elevation = grid.add_zeros('topographic__elevation', at='node', clobber=True)
elevation[grid.y_of_node > 15000.] = 100.

# Define the bathymetry
bathymetry = grid.add_zeros('bathymetric__depth', at='node', clobber=True)

# Define a diffusion component
gdr = GravityDrivenRouter(grid, diffusivity_cont=[2e-1, 2e-2])

# Run the simulation
for i in range(1000):
    gdr.run_one_step(100.)
    grid.stacked_layers.fuse(time=np.mean)
grid.stacked_layers.fuse(finalize=True, time=np.mean)

# Plot a slice through the domain with sediments and bedrock
fig, ax = plt.subplots(figsize=(8, 4))
pc = grid.plot_layers(ax, 'composition', i_class=1, mask_wedges=True, cmap='pink', zorder=2)
fig.colorbar(pc[0], ax=ax, label='Fraction of the second sediment class')
raster_y = grid.y_of_node[grid.core_nodes].reshape(grid.cell_grid_shape)[:, 24]
raster_z = grid.at_node['topographic__elevation'][grid.core_nodes].reshape(grid.cell_grid_shape)[:, 24]
ymin, ymax = ax.get_ylim()
ax.fill_between(raster_y, raster_z, ymin, color='#d9d9d9', zorder=1)
ax.set(xlabel='y (m)', ylabel='z (m)', ylim=(ymin, ymax));
You can find more complete examples in the folder examples.
Citation
If you use StratigraPy in your research, please cite the original article(s) describing the method(s) you used (see the docstrings for the references). An acknowledgment of StratigraPy's use is always appreciated.
Credits
This software was written by:
Guillaume Rongier  |
|---|
License
Copyright notice: Technische Universiteit Delft hereby disclaims all copyright interest in the program StratigraPy written by the Author(s). Prof.dr.ir. S.G.J. Aarninkhof, Dean of the Faculty of Civil Engineering and Geosciences
© 2025-2026, Guillaume Rongier
This work is licensed under a MIT OSS licence, see LICENSE for more information.
1 maintainer

Release files for stratigrapy 0.0.3
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | |
|---|---|---|---|
| stratigrapy-0.0.3.tar.gz | 60.4 kB | Details |
Built distributions (wheels)
Total release size: 46.3 MB
Release files / stratigrapy-0.0.3.tar.gz
| Download URL | stratigrapy-0.0.3.tar.gz |
|---|---|
| Size | 60.4 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
be1a5583ab16616c846bb3bc1680fb8f599d7d53f72719aa5bf50ef8e77d9716
|
|
BLAKE2b-256 checksum How to use checksums |
ab0fc364d891d75c5da44ee5991ef355f4aa348dedff16e87c27b79a80be02db
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.12
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jul 15, 2026.
Transparency logRelease files / stratigrapy-0.0.3-cp314-cp314-win_amd64.whl
| Download URL | stratigrapy-0.0.3-cp314-cp314-win_amd64.whl |
|---|---|
| Size | 712.6 kB |
| Tags | CPython 3.14 Windows x86-64 |
|
SHA-256 checksum How to use checksums |
547eabda560f4a298c4b4f0c2fd1934dfb5615a8e954d1d9b4e8d174bf3f856f
|
|
BLAKE2b-256 checksum How to use checksums |
2a4319dcedd3f634116b90548a3a842296c7e7c8b9dc266d2cc6c93c02aa0c87
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.12
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jul 15, 2026.
Transparency logRelease files / stratigrapy-0.0.3-cp314-cp314-manylinux2014_x86_64.manylinux_2_17_x86_64.manylinux_2_28_x86_64.whl
| Download URL | stratigrapy-0.0.3-cp314-cp314-manylinux2014_x86_64.manylinux_2_17_x86_64.manylinux_2_28_x86_64.whl |
|---|---|
| Size | 4.7 MB |
| Tags | CPython 3.14 Linux glibc 2.17+ x86-64 Linux glibc 2.28+ x86-64 |
|
SHA-256 checksum How to use checksums |
d6c4ce1df72eece2c25577e8a2c08b687693caf6d2e37525471942f0b9be7e65
|
|
BLAKE2b-256 checksum How to use checksums |
9db0cbbc6b6e3ee8446c10c6a14b01faf5876d113524f502f74a73e3923a10fe
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.12
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jul 15, 2026.
Transparency logRelease files / stratigrapy-0.0.3-cp314-cp314-manylinux2014_aarch64.manylinux_2_17_aarch64.manylinux_2_28_aarch64.whl
| Download URL | stratigrapy-0.0.3-cp314-cp314-manylinux2014_aarch64.manylinux_2_17_aarch64.manylinux_2_28_aarch64.whl |
|---|---|
| Size | 4.6 MB |
| Tags | CPython 3.14 Linux glibc 2.17+ ARM64 Linux glibc 2.28+ ARM64 |
|
SHA-256 checksum How to use checksums |
9816ca0b06dc9e66d7dcdc5036fd1f8ad512b7589c21bb9a2c15ca1b7df8bab2
|
|
BLAKE2b-256 checksum How to use checksums |
3e163da4aeebb6bd20e09245803125e17da20b12db272de0d5c99cab9f92e3b5
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.12
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jul 15, 2026.
Transparency logRelease files / stratigrapy-0.0.3-cp314-cp314-macosx_11_0_arm64.whl
| Download URL | stratigrapy-0.0.3-cp314-cp314-macosx_11_0_arm64.whl |
|---|---|
| Size | 693.1 kB |
| Tags | CPython 3.14 macOS 11.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
359ad9399c4b7a9b98f67f634d63a0e31d3fe7e89320f68ae86718e026591c92
|
|
BLAKE2b-256 checksum How to use checksums |
ff3d5bb294f272ecc4c14c76c415ebd04403bef2428ea8a120d0a241b2eb8f05
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.12
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jul 15, 2026.
Transparency logRelease files / stratigrapy-0.0.3-cp314-cp314-macosx_10_15_x86_64.whl
| Download URL | stratigrapy-0.0.3-cp314-cp314-macosx_10_15_x86_64.whl |
|---|---|
| Size | 810.5 kB |
| Tags | CPython 3.14 macOS 10.15+ x86-64 |
|
SHA-256 checksum How to use checksums |
6967d306ac282b2d89fd77c7258852e16364d6b4e6e8e3031cecbd6306648df7
|
|
BLAKE2b-256 checksum How to use checksums |
8abe922020c6f13ded89afbe69666f2c7183f8a3420058c8affbe8662a49c7a4
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.12
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jul 15, 2026.
Transparency logRelease files / stratigrapy-0.0.3-cp313-cp313-win_amd64.whl
| Download URL | stratigrapy-0.0.3-cp313-cp313-win_amd64.whl |
|---|---|
| Size | 693.4 kB |
| Tags | CPython 3.13 Windows x86-64 |
|
SHA-256 checksum How to use checksums |
ca4cd5f96aac53b9053b75045d50539fdaa65cd522c3aa8d01035a7d39fa1421
|
|
BLAKE2b-256 checksum How to use checksums |
3de9e68856a423b1a18d7438535d675febf07330fbf455d4c7866ed8c36a1e27
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.12
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jul 15, 2026.
Transparency logRelease files / stratigrapy-0.0.3-cp313-cp313-manylinux2014_x86_64.manylinux_2_17_x86_64.manylinux_2_28_x86_64.whl
| Download URL | stratigrapy-0.0.3-cp313-cp313-manylinux2014_x86_64.manylinux_2_17_x86_64.manylinux_2_28_x86_64.whl |
|---|---|
| Size | 4.7 MB |
| Tags | CPython 3.13 Linux glibc 2.17+ x86-64 Linux glibc 2.28+ x86-64 |
|
SHA-256 checksum How to use checksums |
431c628112ed6454f036228e80814ffb8b90c1a0ff04ba1c231fc7dc2206ad3a
|
|
BLAKE2b-256 checksum How to use checksums |
7e501595cb2f844eb57e7253948dd60743758d09284e5ba43850b0fbeb10fbbb
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.12
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jul 15, 2026.
Transparency logRelease files / stratigrapy-0.0.3-cp313-cp313-manylinux2014_aarch64.manylinux_2_17_aarch64.manylinux_2_28_aarch64.whl
| Download URL | stratigrapy-0.0.3-cp313-cp313-manylinux2014_aarch64.manylinux_2_17_aarch64.manylinux_2_28_aarch64.whl |
|---|---|
| Size | 4.6 MB |
| Tags | CPython 3.13 Linux glibc 2.17+ ARM64 Linux glibc 2.28+ ARM64 |
|
SHA-256 checksum How to use checksums |
d2c5deb0a52723edd28899d53087d5ee1d5d7fb0320ab6cdc2e39a09f10631ca
|
|
BLAKE2b-256 checksum How to use checksums |
51c0b7eee34dbabb98eb5767ab81d54f40f7c5ca5171eb5bc3d051926c3abcdc
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.12
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jul 15, 2026.
Transparency logRelease files / stratigrapy-0.0.3-cp313-cp313-macosx_11_0_arm64.whl
| Download URL | stratigrapy-0.0.3-cp313-cp313-macosx_11_0_arm64.whl |
|---|---|
| Size | 688.7 kB |
| Tags | CPython 3.13 macOS 11.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
53bcf62514ac0850ca041204a9c973d7bc6322842f630cfad6a6563f3d799c9d
|
|
BLAKE2b-256 checksum How to use checksums |
5e4e2e2fdda96b5cac57714bd9af1ec5b94079eb39234c5c59fea584683fb260
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.12
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jul 15, 2026.
Transparency logRelease files / stratigrapy-0.0.3-cp313-cp313-macosx_10_13_x86_64.whl
| Download URL | stratigrapy-0.0.3-cp313-cp313-macosx_10_13_x86_64.whl |
|---|---|
| Size | 808.9 kB |
| Tags | CPython 3.13 macOS 10.13+ x86-64 |
|
SHA-256 checksum How to use checksums |
d1aa1b9c538d289c327421f79df6fc29e4807aa1b136cd0cf3f144d65da52150
|
|
BLAKE2b-256 checksum How to use checksums |
9b65046a7437ee039048cb254171f08fcb30cbdb79180ee8a53fd302e0d04a73
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.12
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jul 15, 2026.
Transparency logRelease files / stratigrapy-0.0.3-cp312-cp312-win_amd64.whl
| Download URL | stratigrapy-0.0.3-cp312-cp312-win_amd64.whl |
|---|---|
| Size | 695.8 kB |
| Tags | CPython 3.12 Windows x86-64 |
|
SHA-256 checksum How to use checksums |
e65fef84543c1169455df80976d9d63af444345723f225e71e98e575874444e6
|
|
BLAKE2b-256 checksum How to use checksums |
8a22f59b03b1be605e08430b50197c5fc50a903872c3d0b7fe01e6a2797f6ab6
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.12
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jul 15, 2026.
Transparency logRelease files / stratigrapy-0.0.3-cp312-cp312-manylinux2014_x86_64.manylinux_2_17_x86_64.manylinux_2_28_x86_64.whl
| Download URL | stratigrapy-0.0.3-cp312-cp312-manylinux2014_x86_64.manylinux_2_17_x86_64.manylinux_2_28_x86_64.whl |
|---|---|
| Size | 4.8 MB |
| Tags | CPython 3.12 Linux glibc 2.17+ x86-64 Linux glibc 2.28+ x86-64 |
|
SHA-256 checksum How to use checksums |
e61863d10c00e45b78e49272a38b5a2d4bebb50916831a3d4a054987695f6970
|
|
BLAKE2b-256 checksum How to use checksums |
78a55f21612c41de48302da2794e7a35671c2f92f8788c171e904db89a79700f
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.12
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jul 15, 2026.
Transparency logRelease files / stratigrapy-0.0.3-cp312-cp312-manylinux2014_aarch64.manylinux_2_17_aarch64.manylinux_2_28_aarch64.whl
| Download URL | stratigrapy-0.0.3-cp312-cp312-manylinux2014_aarch64.manylinux_2_17_aarch64.manylinux_2_28_aarch64.whl |
|---|---|
| Size | 4.7 MB |
| Tags | CPython 3.12 Linux glibc 2.17+ ARM64 Linux glibc 2.28+ ARM64 |
|
SHA-256 checksum How to use checksums |
3f80a3be89c9d2c92afbafa253254550b12f8eee8ac29a421815599775c15e23
|
|
BLAKE2b-256 checksum How to use checksums |
9ea4a315e957b3eaee07862b406a0a453e10e3e151c7f92a8def63b3dda4d241
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.12
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jul 15, 2026.
Transparency logRelease files / stratigrapy-0.0.3-cp312-cp312-macosx_11_0_arm64.whl
| Download URL | stratigrapy-0.0.3-cp312-cp312-macosx_11_0_arm64.whl |
|---|---|
| Size | 693.5 kB |
| Tags | CPython 3.12 macOS 11.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
9e70a42c75425a5e7c6fdfe50c7092f71191c3221804564b606aceb3e79141cb
|
|
BLAKE2b-256 checksum How to use checksums |
b7c44222bc2c78c492eb5b843d2cf4bedc4fa115541614fecdb38050de41ac6e
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.12
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jul 15, 2026.
Transparency logRelease files / stratigrapy-0.0.3-cp312-cp312-macosx_10_13_x86_64.whl
| Download URL | stratigrapy-0.0.3-cp312-cp312-macosx_10_13_x86_64.whl |
|---|---|
| Size | 813.7 kB |
| Tags | CPython 3.12 macOS 10.13+ x86-64 |
|
SHA-256 checksum How to use checksums |
dd7109379f0e63f5339ef6cd681ba1af7d3a4add5cefccf57b95715898dca96a
|
|
BLAKE2b-256 checksum How to use checksums |
dbb62518c1e824c04fe0da81e7f78a075e36510e2ba61e8365c3bca42b688f4c
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.12
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jul 15, 2026.
Transparency logRelease files / stratigrapy-0.0.3-cp311-cp311-win_amd64.whl
| Download URL | stratigrapy-0.0.3-cp311-cp311-win_amd64.whl |
|---|---|
| Size | 685.7 kB |
| Tags | CPython 3.11 Windows x86-64 |
|
SHA-256 checksum How to use checksums |
10197e94a2be757609d55d5f57562cafc4742c06e6de9291d7e8615e740830f3
|
|
BLAKE2b-256 checksum How to use checksums |
3108be7944d400a9417733def4fd9474fcf89aaa65a59f0824bda7a695b7edef
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.12
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jul 15, 2026.
Transparency logRelease files / stratigrapy-0.0.3-cp311-cp311-manylinux2014_x86_64.manylinux_2_17_x86_64.manylinux_2_28_x86_64.whl
| Download URL | stratigrapy-0.0.3-cp311-cp311-manylinux2014_x86_64.manylinux_2_17_x86_64.manylinux_2_28_x86_64.whl |
|---|---|
| Size | 4.7 MB |
| Tags | CPython 3.11 Linux glibc 2.17+ x86-64 Linux glibc 2.28+ x86-64 |
|
SHA-256 checksum How to use checksums |
daa6ca060be7cb31370ca4e0c3d6a9c03a304852051e7efcc567770688752763
|
|
BLAKE2b-256 checksum How to use checksums |
41cedc0e84ccd1cce319504e9bae15f979d04be5e139ed79735b92f344959266
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.12
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jul 15, 2026.
Transparency logRelease files / stratigrapy-0.0.3-cp311-cp311-manylinux2014_aarch64.manylinux_2_17_aarch64.manylinux_2_28_aarch64.whl
| Download URL | stratigrapy-0.0.3-cp311-cp311-manylinux2014_aarch64.manylinux_2_17_aarch64.manylinux_2_28_aarch64.whl |
|---|---|
| Size | 4.6 MB |
| Tags | CPython 3.11 Linux glibc 2.17+ ARM64 Linux glibc 2.28+ ARM64 |
|
SHA-256 checksum How to use checksums |
fff19430d71ad90717a532db534a303c495566ffadc49caf9c61bbf8b04e4fb4
|
|
BLAKE2b-256 checksum How to use checksums |
ed57e03ff04daf191493f3f77f0f350edb6c0d9d26bf13290445bb90dd97e078
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.12
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jul 15, 2026.
Transparency logRelease files / stratigrapy-0.0.3-cp311-cp311-macosx_11_0_arm64.whl
| Download URL | stratigrapy-0.0.3-cp311-cp311-macosx_11_0_arm64.whl |
|---|---|
| Size | 688.2 kB |
| Tags | CPython 3.11 macOS 11.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
e9c462ebe640a828bdc5dfde030f9fd779eab3d25a62797f25547b380a891429
|
|
BLAKE2b-256 checksum How to use checksums |
2450246feaa1da226d18dc88ee4ad2cc37bad76ae0818fa81b2b46178ca2068b
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.12
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jul 15, 2026.
Transparency logRelease files / stratigrapy-0.0.3-cp311-cp311-macosx_10_9_x86_64.whl
| Download URL | stratigrapy-0.0.3-cp311-cp311-macosx_10_9_x86_64.whl |
|---|---|
| Size | 797.1 kB |
| Tags | CPython 3.11 macOS 10.9+ x86-64 |
|
SHA-256 checksum How to use checksums |
eefa67cefe3ddde815c60e957b9aa29e2fb01d2039bdbc5fcc06fb9c75bdac00
|
|
BLAKE2b-256 checksum How to use checksums |
70cbb3ce030f734da5f869c420a59c2117d1b27fb2a3ad98dec62f8c8a13a828
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.12
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jul 15, 2026.
Transparency log













