
StringCheese
StringCheese is a script written in Python to extract CTF flags (or any other pattern with a prefix) automatically.
It works like a simple strings | grep command, but can detect many encodings (like base64, XOR, rot13) and works on file formats other than plaintext.
Installation
Use the package manager pip to install StringCheese.
sudo pip install stringcheese
Usage
StringCheese only needs to know the flag prefix to work. You can pass it the input file using the --file option or through stdin.
stringcheese FLAG{ --file input.txt
cat  input.txt | stringcheese FLAG{
How it works
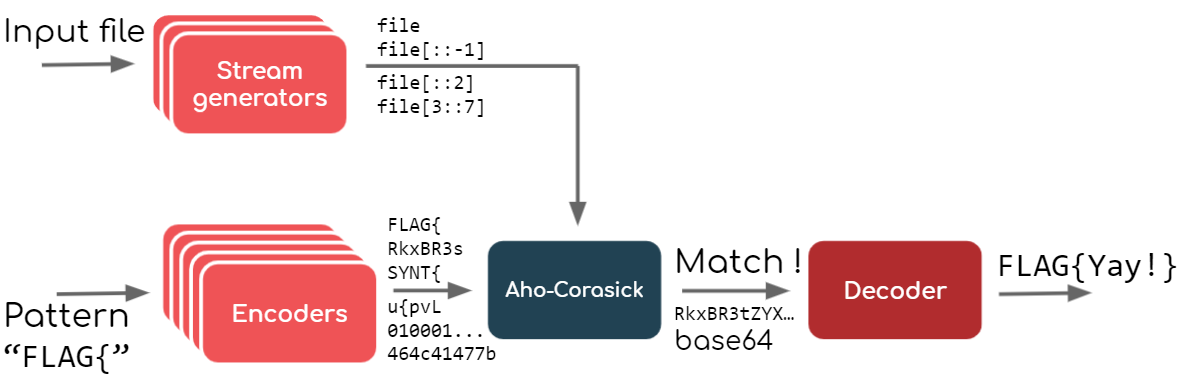
StringCheese generates strings which encode the flag prefix in various ways.
Those strings are then searched in several transformed version of the input file : one in two bytes, reversed, etc.
When the encoded flag prefix is found somewhere, the corresponding decoder is called to regenerate the flag.
Authors and contributors
Contributing
Pull requests are welcome. For major changes, please open an issue first to discuss what you would like to change.
License
1 maintainer

Metadata
1 maintainer
Release files for stringcheese 2.1
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| stringcheese-2.1.tar.gz | 107.4 kB | Without provenance | Details |
Release files / stringcheese-2.1.tar.gz
| Download URL | stringcheese-2.1.tar.gz |
|---|---|
| Size | 107.4 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
929efbee18fa6a57b9ebd6d9588e8de83ae5a87e47817fd6772c85e05c12dd66
|
|
BLAKE2b-256 checksum How to use checksums |
55e22abc86d2957fe0e1f94d65ab5b96062528c4d4bc09e058bd9fd4b06f0086
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/3.4.1 importlib_metadata/4.3.1 pkginfo/1.7.0 requests/2.25.1 requests-toolbelt/0.9.1 tqdm/4.60.0 CPython/3.9.2
|
Security for stringcheese 2.1
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.














