
szpont
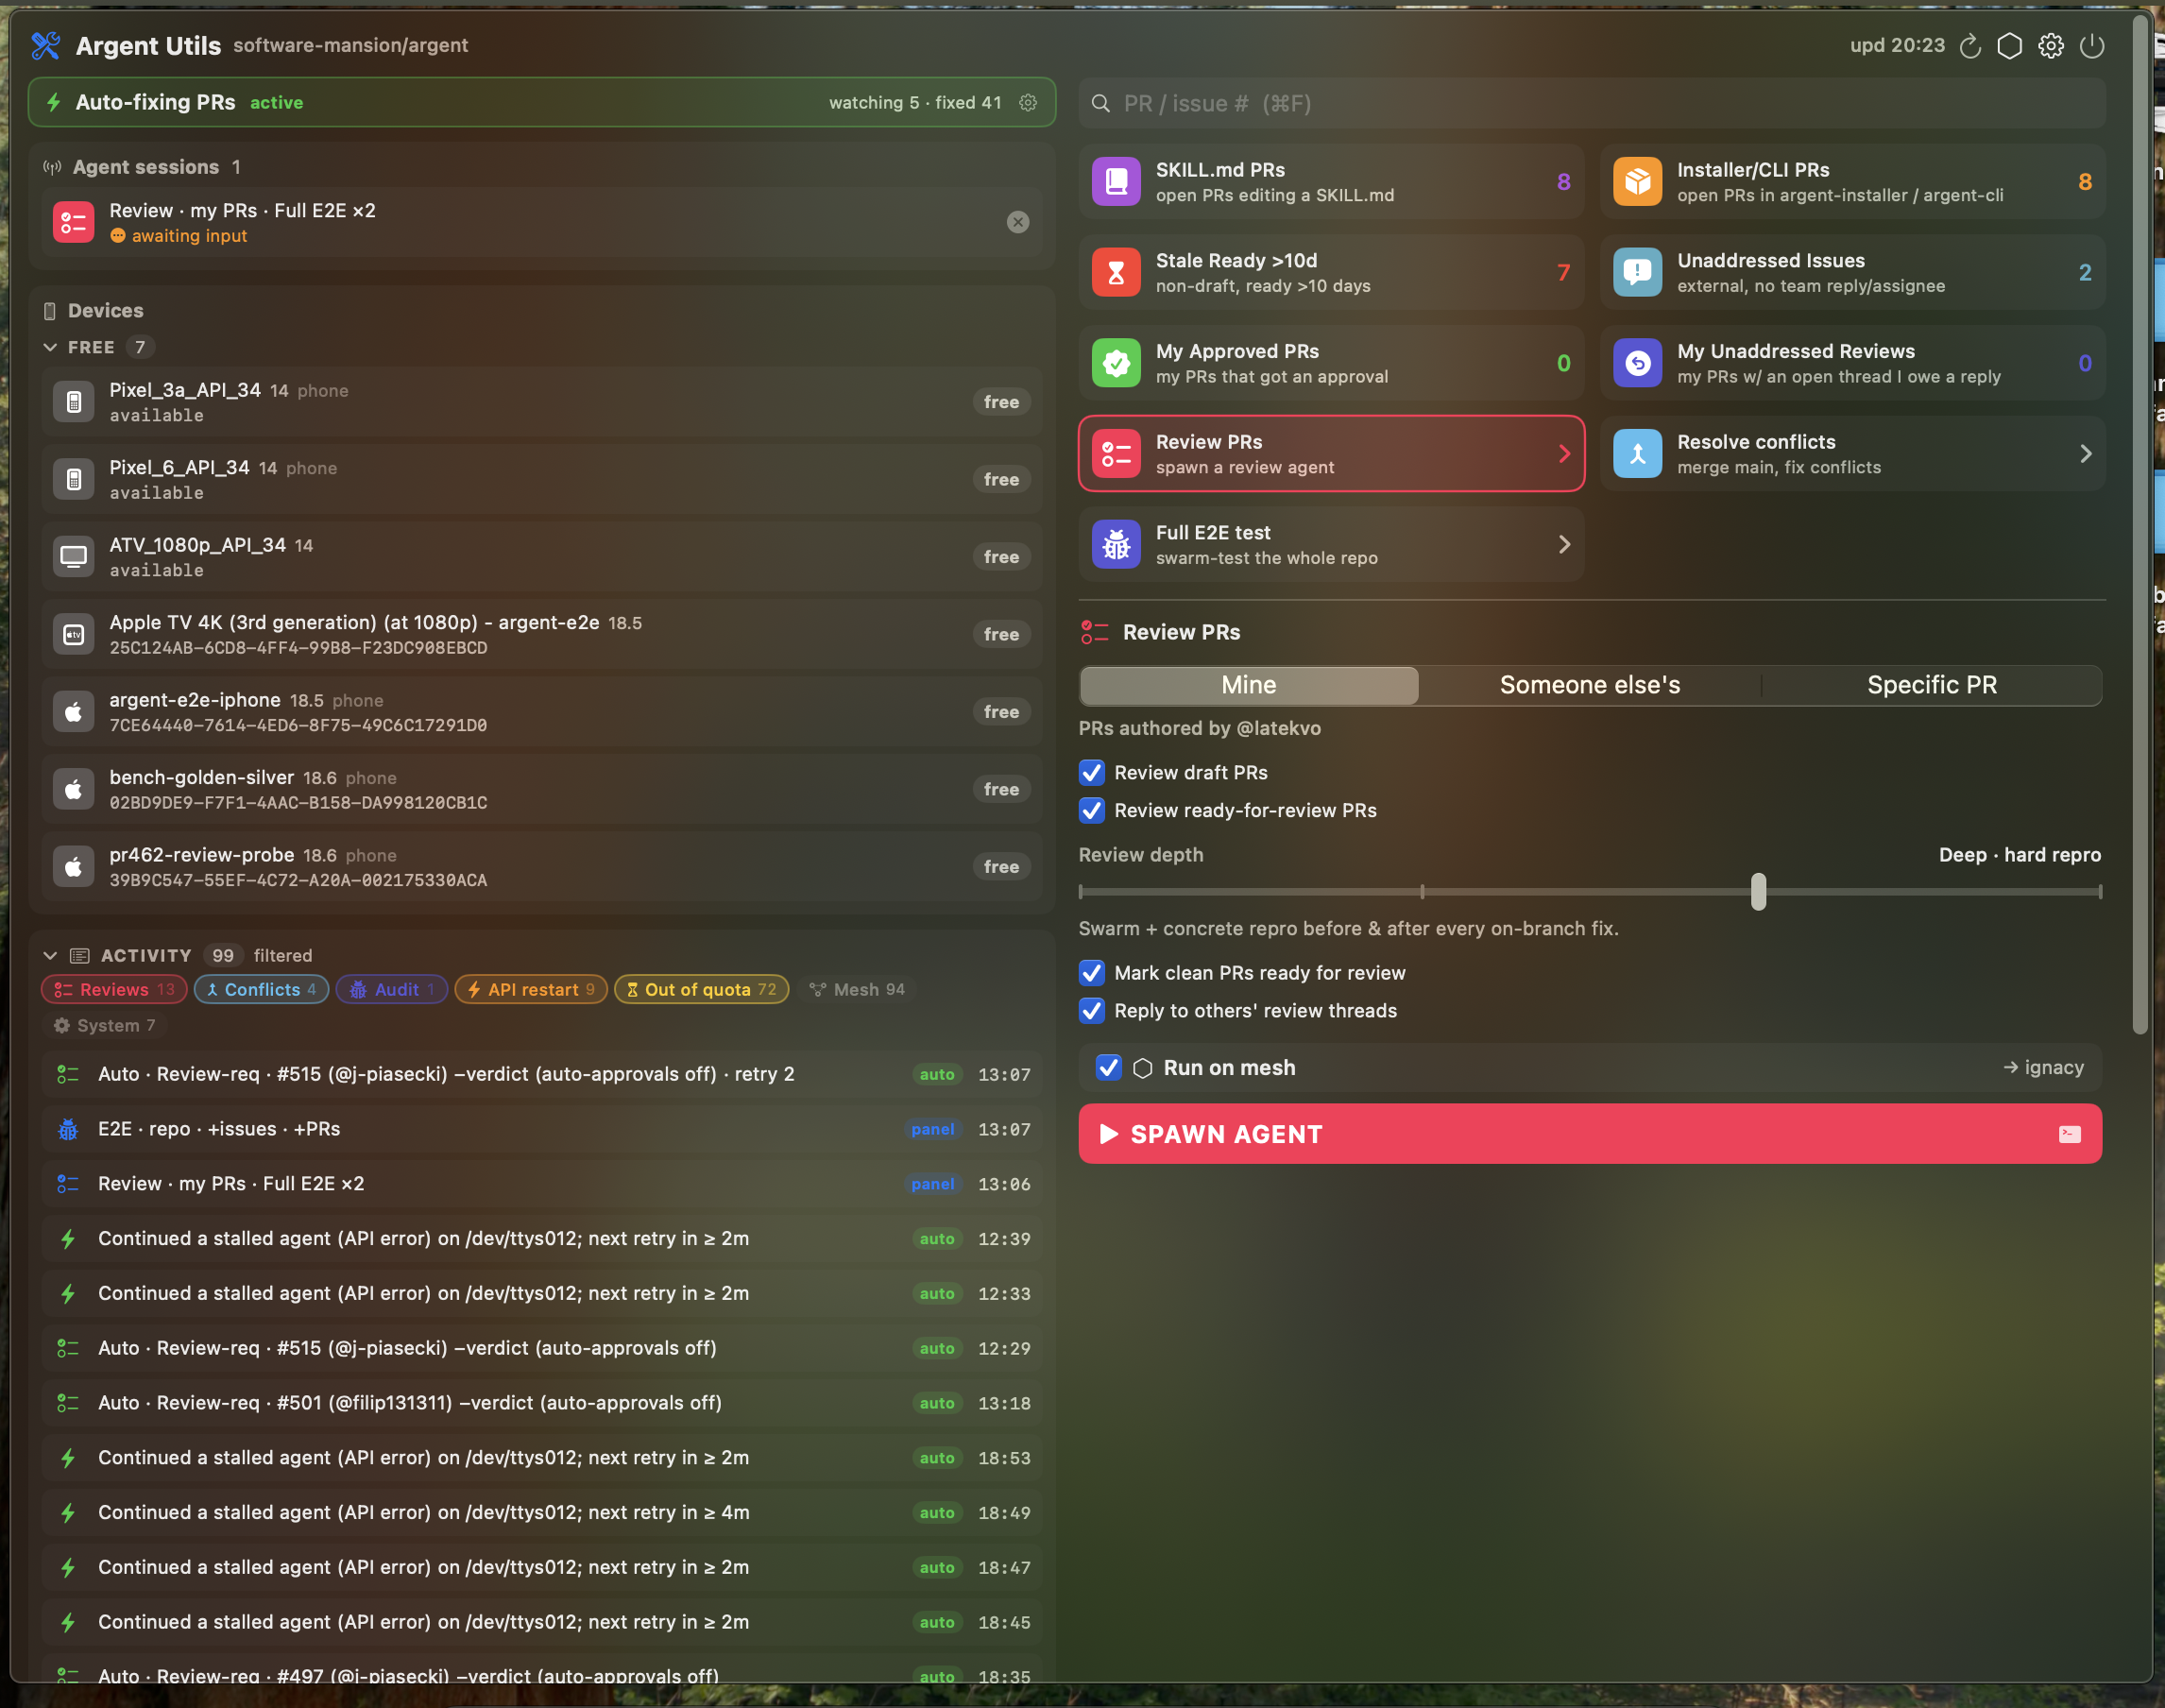
Installs and starts Diplomat (Szpont Yon), a menu-bar / system-tray app that runs coding agents against a GitHub repo: it reviews PRs, fixes your own, resolves conflicts, and gives each agent its own device.
pip install szpont && szpont # or: npx szpont
macOS and Linux.
How it works
Diplomat runs from a git checkout, and its Update button and daily 06:00 update are git operations on that checkout. So this package doesn't ship a copy of Diplomat; it fetches the checkout and runs the scripts already in the repository:
| macOS | Linux | |
|---|---|---|
| get it | git clone into ~/.diplomat/checkout, or fast-forward it |
same |
| build it | install/build-app.sh → Diplomat.app |
install/build-core.sh when the prompt binary is missing |
| set it up | - | a venv at ~/.diplomat/venv with requirements.txt in it |
| start it | open -n Diplomat.app |
the package's own ./diplomat, on the venv's interpreter |
The venv is only rebuilt when requirements.txt changes, and the Swift prompt
binary only when the applet can't find one. You need git and a Swift toolchain; if
either is missing, szpont says which before downloading anything.
szpont --plan        # print what would be run, as JSON, and do none of it
szpont --no-update   # launch the checkout as it stands
szpont -- --dump     # everything after -- goes to the applet
DIPLOMAT_SELF_REPO points at your own checkout, which is never updated since it
may have work in it. DIPLOMAT_REPO_URL clones from a fork.
npm
npx szpont runs the same launcher, written separately in JavaScript. Neither has
dependencies. packages/szpont-npm/test/parity-with-python.mjs runs both against
every machine in test/scenarios.mjs and fails if their plans differ.
Diplomat's machines find each other over
SzpontNet,
published separately as szpontnet. This package doesn't install it.
Tests
pip install pytest
pytest packages/szpont/tests -q
The name
szpont is also the import name of the SzpontNet
conformance tester,
run as python -m szpont from its own directory. They don't collide: this package
installs a szpont console script and a szpont_launcher module, and never the
szpont import name. CI checks that the built wheel keeps it that way.
1 maintainer

Metadata
1 maintainer
Release files for szpont 0.98.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| szpont-0.98.0.tar.gz | 15.8 kB | With provenance | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| szpont-0.98.0-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 25.2 kB
Release files / szpont-0.98.0.tar.gz
| Download URL | szpont-0.98.0.tar.gz |
|---|---|
| Size | 15.8 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
f96aae2da831b1e49726d0479cef8b55c460766d9623cff19878933dbdae83b7
|
|
BLAKE2b-256 checksum How to use checksums |
c0bfdbb8f7e8b2c36257d9eea615765e106198cadfdb8f90bec8ad778bb7381b
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 24, 2026.
Transparency logRelease files / szpont-0.98.0-py3-none-any.whl
| Download URL | szpont-0.98.0-py3-none-any.whl |
|---|---|
| Size | 9.4 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
fb690cd9aeb35bae61e55eda6f37061d2028a0fee13510ec0b227a9bcefeb377
|
|
BLAKE2b-256 checksum How to use checksums |
d4a4041abf91ee6d5168b3ac54196f9d7152a3ceb21285c65ac86b724d93a312
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 24, 2026.
Transparency logSecurity for szpont 0.98.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 2 files in this release have been uploaded with provenance metadata.
Attestation for szpont-0.98.0.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 24, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














