
TactiFoot Vision
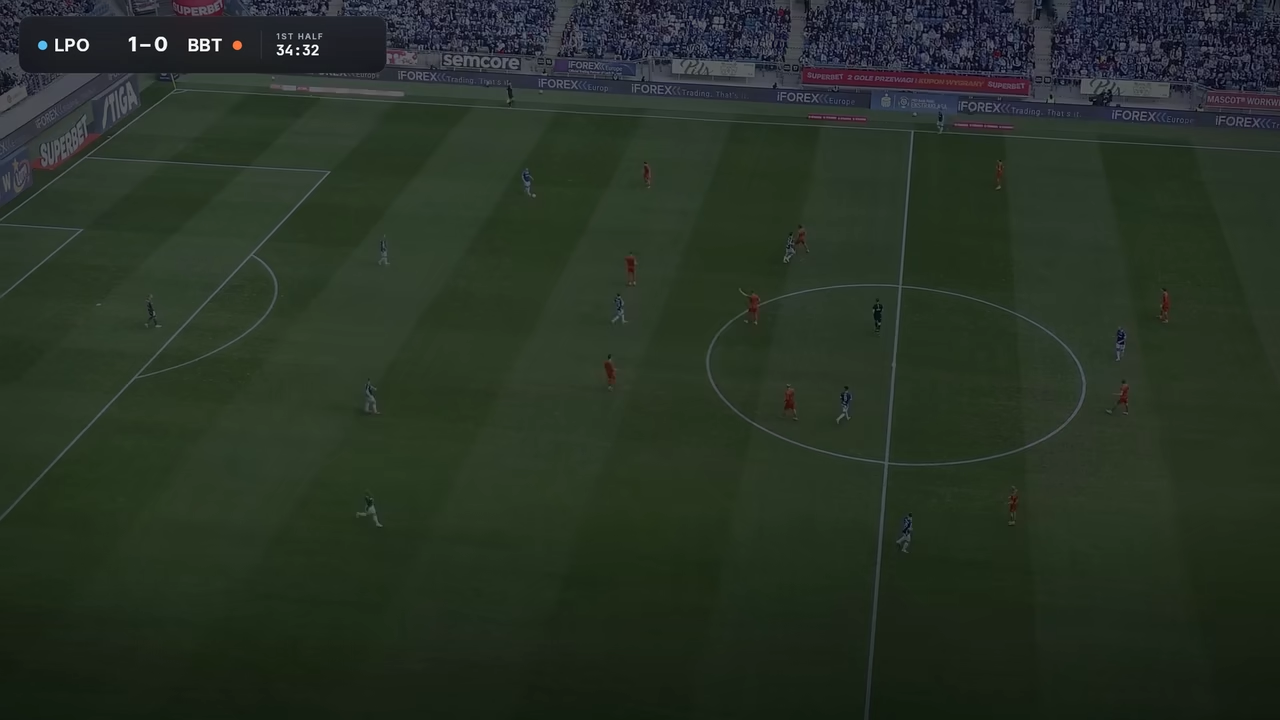
TactiFoot Vision turns football match video into tactical data. It finds and follows every player and the ball, works out who plays for which team, and maps the action onto the pitch in metres.
- Data: load, convert, split and augment annotated football datasets.
- Models: train and evaluate YOLO, RF-DETR and pitch-keypoint models through one interface.
- Pipeline: detection, tracking, team classification and homography to pitch coordinates.
- Output: tracks, StatsBomb-style freeze frames, annotated video and a tactical radar.
Quick start
To see the whole workflow without installing anything, open the overview notebook in Google Colab. It downloads an open demo match, trains a player detector for a few minutes, tracks the players and draws the tactical map:

To use the package on your own footage, install it from PyPI (Python 3.13):
pip install tactifoot-vision
import tactifoot_vision as tv

pipeline = tv.Pipeline(
    detector=tv.load_model("yolo", "models/detector_yolo11l.pt"),
    keypoint_model=tv.load_model("yolo_pose", "models/pitch_yolo11m_pose.pt"),
    team_classifier=tv.teams.TeamClassifier("siglip"),
)
result = pipeline.run("match.mp4")
tv.viz.render_video(result, "match.mp4", "annotated.mp4")
The same pipeline runs from the command line:
tactifoot init pipeline.yaml   # a commented run file to edit
tactifoot run pipeline.yaml --video match.mp4 --output-dir outputs/match
Contributing
git clone https://github.com/RedHot099/TactiFootVision.git && cd TactiFootVision
uv sync                 # the package, its dev tools and the notebook kernel
uv run pytest -q        # the fast suite
The notebooks are generated from notebooks/build/. All but the overview
notebook, and the examples, expect local data and weights; see the
notebooks README.
Learn more
- Notebooks: executed walkthroughs of every module, from data to visualisation. Start with
00_overview, which also runs in Colab. - Architecture: modules, interfaces, run files and the CLI.
- Examples: runnable scripts for each area and the CLI.
1 maintainer

Metadata
1 maintainer
Release files for tactifoot-vision 0.3.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| tactifoot_vision-0.3.0.tar.gz | 190.2 kB | With provenance | Details for tactifoot_vision-0.3.0.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| tactifoot_vision-0.3.0-py3-none-any.whl | Python 3 | none | any | Details for tactifoot_vision-0.3.0-py3-none-any.whl |
Total release size: 425.6 kB
Release files / tactifoot_vision-0.3.0.tar.gz
| Download URL | tactifoot_vision-0.3.0.tar.gz |
|---|---|
| Size | 190.2 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
be96f8c6dac2268cb14a7bbdc24c5cc92ea903cb951812f7ac9bc67f0e721b52
|
|
BLAKE2b-256 checksum How to use checksums |
270afcdb616674c6946f7a4ad1cf584ff93a5ef34c5a6c10a95c230ca56b3f34
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 16, 2026.
Transparency logRelease files / tactifoot_vision-0.3.0-py3-none-any.whl
| Download URL | tactifoot_vision-0.3.0-py3-none-any.whl |
|---|---|
| Size | 235.3 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
38acc3eb7aafbb2c3db5fbce713b62b45124881496bcc9f1c09d0c04aa7f880d
|
|
BLAKE2b-256 checksum How to use checksums |
a9e3bea942da1af0ed54edebb86f14dbfa170fc60fa965c8f423a38ff0f557aa
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 16, 2026.
Transparency logSecurity for tactifoot-vision 0.3.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
Both files in this release have been uploaded with provenance metadata.
Attestation for tactifoot_vision-0.3.0.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 16, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.













