
TESS Aperture Photometry Pollution eStimator 
Note: this module is not yet fully developed. For commercial use, please wait for v1.0.0. It is expected to be in development for at least another month.
Description
A python module that calculates a contamination factor in the aperture region of a tpf based on the relative flux of the background stars and the target.
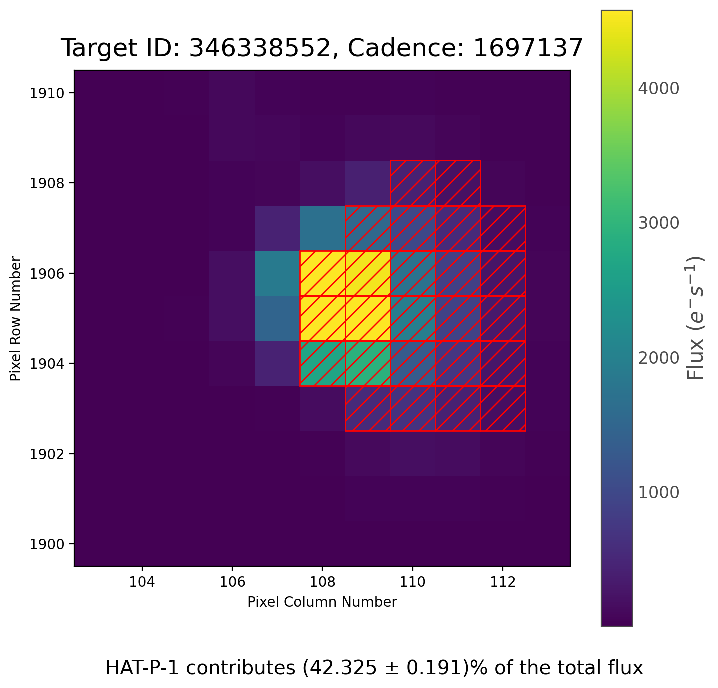
Full documentation is available here. Below is some useful information, taken from the documentation.
Installation
Prerequisites
numpy(>=1.21.2): to make all calculationsscipy(>=1.7.2): to integrate the gaussian functionastropy(>=5.0): to build data used in this moduleastroquery(>=0.4.6): to find stars in the target's regionmatplotlib(>=3.5): to plot the result (image above)lightkurve(>=2.0): to fetch and load tpf files
Python >=3.10 is required. More information about dependencies can be found here.
Install with pip install tessapps.
Running the module
Running from a notebook
A tpf is needed to run this module. If no tpf is supplied, the default is a file with HAT-P-1 (the example picture above). Here is the minimal example:
import tessapps

tessapps.run()

>>> [0.57675, 0.00191]
The first number is the contamination factor, and the second is its error. Here is a more realistic example:
import tessapps as tapps
from tessapps.search_parameters_to_tpf import find_tpf

tpf = find_tpf(TIC=346338552, mission="TESS", sector=84, exptime=120)  # HAT-P-1
contamination, error = tapps.run(tpf, result=True)

>>> The background contributes (57.675 ± 0.191)% of the total flux in the aperture region.
More information about usage in here.
Running from a terminal
Alternatively, from a terminal you can run this module as:
tapps --tpf star_tpf
python3 -m tessapps --tpf star_tpf
Authors
Leonidas Liponis
Links
PyPI page: https://pypi.org/project/tessapps/
Codeberg page: https://codeberg.org/leolip128/tessapps
Email (for contact): lliponis (at) physics.auth.gr
AI Disclosure
No LLMs were used in the making of this project. All code was generated and verified by humans, so it will only contain human-made mistakes. All commits made by bots will be refused, and commits made by humans will be checked: published code should be fully understandable by the authors.
To-Do list
- add description
- redo the examples since they reference the flux instead of the contamination factor
- add the scoring function
- add more stuff in this to-do list
1 maintainer

Metadata
1 maintainer
Release files for tessapps 0.3.3
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| tessapps-0.3.3.tar.gz | 10.6 kB | Without provenance | Details for tessapps-0.3.3.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| tessapps-0.3.3-py3-none-any.whl | Python 3 | none | any | Details for tessapps-0.3.3-py3-none-any.whl |
Total release size: 22.3 kB
Release files / tessapps-0.3.3.tar.gz
| Download URL | tessapps-0.3.3.tar.gz |
|---|---|
| Size | 10.6 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
6be61985153b80c831980cf4ed2bf8d444e195d043f7f630a3a46644af120782
|
|
BLAKE2b-256 checksum How to use checksums |
e088ea2224be9598f9fbb8037964bc4292c66c0b3c21eeb25487c3260eca0cff
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
python-requests/2.32.5
|
Release files / tessapps-0.3.3-py3-none-any.whl
| Download URL | tessapps-0.3.3-py3-none-any.whl |
|---|---|
| Size | 11.7 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
5f8fd0d39ce7fc06cfb547a8f2cd59834550c656455153bf05cba6c8a7cdb797
|
|
BLAKE2b-256 checksum How to use checksums |
60d1f89105369b757868102bf5871cbf78cc3aba408267e403d08c8a94b6a66c
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
python-requests/2.32.5
|
Security for tessapps 0.3.3
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














