
CLI command that connects two awesome tools together - Ansible Vault & Bitwarden Password Manager
Why?
At Thorgate, we deploy project using Ansible. Ansible comes with awesome encrypted storage, and every storage needs it’s own password to access it contents.
We also using Bitwarden to store company-wide passwords and sensitive information. And if we already are storing passwords to Ansible Vault’s in Bitwarden, we thought why not use Bitwarden CLI tool to pass these passwords directly to Ansible Vault?
And that’s how this project was born 😎
Getting Started
Prerequisites
We need these tools to be installed:
Python 3.9+ & Pip
Ansible project that uses Ansible Vault
We strongly recommend installing Python packages in dedicated and isolated virtual environments. There are several tools that helps manage virtual environments:
Poetry (We will be using this one)
Installation
We assume several things:
That you have existing or starting new Ansible project
That your Ansible installation lives in virtual environment
Based on these assumptions, for installation you need to add this package into your virtual environment. For example you might run $ poetry add tg-bw-helper
Setting Up With Ansible
Create if not yet existing shell script with this example content (it can be named ask-vault-pass.sh) - note that you do not need to add poetry run before invoking bw_helper here, or activate virtualenv etc., since your ansible will be already running in correct environment
#!/bin/sh
bw_helper --vault-item "Ansible Vault" --vault-item-field "Password"
Make sure that this script is executable! If not, run $ sudo chmod +x ask-vault-pass.sh
Edit ansible.cfg to specify script that Ansible will be using to get Vault password
[defaults]
vault_password_file=./ask-vault-pass.sh
Usage
Now when all these steps completed:
tg-bw-helper is installed into virtual environment where Ansible is installed
Ansible project is configured to use special script
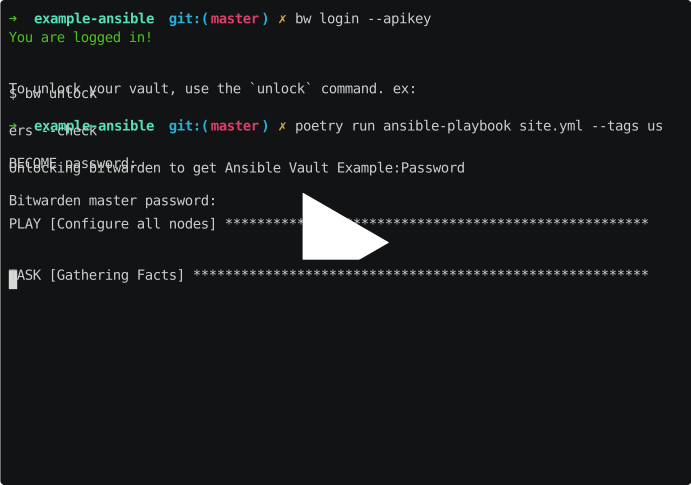
We are ready to use the tool:
Run $ bw login (Needs to be run once per user session)
Run your usual Ansible playbook that previously asked for Vault password
Enter Bitwarden master password
CLI Options
- --bw-executable
Optional, should point to bw executable, defaults to /usr/bin/bw, can also be set with TG_BW_AP_EXECUTABLE_PATH env variable
- --fallback-prompt
optional, prompt to display if bw fails, defaults to “Vault password: “, can also be set with TG_BW_AP_FALLBACK_PROMPT env variable
- --vault-item
vault item ID or name, should be specific since tool will fail if multiple items are found
Item name is what you see as it’s name in bitwarden UI
Item ID is useful if you have two items with same name, you can learn it by using bitwarden CLI (use bw login to login, follow the instructions for how to pass the session information over to the next command, and then use bw list items --search <item name>. You will get json array of matching objects, each object will have ID that you can use.)
- --vault-item-field
optional, field to use on the item. If not specified, password is used. Examples:
You have an item “Awesome project ansible vault” with password “123”, and you want to use “123”. You do not specify --valut-item-field in this case.
You have an item “Ansible secrets” with password set to “abc”, that has additional fields “Test server ansible” set to “123” and “Live server ansible” set to “456”, and you want to use “123”. You specify --valut-item-field="Test server ansible" in this case.
Environment
If BW_SESSION is set in environment, it will be used instead of asking bitwarden master password to unlock bitwarden.
If using linux, you can opt to save the bitwarden session in linux kernel secret storage by setting TG_BW_SESSION_SECRET_NAME environment variable to to some string (preferably random) that will be used to store the secret on user’s session keyring.
Contributing
Contributions are what make the open source community such an amazing place to learn, inspire, and create. Any contributions you make are greatly appreciated.
Developing
For local development project repository contains pyproject.toml and poetry.lock. When using them with Poetry you will be able to recreate ready to use environment.
We also added Makefile that contains lots of useful commands to help setup the project, run tests and lint code. Do check it out by running make
Opening MR
Clone the Project
Create your Feature Branch (git checkout -b feature/AmazingFeature)
Commit your Changes (git commit -m 'Add some AmazingFeature')
Push to the Branch (git push origin feature/AmazingFeature)
Open a Merge Request
License
Distributed under the MIT License. See LICENSE for more information.
1 maintainer

Metadata
1 maintainer
Release files for tg-bw-helper 1.1.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| tg_bw_helper-1.1.0.tar.gz | 12.2 kB | Without provenance | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| tg_bw_helper-1.1.0-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 27.3 kB
Release files / tg_bw_helper-1.1.0.tar.gz
| Download URL | tg_bw_helper-1.1.0.tar.gz |
|---|---|
| Size | 12.2 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
91e1786b09e4e1278d8af1702dfc46b7addd6acc1442219933f3f96ccca7f9c8
|
|
BLAKE2b-256 checksum How to use checksums |
3944ef75d0cfa09c43b996531113e7c7b01eb821e600928528da7cde3af9f4bf
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
poetry/2.2.0.dev0 CPython/3.13.11 Linux/6.18.5-arch1-1
|
Release files / tg_bw_helper-1.1.0-py3-none-any.whl
| Download URL | tg_bw_helper-1.1.0-py3-none-any.whl |
|---|---|
| Size | 15.1 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
7d35d36655d67a41ee8019b6436cd7b577c13db020c098ada621cf649d6d7696
|
|
BLAKE2b-256 checksum How to use checksums |
fe3e8842b11c509878654d3a1aaa587f1b3055598d53bc4d36bd4bf3ece4301a
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
poetry/2.2.0.dev0 CPython/3.13.11 Linux/6.18.5-arch1-1
|
Security for tg-bw-helper 1.1.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














