
The Third Eye
AI model health and governance control plane for Databricks
Watch. Understand. Act.
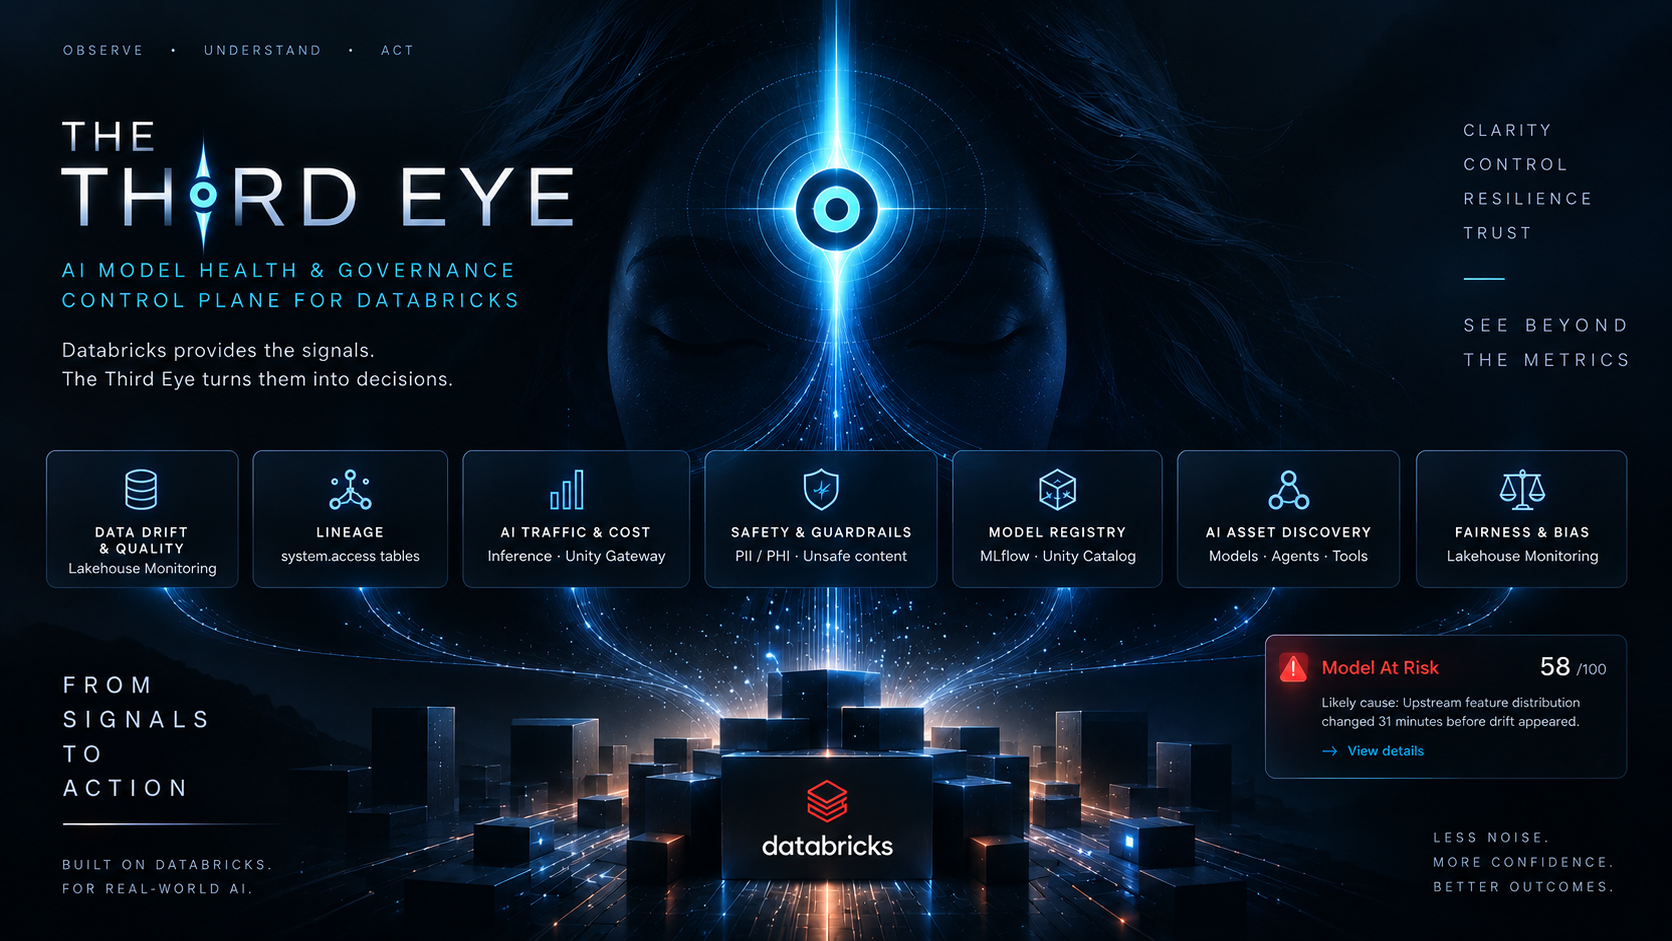
Databricks provides the signals. The Third Eye turns them into decisions.


What is The Third Eye?
The Third Eye is a Databricks-native AI health and governance control plane.
It does not replace Model Serving, MLflow, Unity Catalog, Lakehouse Monitoring, Unity Gateway, or Workflows. It sits above those primitives and turns their signals into an explainable operating view:
Databricks signals
      │
      ├── monitoring
      ├── inference / trace
      ├── lineage
      ├── usage / cost
      └── governance / guardrails
      │
      ▼
The Third Eye
      │
      ├── normalize
      ├── correlate
      ├── score
      ├── explain
      └── recommend
      │
      ▼
governed model health
      │
      ├── dashboard
      ├── Genie
      └── Teams / Slack
Positioning: not another drift detector. Not another dashboard. The Third Eye is the decision layer above the native Databricks AI stack.
Why this exists
AI fleets fail in ways that are difficult to diagnose from a single metric.
A model can look healthy in one system while another already shows a warning:
- feature drift is rising
- quality is deteriorating
- an upstream table changed
- token or endpoint cost spiked
- a gateway policy was breached
- model criticality makes the event more urgent
The Third Eye correlates these signals into a single evidence-backed health view.
The core distinction
Traditional monitoring:
metric → threshold → alert

The Third Eye:
signals → correlation → context → risk → explanation → action
Core capabilities
| Capability | What The Third Eye adds |
|---|---|
| Zero-touch discovery | Builds a governed model inventory from MLflow, Unity Catalog, and Gateway assets |
| Signal normalization | Creates a common index over native Databricks signals |
| Evidence correlation | Links drift, quality, usage, guardrail, and lineage events |
| Composite health | Produces a criticality-aware 0-100 health score |
| Confidence | Separates strong evidence from incomplete evidence |
| Root cause | Generates evidence-grounded narratives |
| Remediation | Produces ranked next actions rather than just alerts |
| Model passport | Produces a compact governance and audit view per model |
| Decision surface | Feeds AI/BI, Genie, Teams, and Slack from governed outputs |
Architecture
┌──────────────────────── Databricks native layer ────────────────────────┐
│ Unity Catalog · MLflow · Monitoring · Inference / Trace · Lineage       │
│ Unity Gateway · Usage · Guardrails · Databricks Workflows               │
└────────────────────────────────┬────────────────────────────────────────┘
                                 │
                                 ▼
                    ┌──────────────────────────┐
                    │ Discovery & Sync         │
                    │ model / asset registry  │
                    └─────────────┬────────────┘
                                  ▼
                    ┌──────────────────────────┐
                    │ Signal Normalization     │
                    │ common signal index      │
                    └─────────────┬────────────┘
                                  ▼
                    ┌──────────────────────────┐
                    │ Correlation & Scoring    │
                    │ health + confidence      │
                    └─────────────┬────────────┘
                                  ▼
                    governance.model_health.*
                         │        │        │
                         ▼        ▼        ▼
                       AI/BI    Genie   Alerts
                                  │
                                  ▼
                        Root cause / remediation
Repository structure
The repository remains the full Databricks implementation and deployment reference:
adapters/         native-signal adapters
discovery/        model and lineage discovery
scoring/          correlation and health scoring jobs
remediation/     root-cause and remediation generation
passport/         model passport generation
sql/              Unity Catalog bootstrap + governed tables
genie/            Genie instructions
copilot_studio/  notification / topic notes
workflows/       Databricks Workflow definitions
demo/             product demonstration assets
v2_stretch/       planned governed-autonomy components
third_eye/       reusable Python scoring primitives
Quickstart
Install the reusable Python package
pip install the-third-eye
Use the portable scoring kernel
from third_eye.scoring import health_score, health_tier

score = health_score(
    drift=0.30,
    quality=0.92,
    cost=0.15,
    guardrail=0.05,
)

print(f"Health: {score:.2f}")
print(f"Tier:   {health_tier(score)}")
The package is intentionally small. It exposes deterministic scoring primitives while the Databricks-specific orchestration remains in the repository.
Databricks integrations
pip install "the-third-eye[databricks]"
This optional extra installs the Databricks SDK, MLflow, and Spark dependencies used by the workspace integration layer.
Run locally
The Databricks jobs support the existing mock-mode development path:
set THIRD_EYE_MOCK_MODE=true
python scoring/compute_health_score.py
python scoring/correlate_signals.py
PowerShell:
$env:THIRD_EYE_MOCK_MODE = "true"
python scoring/compute_health_score.py
python scoring/correlate_signals.py
The health score
The central composite calculation is:
health_score = 100 - (
    w1 · drift
  + w2 · (1 - quality)
  + w3 · cost
  + w4 · guardrail
) · criticality_weight
The portable Python implementation keeps this kernel deterministic and independent of Databricks runtime concerns.
Evidence before action
The Third Eye follows a read-first, evidence-before-action principle.
A single weak signal should not automatically become a production action.
signal
  ↓
corroborating evidence
  ↓
criticality context
  ↓
risk / confidence
  ↓
incident
  ↓
root cause
  ↓
recommended action
High-impact production actions remain policy-controlled.
Security and governance
The control plane is designed around governed access rather than copying source systems.
Key principles:
- native Databricks tables remain the source of record
- normalized signals store pointers and snapshots rather than duplicating raw telemetry
- secrets should be resolved through Databricks Secrets
- high-impact automation remains policy-controlled
- evidence and confidence accompany health decisions
Roadmap
V1
Discovery → normalization → correlation → scoring → diagnosis → governed outputs.
V2
Governed autonomy:
health degradation
      ↓
candidate retraining
      ↓
champion / challenger
      ↓
approval gate
      ↓
promotion / rollback
Planned work includes blast-radius analysis, multi-workspace federation, silent-failure detection, richer compliance reporting, and cost-of-drift business impact.
Development
git clone https://github.com/dcsgod/theThirdEye.git
cd theThirdEye

python -m pip install -e ".[dev]"
ruff check .
pytest
python -m build
python -m twine check dist/*
Publishing to PyPI
The repository includes a GitHub Actions workflow for PyPI Trusted Publishing.
GitHub Release
      ↓
build sdist + wheel
      ↓
twine check
      ↓
PyPI Trusted Publishing
For the first release, configure a PyPI Trusted Publisher with:
Owner:       dcsgod
Repository:  theThirdEye
Workflow:    publish.yml
Environment: pypi
Then create a GitHub release such as:
v0.1.0
The workflow publishes the built distributions to PyPI without a long-lived API token.
License
Apache-2.0.
The Third Eye
Watch. Understand. Act.
1 maintainer

Metadata
1 maintainer
Release files for the-third-eye 0.1.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| the_third_eye-0.1.0.tar.gz | 101.2 kB | With provenance | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| the_third_eye-0.1.0-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 108.0 kB
Release files / the_third_eye-0.1.0.tar.gz
| Download URL | the_third_eye-0.1.0.tar.gz |
|---|---|
| Size | 101.2 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
5594f4020f26fe37ac2c9d45f853f1d1ac252d1735dffd33eb8503777eb89876
|
|
BLAKE2b-256 checksum How to use checksums |
cca712f019a280572639f8020299f78a2235da25d96dd02517a91048e518cfec
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 4, 2026.
Transparency logRelease files / the_third_eye-0.1.0-py3-none-any.whl
| Download URL | the_third_eye-0.1.0-py3-none-any.whl |
|---|---|
| Size | 6.9 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
84f09e6c948915c7dd00aae2a5a26c37c3acaeaa5e26b2e01fa6295605d05678
|
|
BLAKE2b-256 checksum How to use checksums |
eedd3250cc39b90a8fd21922b41ca90d0c73588e89b93a7311ca2d06407abd6f
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 4, 2026.
Transparency logSecurity for the-third-eye 0.1.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 2 files in this release have been uploaded with provenance metadata.
Attestation for the_third_eye-0.1.0.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 4, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.













