
tikra
TikZ and pgfplots figures to SVG and PNG, without a TeX install: no LaTeX, no fonts on the system, no external processes. It reimplements TikZ, pgf and pgfplots, and labels are set by mathra in Latin Modern, TeX's own Computer Modern. Try it in the browser · See the gallery.
pip install tikra
Wheels for Linux, macOS and Windows, for Python 3.9 and later; nothing else to install.
Usage
import tikra

svg = tikra.tikz_to_svg(r"""
\begin{tikzpicture}
  \draw[->] (0,0) -- (2,1) node[right] {$\vec v$};
\end{tikzpicture}
""")
open("v.svg", "w", encoding="utf-8").write(svg)
open("v.png", "wb").write(tikra.png(svg, dpi=300))

r = tikra.render(r"\tikz \draw (0,0) circle (1);")
r["warnings"]      # [] — what tikra skips or approximates is listed here, and the rest is drawn
r["alt"]           # 'Drawing of one shape, without text' — the figure in words, for those who cannot see it
tikz_to_svg(code, *, locale="en") |
The SVG as a string. locale (en, pt-BR, es, fr, de, it, ru, zh, ja, ko, hi, ar, id, tr, nl, pl) is the language of the figure in words; the drawing is the same in all. |
render(code, *, locale="en") |
A dict, the words in locale: svg; alt, the figure in one sentence (the SVG's <title>, for an image's alt text); description, the figure in words (the SVG's <desc>: a chart's axes and data, a diagram's nodes and connections); and warnings (a list of strings). When the picture has its author's text (\begin{tikzpicture}[alt={…}]), alt and description are that text. The words tikra writes are not perfect (they say what is in the drawing, not what it means, and little about free drawings): review them before publishing. |
png(svg, *, dpi=300, background=True) |
PNG bytes; background=False keeps it transparent instead of white. |
code is a full standalone document, a bare tikzpicture, an inline \tikz, an axis environment or loose TikZ statements. Errors (no figure in the input, an invalid dpi, a PNG past 100 megapixels) are ValueError. Types are included (py.typed).
What it draws
Every image below is an SVG written by tikra from a figure in the repository's corpus, on a white card; the gallery has all 227. Of the 2502 figures of the TikZ and pgfplots manuals, tikra draws 93.1% as TeX does (95.4% of the ones a converter can reproduce): docs/conformance.md.
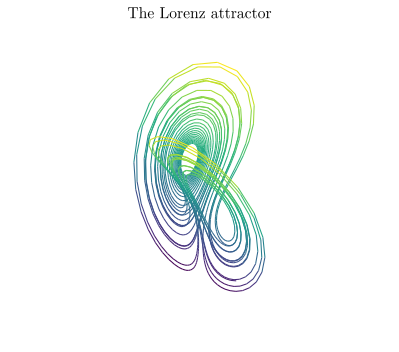 The Lorenz attractor, colored by height | 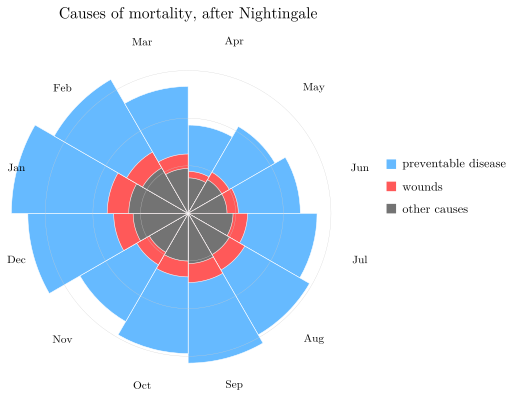 Nightingale's rose of the causes of mortality |
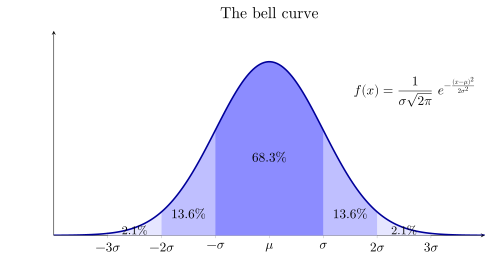 The bell curve and the 68–95–99.7 rule | 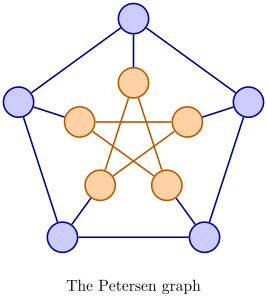 The Petersen graph |
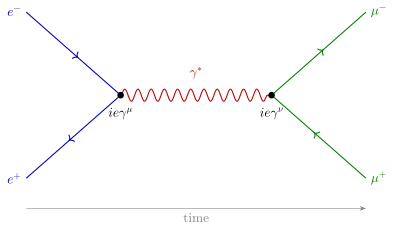 A Feynman diagram, with decorations | 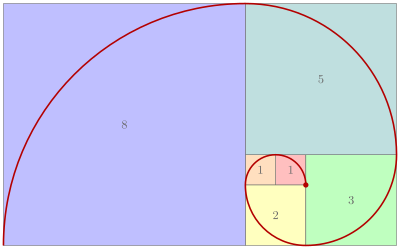 The golden spiral |
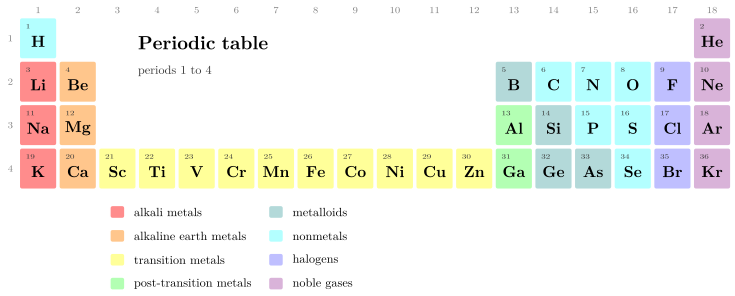 The periodic table, by family | 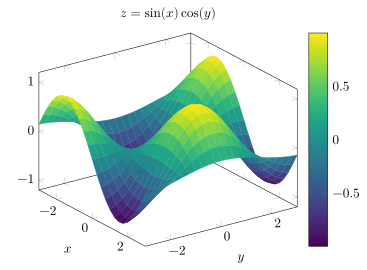 A pgfplots surface and its colorbar |
Paths, nodes and every shape library, matrices, trees, graphs, mind maps, automata, circuits, arrow tips, shadings, fadings, patterns, decorations, pgfplots in 2D and 3D (polar, ternary, Smith charts, fill between, colormaps) and data visualization. What tikra does not understand becomes a warning, never a failure: the full subset is in spec/subset.md.
Also for JavaScript, Rust and the terminal
The same core is an npm package (@mathlabs/tikra), a Rust crate and a command-line tool: github.com/matheusmota-dev-br/tikra.
License
The code is MIT or Apache-2.0; the fonts embedded through mathra are Latin Modern Math, under the GUST Font License, and STIX Two Math, under the SIL Open Font License 1.1.
1 maintainer

Metadata
1 maintainer
Release files for tikra 1.2.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| tikra-1.2.0.tar.gz | 675.8 kB | With provenance | Details |
Built distributions (wheels)
| File | Reset | |||
|---|---|---|---|---|
| tikra-1.2.0-cp39-abi3-win_amd64.whl | CPython 3.9 | abi3 | Windows x86-64 | Details |
| tikra-1.2.0-cp39-abi3-manylinux_2_17_x86_64.manylinux2014_x86_64.whl | CPython 3.9 | abi3 | Linux glibc 2.17+ x86-64 | Details |
| tikra-1.2.0-cp39-abi3-manylinux_2_17_aarch64.manylinux2014_aarch64.whl | CPython 3.9 | abi3 | Linux glibc 2.17+ ARM64 | Details |
| tikra-1.2.0-cp39-abi3-macosx_11_0_arm64.whl | CPython 3.9 | abi3 | macOS 11.0+ ARM64 | Details |
| tikra-1.2.0-cp39-abi3-macosx_10_12_x86_64.whl | CPython 3.9 | abi3 | macOS 10.12+ x86-64 | Details |
Total release size: 25.1 MB
Release files / tikra-1.2.0.tar.gz
| Download URL | tikra-1.2.0.tar.gz |
|---|---|
| Size | 675.8 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
d0139286bdc0bab761f18f9312fe4cf9e3a3e32464e64cf81ee8f52d68263659
|
|
BLAKE2b-256 checksum How to use checksums |
c2489488142026a6c2e9e69260f074b9ae560f355b8ae2eaff6d7f17d2674a79
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 24, 2026.
Transparency logRelease files / tikra-1.2.0-cp39-abi3-win_amd64.whl
| Download URL | tikra-1.2.0-cp39-abi3-win_amd64.whl |
|---|---|
| Size | 5.0 MB |
| Tags | CPython 3.9 Windows x86-64 abi3 |
|
SHA-256 checksum How to use checksums |
2b448932d3197ee066d1e6d729ff14216d95b01c6ad945c755a50a487d45df8e
|
|
BLAKE2b-256 checksum How to use checksums |
15228aa25b2102c7ea1a88b0bf86237ef5a79d8de1e6361690ff50cd4f57462a
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 24, 2026.
Transparency logRelease files / tikra-1.2.0-cp39-abi3-manylinux_2_17_x86_64.manylinux2014_x86_64.whl
| Download URL | tikra-1.2.0-cp39-abi3-manylinux_2_17_x86_64.manylinux2014_x86_64.whl |
|---|---|
| Size | 5.0 MB |
| Tags | CPython 3.9 Linux glibc 2.17+ x86-64 abi3 |
|
SHA-256 checksum How to use checksums |
4f5ef8b38452ae12b2494204aca64470f94dc8a871b4fbf297991efa14a749b9
|
|
BLAKE2b-256 checksum How to use checksums |
2708bad5d6be62fe4804483402acfdc663ec883c64bc243e98ede22fb1877ab4
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 24, 2026.
Transparency logRelease files / tikra-1.2.0-cp39-abi3-manylinux_2_17_aarch64.manylinux2014_aarch64.whl
| Download URL | tikra-1.2.0-cp39-abi3-manylinux_2_17_aarch64.manylinux2014_aarch64.whl |
|---|---|
| Size | 4.9 MB |
| Tags | CPython 3.9 Linux glibc 2.17+ ARM64 abi3 |
|
SHA-256 checksum How to use checksums |
c13bcdf86b129fbe3ed3ee6f03dbe55f76c92296c75412d8a2d188a9a68af12b
|
|
BLAKE2b-256 checksum How to use checksums |
1253d5ee25a4d7017e66d838b3a37e0b511dc646ac67a52178a389bf7dcea9ea
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 24, 2026.
Transparency logRelease files / tikra-1.2.0-cp39-abi3-macosx_11_0_arm64.whl
| Download URL | tikra-1.2.0-cp39-abi3-macosx_11_0_arm64.whl |
|---|---|
| Size | 4.7 MB |
| Tags | CPython 3.9 abi3 macOS 11.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
ae6180d9a43e790dd322d64c80bfdde9e1a6188ab78bb452e0bf444f2f449626
|
|
BLAKE2b-256 checksum How to use checksums |
66d14784ae4f42a9079ef771558574e8c545296231bae844be4657c3be94d8e4
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 24, 2026.
Transparency logRelease files / tikra-1.2.0-cp39-abi3-macosx_10_12_x86_64.whl
| Download URL | tikra-1.2.0-cp39-abi3-macosx_10_12_x86_64.whl |
|---|---|
| Size | 4.9 MB |
| Tags | CPython 3.9 abi3 macOS 10.12+ x86-64 |
|
SHA-256 checksum How to use checksums |
f39b3dd8351791b156dc24d54f67425ce8e9b7d6b9c8456aabd096e12b8da005
|
|
BLAKE2b-256 checksum How to use checksums |
12b0d655297beabeb857c7f67bfe26a90f5c28feaefce859fa21574ed9e97eb7
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 24, 2026.
Transparency logSecurity for tikra 1.2.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 6 files in this release have been uploaded with provenance metadata.
Attestation for tikra-1.2.0.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 24, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














