
torquests
Tor in your Python process, with the requests API you already know.


torquests speaks the Tor protocol itself. No Tor daemon, no Stem, no C extension past the
crypto libraries. You pip install it and your program gets its own Tor client, so a call
returns a real requests.Response that happened to travel through three relays.
import torquests

r = torquests.get("https://check.torproject.org/api/ip")
print(r.json())        # {"IsTor": true, "IP": "185.220.101.4"}
One line built a circuit, ran an ntor handshake at each hop, and carried your HTTP over it.
Why torquests
- v3 onion services. Fetch a
.onionthe way you fetch anything else: blinded-key derivation, the HSDir hash ring, two-layer descriptor decryption, and the rendezvous handshake. - The same requests API. Module verbs, a
Session, realrequests.Responseobjects, cookies, redirects, streaming, and an exception tree that subclasses the matchingrequestserrors. Mount Tor as a transport and keep the code you have. - No daemon. The whole client lives in your process. Nothing to install alongside it, start, or leave listening on a port.
- A proxy and a CLI in the box. Point a browser at the built-in SOCKS5 proxy, or fetch
from a shell with
torquests get.
Install
Python 3.10+:
pip install torquests
For the TLS-fingerprint stealth mode, add the extra:
pip install "torquests[stealth]"
Quickstart
The module verbs mirror requests. The first call bootstraps a verified consensus of the
Tor network and reuses it for the rest of the process:
import torquests

r = torquests.get("https://httpbin.org/get", timeout=30)
torquests.post("https://httpbin.org/post", json={"hello": "tor"})
A Session keeps circuits and cookies across requests and adds a Tor control:
with torquests.Session() as s:
    s.get("https://example.com")
    s.new_identity()          # fresh circuits, a new exit, and a cleared cookie jar
Runnable scripts for the common flows live in examples/.
Onion services
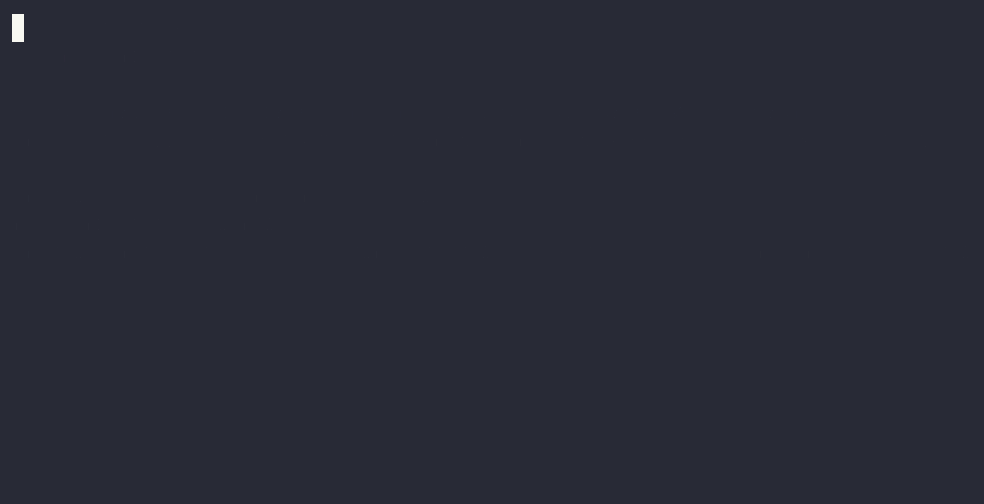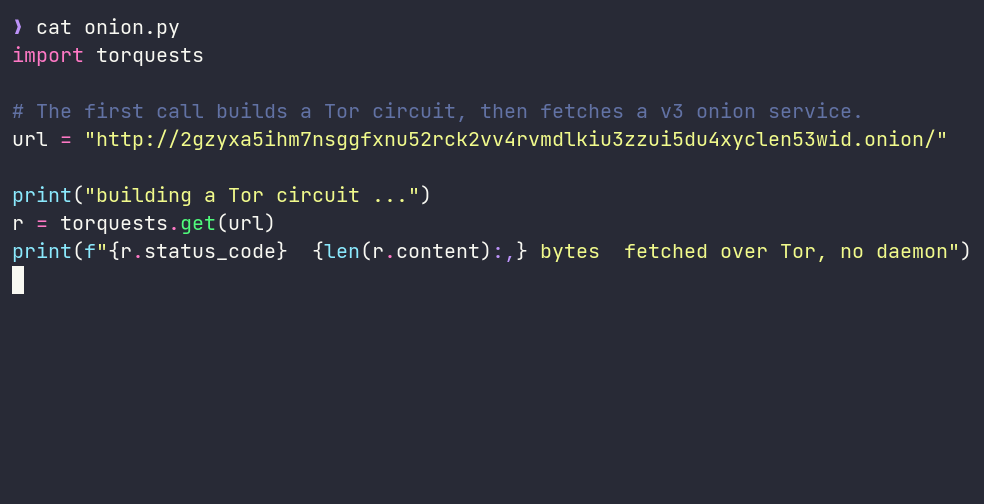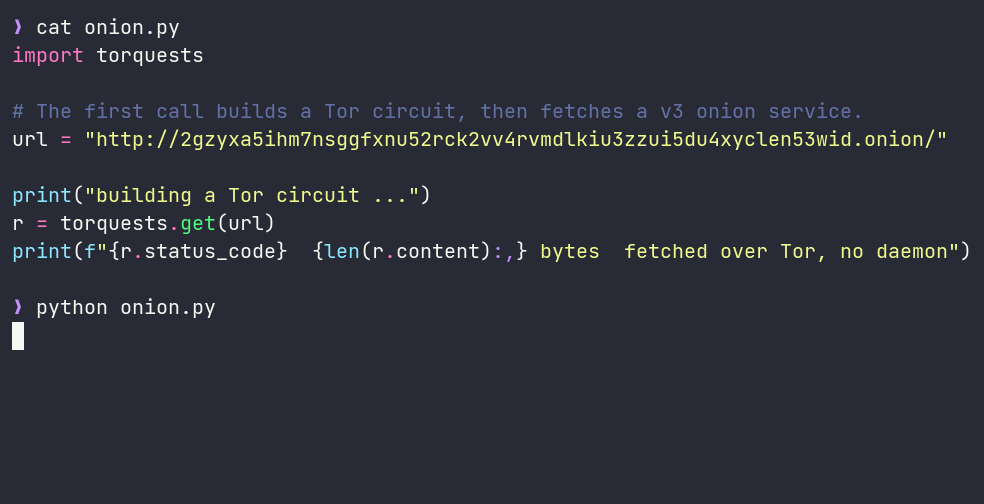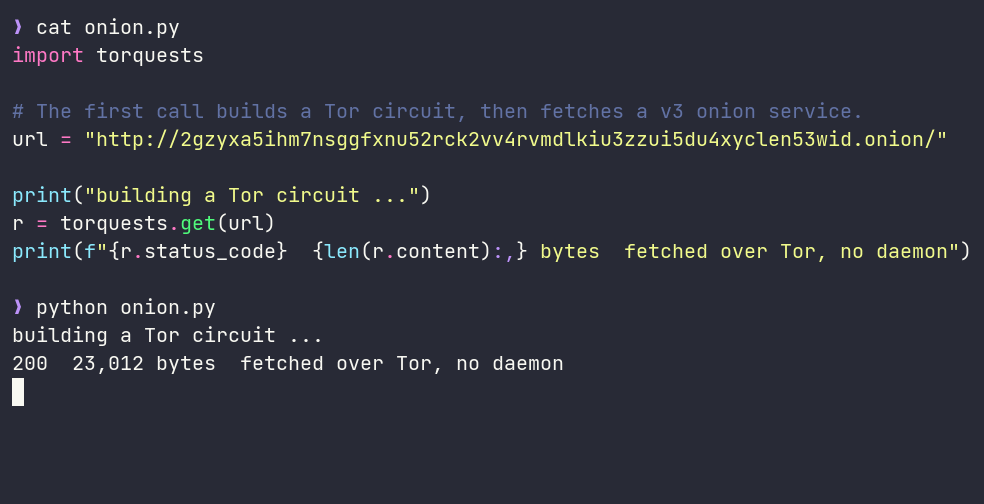
A .onion host routes over the rendezvous protocol. Same call, different address:
url = "http://2gzyxa5ihm7nsggfxnu52rck2vv4rvmdlkiu3zzui5du4xyclen53wid.onion/"
r = torquests.get(url)
print(r.status_code)          # 200, fetched over an onion circuit
Drop-in alias
torquests re-exports the requests names you reach for, so a lot of code ports by changing
one import:
import torquests as requests

r = requests.get("https://check.torproject.org/api/ip")
if r.status_code == requests.codes.ok:
    print(r.json())
Response, Request, PreparedRequest, codes, and the exception aliases (HTTPError,
ConnectionError, Timeout, and the rest) all come along.
More
The documentation covers the rest:
- Circuit isolation. One circuit, and exit, per destination host by default; switch to per-session or per-request.
- Stealth mode. A real browser TLS and
HTTP/2 fingerprint over Tor, through the
torquests[stealth]extra. - Command line.
torquests get,torquests ip, andtorquests socksfrom any shell. - SOCKS5 proxy. Send any program's traffic over Tor, with names resolved remotely, never on your machine.
- Mixed routing.
MixedSessionsends.onionover Tor and lets clearnet go out directly. - Consensus caching.
Point
TorConfig(cache_dir=...)at a directory to reuse a verified consensus across processes and skip the bootstrap's consensus fetch on a warm start.
Safety
By default torquests blends in: a Firefox-shaped header set with no tool-identifying
User-Agent, a stable entry guard, a circuit per destination host, cookies cleared on
new_identity(), clearnet names resolved at the exit, and .onion addresses reached over
rendezvous rather than resolved at an exit.
It cannot match Tor Browser's TLS ClientHello (JA3/JA4) on the wire, though. The standard-library stack emits a Python-shaped handshake that a destination or a hostile exit can fingerprint. To blend the TLS layer too, use stealth mode or Tor Browser. See Safety and SECURITY.md.
Credits
torquests is a modern successor to torpy, whose ntor and relay-cell cryptography it ports and modernizes. It is not affiliated with The Tor Project. See NOTICE.
1 maintainer

Release files for torquests 1.0.1
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | |
|---|---|---|---|
| torquests-1.0.1.tar.gz | 176.8 kB | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| torquests-1.0.1-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 306.1 kB
Release files / torquests-1.0.1.tar.gz
| Download URL | torquests-1.0.1.tar.gz |
|---|---|
| Size | 176.8 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
5362a815efb7dcfc2d21bb7f4aa5422ebde1e8d215e4631099c85310f9d087b7
|
|
BLAKE2b-256 checksum How to use checksums |
967ddbc907e452821bbb8946032160334b6c151610d667796d77bcd70191c072
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jul 19, 2026.
Transparency logRelease files / torquests-1.0.1-py3-none-any.whl
| Download URL | torquests-1.0.1-py3-none-any.whl |
|---|---|
| Size | 129.2 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
df9ef77986ddf7757ac30f3cc61bdf6fabdcb0fdb76c3b51fe288ef6bdae1d2c
|
|
BLAKE2b-256 checksum How to use checksums |
07cd9cb106a034835bb9062c9df687da3d5ede94a7f1a14af955e6cf6624c119
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jul 19, 2026.
Transparency log













