




Quick start · How it works · Safety filter · Real-world test · Survey
Your AI app's monitoring data (OpenTelemetry traces and logs) records prompts, tool calls and errors, and sends them to a dashboard. Secrets ride along: an API key in an error message, a password a user pasted into the chat, a token in a URL. Redaction code passes its unit tests while the key still leaks through a field nobody thought about.
TraceLeakCheck plants a fake secret, captures everything your app really exports, and tells you in plain English exactly where it leaked.
What you get
| 🔎 Find | pytest --traceleak checks every test that uses the canary fixture: traces, logs and metrics, over HTTP or gRPC, raw or encoded (base64 at any offset, URL, hex, truncated). |
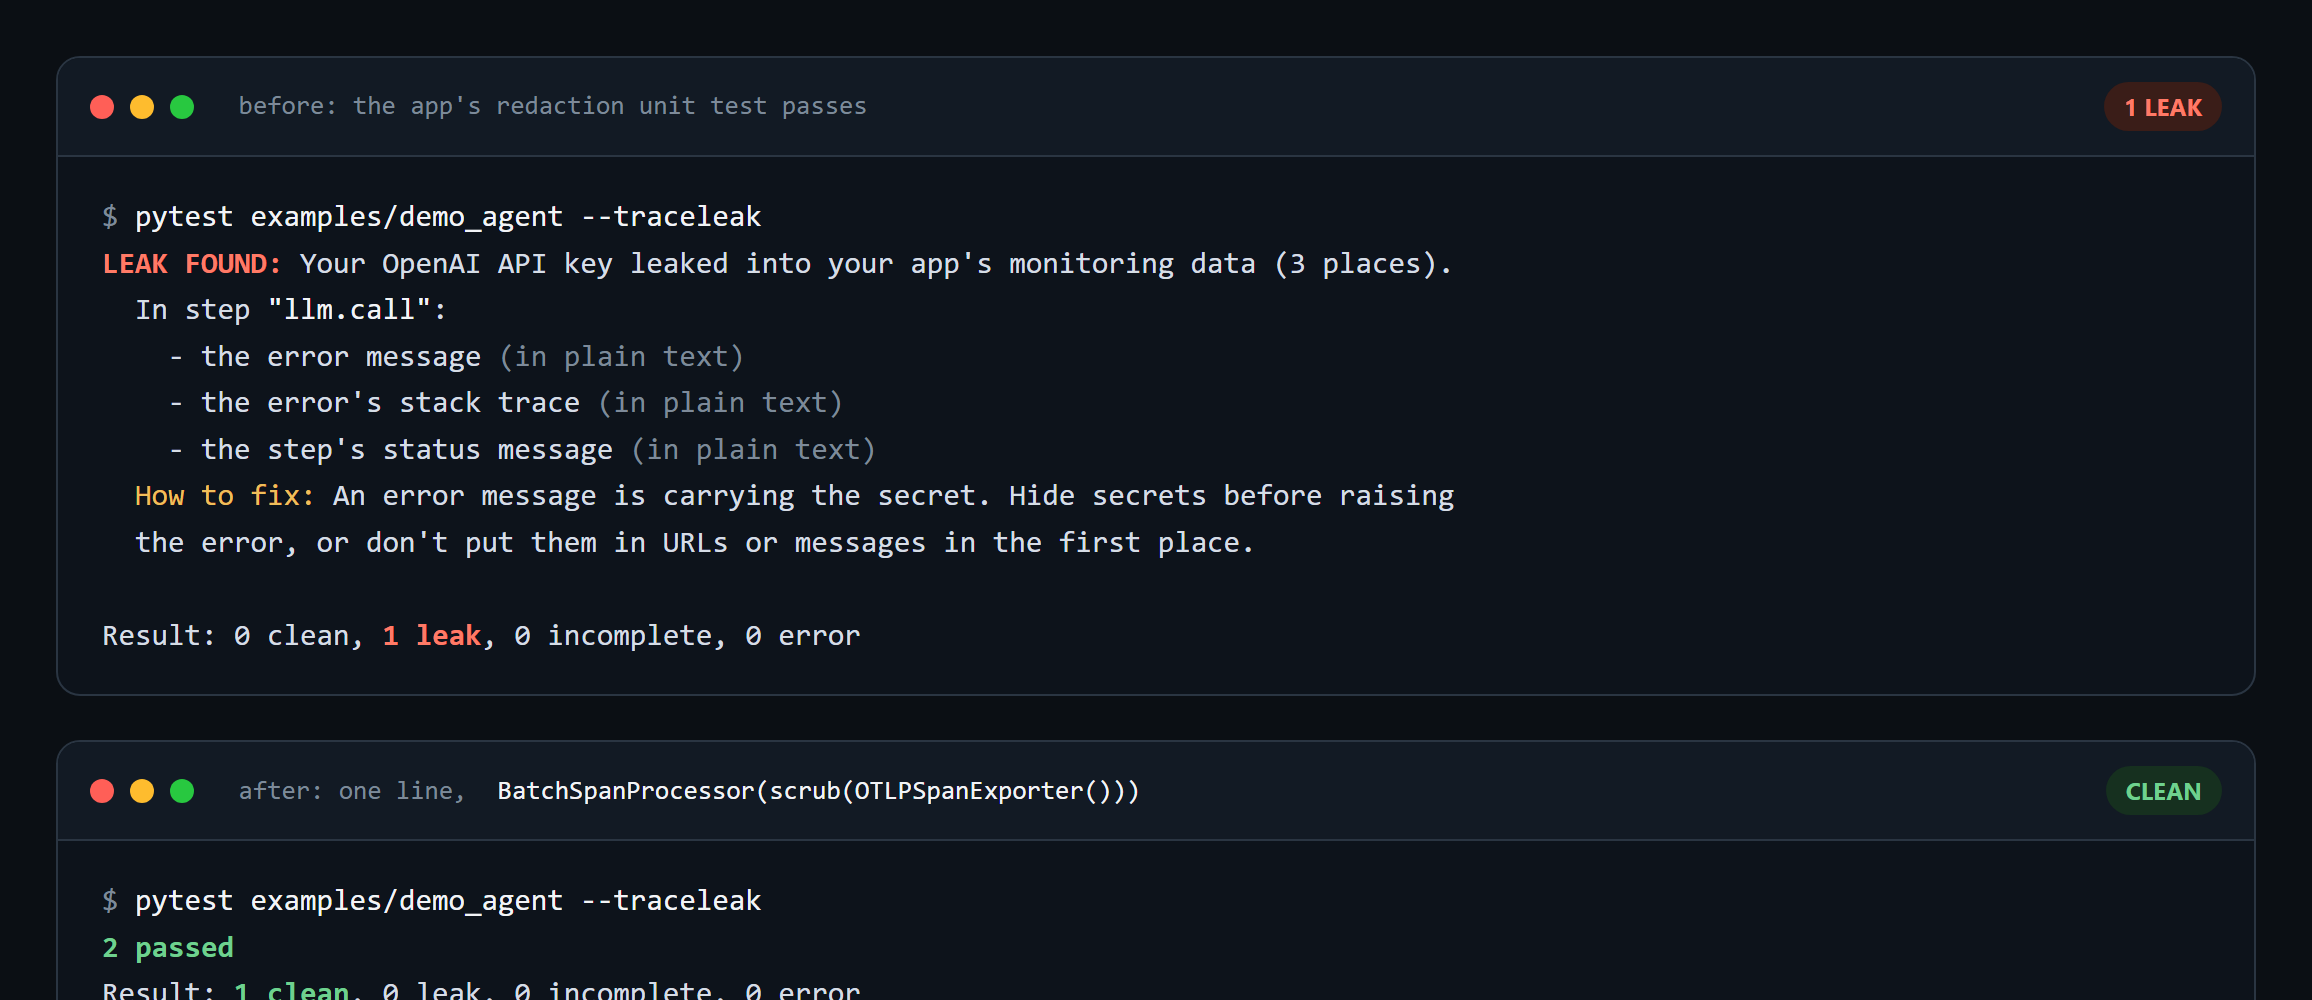
| 🛠️ Fix | scrub() wraps your exporter and removes secrets before anything leaves your app. Every report comes with how-to-fix tips. |
| ✅ Prove | Re-run and get clean, backed by a control check showing your telemetry really arrived. "Nothing arrived" is never "nothing leaked". |
Quick start
pip install traceleakcheck
def test_agent_does_not_leak_key(canary):
    key = canary("openai").value          # a fresh fake secret; this test is now checked
    run_agent("summarize this", api_key=key)
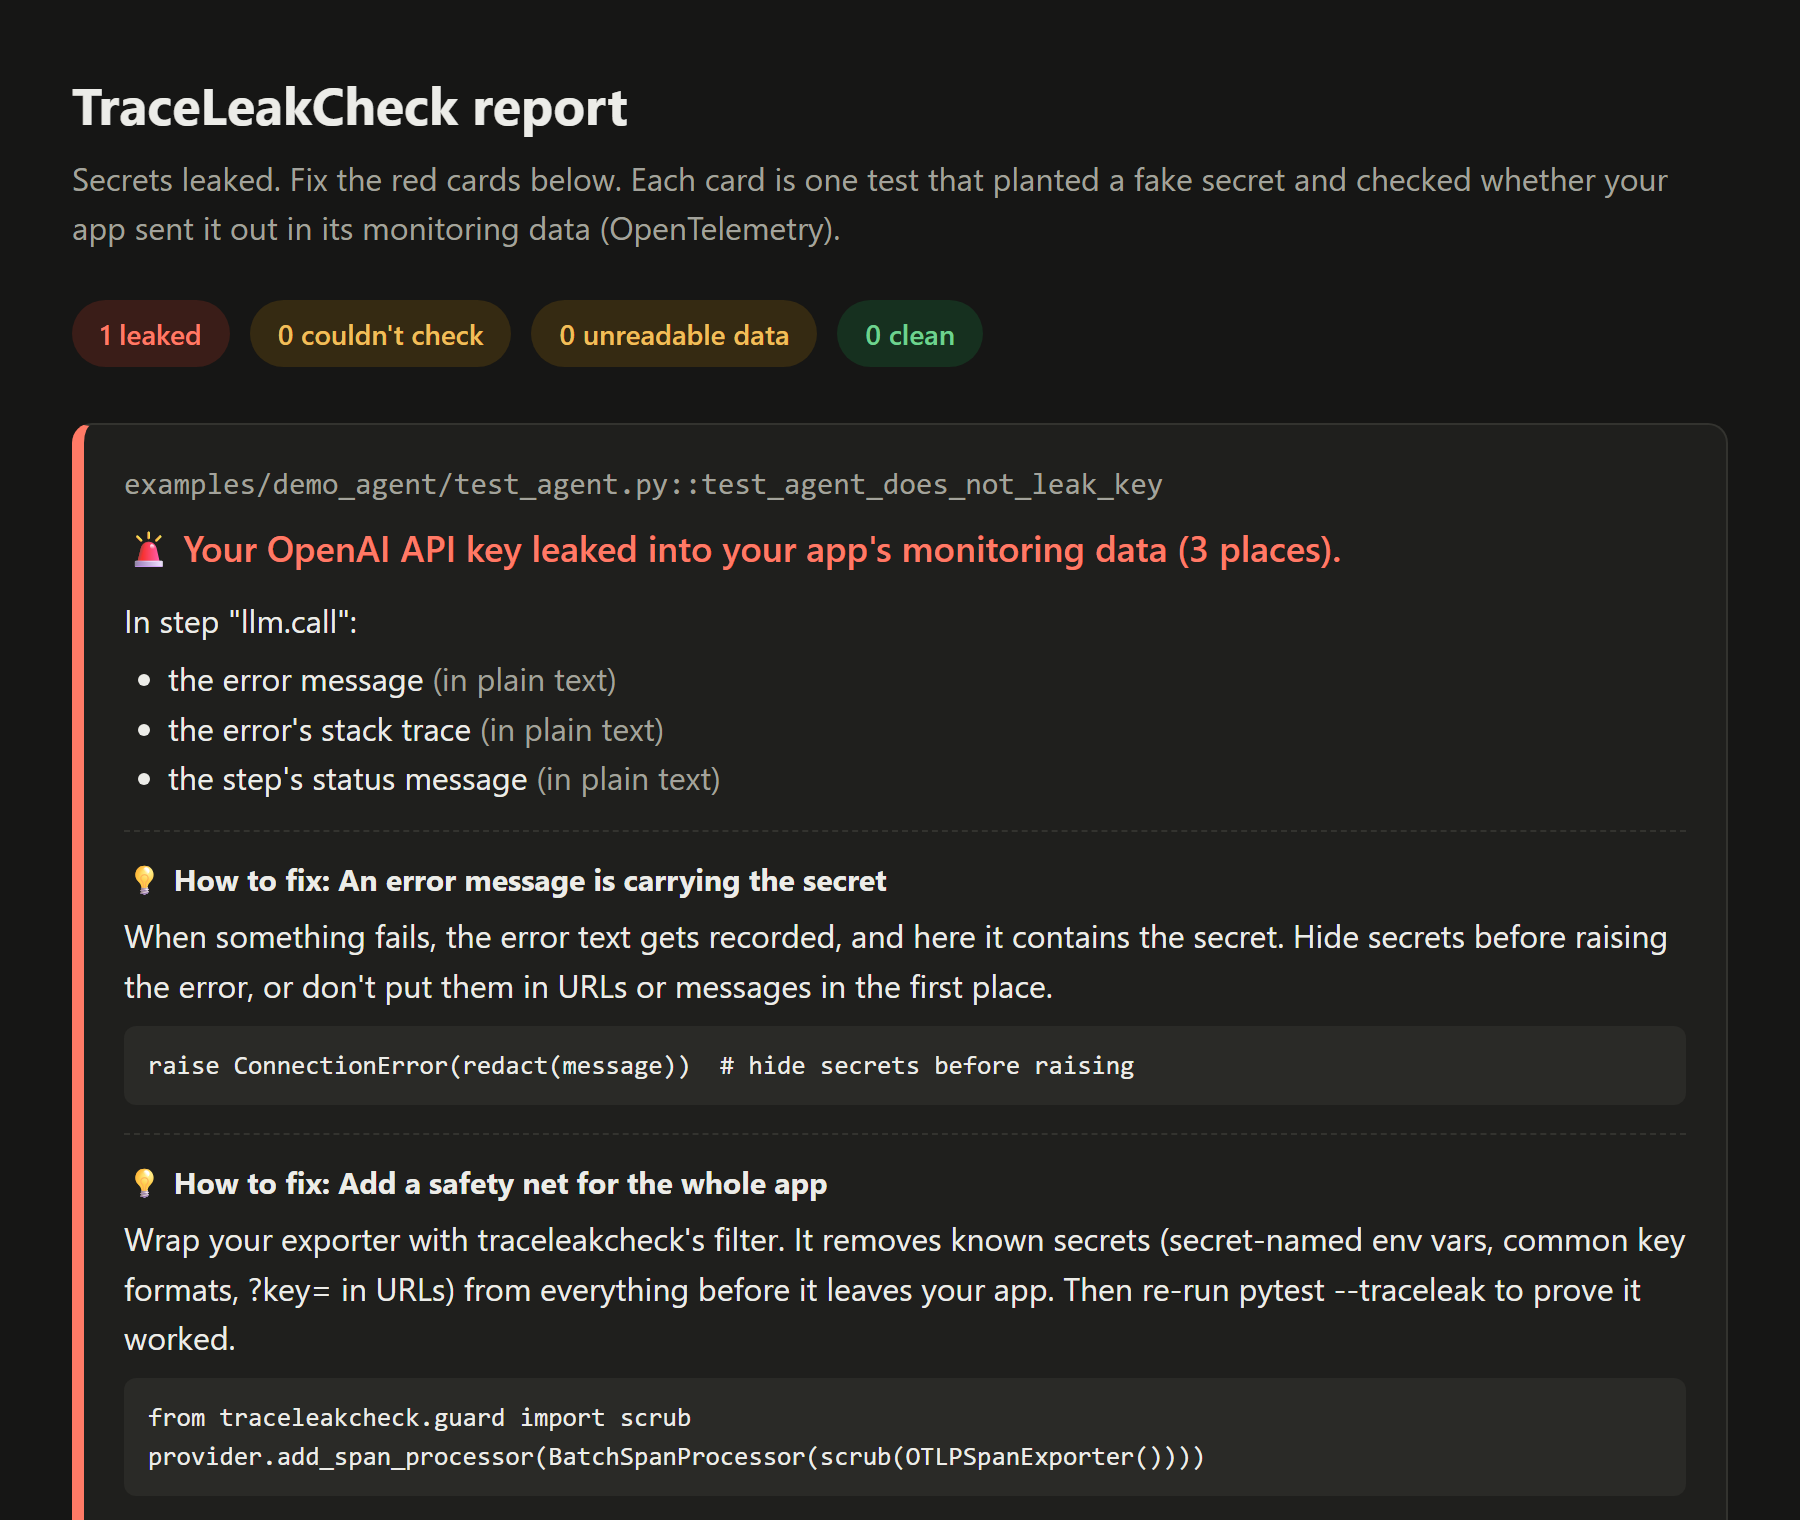
pytest --traceleak                                 # plain-English results in the terminal
pytest --traceleak --traceleak-html=report.html    # + a report page for your browser
pytest --traceleak -v                              # + exact technical field paths
If your app configures OpenTelemetry from the standard OTEL_EXPORTER_OTLP_* settings, it needs no changes. Traceloop's TRACELOOP_BASE_URL is set too. If your app builds a provider by hand, register it with traceleak.watch(provider).
The HTML report
How it works
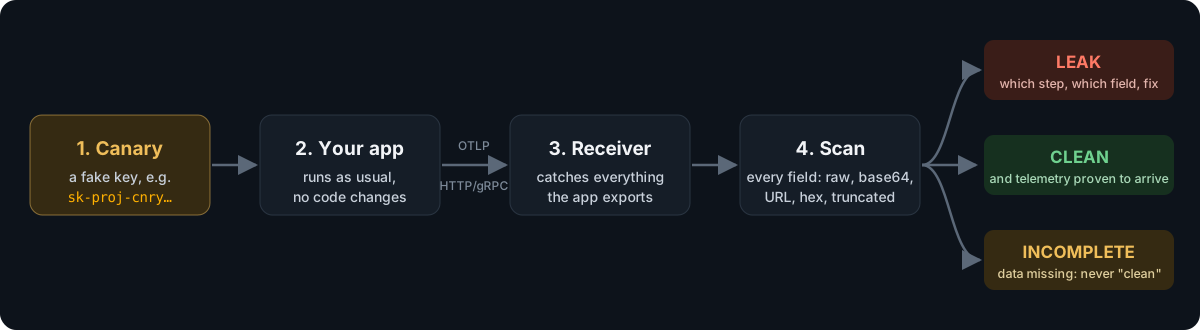
- Before your
conftest.pyloads,--traceleakstarts a receiver and points the app's exporters at it. - Each test that asks for a
canarygets unique fake secrets in realistic formats: OpenAI, Anthropic, AWS, GitHub, JWT or password. - After the test and its fixtures finish, a control marker is sent through every configured pipeline (traces, logs, metrics), everything is flushed, and every exported field is searched.
Each test gets one verdict:
| Verdict | Meaning | Test |
|---|---|---|
✅ clean |
Every pipeline delivered its control marker, and no canary was found | passes |
🚨 leak |
A canary was found; the report names the step and field | fails |
⚠️ incomplete |
A pipeline's control marker never arrived, or a span was still open at the end of the test (open spans are never exported), so "clean" can't be claimed | fails |
⚠️ error |
An export couldn't be decoded, so a scan would under-report | fails |
pytest shows a failed check as ERROR at teardown, because it runs after the fixtures finish. It works with pytest -n (xdist). In GitHub Actions the verdicts also go to the job summary, and there's a ready-made action.
Fix it: the safety filter
from traceleakcheck.guard import scrub

tracer_provider.add_span_processor(BatchSpanProcessor(scrub(OTLPSpanExporter())))
logger_provider.add_log_record_processor(BatchLogRecordProcessor(scrub(OTLPLogExporter())))
Before anything is exported, the filter removes:
- Known secrets: the values of environment variables named like
*KEY*,*TOKEN*,*SECRET*or*PASSWORD*, plus anything registered withadd_secret(). Their base64, URL and hex forms are removed too. - Well-known key formats: OpenAI, Anthropic, AWS, GitHub, Google, Slack, JWT and Bearer tokens, and credential query parameters such as
?key=.
It covers span names, attributes, exception events, status messages, log bodies and log attributes.
A filter can't recognize a secret that matches none of these rules, such as an unusual password a user types. That's why the two go together: the filter is the fix, and pytest --traceleak is the proof.
Tested on real code
We pointed TraceLeakCheck at the OpenTelemetry Demo's AI shop assistant (LangGraph + Traceloop), unmodified, talking to a fake LLM:
| Scenario | Without the filter | With scrub() |
|---|---|---|
| A shopper pastes a key into the chat | 🚨 leaked in 9 places | ✅ clean |
| The service's own API key | ✅ clean | ✅ clean |
| The LLM gateway rejects the key and echoes it | 🚨 leaked in 15 places | ✅ clean |
One secret becomes many copies, because every layer of an agent (chat step, agent step, workflow) records its own copy. The run also surfaced a real integration bug in TraceLeakCheck: the Traceloop SDK ignores OTEL_EXPORTER_OTLP_*. That's now fixed.
Survey: do GenAI instrumentations leak secrets?
survey/FINDINGS.md runs the OpenAI SDK under OTel openai-v2, OpenLLMetry, OpenInference, Logfire and httpx instrumentation, across 6 leak scenarios:
- No content opt-out we tested stops a secret in an error message. That includes
TRACELOOP_TRACE_CONTENT=false,OPENINFERENCE_HIDE_*andNO_CONTENT. ?key=query auth is exported verbatim inhttp.url.- Logfire's default scrubbing skips LLM messages and exception messages, even when they contain "API key".
- OTel openai-v2's documented legacy
CAPTURE_MESSAGE_CONTENT=truefalls back toNO_CONTENTon util-genai 1.x, with only a log warning. - Streamed replies are reassembled, so a secret split across chunks still leaks. But OTel openai-v2 never ends the span of an abandoned stream, so its contents are never exported. traceleakcheck now reports that as
incompleteinstead of a falseclean.
Limits
- Python and pytest only for now.
- Sampling is forced on with
OTEL_TRACES_SAMPLER=always_on. An app that passes an explicit sampler in code can still drop the span that leaks. - Telemetry that isn't OTLP, such as metrics read by a Prometheus reader, can't be checked. Skip it with
--traceleak-ignore=metrics.
Compared to Weir
Weir uses the same canary idea, and it covers more ground: it runs agent flows against a fake model and checks console output and network requests as well as telemetry. TraceLeakCheck focuses on the OTLP export boundary, needs no fake model, and ships a fix (scrub()) alongside the check.
Weir's README says it "finds whole values only, not hashed, split or truncated ones". TraceLeakCheck catches truncated secrets. It also has tests for base64 at any byte offset, secrets used as attribute keys, protobuf fields the decoder drops, and mixed-case hex. As of 2026-11-01, Weir's README doesn't say either way whether it handles these.
Library API
from traceleakcheck import OTLPReceiver, make_canary, scan

with OTLPReceiver() as rx:
    canary = make_canary("openai")
    # point your OTLP exporter at rx.endpoint, run your app with canary.value as the API key...
    findings = scan(rx.snapshot(), [canary])
Develop
uv sync
uv run pytest
1 maintainer

Metadata
1 maintainer
Release files for traceleakcheck 0.1.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| traceleakcheck-0.1.0.tar.gz | 438.7 kB | With provenance | Details for traceleakcheck-0.1.0.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| traceleakcheck-0.1.0-py3-none-any.whl | Python 3 | none | any | Details for traceleakcheck-0.1.0-py3-none-any.whl |
Total release size: 469.7 kB
Release files / traceleakcheck-0.1.0.tar.gz
| Download URL | traceleakcheck-0.1.0.tar.gz |
|---|---|
| Size | 438.7 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
ec7159c77039ac3b9366c184af3e664a175e3667c9d79788febce1f1f7d12aa0
|
|
BLAKE2b-256 checksum How to use checksums |
1ceea753c51bcd72adf0489bcc8f1cb01caa042cc63149631b9fcf92606053b0
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 2, 2026.
Transparency logRelease files / traceleakcheck-0.1.0-py3-none-any.whl
| Download URL | traceleakcheck-0.1.0-py3-none-any.whl |
|---|---|
| Size | 31.0 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
4a2527dcd962e31cb79c4e7bd6ae516dd7fa64c8ad292c9ad24dcab819ef8c31
|
|
BLAKE2b-256 checksum How to use checksums |
06a2908cc62b165f17d763e984f04b10b51b7b02830ab649877afdf09a453280
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 2, 2026.
Transparency logSecurity for traceleakcheck 0.1.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
Both files in this release have been uploaded with provenance metadata.
Attestation for traceleakcheck-0.1.0.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 2, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














