
troml 🥁
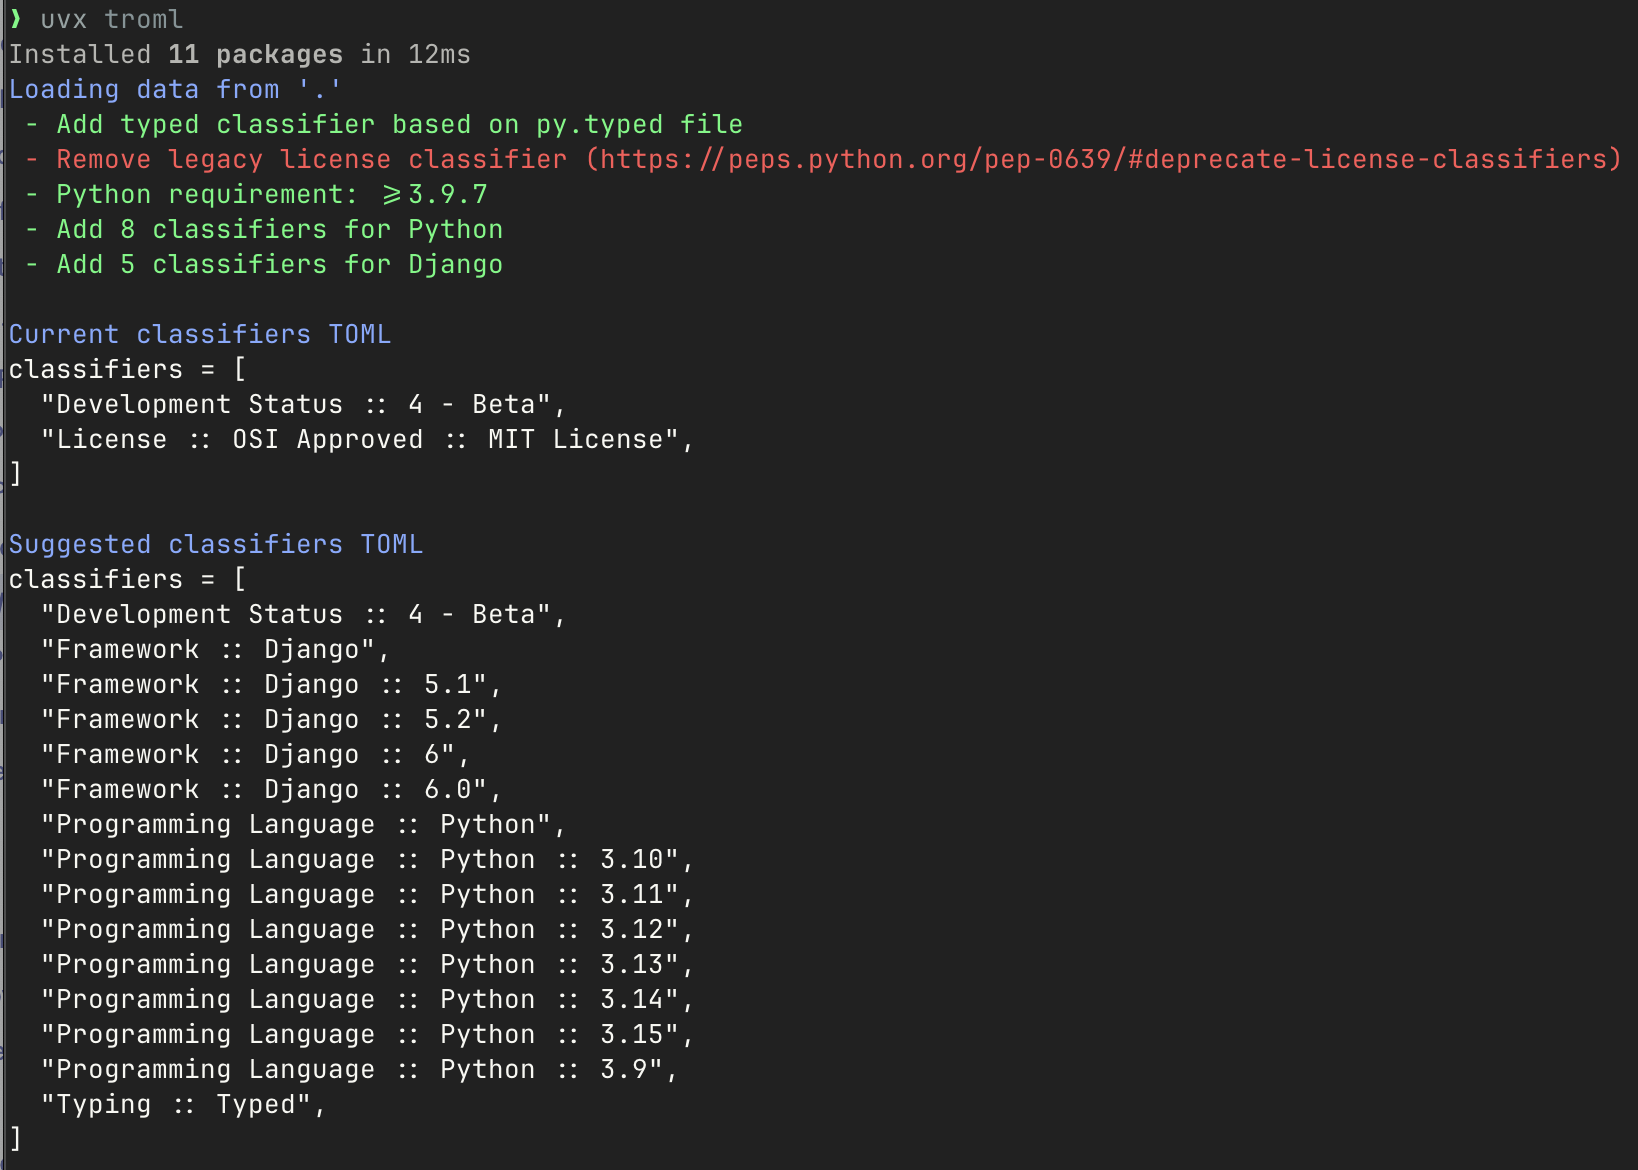
troml provides a list of potential classifiers that could be added to a Python package.
It supports modern Python packages that use the pyproject.toml standard (aka PEP 621 and PEP 639). troml also follows PEP 561 to determine whether a package should be considered typed or not.
Usage
uvx
uv is an extremely fast Python package and project manager, written in Rust. uvx is an alias for uv tool run ....
- Install
uv - Go to a directory with source code for a Python package
uvx troml
pipx
pipx is a way to run install and run Python applications in isolated environments.
- Install
pipx pipx install troml- Go to a directory with source code for a Python package
troml
pip --user
Install troml to the Python user install directory. More details in the pip docs.
pip install --user troml- Go to a directory with source code for a Python package
troml
CLI arguments
path
troml optionally accepts a path as the first argument. Defaults to . for the current directory.
uvx troml /path/to/pypyproject.toml
suggest
Provides an output of suggested classifiers. The default if no other command is used.
uvx troml suggest /path/to/pypyproject.toml
--fix
Automatically add classifiers in the pyproject.toml based on the suggestions. Will not remove existing classifiers.
uvx troml suggest --fix /path/to/pypyproject.toml
--no-multiline
Output the classifiers in a single-line. No-op if used without --fix.
uvx troml suggest --fix --multiline /path/to/pypyproject.toml
check
Exits with an error code if there are any suggested classifiers. Useful for pre-commit, CI/CD, etc.
uvx troml check /path/to/pypyproject.toml
Supported classifiers
Python version
troml will read project.python-requires and suggest classifiers based on it.
License (deprecated)
troml will suggest removing the legacy license classifiers.
Dependencies
troml will suggest classifiers based on the dependencies in project.dependencies, project.dependency-groups, and tool.uv.constraint-dependencies.
Typing
troml will suggest the "Typing :: Typed" classifier based on the existence of the py.typed file in the same directory as the pyproject.toml file.
FAQ
Does this add classifiers interactively?
Nope and it's not something I would add in. Take a look at https://codeberg.org/kfdm/add-classifiers or https://github.com/jvllmr/trove-setup if that's what you are looking for.
What's with the name?
- The classifiers for Python are called "Trove classifiers"
- Modern Python packages use TOML for configuration
"trove" 🤝 "TOML"
In a happy coincidence, "trommel" in Dutch means "drum".
Development
- Install
just: https://just.systems/man/en/packages.html just fetch
Run from source
uv run troml [PATH-TO-PYPROJECT-TOML]
Commands
- unit tests (via
pytest):just test - linting (via
ruff):just lint - type checking (via
mypy):just type - unit test coverage (via
coverage.py):just coverage - run 'em all:
just dev
Inspiration
- https://indieweb.social/@adamghill/115174743670090084
- another approach from @kfdm: https://codeberg.org/kfdm/add-classifiers
- post about
add-classifers: https://paultraylor.net/blog/2025/add-classifiers/ - https://github.com/jvllmr/trove-setup
- https://pypi.org/project/typer/ for creating the CLI
1 maintainer

Metadata
1 maintainer
Release files for troml 0.4.1
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| troml-0.4.1.tar.gz | 12.6 kB | With provenance | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| troml-0.4.1-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 26.2 kB
Release files / troml-0.4.1.tar.gz
| Download URL | troml-0.4.1.tar.gz |
|---|---|
| Size | 12.6 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
d71b6ea5dcc503bb31937b05f7a7752076d00052c2a0c963f33a2325d0dc0c4b
|
|
BLAKE2b-256 checksum How to use checksums |
89e381d7e78cd1508435f02baea95325342f8e997ee25bfa9104c3d49e64e5ae
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 14, 2025.
Transparency logRelease files / troml-0.4.1-py3-none-any.whl
| Download URL | troml-0.4.1-py3-none-any.whl |
|---|---|
| Size | 13.6 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
cac2bd3663f03af716c221e795500a9ca85eca6b4e27b816db10c89d04f35905
|
|
BLAKE2b-256 checksum How to use checksums |
843092d5e111c77a89df4267b359a1463e703d47b4e10dc7f33a4b49a2e3252b
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 14, 2025.
Transparency logSecurity for troml 0.4.1
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 2 files in this release have been uploaded with provenance metadata.
Attestation for troml-0.4.1.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 14, 2025.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.














