
ultravin


An extremely fast, fully offline NHTSA vPIC VIN decoder, written in Rust.
VINs decoded per second over a random corpus, single sequential caller — ultravin also batches across cores.
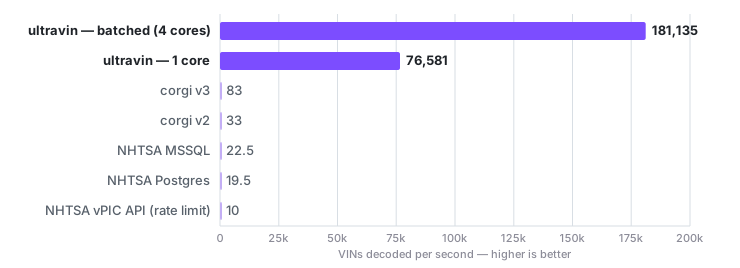
- ⚡️ ~76,600 VIN/s on one core — orders of magnitude faster than the NHTSA SQL procedures
- 🦀 Pure Rust core, shipped as a Python library and a Rust crate
- 📦 The entire vPIC vehicle database baked into the wheel
- 🔌 Fully offline — no network, no database, no data files at runtime
- 🎯 Byte-for-byte parity with vPIC's
spVinDecode, verified across every decodable VIN — except documented vPIC defects, which ultravin deliberately does not reproduce (the registry, evidence) - 🐍 Installable via
pip, with a CLI and a library API - 🧵 Batches in parallel to ~181,000 VIN/s on 4 cores
- 🗃️ Parquet in, parquet out — decodes a dataset of any size in the memory of one chunk
ultravin is a faithful port of NHTSA's spVinDecode — the SQL procedure behind
vPIC — reimplemented in Rust and verified against the reference Postgres
implementation. Because the vehicle database ships inside the binary, decoding
needs no network, no database server, and no data files. Install it and decode.
Getting Started
Installation
uv add ultravin
Prebuilt wheels require Python 3.10+ and nothing else — the data ships inside the wheel.
Usage
From Python:
import ultravin

r = ultravin.decode("1HGCM82633A004352")

r["model_year"]  # 2003
r["wmi"]  # '1HG'
r["check_digit_valid"]  # True
r["error_codes"]  # [0]

# `attributes` is the decoded vehicle, one entry per vPIC variable:
r["attributes"]["Make"]  # 'HONDA'
r["attributes"]["Model"]  # 'Accord'
decode(vin) returns a dict with keys vin, wmi, descriptor,
model_year, error_codes, check_digit_valid, corrected_vin, and
attributes — a single variable -> value mapping. Values are str, except the
free-text note fields listed in ultravin.MULTI_VALUED, which are always
list[str]: those are the only vPIC elements allowed to repeat within one
decode, and each row is a separate note rather than a competing value.
Decode many at once with decode_batch:
results = ultravin.decode_batch(["1HGCM82633A004352", "5YJ3E1EA7JF000000"])
If you already know a vehicle's model year, pass it — the same optional hint the
vPIC API calls modelyear. It matters for pre-2010 vehicles, where the VIN's
year character is ambiguous (A means 1980 or 2010): the hinted year gets its
own decode pass that competes against the VIN-derived one, and a hint that
contradicts the decoded year adds error code 12.
ultravin.decode("1HGCM82633A004352", year=1995)  # decodes as a 1995
ultravin.decode_batch(vins, years=[2011, None, 1987])  # one entry per VIN
Provenance: full=True
The default keeps the value and drops the provenance. If you need to know where
a value came from — source, over half of all rows being vehicle-type defaults
rather than something the VIN encodes — or the raw vPIC attribute_id, pass
full=True:
r = ultravin.decode("1HGCM82633A004352", full=True)

r["elements"][0]  # {'variable': 'Make', 'value': 'HONDA', 'source': 'Manu. Name', …}
full=True replaces attributes with elements, a list of per-attribute dicts
(group_name, variable, value, element_id, attribute_id, source,
pattern_id, …), and works the same on decode_batch, decode_json and
decode_batch_json. It is ~2× slower end to end: decoding is not the
expensive part, and elements costs ~615 dict entries per VIN against the
default's ~41.
ultravin.ELEMENTS maps each variable name to its static metadata
(element_id, group_name, data_type, …). Pin to element_id if you need a
key that survives NHTSA renaming a variable between data releases.
From the command line — every command emits JSON:
ultravin decode 1HGCM82633A004352             # JSON object
ultravin decode 1HGCM82633A004352 --year 1995 # with a caller model-year hint
ultravin decode 1HGCM82633A004352 --full      # with per-element provenance
ultravin decode-batch vins.txt                # one VIN per line -> JSON array
ultravin version
Rust
The engine is its own crate, ultravin:
cargo add ultravin, then
let r = ultravin::decode("1HGCM82633A004352", None);
assert_eq!(r.model_year, Some(2003));
The 83 MB vPIC database is too big for crates.io, so the first build fetches it from the matching GitHub release, verifies it, caches it per machine and bakes it into your binary — runtime stays fully offline. Offline builds and runtime loading: crates/ultravin/README.md.
Datasets
For bulk work there is decode_stream — a stream of decoded Arrow batches,
without a single row ever becoming a Python object:
import ultravin

rows = ultravin.decode_stream("registrations.parquet").to_parquet("decoded.parquet")

rows  # 4812004 — the rows written, not the rows themselves
The source is a parquet file, a directory of *.parquet read in sorted order, or
anything speaking the Arrow C data interface — so the same call takes a pandas
DataFrame (pandas ≥ 2.2, with pyarrow installed), a pyarrow Table, a polars
DataFrame, a duckdb result, or a RecordBatchReader. A DecodeStream is
itself an Arrow source, which is what lets it hand the decode straight to
whatever you already use:
import pandas as pd, polars as pl, pyarrow as pa, duckdb

df = pd.DataFrame({"vin": ["1HGCM82633A004352", "5YJ3E1EA7KF328931"]})

pl.DataFrame(ultravin.decode_stream(df))  # -> polars
pa.table(ultravin.decode_stream(df))  # -> pyarrow
ultravin.decode_stream(df).to_pandas()  # -> pandas (needs pandas + pyarrow)

stream = ultravin.decode_stream(df)  # duckdb resolves the name from scope
duckdb.sql("select Make, count(*) from stream group by 1")
Each stream is single-use — note the fresh decode_stream(...) on every line
above. It pulls from a source that has already moved on, so a second consumer
would get a silently truncated result; consuming one twice raises RuntimeError
rather than handing back a short answer. Call decode_stream again to re-read.
Picking columns
columns= takes vPIC variable names, element_ids, or both together; omit it for
every publicly decodable element:
ultravin.decode_stream("registrations.parquet", columns=["Make", "Model", 13])
Pin to element_id for anything long-lived. The id is the one key NHTSA does
not rename between monthly data releases.
Column naming and schema drift
Naming output columns after vPIC variables means a data refresh can silently
change your table's shape — NHTSA renames variables, and Displacement (L)
becoming something else takes every downstream query with it. column_names="id"
labels each projected column attr_<element_id> instead, which never moves:
ultravin.decode_stream(src, columns=[26, 13], column_names="id")
# -> vin, decoded_model_year, attr_26, attr_13
Passthrough columns (the source VIN column, the source year column, and
decoded_model_year) keep their own names in both modes; only the projection is
renamed. The default is "variable" — reach for "id" when the output feeds a
persisted schema rather than a human.
You never lose the other name. Every projected column carries both keys as Arrow field metadata, in both modes, and they survive the parquet round-trip:
table = pa.table(ultravin.decode_stream(src, columns=[26, 13], column_names="id"))
{f.name: dict(f.metadata) for f in table.schema if f.metadata}
# {'attr_26': {b'element_id': b'26', b'variable': b'Make'},
#  'attr_13': {b'element_id': b'13', b'variable': b'Displacement (L)'}}
Columns and layout
The VIN column is found by name (vin, case-insensitively) and then, for a
parquet source, by sniffing the leading rows — as is the optional caller-year
column (year, model_year, …); pass vin_column=/year_column= to name them
outright. Any text encoding works: Utf8, LargeUtf8, Utf8View, or the
dictionary a pandas categorical arrives as.
The output holds the VIN and caller year passed through, then
decoded_model_year (named so it cannot collide with an input column called
model_year), then one column per projected element — string, int64 or
float64 following vPIC's own data_type, with an empty value written as null.
Row order and row count always equal the input's: an undecodable VIN is a row of
nulls, never a raise and never a dropped row.
For a parquet source, rows stream through in batch_size-row chunks with the GIL
released, so peak memory is one chunk no matter how large the source is. For an
Arrow source the producer decides the input chunking, and batch_size only sets
the parquet row-group size of to_parquet. Reading and writing parquet is the
same Rust as the decoding, so the parquet path needs no pyarrow and no other
install; only the pyarrow/polars/pandas hand-offs need those libraries.
From the command line:
ultravin decode-parquet registrations.parquet decoded.parquet --columns Make,Model
ultravin decode-parquet parts/ decoded.parquet --columns 26,28 --vin-column chassis_no
ultravin decode-parquet registrations.parquet decoded.parquet --column-names id
Benchmarks
How many VINs each engine decodes per second. ultravin was measured on September 9, 2026, over a random corpus of 5,000 valid VINs on an Apple M1 Max: medians of three 60-second runs after warming the full corpus, with batches capped at four cores. The other engines retain their earlier comparison figures:
| engine | VIN/s | vs ultravin (1 core) |
|---|---|---|
| ultravin — batched, 4 cores | 181,135 | ~2.4× faster |
| ultravin — 1 core | 76,581 | 1× |
corgi v3 — @cardog/corgi (binary index) |
~83 | ~923× slower |
corgi v2 — @cardog/corgi 2.0.1 (SQLite) |
~33 | ~2,321× slower |
NHTSA MSSQL — spVinDecode (SQL Server) |
22.5 | ~3,404× slower |
NHTSA Postgres — spvindecode |
19.5 | ~3,927× slower |
| NHTSA vPIC web API — public rate limit | ~10 | ~7,658× slower |
ultravin runs in-process with the database embedded — no server, no round-trip.
These measure the Rust engine on a shared host. Python output construction
and parquet I/O have separate costs. The paired benchmark report
records a 1.67× single-core and 1.40× batch improvement over the previous release,
with startup and memory tradeoffs. The corgi figures are derived from its project's
published per-VIN latency (~12 ms v3 / ~30 ms v2, not re-measured here). The NHTSA
Postgres and MSSQL oracles run the unmodified spVinDecode over localhost;
MSSQL is SQL Server under amd64 emulation on Apple Silicon, so its number
understates native hardware — ultravin is still ~3,404× faster. The NHTSA vPIC web API row is its
published ~10 req/s rate limit, not
a decode time — a hard ceiling regardless of hardware. Methodology and
reproduction: docs/BENCHMARKS.md.
Documentation
- Vision — what this is, and what it deliberately is not
- Benchmarks — the numbers, the methodology, how to reproduce them
- Acceptance — the parity policy: what counts as passing, how a divergence is adjudicated
- Known deviations — the vPIC defects ultravin does not reproduce, with evidence
- Corpora —
generate,cover_vins,sweep: hitting every decode behaviour with the fewest VINs - Data refresh — how the monthly NHTSA dump is integrated behind parity gates
- Release — tags, wheels, the embedded artifact, crates.io
License
MIT. The embedded NHTSA vPIC data has its own provenance — see NOTICE.
1 maintainer

Metadata
1 maintainer
Release files for ultravin 2.2.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| ultravin-2.2.0.tar.gz | 21.2 MB | With provenance | Details |
Built distributions (wheels)
Total release size: 435.5 MB
Release files / ultravin-2.2.0.tar.gz
| Download URL | ultravin-2.2.0.tar.gz |
|---|---|
| Size | 21.2 MB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
3c33cdcfed98a57080acd789047181e4d9d2090c7c7fedce036a6985afa40637
|
|
BLAKE2b-256 checksum How to use checksums |
250149aab4110580d936763ea852bcdd124af497129fae9389ff5ede0b9597c2
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 9, 2026.
Transparency logRelease files / ultravin-2.2.0-cp310-abi3-win_arm64.whl
| Download URL | ultravin-2.2.0-cp310-abi3-win_arm64.whl |
|---|---|
| Size | 25.3 MB |
| Tags | CPython 3.10 Windows ARM64 abi3 |
|
SHA-256 checksum How to use checksums |
3f8bd6413c3db0c0c02ef03d460da010aa7939cf921f277091282d270740a05c
|
|
BLAKE2b-256 checksum How to use checksums |
98ce499e3c4320aac1ade2449567035b9aa0ef4d7f7b8a2a5cdbaca87554d52c
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 9, 2026.
Transparency logRelease files / ultravin-2.2.0-cp310-abi3-win_amd64.whl
| Download URL | ultravin-2.2.0-cp310-abi3-win_amd64.whl |
|---|---|
| Size | 25.8 MB |
| Tags | CPython 3.10 Windows x86-64 abi3 |
|
SHA-256 checksum How to use checksums |
774b599d82ca4c1a73d1f7ad60ba2364b58c7fc89feda70709629898a598f630
|
|
BLAKE2b-256 checksum How to use checksums |
a7bf28b627ba59955125c5942258e74aa038b2c4d4b99a5bfc3d335490341cd7
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 9, 2026.
Transparency logRelease files / ultravin-2.2.0-cp310-abi3-win32.whl
| Download URL | ultravin-2.2.0-cp310-abi3-win32.whl |
|---|---|
| Size | 25.3 MB |
| Tags | CPython 3.10 Windows x86-32 abi3 |
|
SHA-256 checksum How to use checksums |
ec8de738d435a94c9ee25d500fde6189d8bd6009400a7130e0e3ff7ef7ef0558
|
|
BLAKE2b-256 checksum How to use checksums |
3d299d48e16146b5af1f679c10fdce91effcb9e531d1652a4001aee5b3a5e27f
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 9, 2026.
Transparency logRelease files / ultravin-2.2.0-cp310-abi3-musllinux_1_2_x86_64.whl
| Download URL | ultravin-2.2.0-cp310-abi3-musllinux_1_2_x86_64.whl |
|---|---|
| Size | 26.0 MB |
| Tags | CPython 3.10 Linux musl 1.2+ x86-64 abi3 |
|
SHA-256 checksum How to use checksums |
ec169009fa0ef0bfe3ca182eeddd66c33f28615aa44485e84f1e0d2c6d8749d7
|
|
BLAKE2b-256 checksum How to use checksums |
5c6d670ed9941258941ae0792b48149b039f4464a6d2253c0d5f9564c2aaa77e
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 9, 2026.
Transparency logRelease files / ultravin-2.2.0-cp310-abi3-musllinux_1_2_i686.whl
| Download URL | ultravin-2.2.0-cp310-abi3-musllinux_1_2_i686.whl |
|---|---|
| Size | 26.0 MB |
| Tags | CPython 3.10 Linux musl 1.2+ x86-32 abi3 |
|
SHA-256 checksum How to use checksums |
d38b388ea3bf8fe1d07e3a2e14df8bac8e1244f02c116bf103a0524cdb991a44
|
|
BLAKE2b-256 checksum How to use checksums |
d02a5f628dfa84dded7cba5ae211af40d728a50145245e6e6819faa5752e39a3
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 9, 2026.
Transparency logRelease files / ultravin-2.2.0-cp310-abi3-musllinux_1_2_armv7l.whl
| Download URL | ultravin-2.2.0-cp310-abi3-musllinux_1_2_armv7l.whl |
|---|---|
| Size | 26.2 MB |
| Tags | CPython 3.10 Linux musl 1.2+ ARMv7l abi3 |
|
SHA-256 checksum How to use checksums |
0389da79a11f55dbd437bc4ca4bfca2f4c5de5b00224b6b5c6d548fb8e8b278f
|
|
BLAKE2b-256 checksum How to use checksums |
11791a3aab356727ceea79c4f1340c9f723091d4acf9398c1afcf7fff26bd10f
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 9, 2026.
Transparency logRelease files / ultravin-2.2.0-cp310-abi3-musllinux_1_2_aarch64.whl
| Download URL | ultravin-2.2.0-cp310-abi3-musllinux_1_2_aarch64.whl |
|---|---|
| Size | 25.7 MB |
| Tags | CPython 3.10 Linux musl 1.2+ ARM64 abi3 |
|
SHA-256 checksum How to use checksums |
18c11688915c6ea33dddb89c7085c59efcdb7d99f565130c78411effde173a51
|
|
BLAKE2b-256 checksum How to use checksums |
e96574c5c359e00187eab8d15a4d39646b9aa74db0a5f382023c3ee584801db0
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 9, 2026.
Transparency logRelease files / ultravin-2.2.0-cp310-abi3-manylinux_2_31_riscv64.whl
| Download URL | ultravin-2.2.0-cp310-abi3-manylinux_2_31_riscv64.whl |
|---|---|
| Size | 25.9 MB |
| Tags | CPython 3.10 Linux glibc 2.31+ RISC-V 64 abi3 |
|
SHA-256 checksum How to use checksums |
694b9a687b37a753690e391c3cf7f7a848b4509bae2e02bc17921378770a9c4e
|
|
BLAKE2b-256 checksum How to use checksums |
0bbf521df6de1ed72d614632fa45e4e8a648b1832bd7f65cfe01dd10c8a77c5f
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 9, 2026.
Transparency logRelease files / ultravin-2.2.0-cp310-abi3-manylinux_2_28_aarch64.whl
| Download URL | ultravin-2.2.0-cp310-abi3-manylinux_2_28_aarch64.whl |
|---|---|
| Size | 25.5 MB |
| Tags | CPython 3.10 Linux glibc 2.28+ ARM64 abi3 |
|
SHA-256 checksum How to use checksums |
0a0bf37f59971ede4363e858cf8951e6eb6156e7ae5f0861f104b836eb2b4513
|
|
BLAKE2b-256 checksum How to use checksums |
6f4d9486b582e13a1557c6f453426b131f15bc41b4df58ab6d995b2759272711
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 9, 2026.
Transparency logRelease files / ultravin-2.2.0-cp310-abi3-manylinux_2_17_x86_64.manylinux2014_x86_64.whl
| Download URL | ultravin-2.2.0-cp310-abi3-manylinux_2_17_x86_64.manylinux2014_x86_64.whl |
|---|---|
| Size | 25.8 MB |
| Tags | CPython 3.10 Linux glibc 2.17+ x86-64 abi3 |
|
SHA-256 checksum How to use checksums |
868886a8ee1c1d1951b856ba5ddda4414516689a8050e124736affff5ca2b45e
|
|
BLAKE2b-256 checksum How to use checksums |
06d43a8f1b86b3417abc4897676dbf0def857b449a42ddcd704f0ced6717c166
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 9, 2026.
Transparency logRelease files / ultravin-2.2.0-cp310-abi3-manylinux_2_17_s390x.manylinux2014_s390x.whl
| Download URL | ultravin-2.2.0-cp310-abi3-manylinux_2_17_s390x.manylinux2014_s390x.whl |
|---|---|
| Size | 26.3 MB |
| Tags | CPython 3.10 Linux glibc 2.17+ IBM System/390x abi3 |
|
SHA-256 checksum How to use checksums |
e64f9559b6982b162ddb58daf119f01718769da8f38ce382c831f615405714cd
|
|
BLAKE2b-256 checksum How to use checksums |
848506e113f09f760341fdc451f6db83892dcca1c06c57793f6875578b867831
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 9, 2026.
Transparency logRelease files / ultravin-2.2.0-cp310-abi3-manylinux_2_17_ppc64le.manylinux2014_ppc64le.whl
| Download URL | ultravin-2.2.0-cp310-abi3-manylinux_2_17_ppc64le.manylinux2014_ppc64le.whl |
|---|---|
| Size | 26.0 MB |
| Tags | CPython 3.10 Linux glibc 2.17+ PowerPC 64-le abi3 |
|
SHA-256 checksum How to use checksums |
1702808d1377335fe379b34824c83c2ec5c98b82b7742b8a90a5455de746b9b1
|
|
BLAKE2b-256 checksum How to use checksums |
5e8500269ff83f6c36de71e0eae636a5b966258a73cd77a4be27840668ae5e77
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 9, 2026.
Transparency logRelease files / ultravin-2.2.0-cp310-abi3-manylinux_2_17_i686.manylinux2014_i686.whl
| Download URL | ultravin-2.2.0-cp310-abi3-manylinux_2_17_i686.manylinux2014_i686.whl |
|---|---|
| Size | 27.1 MB |
| Tags | CPython 3.10 Linux glibc 2.17+ x86-32 abi3 |
|
SHA-256 checksum How to use checksums |
6aa9fd6826ddb617b836e01b52f33ed908304f5f32b8a01e2790a97963fef02e
|
|
BLAKE2b-256 checksum How to use checksums |
45bf8852d442279146e879067e01b84122d0a4e257304ca5f0bbf588d0c9e6a5
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 9, 2026.
Transparency logRelease files / ultravin-2.2.0-cp310-abi3-manylinux_2_17_armv7l.manylinux2014_armv7l.whl
| Download URL | ultravin-2.2.0-cp310-abi3-manylinux_2_17_armv7l.manylinux2014_armv7l.whl |
|---|---|
| Size | 26.0 MB |
| Tags | CPython 3.10 Linux glibc 2.17+ ARMv7l abi3 |
|
SHA-256 checksum How to use checksums |
32e28115f55b78975bad1f493eb91c62822018803769f22745c02c9b55fb9d05
|
|
BLAKE2b-256 checksum How to use checksums |
3021f92f4ed3012caf3f473229f6828fce42093c7914816bca6015ade67e6a50
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 9, 2026.
Transparency logRelease files / ultravin-2.2.0-cp310-abi3-macosx_11_0_arm64.whl
| Download URL | ultravin-2.2.0-cp310-abi3-macosx_11_0_arm64.whl |
|---|---|
| Size | 25.9 MB |
| Tags | CPython 3.10 abi3 macOS 11.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
7ff3c91555014dfd383eadf0d7513bac167ee87b9ba2ef06ed87fd6153ba7129
|
|
BLAKE2b-256 checksum How to use checksums |
079de5ba8431eac17a12c8586513f9e625879816f1bdb8da487f3a39185b9a2e
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 9, 2026.
Transparency logRelease files / ultravin-2.2.0-cp310-abi3-macosx_10_12_x86_64.whl
| Download URL | ultravin-2.2.0-cp310-abi3-macosx_10_12_x86_64.whl |
|---|---|
| Size | 25.6 MB |
| Tags | CPython 3.10 abi3 macOS 10.12+ x86-64 |
|
SHA-256 checksum How to use checksums |
19f901cc0ef1f92615502a3c054b400032fa4616f2dce4c700c826ba4efb8c4a
|
|
BLAKE2b-256 checksum How to use checksums |
1b408581e9b39062959a2336a43ceebe2e229199e0bd97be9131c122c7f666fc
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 9, 2026.
Transparency logSecurity for ultravin 2.2.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 17 files in this release have been uploaded with provenance metadata.
Attestation for ultravin-2.2.0.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 9, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.














