
$ vcspull · 

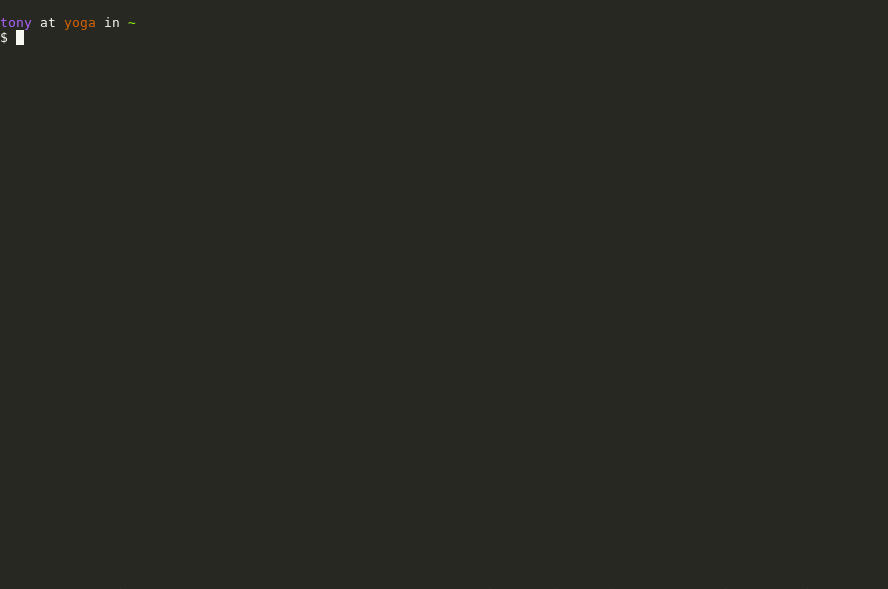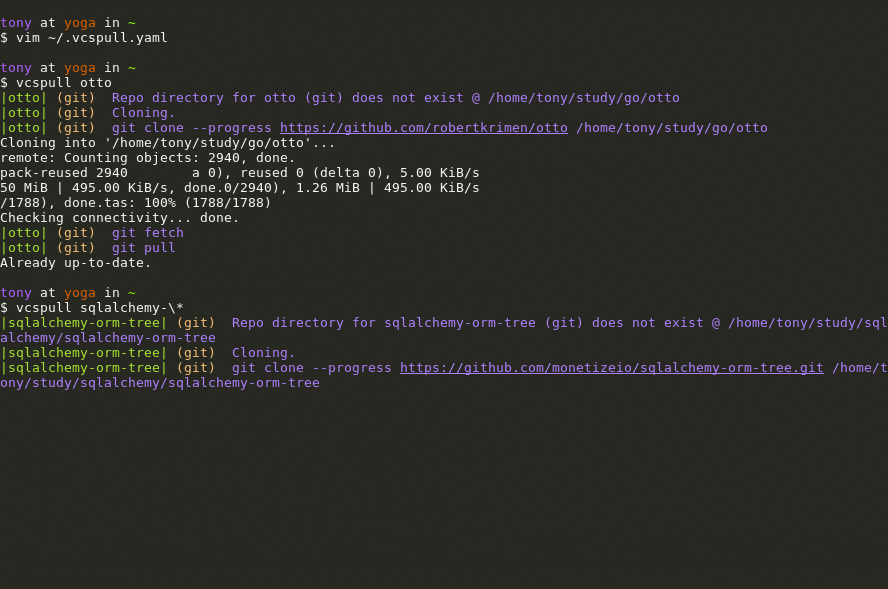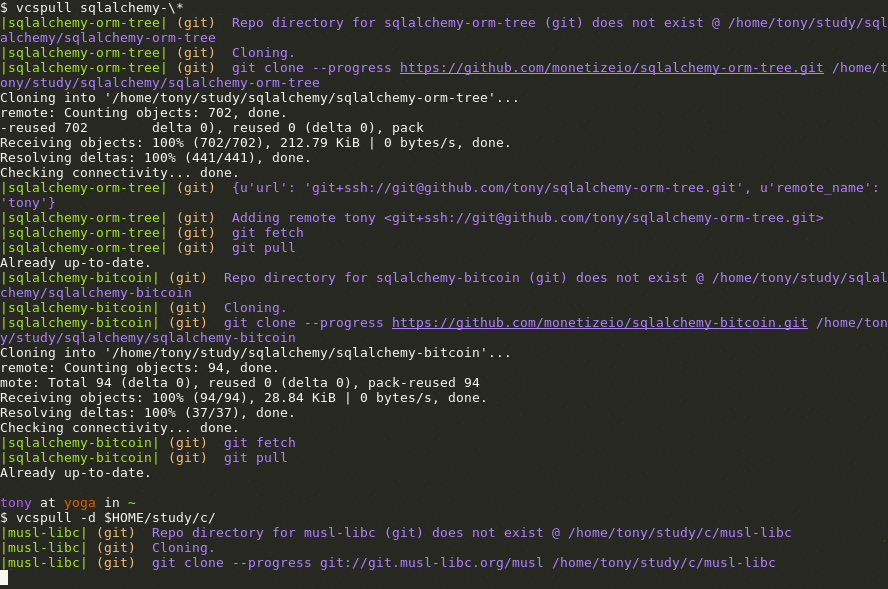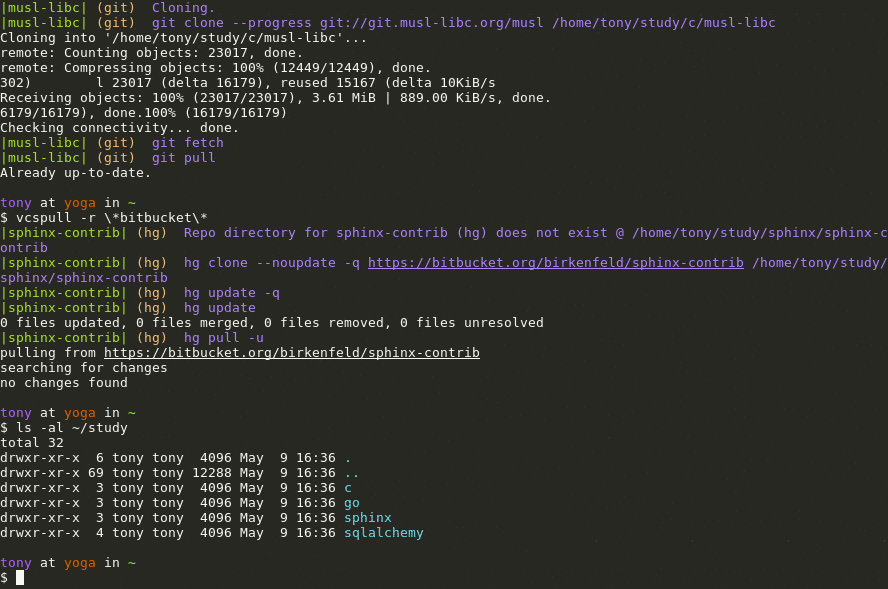
Manage and sync multiple git, svn, and mercurial repos via JSON or YAML file. Compare to myrepos, mu-repo. Built on libvcs.
Great if you use the same repos at the same locations across multiple
machines or want to clone / update a pattern of repos without having to
cd into each one.
- clone / update to the latest repos with
$ vcspull sync --all - use filters to specify a location, repo url or pattern in the manifest to clone / update
- supports svn, git, hg version control systems
- automatically checkout fresh repositories
- supports pip-style URL's (RFC3986-based url scheme)
See the documentation, configuration examples, and config generators.
How to
Install
$ pip install --user vcspull
Or using uv:
$ uv tool install vcspull
For one-time use without installation:
$ uvx vcspull
Developmental releases
You can test the unpublished version of vcspull before it's released.
-
pip:
$ pip install --user --upgrade --pre vcspull
-
pipx:
$ pipx install --suffix=@next 'vcspull' --pip-args '\--pre' --force
Then use
vcspull@next sync [config].... -
uv:
$ uv tool install --prerelease=allow vcspull
Configuration
Add your repos to ~/.vcspull.yaml. You can edit the file by hand or let
vcspull add, vcspull discover, or vcspull import create entries for you.
~/code/:
  flask: "git+https://github.com/mitsuhiko/flask.git"
~/study/c:
  awesome: "git+git://git.naquadah.org/awesome.git"
~/study/data-structures-algorithms/c:
  libds: "git+https://github.com/zhemao/libds.git"
  algoxy:
    repo: "git+https://github.com/liuxinyu95/AlgoXY.git"
    remotes:
      tony: "git+ssh://git@github.com/tony/AlgoXY.git"
(see the author's .vcspull.yaml, more configuration)
$HOME/.vcspull.yaml and $XDG_CONFIG_HOME/vcspull/ (~/.config/vcspull) can
be used as a declarative manifest to clone your repos consistently across
machines. Subsequent syncs of initialized repos will fetch the latest commits.
Add repositories from the CLI
Register a single repository by pointing at the checkout:
$ vcspull add ~/projects/libs/my-lib
- vcspull infers the name from the directory and detects the
originremote. Pass--urlwhen you need to record a different remote. - Override the derived name with
--nameand the workspace root with-w/--workspace. --dry-runpreviews the update, while--yesskips the confirmation prompt.-f/--fileselects an alternate configuration file.- Append
--no-mergeif you prefer to review duplicate workspace roots yourself instead of having vcspull merge them automatically. - Follow with
vcspull sync my-libto clone or update the working tree after registration.
Discover local checkouts and add en masse
Have a directory tree full of cloned Git repositories? Scan and append them to your configuration:
$ vcspull discover ~/code --recursive
The scan shows each repository before import unless you opt into --yes.
Add --workspace ~/code/ to pin the resulting workspace root or
-f/--file to write somewhere other than the default ~/.vcspull.yaml.
Duplicate workspace roots are merged by default; include --no-merge to
keep them separate while you review the log.
Import from remote services
Pull repository lists from GitHub, GitLab, Codeberg, Gitea, Forgejo, or AWS CodeCommit directly into your configuration:
$ vcspull import github myuser \
    --workspace ~/code/ \
    --mode user
$ vcspull import gitlab my-group \
    --workspace ~/work/ \
    --mode org
Use --dry-run to preview changes, --https for HTTPS clone URLs, and
--language/--topics/--min-stars to filter results. See the
import documentation for all
supported services and options.
Inspect configured repositories
List what vcspull already knows about without mutating anything:
$ vcspull list
$ vcspull list --tree
$ vcspull list --json | jq '.[].name'
--json emits a single JSON array, while --ndjson streams newline-delimited
objects that are easy to consume from shell pipelines.
Search across repositories with an rg-like query syntax:
$ vcspull search django
$ vcspull search name:django url:github
$ vcspull search --fixed-strings 'git+https://github.com/org/repo.git'
Check repository status
Get a quick health check for all configured workspaces:
$ vcspull status
$ vcspull status --detailed
$ vcspull status --ndjson | jq --slurp 'map(select(.reason == "summary"))'
The status command respects --workspace/-w filters and the global
--color {auto,always,never} flag. JSON and NDJSON output mirrors the list
command for automation workflows.
Normalize configuration files
After importing or editing by hand, run the formatter to tidy up keys, merge duplicate workspace sections, and keep entries sorted:
$ vcspull fmt \
    --file ~/.vcspull.yaml \
    --write
Use vcspull fmt --all --write to format every YAML file that vcspull can
discover under the standard config locations. Add --no-merge if you only want
duplicate roots reported, not rewritten.
Sync your repos
$ vcspull sync --all
Preview planned work with Terraform-style plan output or emit structured data for CI/CD:
$ vcspull sync --dry-run "*"
$ vcspull sync --dry-run --show-unchanged "workspace-*"
$ vcspull sync --dry-run --json "*" | jq '.summary'
$ vcspull sync --dry-run --ndjson "*" \
    | jq --slurp 'map(select(.type == "summary"))'
Dry runs stream a progress line when stdout is a TTY, then print a concise plan
summary (+/~/✓/⚠/✗) grouped by workspace. Use --summary-only,
--relative-paths, --long, or -v/-vv for alternate views, and
--fetch/--offline to control how remote metadata is refreshed.
Keep nested VCS repositories updated too — say you have a mercurial or svn project with a git dependency:
external_deps.yaml in your project root (any filename will do):
./vendor/:
  sdl2pp: "git+https://github.com/libSDL2pp/libSDL2pp.git"
Clone / update repos via config file:
$ vcspull sync --file external_deps.yaml '*'
See the Quickstart for more.
Pulling specific repos
Have a lot of repos? Choose to update only select repos through
fnmatch
patterns. Add the repos to your ~/.vcspull.{json,yaml} first.
The patterns filter by directory, repo name, or vcs url.
Any repo starting with "fla":
$ vcspull sync "fla*"
Any repo with django in the name:
$ vcspull sync "*django*"
Search by vcs + url, since urls are in this format +://:
$ vcspull sync "git+*"
Any git repo with python in the vcs url:
$ vcspull sync "git+*python*"
Any git repo with django in the vcs url:
$ vcspull sync "git+*django*"
All repositories in your ~/code directory:
$ vcspull sync "$HOME/code/*"
Donations
Your donations fund development of new features, testing and support. Your money will go directly to maintenance and development of the project. If you are an individual, feel free to give whatever feels right for the value you get out of the project.
See donation options at https://tony.sh/support.html.
More information
- Python support: >= 3.10, pypy
- VCS supported: git(1), svn(1), hg(1)
- Source: https://github.com/vcs-python/vcspull
- Docs: https://vcspull.git-pull.com
- Changelog: https://vcspull.git-pull.com/history.html
- API: https://vcspull.git-pull.com/api.html
- Issues: https://github.com/vcs-python/vcspull/issues
- Test Coverage: https://codecov.io/gh/vcs-python/vcspull
- pypi: https://pypi.python.org/pypi/vcspull
- Open Hub: https://www.openhub.net/p/vcspull
- License: MIT.


Release files for vcspull 1.68.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| vcspull-1.68.0.tar.gz | 2.6 MB | With provenance | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| vcspull-1.68.0-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 2.7 MB
Release files / vcspull-1.68.0.tar.gz
| Download URL | vcspull-1.68.0.tar.gz |
|---|---|
| Size | 2.6 MB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
8b18dbe81569cbea3de7c3ae5c8ad8c44f700840d6c0ce26e817adcdee5c587d
|
|
BLAKE2b-256 checksum How to use checksums |
eb46761d9c7c935816d49367608b9cf434f6dcd9711104541161829d299df9a8
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 24, 2026.
Transparency logRelease files / vcspull-1.68.0-py3-none-any.whl
| Download URL | vcspull-1.68.0-py3-none-any.whl |
|---|---|
| Size | 157.3 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
9cda7300f914d3f217b8141257dacbb7508ec73c2a24fd681857404991d919fd
|
|
BLAKE2b-256 checksum How to use checksums |
f4c46ff75b7fcaaf4b2b8aaaa10b4153424ebd8f143177b6e0d1eaf8e1f3431c
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 24, 2026.
Transparency logSecurity for vcspull 1.68.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 2 files in this release have been uploaded with provenance metadata.
Attestation for vcspull-1.68.0.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 24, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














