
vekna



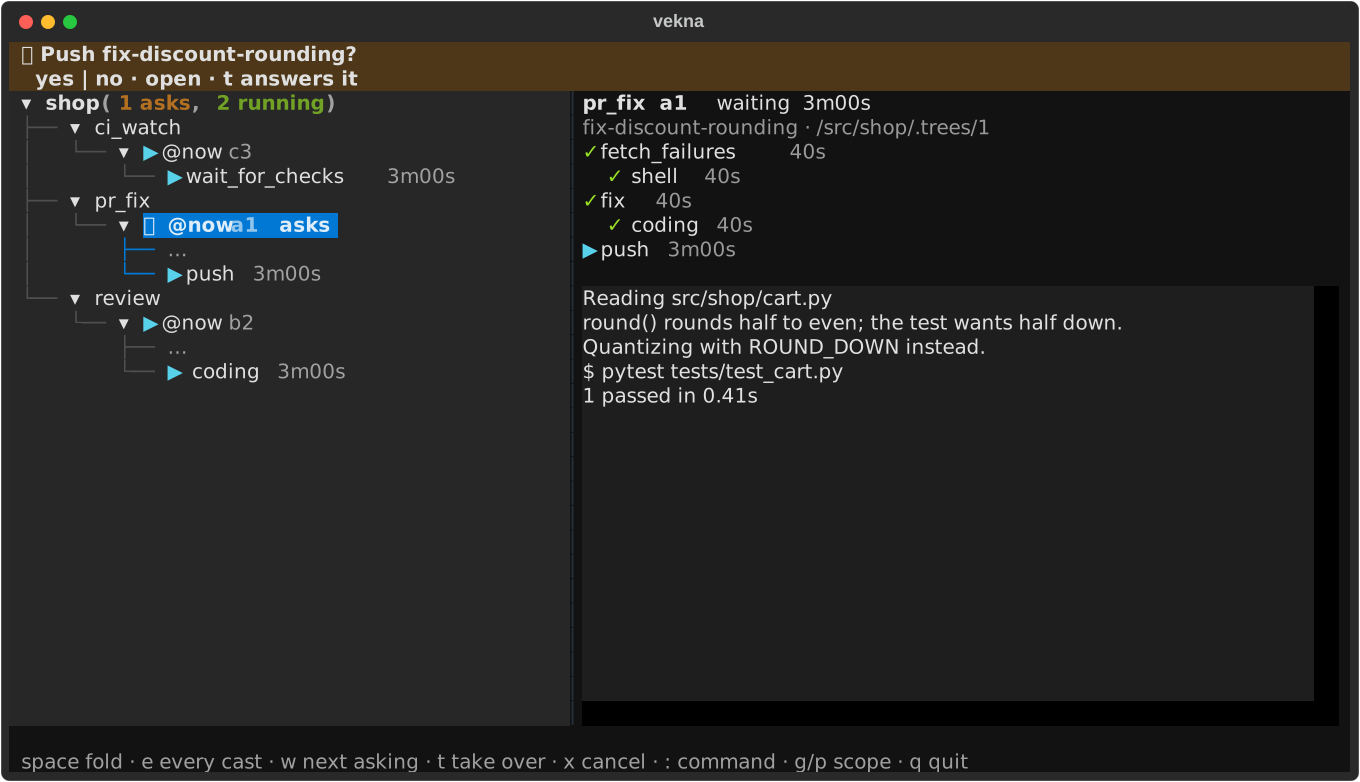
Run coding agents as rituals: ordinary Python programs whose steps you control and whose agent calls happen inside those steps. Agents run permissively within a step; determinism lives at the step boundaries.
Documentation is at vekna.fancysnake.dev.
Install
pip install vekna
Python 3.11+. Testing your rituals needs the trial extra:
pip install 'vekna[trial]' — quoted, because zsh globs the brackets.
A ritual
Put a rituals.py in your project — or a rituals/ package, split however you
like, once one file stops being enough:
from typing import Annotated

from pydantic import BaseModel, Field

from vekna.folio.coding import coding
from vekna.folio.shell import shell
from vekna.lexicon import Done, ritual, step


class FixTests(BaseModel):
    # A retry budget counts down to zero, so the CLI rejects a negative one
    # rather than letting `--bound -1` run until the step backstop.
    bound: Annotated[int, Field(ge=0)] = 3


class Attempt(BaseModel):
    left: int


class Verdict(BaseModel):
    outcome: str


# The return annotation is the step's exits: back to `fix`, or finished with a
# `Verdict`. mypy checks every return against it, so a mis-wire fails the type
# check rather than a cast.
@step
async def fix(state: Attempt) -> Attempt | Done[Verdict]:
    result = await shell("mise run test:py")
    if result.exit_code == 0:
        return Done(Verdict(outcome="green"))
    if state.left <= 0:
        return Done(Verdict(outcome="gave up"))
    await coding(f"The test suite fails:\n{result.stdout}\nFix it.")
    return Attempt(left=state.left - 1)


# `def`, not `async def`: naming the first step has nothing to await. A step or
# entrypoint is written whichever way its body needs.
@ritual("fix_tests")
def fix_tests(components: FixTests) -> Attempt:
    return Attempt(left=components.bound)
Then cast it:
vekna cast fix_tests --bound 5
Output streams live as a tree of rites — one node per step, one nested under it per medium call, with the agent's own output indented beneath. The last line is the cast's result, as JSON:
result: {"outcome":"green"}
Claude Code plugin
The ritual-scribe skill teaches Claude Code to write rituals. Install it from
this repo's marketplace:
claude plugin marketplace add fancysnake/vekna
claude plugin install ritual-scribe@vekna
Commands
| Command | What it does |
|---|---|
vekna cast <ritual> [--<component> value …] |
Run a ritual from rituals.py |
vekna cast --prompt "<text>" |
One-shot cast on the coding medium, no rituals.py needed |
vekna rituals list |
Every ritual and the options it takes |
vekna rituals show <ritual> |
A ritual's components and its step graph |
Contributing
CONTRIBUTING.md
covers setup, the check loop, where code goes, and pull requests.
docs/README.md
is where the ideas live.
Licence
BSD-3-Clause.
1 maintainer

Metadata
1 maintainer
Release files for vekna 1.0.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| vekna-1.0.0.tar.gz | 138.4 kB | With provenance | Details for vekna-1.0.0.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| vekna-1.0.0-py3-none-any.whl | Python 3 | none | any | Details for vekna-1.0.0-py3-none-any.whl |
Total release size: 309.4 kB
Release files / vekna-1.0.0.tar.gz
| Download URL | vekna-1.0.0.tar.gz |
|---|---|
| Size | 138.4 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
176ba40568295167261a0f780548c9e4ae1cdacf44d34bc8b2122dfdaa214da2
|
|
BLAKE2b-256 checksum How to use checksums |
444323aacc585b60e1cd5439d480678b361eea1188d040a13f6ab771b00a80ef
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 11, 2026.
Transparency logRelease files / vekna-1.0.0-py3-none-any.whl
| Download URL | vekna-1.0.0-py3-none-any.whl |
|---|---|
| Size | 171.0 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
14728664cf2b1b55ddaa9926b403a74073a7c4cf964aa03bca23f42ced2f6395
|
|
BLAKE2b-256 checksum How to use checksums |
dbeba71e925d49aa0f209e2d3c833557c9c01dc9fcc9f39a15f8baeb652c42fe
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 11, 2026.
Transparency logSecurity for vekna 1.0.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
Both files in this release have been uploaded with provenance metadata.
Attestation for vekna-1.0.0.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 11, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














