
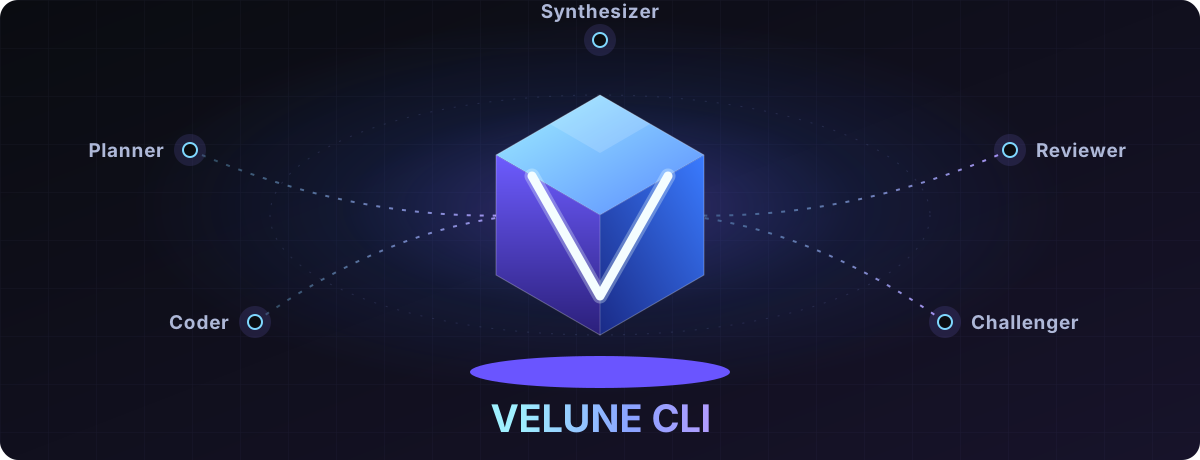
Velune CLI
Your models. Your machine. Your approval.
An open-source, local-first AI engineer for your terminal.




Here's the deal.
AI can write code. Fine. The real question is whether you let it near the codebase that pays your bills.
You've got five worries, and they're all fair:
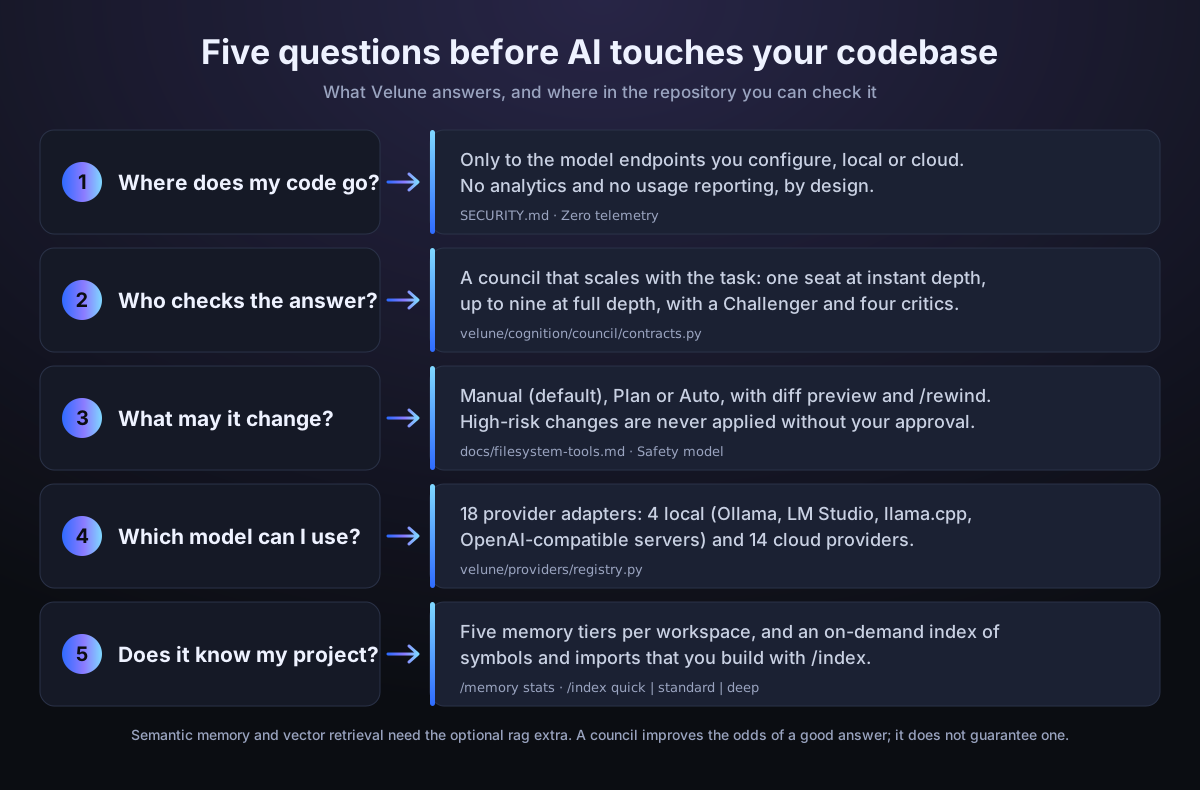
Velune answers every one of them. And every answer points at a file in this repo. Don't take my word for it. Go check.
What you get
- 🔒 Your code stays yours. Run a model on your own machine. No analytics, no usage data sent to us (proof).
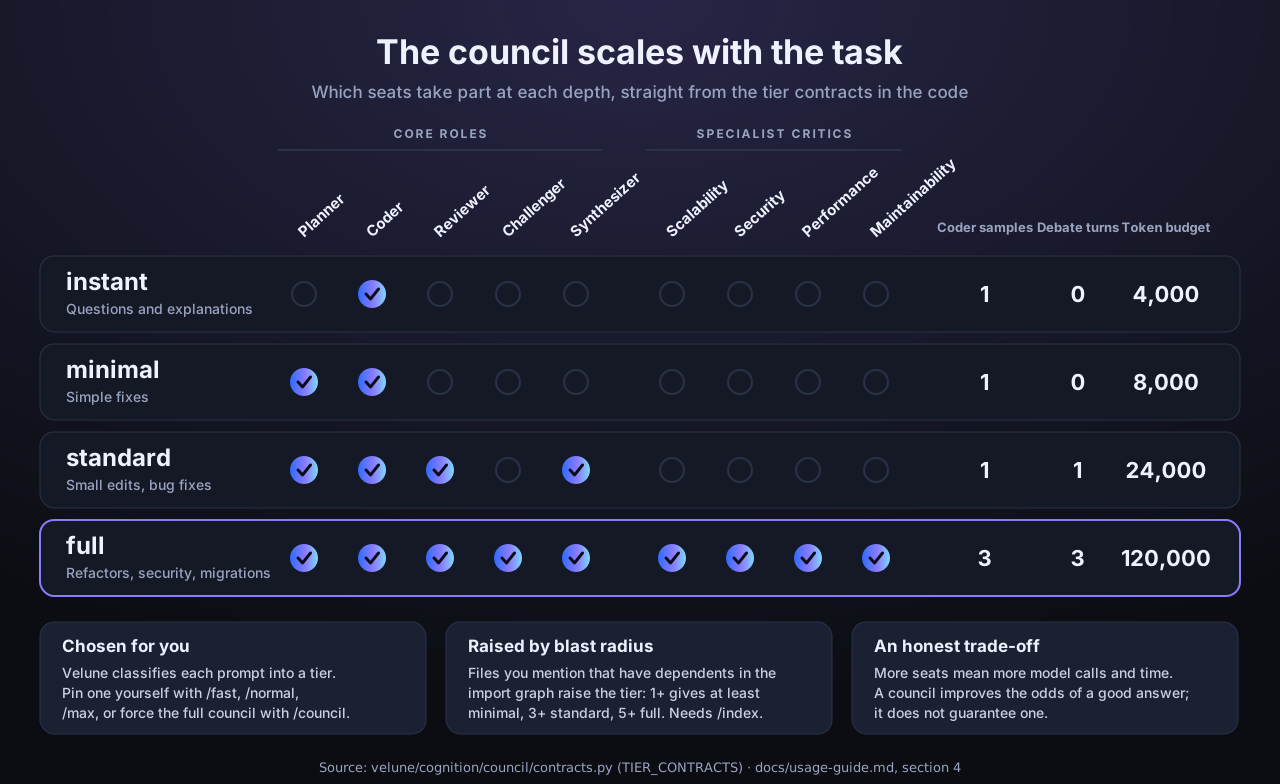
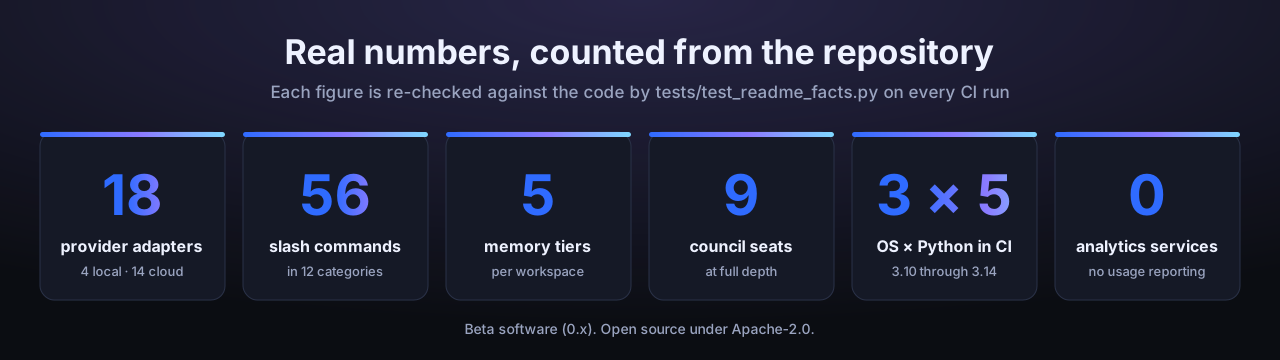
- 🧠 A council, not a lone gun. Easy question? One seat. Big refactor? Up to nine seats, including a Challenger whose whole job is to poke holes in the plan.
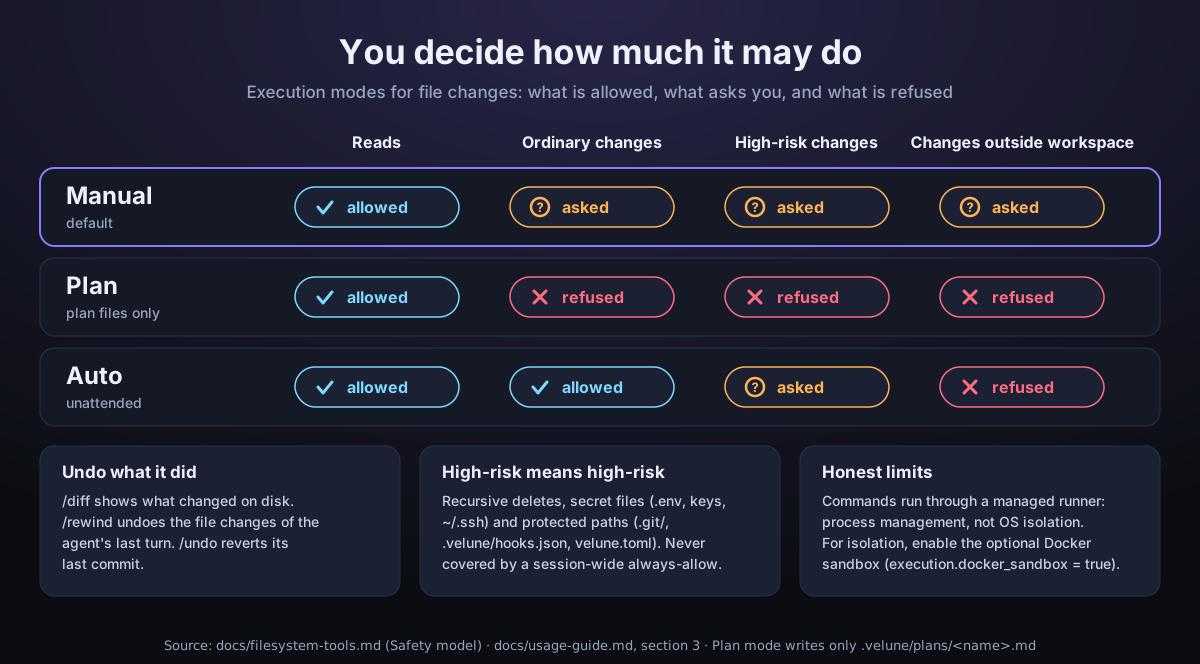
- 🛡️ You hold the leash. Manual by default. Every change is a diff you approve. One command to undo.
- 📚 It remembers. Five memory tiers per project, so it knows your code before you explain it.
It works like this:
/plan add input validation to signup     it investigates and writes a plan. No file touched.
approve                                  it runs the plan. You see every diff first.
/diff                                    see exactly what changed
/rewind                                  don't like it? Undo the agent's last turn.
A council raises your odds of a good answer. It doesn't promise one. It costs more calls than a single model, so it only shows up when the task needs it. Read your diffs.
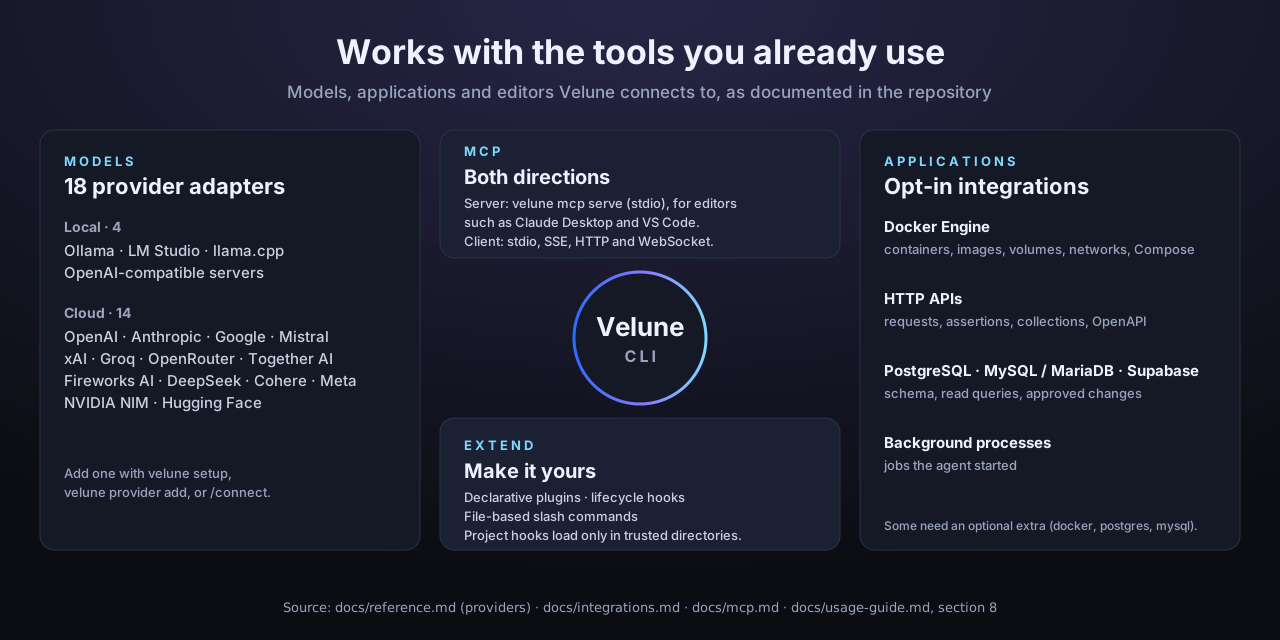
Plugs into everything
The numbers
No hype. Counted from the code. A test recomputes them on every CI run and fails if they drift.
The honest part: this is beta. Things change between releases. Command execution is process management, not an OS-level sandbox (a Docker sandbox is opt-in). The full list of limits is in SECURITY.md.
Get in. Two minutes.
macOS, Linux, WSL
curl -fsSL https://raw.githubusercontent.com/Surya-Hariharan/Velune-CLI/main/scripts/install.sh | sh
Windows (PowerShell)
irm https://raw.githubusercontent.com/Surya-Hariharan/Velune-CLI/main/scripts/install.ps1 | iex
Or pipx install velune-cli / uv tool install velune-cli. The installer needs no existing Python.
Then pick your lane:
# Fully local
ollama pull qwen2.5-coder:7b
cd your-project && velune init && velune

# Cloud (Groq free tier)
cd your-project && velune init --provider groq && velune setup && velune
Something off? Run velune doctor.
Join in
One maintainer. Open doors. Open an issue · Contribute · Report a vulnerability (privately, never in a public issue).
Go deeper: Reference · Usage guide · Slash commands · Security · Changelog
Licensed under Apache 2.0. Copyright 2026 Surya HA. Third-party names belong to their owners and identify services Velune can connect to. See NOTICE, AUTHORS and the Code of Conduct.
1 maintainer

Metadata
1 maintainer
Release files for velune-cli 0.9.9
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| velune_cli-0.9.9.tar.gz | 1.7 MB | Without provenance | Details for velune_cli-0.9.9.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| velune_cli-0.9.9-py3-none-any.whl | Python 3 | none | any | Details for velune_cli-0.9.9-py3-none-any.whl |
Total release size: 3.5 MB
Release files / velune_cli-0.9.9.tar.gz
| Download URL | velune_cli-0.9.9.tar.gz |
|---|---|
| Size | 1.7 MB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
a1511794edef24d263a24a100b834fc06e6a59110760f6b994950280af18d6c9
|
|
BLAKE2b-256 checksum How to use checksums |
5aef6f6425ad01a9e37f84fd7db691b32c5eab237b8a21b922097c96339991ba
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Release files / velune_cli-0.9.9-py3-none-any.whl
| Download URL | velune_cli-0.9.9-py3-none-any.whl |
|---|---|
| Size | 1.9 MB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
e3c974e81e8f06ee85b02e9293d711b7b8026b3abe9de1be520fbf87efef1c7c
|
|
BLAKE2b-256 checksum How to use checksums |
08e3721f8d06fddc63e49022b758efc6914861bd22578a33ac0ec1e14ee4494c
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Security for velune-cli 0.9.9
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














