
venom-report


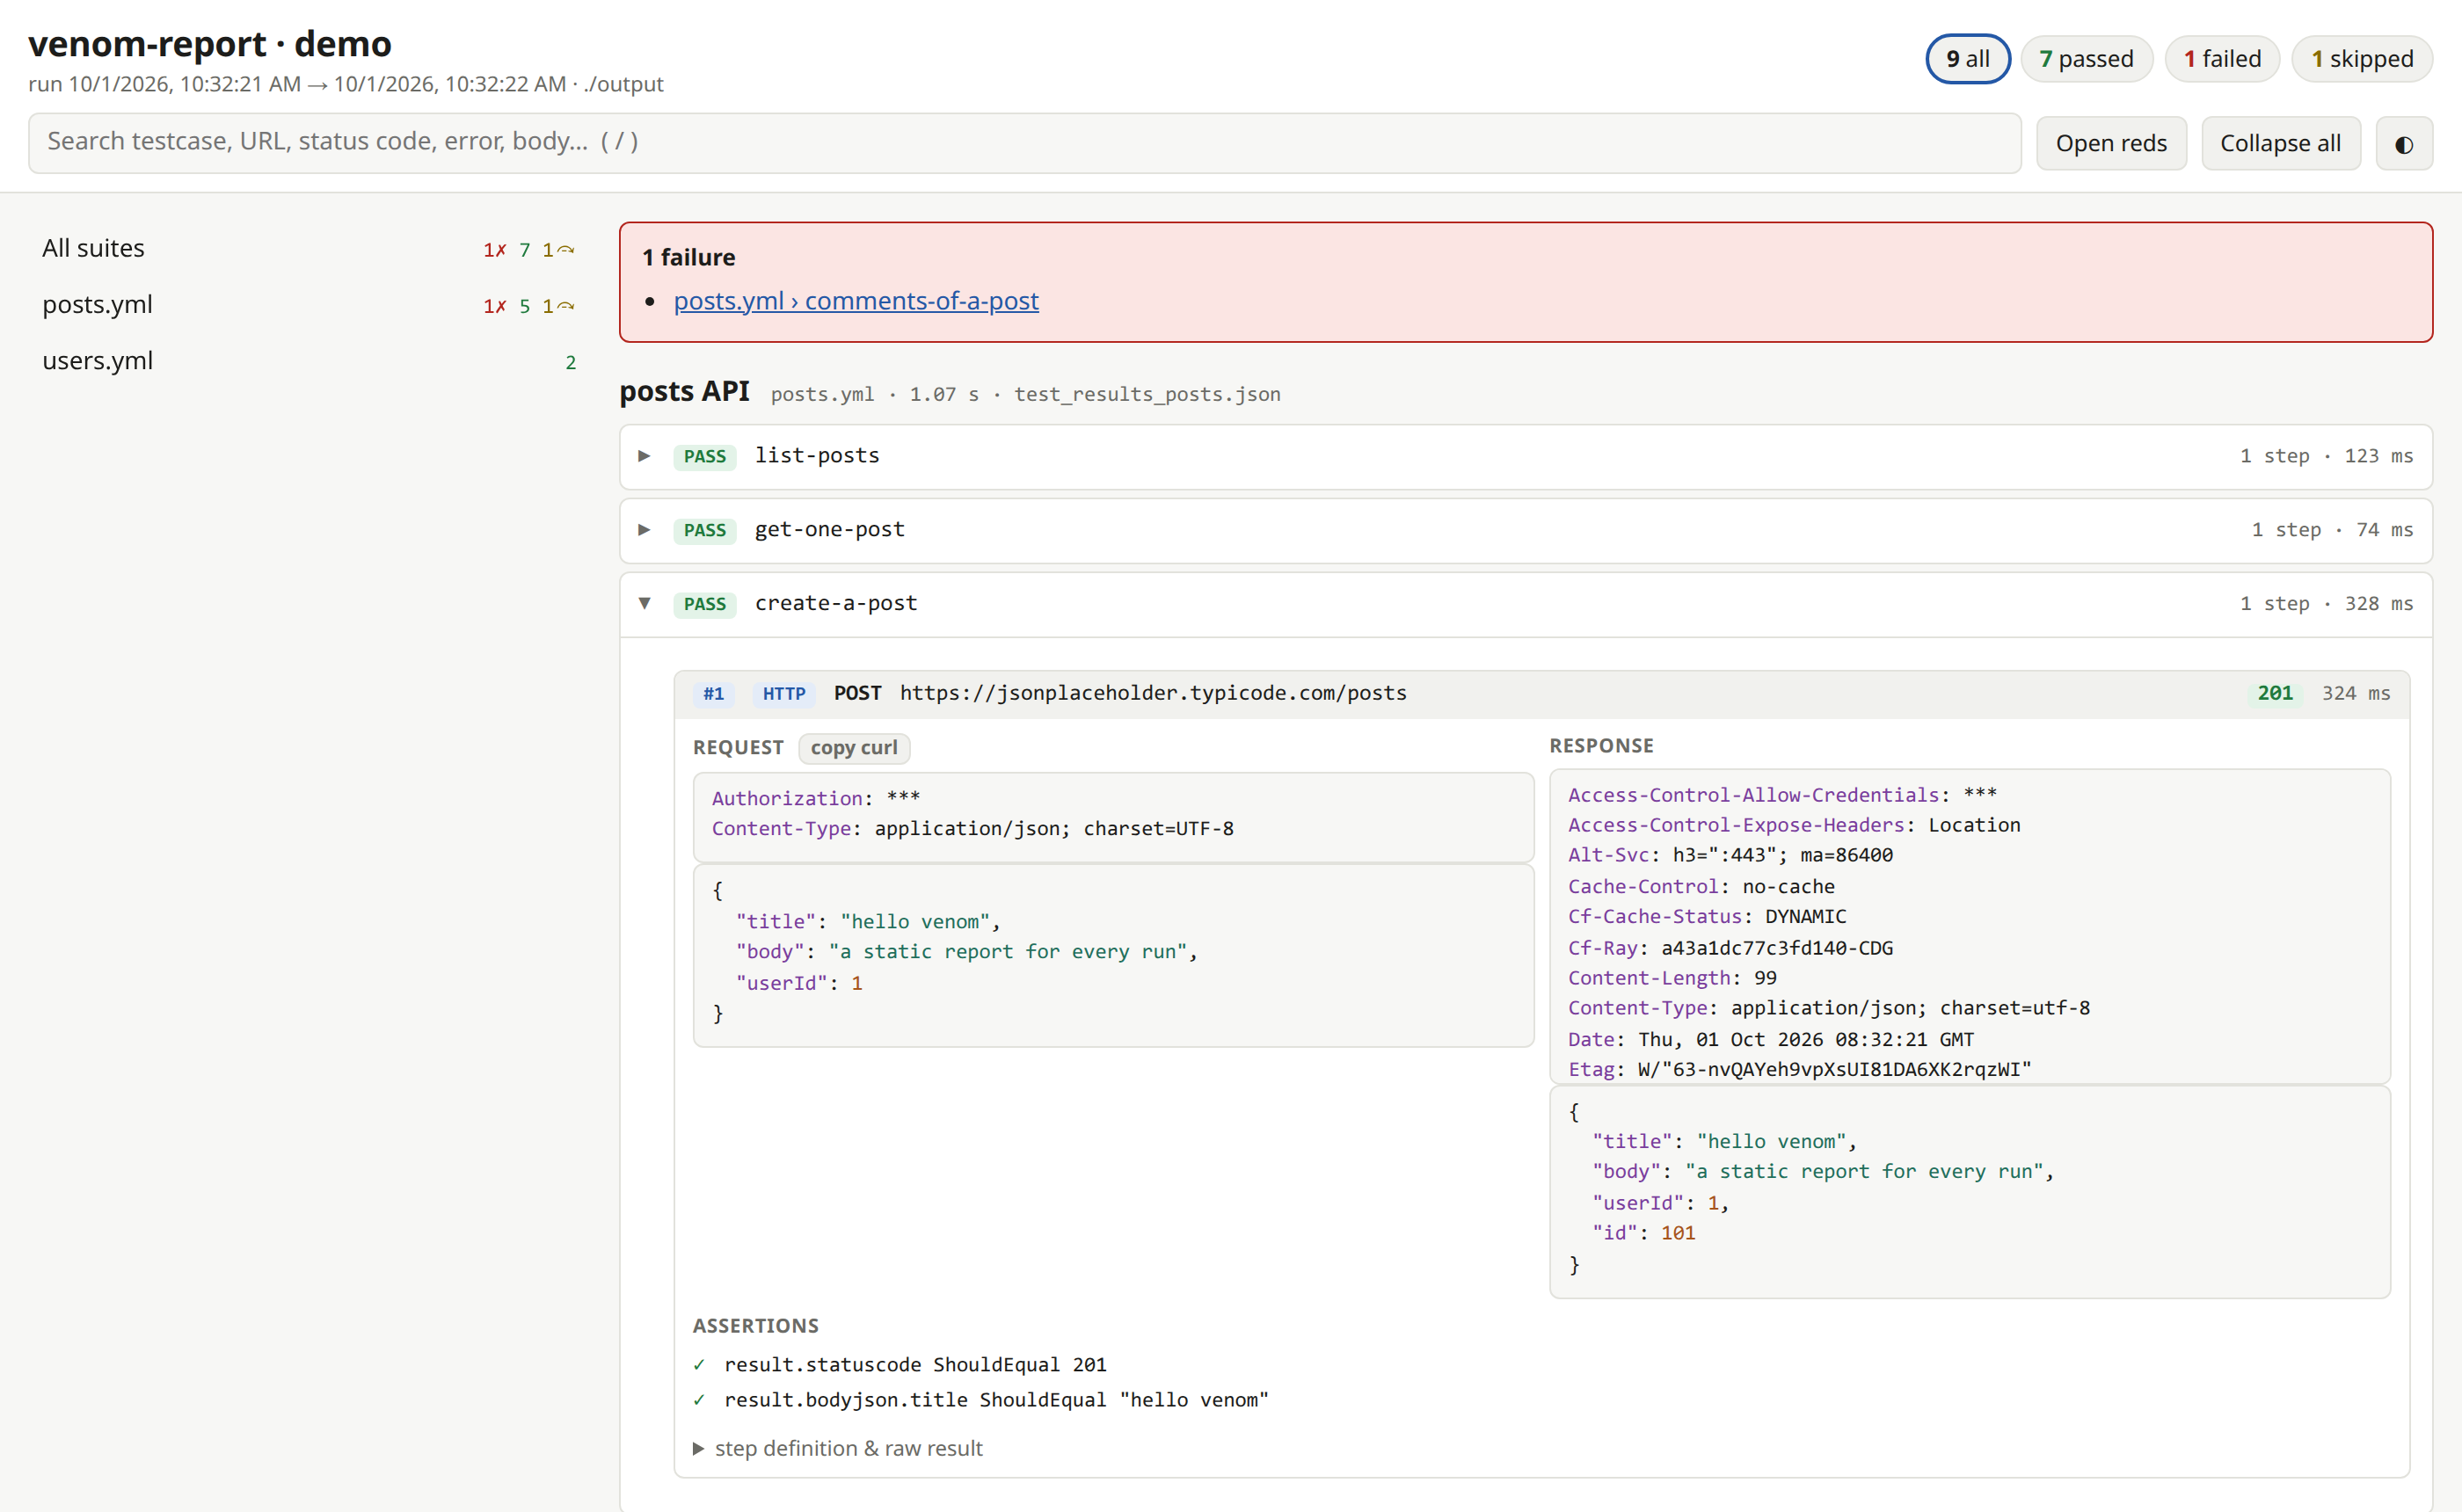
A static HTML report for any venom run, like coverage html:
every suite, testcase and step, the HTTP call made (method, URL, headers, body), the
response, the assertions (the failing one in red), and why a testcase was skipped.
pipx install venom-report          # or: uv tool install venom-report
venom-report path/to/output        # -> path/to/output/report/index.html
venom-report output --open         # and open it
No dependency (Python ≥ 3.10). The page is one self-contained file that opens over file://.
venom writes its reports only with --output-dir (or output_dir: in .venomrc): point
venom-report at that directory.
What it reads
| venom writes | when | gives |
|---|---|---|
test_results_*.xml |
format: xml (default) |
suites, testcases, pass/fail/skip, failure messages |
test_results_*.json |
format: json |
same, plus every step with its request/response, no dump needed |
*.dump.json |
-vvv / verbosity: 3 |
each step: the request sent and the full response |
Without dumps (xml, no -vvv), the report falls back on the JUnit system-out and says so.
venom never cleans output/: dumps from older runs sit next to fresh ones. A dump is
used only if it was written during the run that produced the report (from its mtime).
If the same suite was reported twice (e.g. venom run tests/ then venom run tests/x.yml),
the newest report wins.
Options
| option | default | |
|---|---|---|
-o FILE |
OUTPUT_DIR/report/index.html |
where to write |
--title T |
venom · <parent dir> |
page title |
--redact REGEX |
authorization|token|secret|passw(or)?d|cookie|api[-_]?key|credential |
keys and headers whose values are masked |
--max-body N |
100000 |
bodies longer than N chars are truncated |
--open |
open the report in a browser |
Secrets
Values under a sensitive key (in dumps, headers, venom vars, venom secrets) are masked,
then every other occurrence of those values is masked too (URLs, bodies, logs), as is
any Bearer … / Basic …. The venom variables block is never embedded. Still, check a
report before sharing it outside your team.
Tests
uv run pytest
The fixtures are real venom v1.3.0 outputs of tests/fixtures/suite_a.yml.
Release
Publish a GitHub release with a vX.Y.Z tag: the version comes from the tag, and the
Release workflow uploads to PyPI (trusted publishing, no token).
License
1 maintainer

Metadata
1 maintainer
Release files for venom-report 0.1.1
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | |
|---|---|---|---|
| venom_report-0.1.1.tar.gz | 26.7 kB | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| venom_report-0.1.1-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 48.8 kB
Release files / venom_report-0.1.1.tar.gz
| Download URL | venom_report-0.1.1.tar.gz |
|---|---|
| Size | 26.7 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
80f010590b29ce3ed1699e62da3e9745e951850e135f670b53c379621a4818cd
|
|
BLAKE2b-256 checksum How to use checksums |
9fe8d2f2e9ad748df0e5a067d5dcd6fff83a7dba04c69fb33262bbba4ff29b97
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 1, 2026.
Transparency logRelease files / venom_report-0.1.1-py3-none-any.whl
| Download URL | venom_report-0.1.1-py3-none-any.whl |
|---|---|
| Size | 22.0 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
16e4b1fde2cc2e0b6dfcf4c105574f9ea92c64f527386b1d3dedb4770e3b6a87
|
|
BLAKE2b-256 checksum How to use checksums |
34c9e8b90d8c6099214be25db186fdde1dfd42abff41d17cf3d29d4ad5e8139d
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 1, 2026.
Transparency log













