
vibesequence



Turn your codebase into zoomable sequence diagrams that show when a user does X, who calls whom, and in what order. Use them as a map while you build, review or learn the code, on your own or with an AI assistant.
Inspired by graphify, which turns a codebase into a knowledge
graph so an AI assistant can navigate it without re-reading every file. vibesequence takes the same idea
and adds what a graph leaves out: the order of calls and the branches around them (if, loops, error
handling), drawn as user sequence diagrams that you and the assistant can both read.
Why
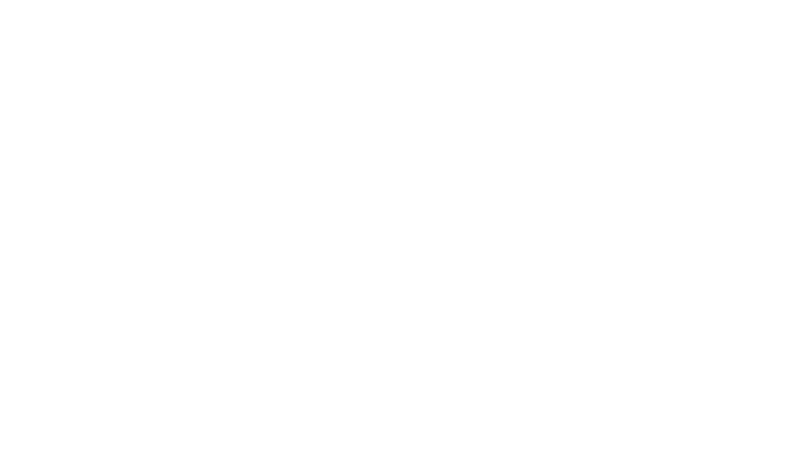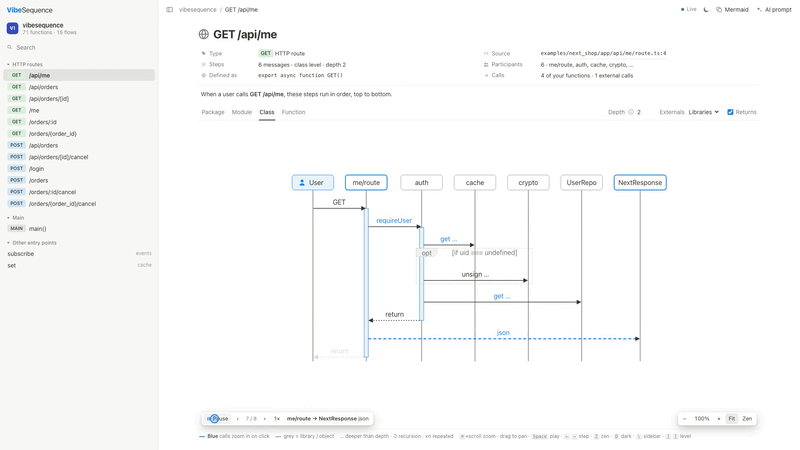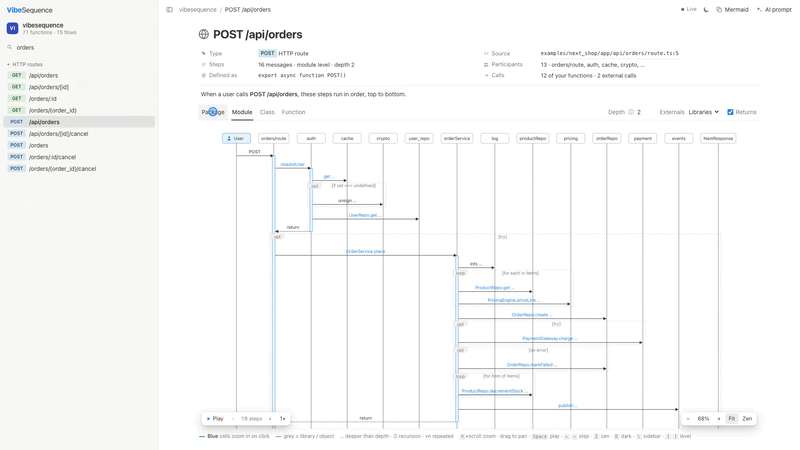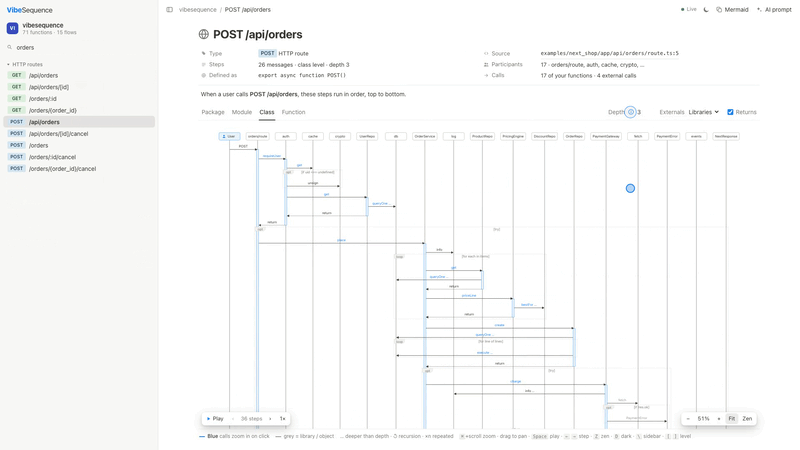
When an AI assistant edits your code, it is hard to see what actually changed in the behavior. vibesequence reads your code (no running it), finds the entry points (HTTP routes, CLI commands, handlers), and draws each one as a sequence diagram:
- Zoom between package, module, class and function level. Click a blue call to open it on its own.
- Play a flow arrow by arrow, with the
file:lineof each step. - Live: while the AI edits, changed steps turn green and you can play only the changes.
- AI friendly: the same flow is available as compact text, so your assistant reads one diagram instead of eight files.
Supports Python (stdlib only), TypeScript / JavaScript (Next.js, Express) and Go (net/http, Gin, Echo, Chi, Fiber, Cobra).
Does it save tokens?
We benchmarked Claude Code on the same tasks with and without vibesequence. Every run passed in both setups.
| task type | input tokens | cost | turns |
|---|---|---|---|
| understanding a flow ("what happens when…", "what breaks if I change…") | −23% | −18% | 8 → 4 |
| small edits | +19% | +15% | 5.5 → 6 |
Impact questions save the most: one vibesequence callers call replaced 6–7 greps and reads (−53% tokens).
For edits, the agent still has to read the files it changes, so on the tiny example projects the map is
extra overhead. Full method, per-task results and caveats: docs/benchmark.
Install
From PyPI:
pip install vibesequence
pip install "vibesequence[ts]"   # with TypeScript / JavaScript support
pip install "vibesequence[go]"   # with Go support
Quick start
vibesequence build .        # parse the repo into vibesequence-out/
vibesequence serve          # open the viewer at http://127.0.0.1:8765
Try it on the bundled examples: clone this repo and run vibesequence build examples.
Commands
| command | what it does |
|---|---|
vibesequence build . |
parse the repo into vibesequence-out/ (incremental) |
vibesequence serve |
live viewer; source links open your editor |
vibesequence list |
list all flows |
vibesequence show "POST /orders" |
one flow as Mermaid (--format text for the AI-friendly tree) |
vibesequence callers OrderRepo.create |
who calls this, and which flows are affected |
vibesequence diff |
which flows changed in the last build |
vibesequence install |
add instructions to CLAUDE.md + a Claude Code hook that shows changed flows after each edit |
Viewer shortcuts
Space play · ← → step · [ ] level · Z zen · D dark mode · \ sidebar · ⌘+scroll zoom · drag to pan
Roadmap
- Go: tree-sitter extractor, entry points for
net/http, Gin, Echo, Chi, Fiber and Cobra commands - Java: Spring controllers
- Smarter resolution: return-type inference, dependency injection, interface → implementations
- Diff against a git ref: review a PR as sequence changes, not line changes
- MCP server: let the assistant call
list_flows/show_flowinstead of reading files - Runtime traces (optional): mark the paths that actually ran
Contributing
Open for contributions! Pick a roadmap item, fix a bug, or improve the docs. Issues and pull requests are welcome.
- New language: add one extractor class in
vibesequence/extractors/that outputsModuleFacts(seeextractors/base.py). The resolver, viewer and CLI work without changes. - Set up: clone the repo and run
pip install -e ".[ts,go]". - Run the tests before opening a PR:
python tests/test_flow.py - Not sure where to start? Open an issue and say what you want to build.
Learn more
How the engine turns code into sequence diagrams (extract → resolve → expand → project → render), plus live mode, editor links and the AI hook: docs/how-it-works.md.
1 maintainer

Metadata
1 maintainer
Release files for vibesequence 0.2.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| vibesequence-0.2.0.tar.gz | 76.5 kB | With provenance | Details for vibesequence-0.2.0.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| vibesequence-0.2.0-py3-none-any.whl | Python 3 | none | any | Details for vibesequence-0.2.0-py3-none-any.whl |
Total release size: 154.6 kB
Release files / vibesequence-0.2.0.tar.gz
| Download URL | vibesequence-0.2.0.tar.gz |
|---|---|
| Size | 76.5 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
2ed729014dab3ab4306a5c6b6ef0cb7b0ac230cc5a27dcf02c44f46db5abfc5d
|
|
BLAKE2b-256 checksum How to use checksums |
f0d53a6b7aee9f6c12dca144a96136f40af8899a57f184145a9c5724a48194ca
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 28, 2026.
Transparency logRelease files / vibesequence-0.2.0-py3-none-any.whl
| Download URL | vibesequence-0.2.0-py3-none-any.whl |
|---|---|
| Size | 78.0 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
ad4939515f042daf4158a7e9e1f78fd32f94773166406bb1de62f8ad7a79e53d
|
|
BLAKE2b-256 checksum How to use checksums |
34e25714b979290736a2a849b53c6944d0e19b14a964a8610f4973a0adf85134
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 28, 2026.
Transparency logSecurity for vibesequence 0.2.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 2 files in this release have been uploaded with provenance metadata.
Attestation for vibesequence-0.2.0.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 28, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














