
VizControl
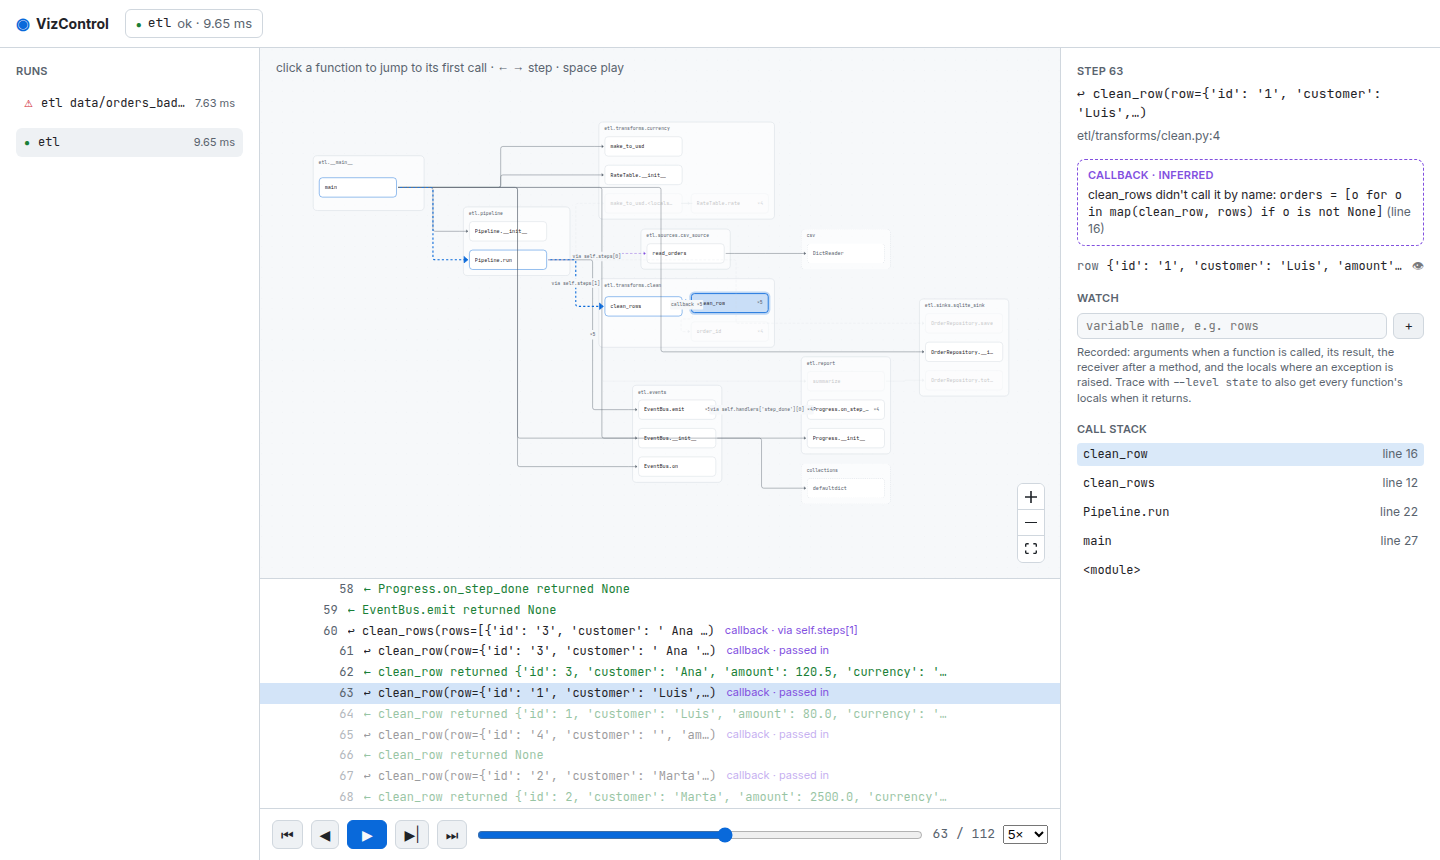
Record what a Python program really does while it runs, then step through it like a debugger after the fact. Everything shown comes from runtime evidence, not from a model's guess about the code.
pip install vizcontrol
vizcontrol run --serve app.py --flag # trace app.py, then open the run in the browser
vizcontrol run app.py --flag          # or only write .vizcontrol/runs/<time>-app.vizc
pytest --vizcontrol                   # or: one trace per test
vizcontrol serve                      # explore the runs in the browser
vizcontrol diagram <run>.vizc         # the run's stages as a Mermaid flowchart
vizcontrol diff <a>.vizc <b>.vizc     # where two runs split and which results differ
A run opens as a recording you can step through, like a debugger after the fact: the call graph (one box per module) lights up as the program goes, a transcript says who called whom with what and what came back, callbacks are marked with where the function came from, and Watch follows the variables you pick. A failed run opens on the step where it raised.
Try it on the ETL example, or read Understanding a project you didn't write.
import vizcontrol

with vizcontrol.trace("checkout") as run:
    place_order(cart)
print(run.path)
For a web app, one run per request (FastAPI shown; WSGIMiddleware for Flask and Django):
from vizcontrol.web import ASGIMiddleware

app.add_middleware(ASGIMiddleware, every=1)   # or only requests with an X-VizControl header
Requires Python 3.12+ (uses sys.monitoring). See docs/ for requirements and architecture.
Development
uv sync                                   # Python package (editable) + pytest
uv run pytest
cd frontend && npm ci && npm run build    # viewer -> src/vizcontrol/viewer/static
cd frontend && npm run e2e               # drive the built viewer in headless Chrome
uv run python benchmarks/overhead.py
License
VizControl is free software, licensed under the GNU Affero General Public License v3.0 or later. © Datzin · contacto@datzin.com.mx
1 maintainer

Metadata
1 maintainer
Release files for vizcontrol 0.4.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| vizcontrol-0.4.0.tar.gz | 301.6 kB | With provenance | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| vizcontrol-0.4.0-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 1.9 MB
Release files / vizcontrol-0.4.0.tar.gz
| Download URL | vizcontrol-0.4.0.tar.gz |
|---|---|
| Size | 301.6 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
8ed12b0851c7a92964ab84e5901f70fbab69d785241073f918d37406db81ae3e
|
|
BLAKE2b-256 checksum How to use checksums |
489ff64f2b6e732e7634906205aa6cb4a8fe24231a877efb637bc494062bbd15
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 21, 2026.
Transparency logRelease files / vizcontrol-0.4.0-py3-none-any.whl
| Download URL | vizcontrol-0.4.0-py3-none-any.whl |
|---|---|
| Size | 1.6 MB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
f2e47bbe244ee18784c12c867448ccf91fc84ee207d0c22380e3728d6b0af4b0
|
|
BLAKE2b-256 checksum How to use checksums |
914ba6dea4629020e1e71d57fbd4820fe773d08a351b7da57bce5977bd413cc0
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 21, 2026.
Transparency logSecurity for vizcontrol 0.4.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 2 files in this release have been uploaded with provenance metadata.
Attestation for vizcontrol-0.4.0.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 21, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.














